
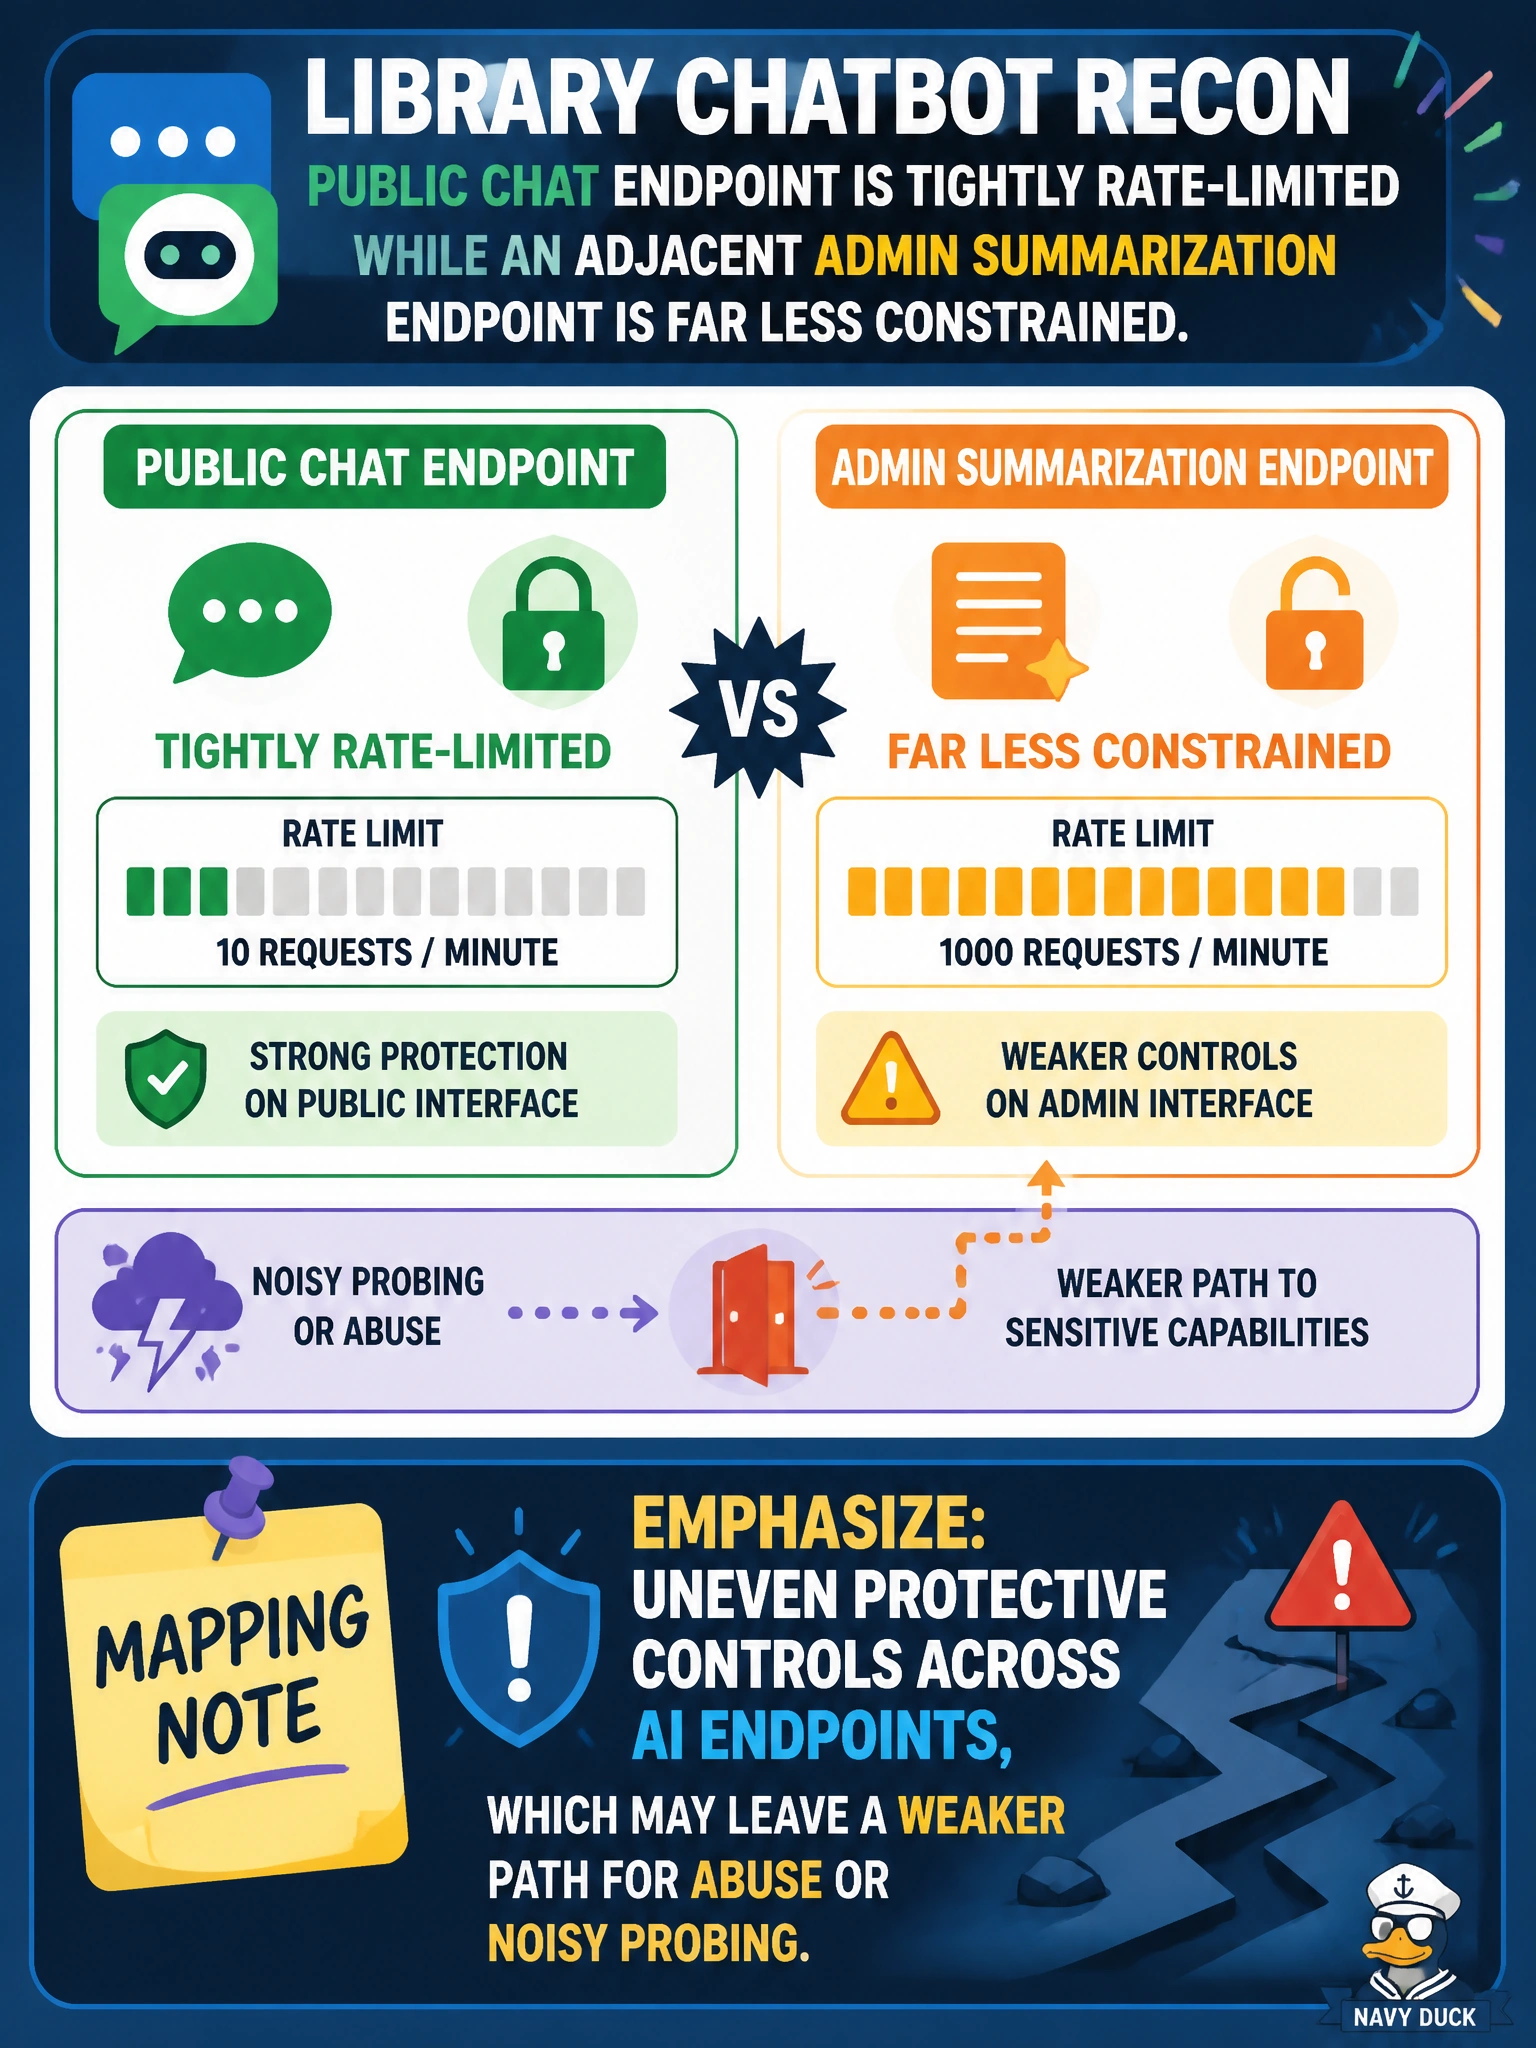
Library chatbot recon shows the public chat endpoint is tightly rate-limited while an adjacent admin summarization endpoint is far less constrained. What should the mapping note emphasize?
Select an answer to reveal the explanation.
Short Explanation
Uneven rate limits are like a vault door on the lobby and a screen door on the staff hallway—your map should call out the soft path so defenders can even things up.
Full Explanation
Library chatbot reconnaissance that finds the public chat endpoint tightly rate-limited while an adjacent admin summarization endpoint is far less constrained should emphasize uneven protective controls across AI endpoints. Control disparity is a prioritization signal: quieter or weaker paths become preferred avenues for noisy probing, credential stuffing, or abuse if admin routes are reachable to a broader audience than intended. Mapping that unevenness guides hardening so admin AI functions receive equivalent or stronger rate limiting, authentication, and monitoring than public chat.
That a shared gateway policy extends the public chat limit to the admin summarization endpoint fails because the observed disparity shows the admin route is not covered by the same limit, and assuming gateway uniformity ignores the very control gap the recon found. That the tighter public chat limit shows backend capacity planning for peak borrower traffic during term time fails because capacity planning does not explain why an adjacent admin endpoint is far less constrained; the disparity is a control gap, not a traffic forecast. That admin summarization output stays safe because summary text carries lower exposure than chat replies fails because lower perceived exposure does not remove the need for rate limiting and abuse controls on an admin AI endpoint that can still be probed or abused.
Exam caveat: Look for “weakest-path / control disparity” answers when stems contrast protective settings across related AI endpoints. Avoid assuming shared gateway uniformity and treating endpoint gaps as mere capacity planning or output sensitivity.
Operational check: document both endpoints’ authN/authZ, rate limits, and logging; remediate the weaker admin path to at least match public protections; and re-verify under authorized tests that probing the admin summarization API is appropriately constrained and alertable.