
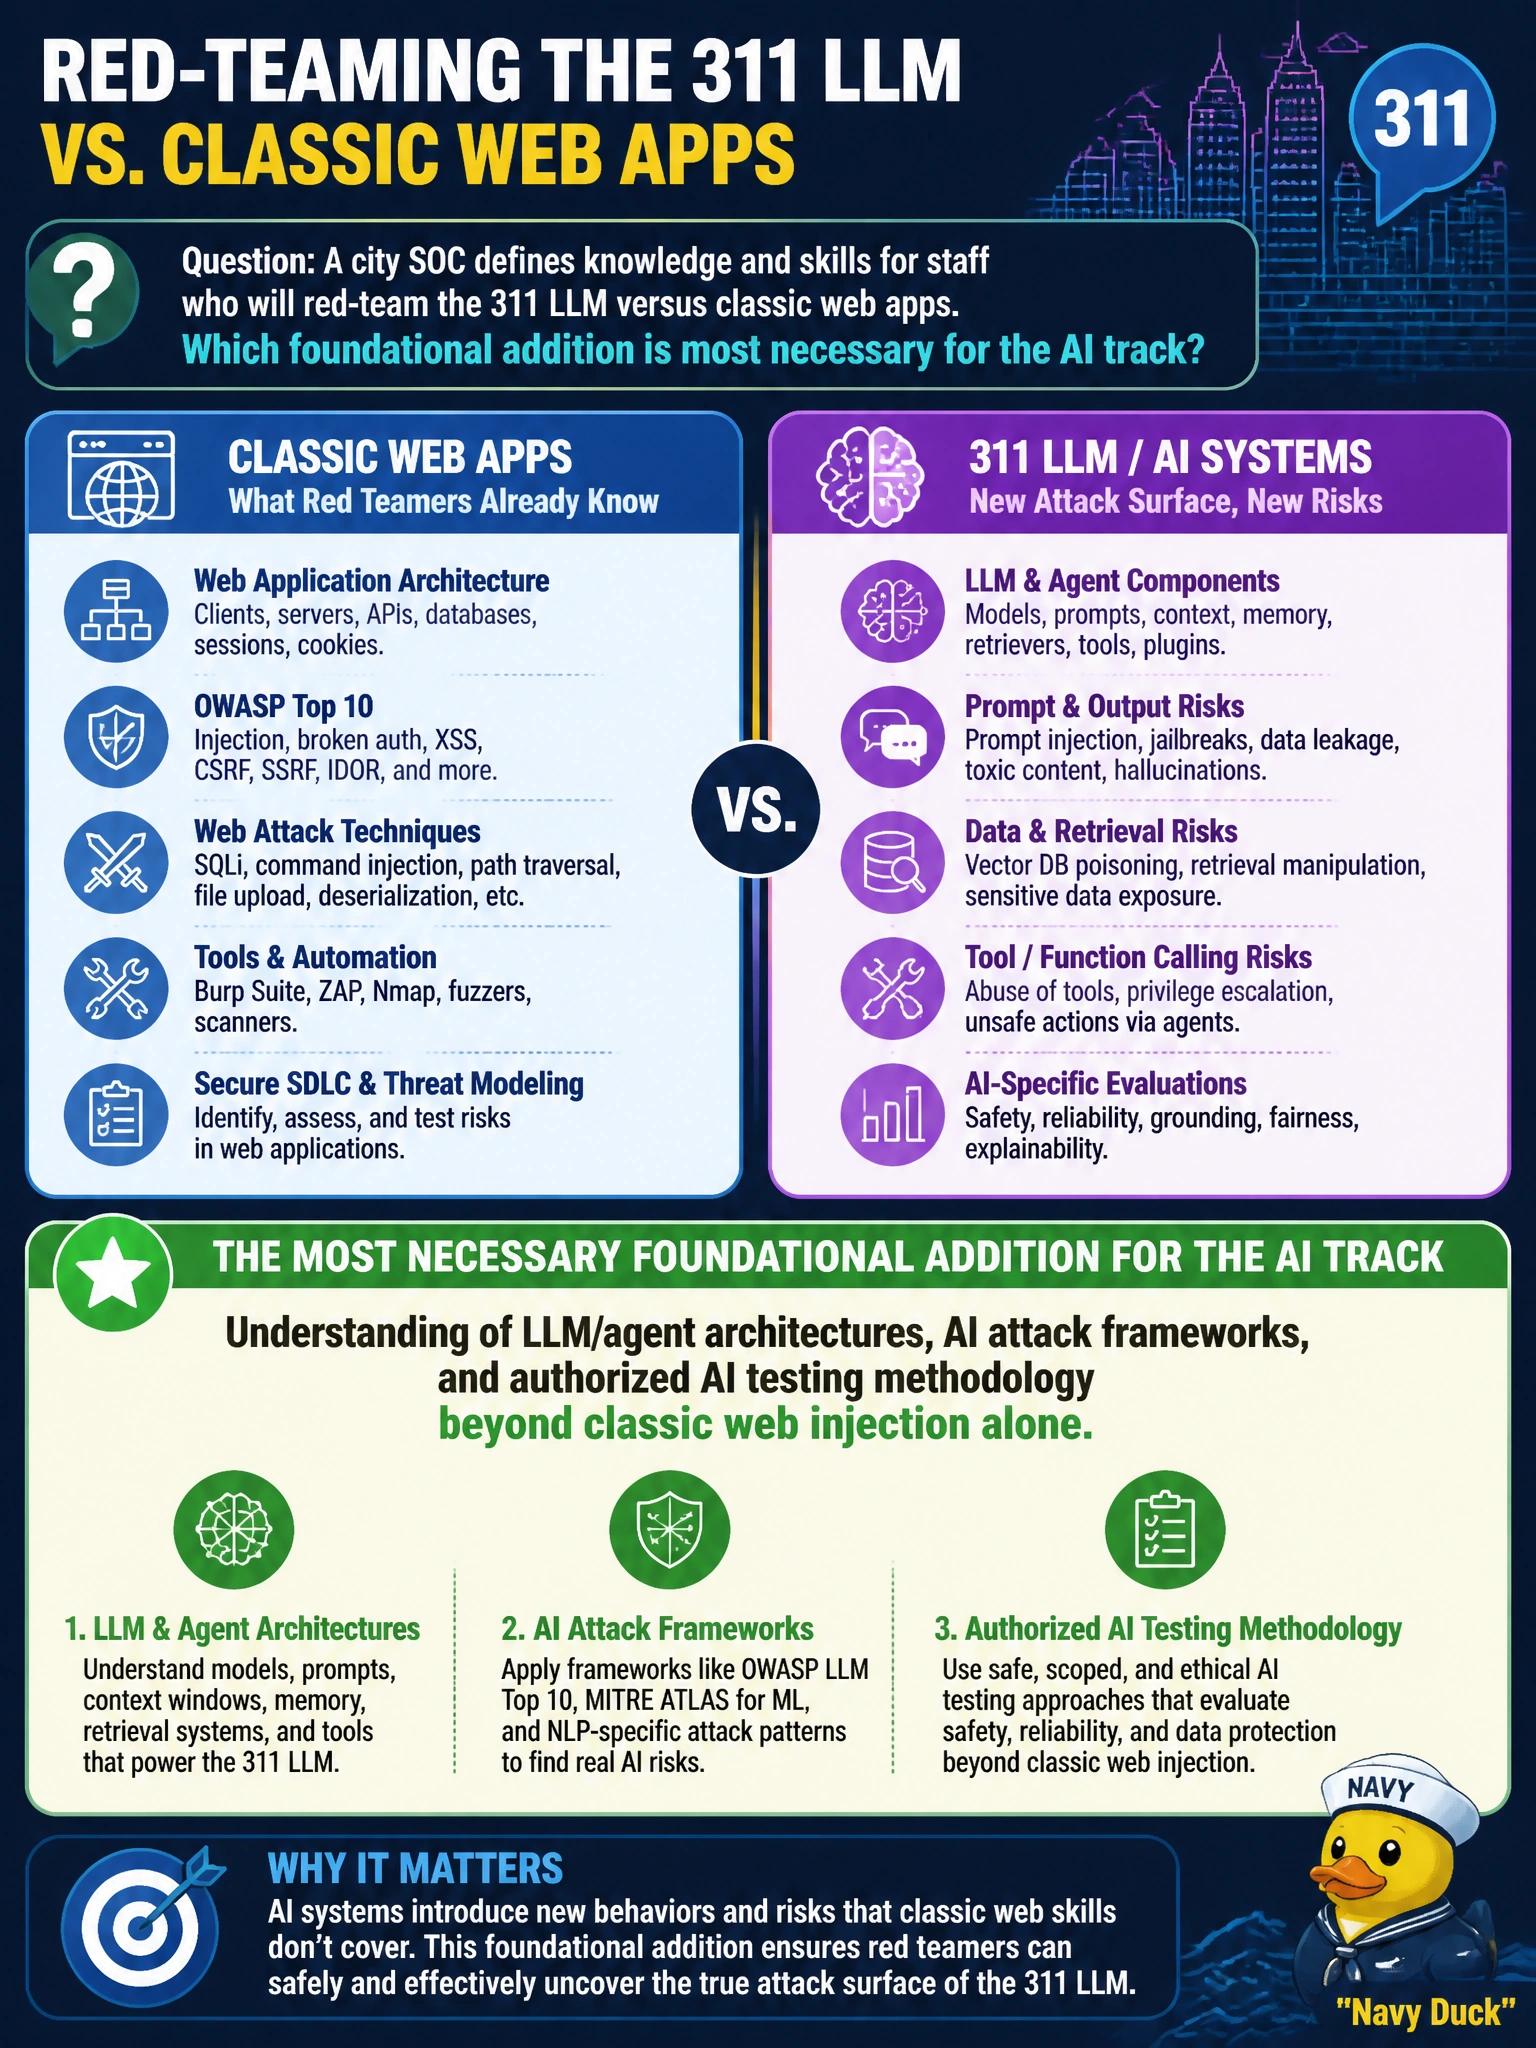
A city SOC defines knowledge and skills for staff who will red-team the 311 LLM versus classic web apps. Which foundational addition is most necessary for the AI track?
Select an answer to reveal the explanation.
Short Explanation
Proficiency in classic web injection for resident portals isn't enough by itself. You still need the AI playbook: how agents and RAG work, LLM-oriented frameworks, and how to test under a civic MoU without turning into a chaos monkey.
Full Explanation
City SOC staff who red-team a 311 LLM need KSAs beyond classic web AppSec: LLM and agent architecture literacy, familiarity with AI attack frameworks, and judgment for authorized recon and testing of prompts, retrieval, and tools. Municipal programs should upskill or hire for those capabilities rather than assuming web scanning alone covers AI assistants. Foundational training keeps civic purple-team work effective and in-bounds under MoU. Proficiency in classic web application injection testing such as SQL injection and XSS for city resident portals is not the foundational addition this track requires, since it omits LLM and agent architectures, AI attack frameworks, and authorized AI testing methodology. Expertise in hardening model hosting infrastructure with patch management, logging, and identity access controls for municipal cloud workloads is valuable for operations but does not supply the AI red-team KSAs—architecture literacy, AI attack frameworks, and authorized testing judgment—that staff need to assess the 311 assistant itself. Knowledge of traditional vulnerability scoring, risk ranking, and compliance reporting workflows for citywide remediation programs supports remediation but is not a substitute for the LLM/agent architecture, AI framework, and authorized AI testing expertise needed to red-team the assistant. Exam caveat: AI red-team KSAs add architecture, frameworks, and authorized AI methodology—classic web injection alone, infrastructure hardening alone, or traditional scoring and compliance workflows alone fail. Operational check: update SOC role profiles and training plans with LLM/RAG/agent topics and AI frameworks; require MoU-aware methodology before 311 AI tests; pair classic AppSec skills with AI-specific exercises on a non-production twin.