
A city CISO reviews a new 311 LLM assistant that answers resident requests and can open service tickets. How does this change the municipal attack surface compared with the prior static FAQ pages?
Select an answer to reveal the explanation.
Short Explanation
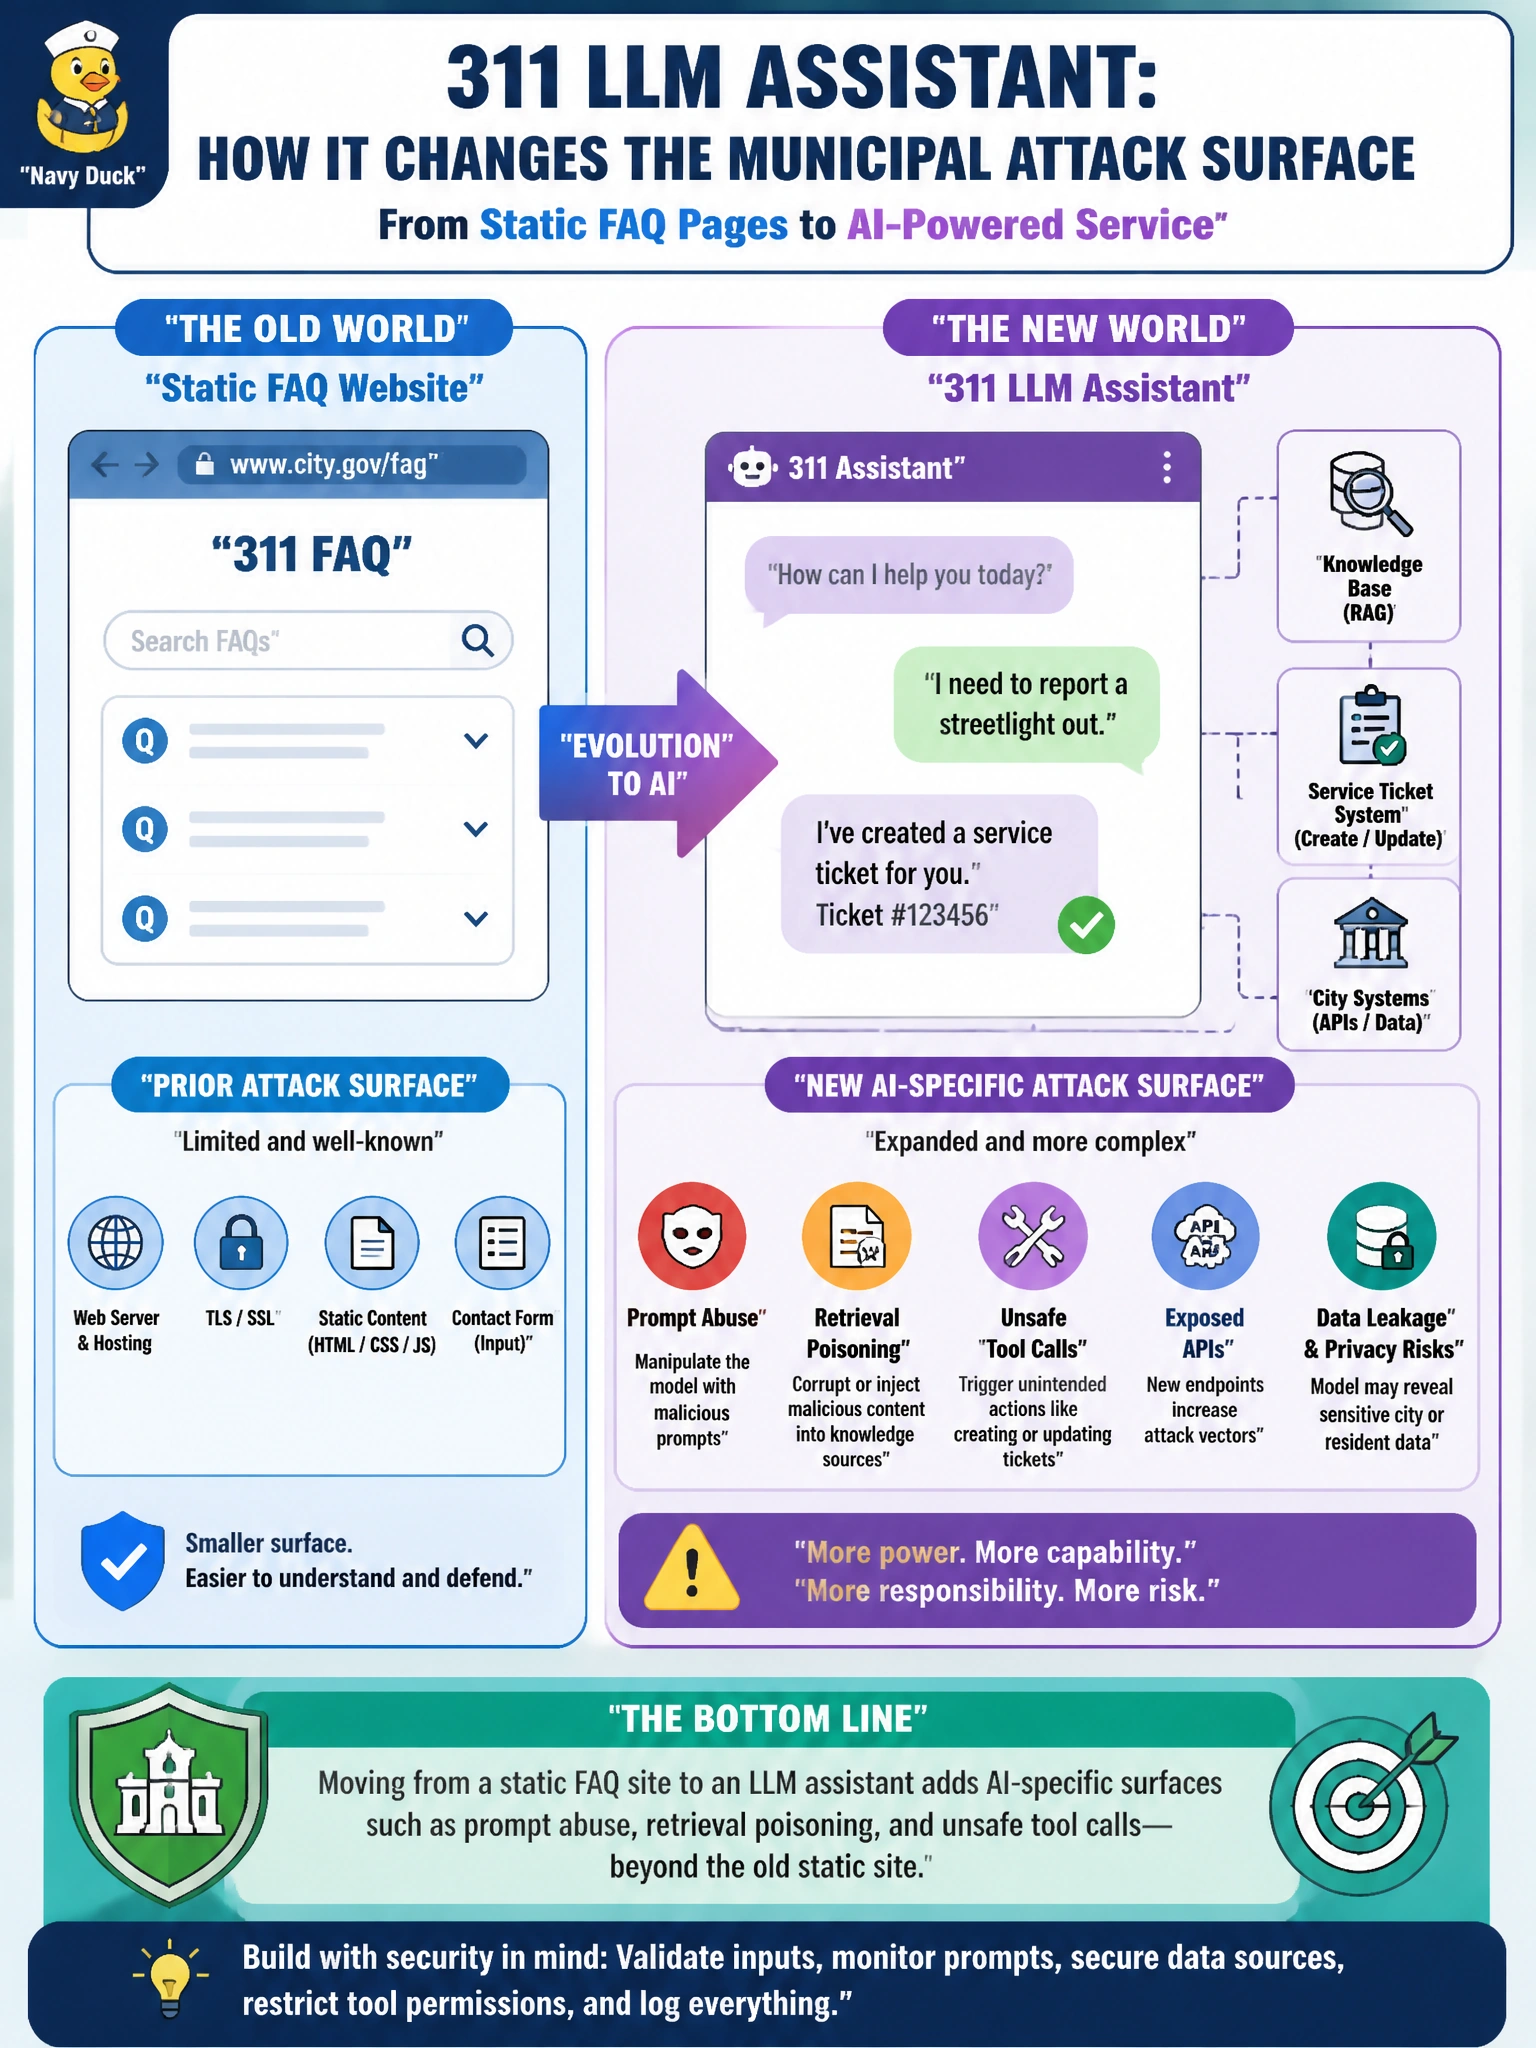
Think of the old FAQ pages like a locked bulletin board—people can read, not rewrite city workflows. The 311 LLM is more like a new front desk that takes instructions and can open tickets, so you're defending prompts, retrieved knowledge, and tool actions, not just HTML.
Full Explanation
Replacing static 311 FAQ pages with an LLM assistant that can open service tickets expands the municipal attack surface beyond classic web flaws. The assistant accepts natural-language instructions, may retrieve knowledge into context, and can invoke tools that mutate tickets or records. Those AI-specific surfaces—prompt abuse, retrieval poisoning, and unsafe tool calls—sit alongside XSS and form risks rather than replacing them. Authorized offensive AI assessments must inventory prompts, RAG corpora, and ticket-writing tools so civic defenders can prioritize input handling, retrieval integrity, and least-privilege integrations.
Attributing the added exposure to model hosting costs and response latency during citywide peak 311 demand periods and major outages mistakes performance and capacity issues for the attack surface; the real additions are prompt abuse, retrieval poisoning, and unsafe tool calls that static pages never had. Associating added exposure with encrypted storage for municipal ticket records and chat transcripts at rest and access reviews addresses data protection and governance, not the AI-specific attack surface; encryption and reviews do not create or remove prompt, retrieval, or tool-invocation risks. Attributing added risk to public records retention and redaction workflows for 311 resident chat logs and service histories concerns compliance and data governance, not the new AI-specific surfaces created by natural-language input, retrieval, and ticket-writing tools.
Exam caveat: AI assistants add surfaces; they do not erase traditional AppSec or network controls. Operational check: for the 311 rollout, list prompt entry points, retrieval indexes, and ticket tools in the attack-surface register; confirm tool scopes are least privilege; and include those AI surfaces in the next authorized purple-team charter alongside ordinary web tests.