
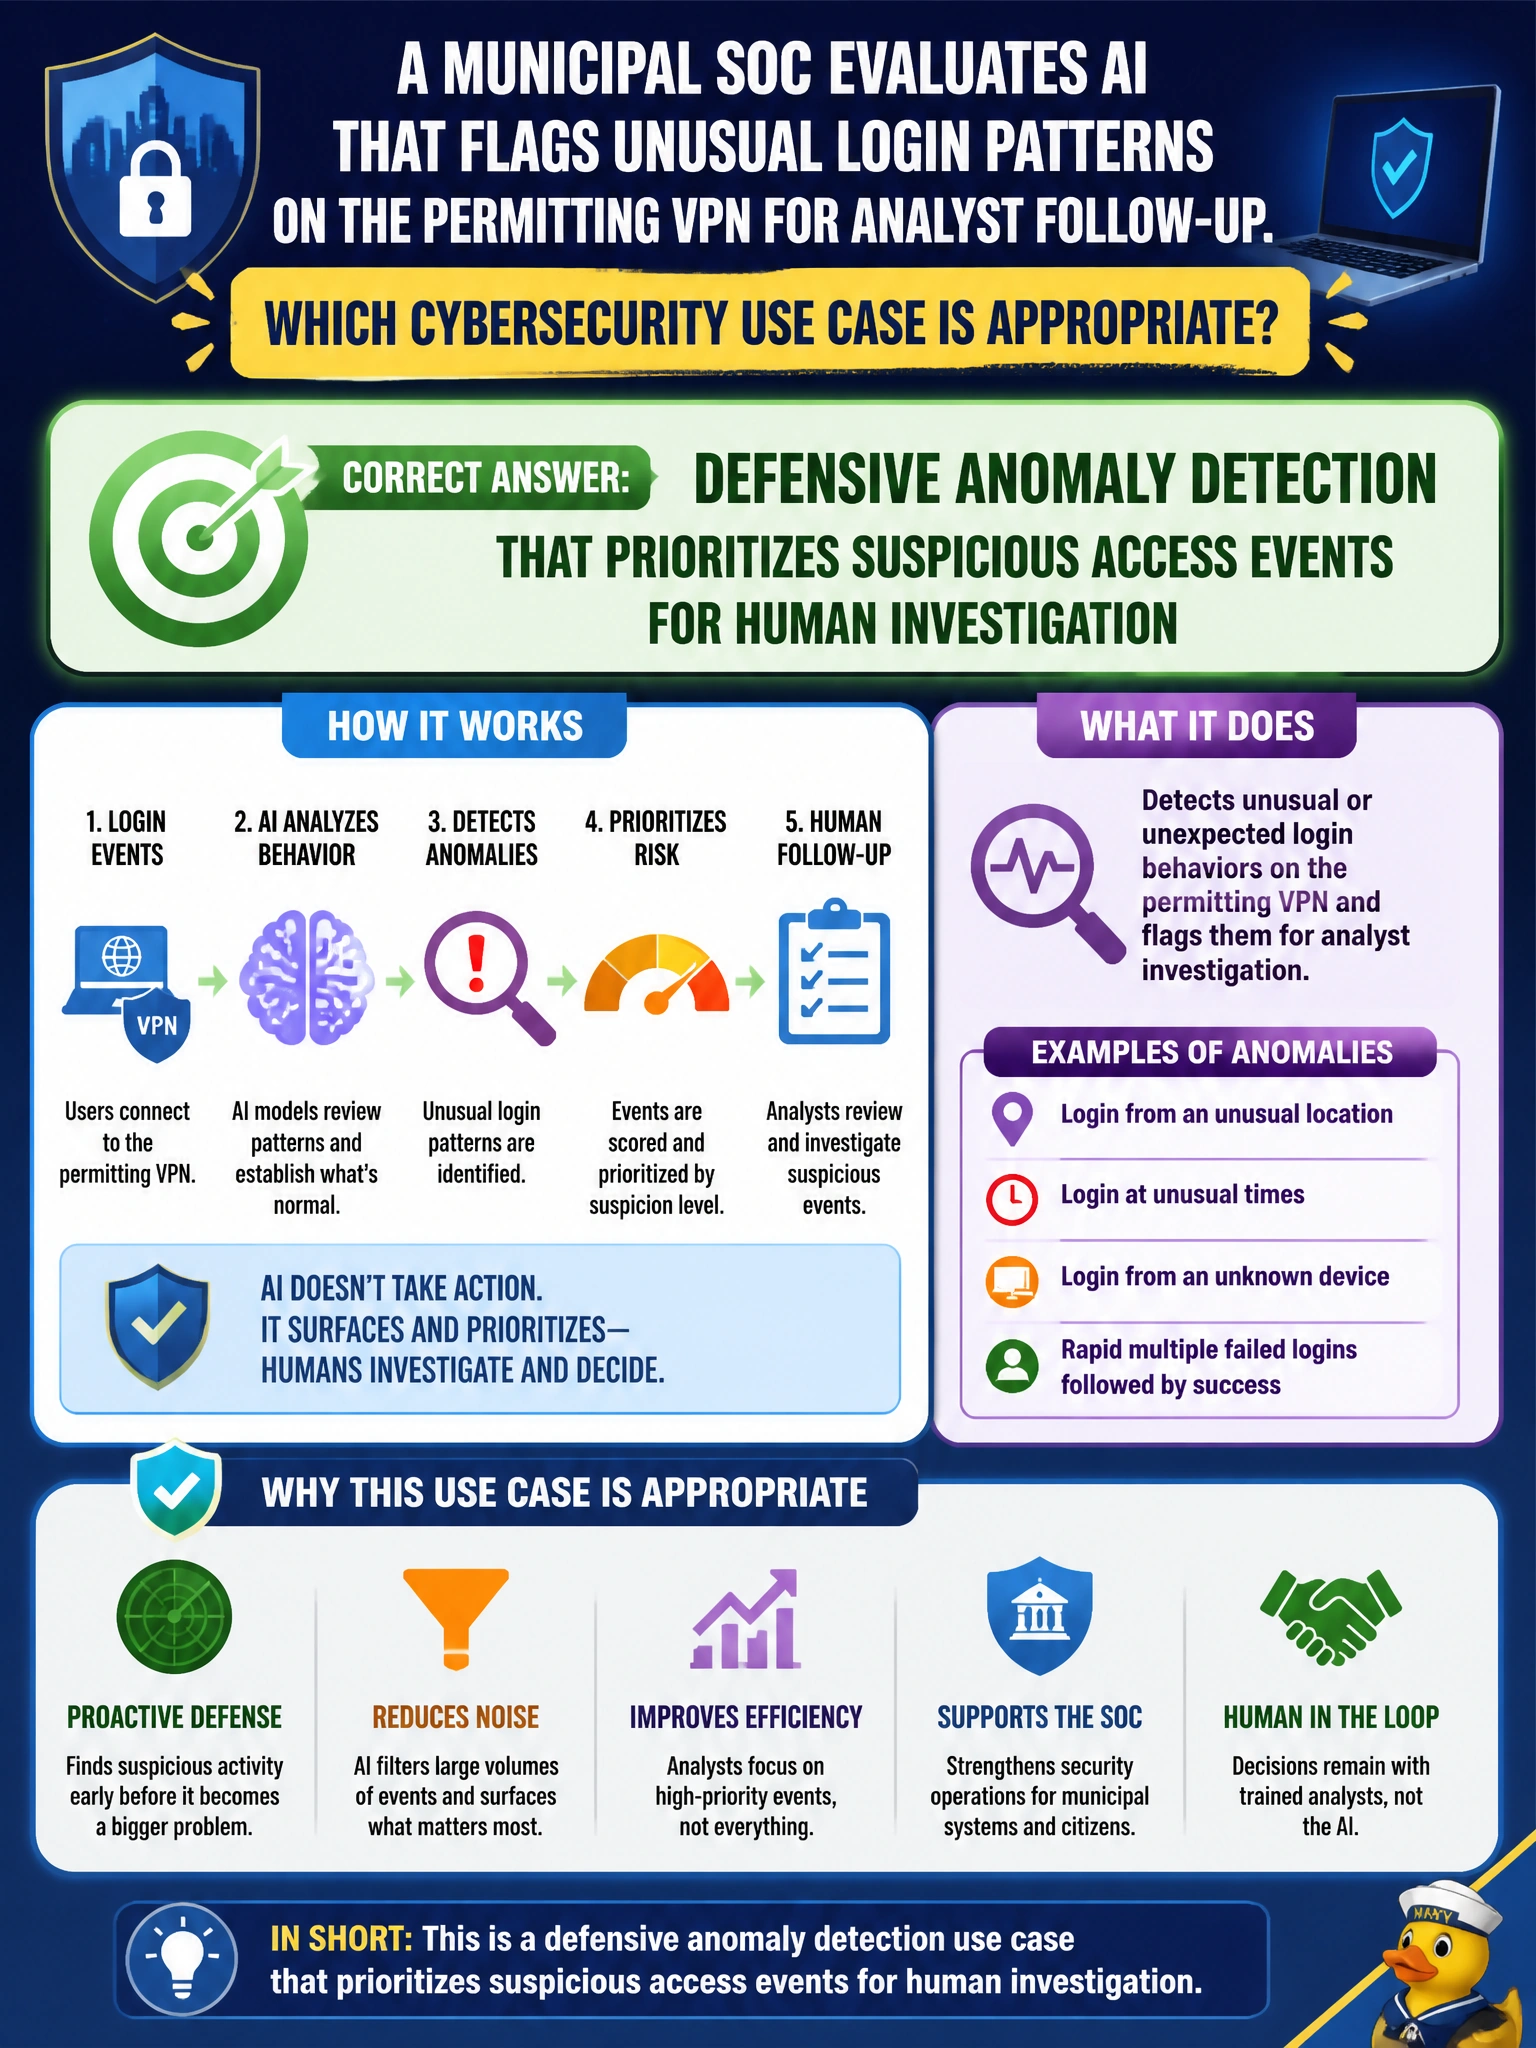
A municipal SOC evaluates AI that flags unusual login patterns on the permitting VPN for analyst follow-up. Which cybersecurity use case is appropriate?
Select an answer to reveal the explanation.
Short Explanation
Odd VPN logins are like a door sensor going off in the middle of the night—you'll have defensive AI wave the flag so analysts check the strange pattern because it's new, not because it matches a known login signature. You'll stay focused on login weirdness for analyst follow-up, so privilege-event tracking and exposed-service scans won't do the job.
Full Explanation
A municipal SOC evaluating AI that flags unusual login patterns on the permitting VPN for analyst follow-up needs defensive anomaly detection that prioritizes suspicious access events for human investigation. Behavioral or statistical models surface unusual times, locations, or sequences so analysts investigate before account takeover or data exposure expands. Essentials cybersecurity literacy for civic staff emphasizes defense and escalation, spotting novel unusual login behavior with anomaly models rather than matching known login signatures with signature detection. Defensive signature detection that prioritizes suspicious access events for human investigation looks for already-known patterns, not the novel unusual login timing or sequences that require anomaly detection for analyst follow-up. Defensive anomaly detection that prioritizes suspicious privilege events for human investigation targets unusual privilege grants or role changes, not the unusual VPN login timing or patterns the SOC needs flagged for analyst follow-up. Defensive vulnerability detection that prioritizes exposed access services for human investigation scans for exposed or misconfigured services, not the unusual VPN login timing or patterns the SOC needs flagged for analyst follow-up. Exam caveat: Appropriate cybersecurity AI use here is defensive anomaly detection with human investigation. Signature detection for suspicious access events and anomaly detection for privilege events are deliberate distractors. Operational check: Tune detections to reduce alert fatigue, require analyst disposition notes, integrate with identity and ticket systems, and ensure signature detection for suspicious access events does not replace anomaly triage for unusual logins.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.