
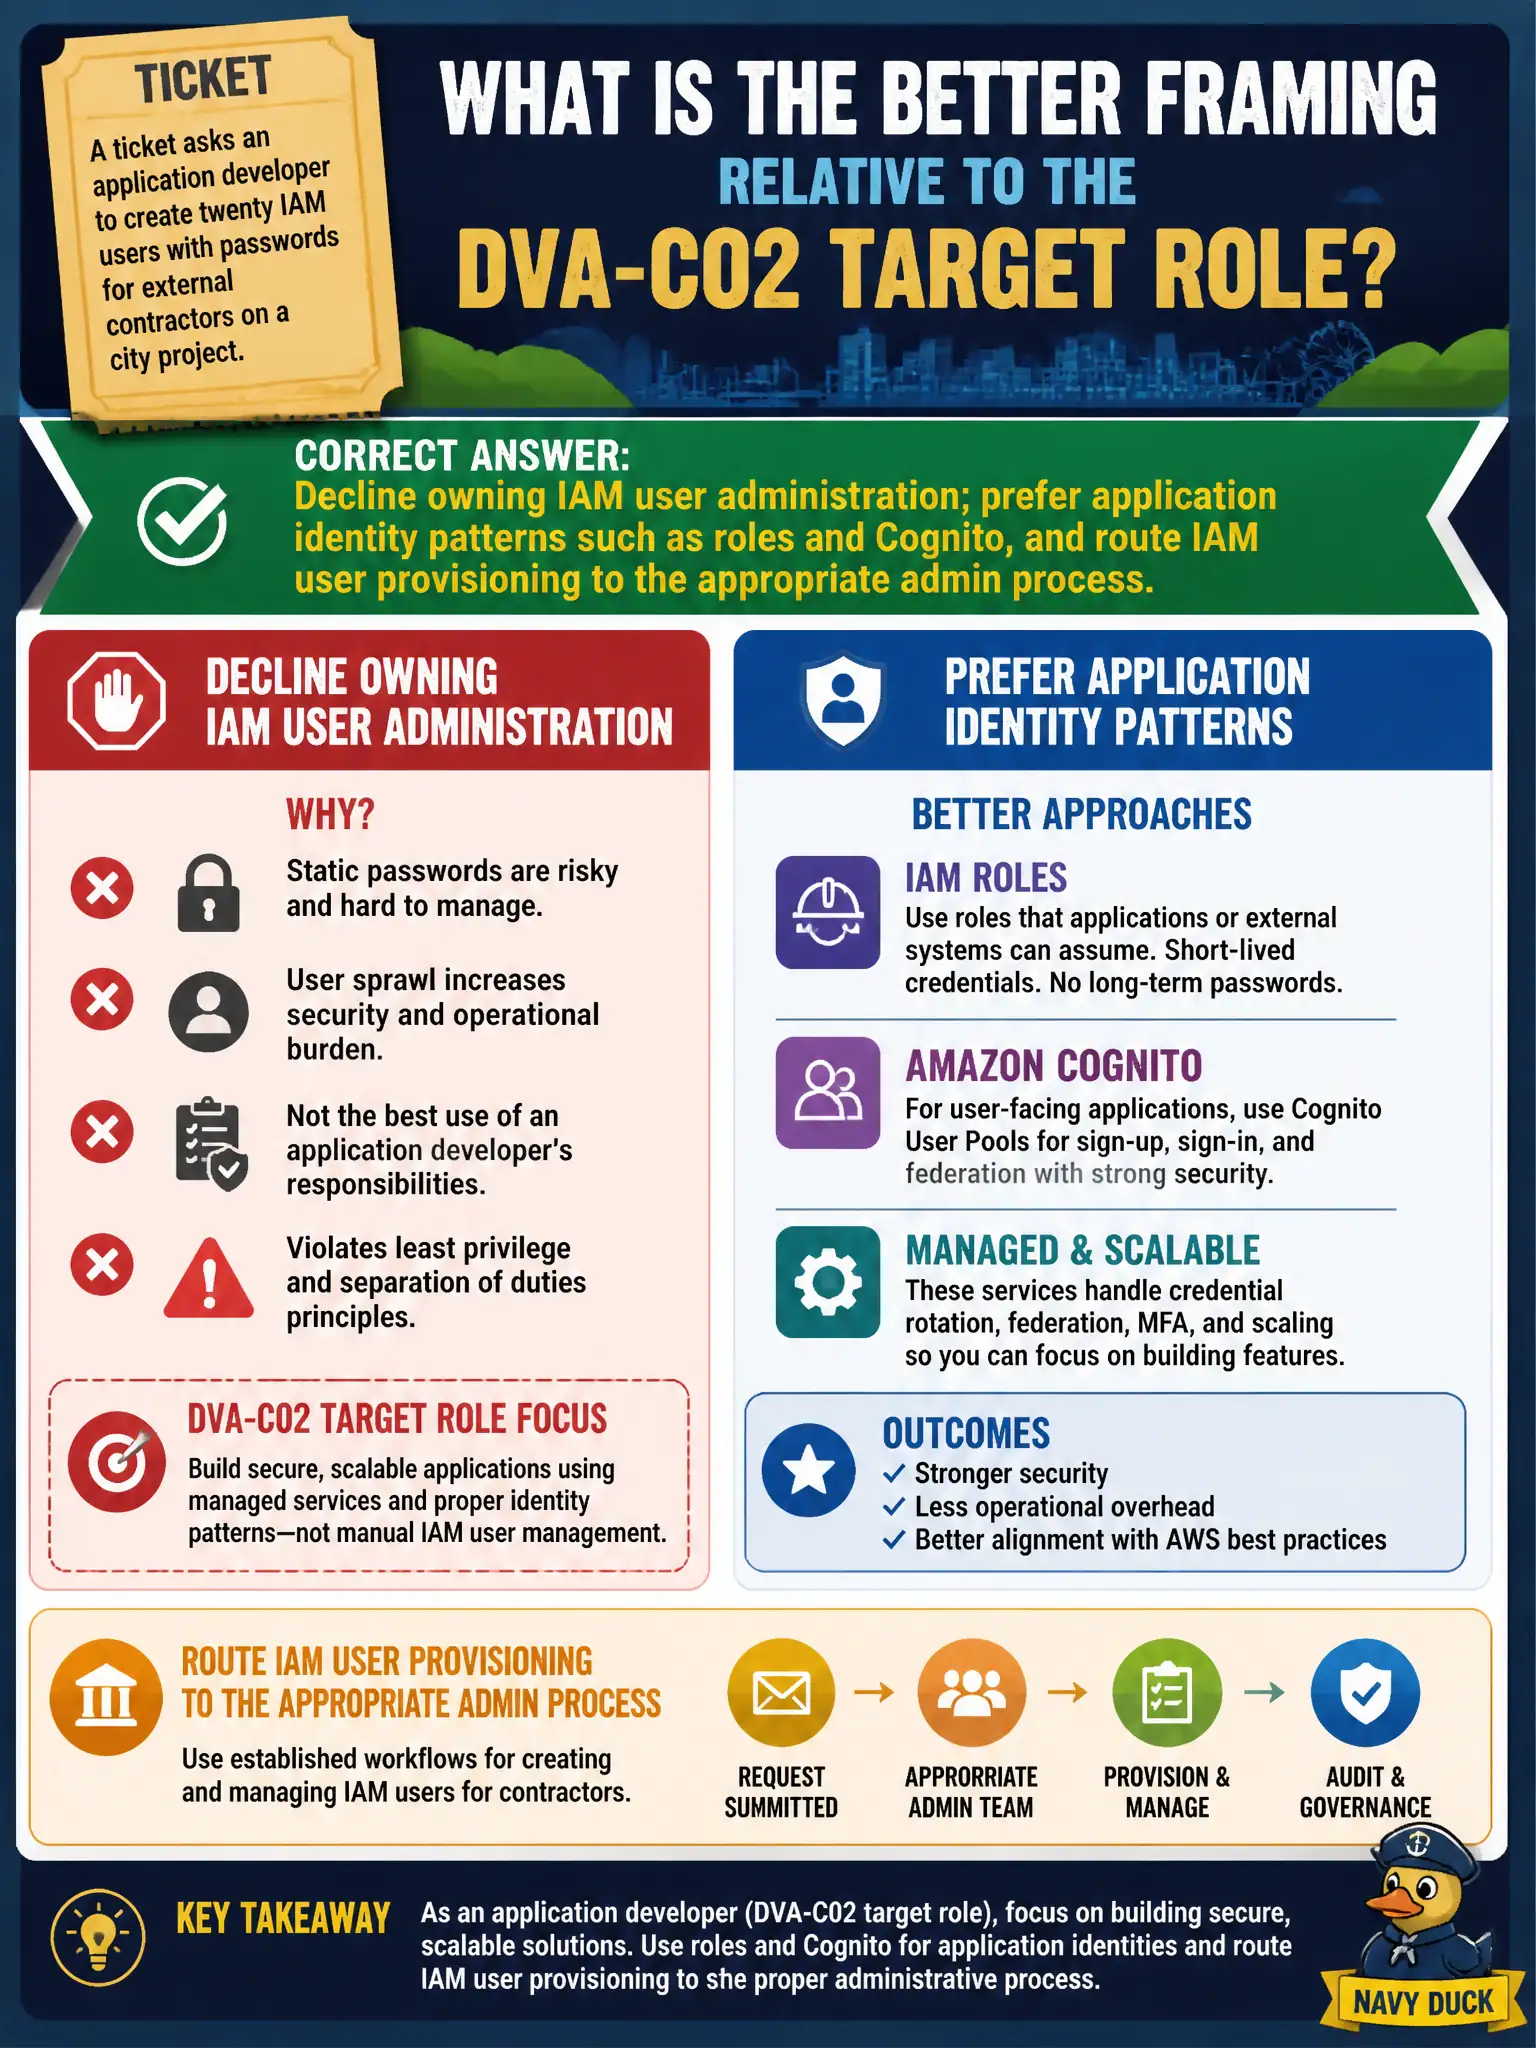
A ticket asks an application developer to create twenty IAM users with passwords for external contractors on a city project. Relative to the DVA-C02 target role, what is the better framing?
Select an answer to reveal the explanation.
Short Explanation
Making twenty IAM users with passwords is an admin help-desk job, not the developer Associate’s core lane. Point contractors at Cognito or roles for the app, and send the IAM-user ticket to the right owners. Shared passwords and root users are worse.
Full Explanation
Creating twenty IAM users with passwords for external contractors is workforce identity administration, not the typical DVA-C02 application-developer scope. Prefer application identity patterns—IAM roles for AWS access from compute, Cognito or partner federation for application users—and route IAM user provisioning to the appropriate cloud admin or enterprise identity process. Decline owning a ticket that asks developers to mint standing IAM users as a shortcut.
Creating the IAM users immediately because “application developers always own workforce IAM” misstates the target certification role. Sharing one IAM user password among twenty contractors destroys individual accountability and complicates revocation. Converting each contractor into an AWS account root user is absurdly privileged and operationally unmanageable.
Exam caveat: the exam often tests recognizing when a request is really IAM administration versus when Cognito, federation, or roles solve the application need. Operational check: propose Cognito federation or IAM Identity Center access for contractors, refuse shared passwords in tickets, and open the correct operations request only if policy truly mandates long-lived IAM users with named owners and MFA.