
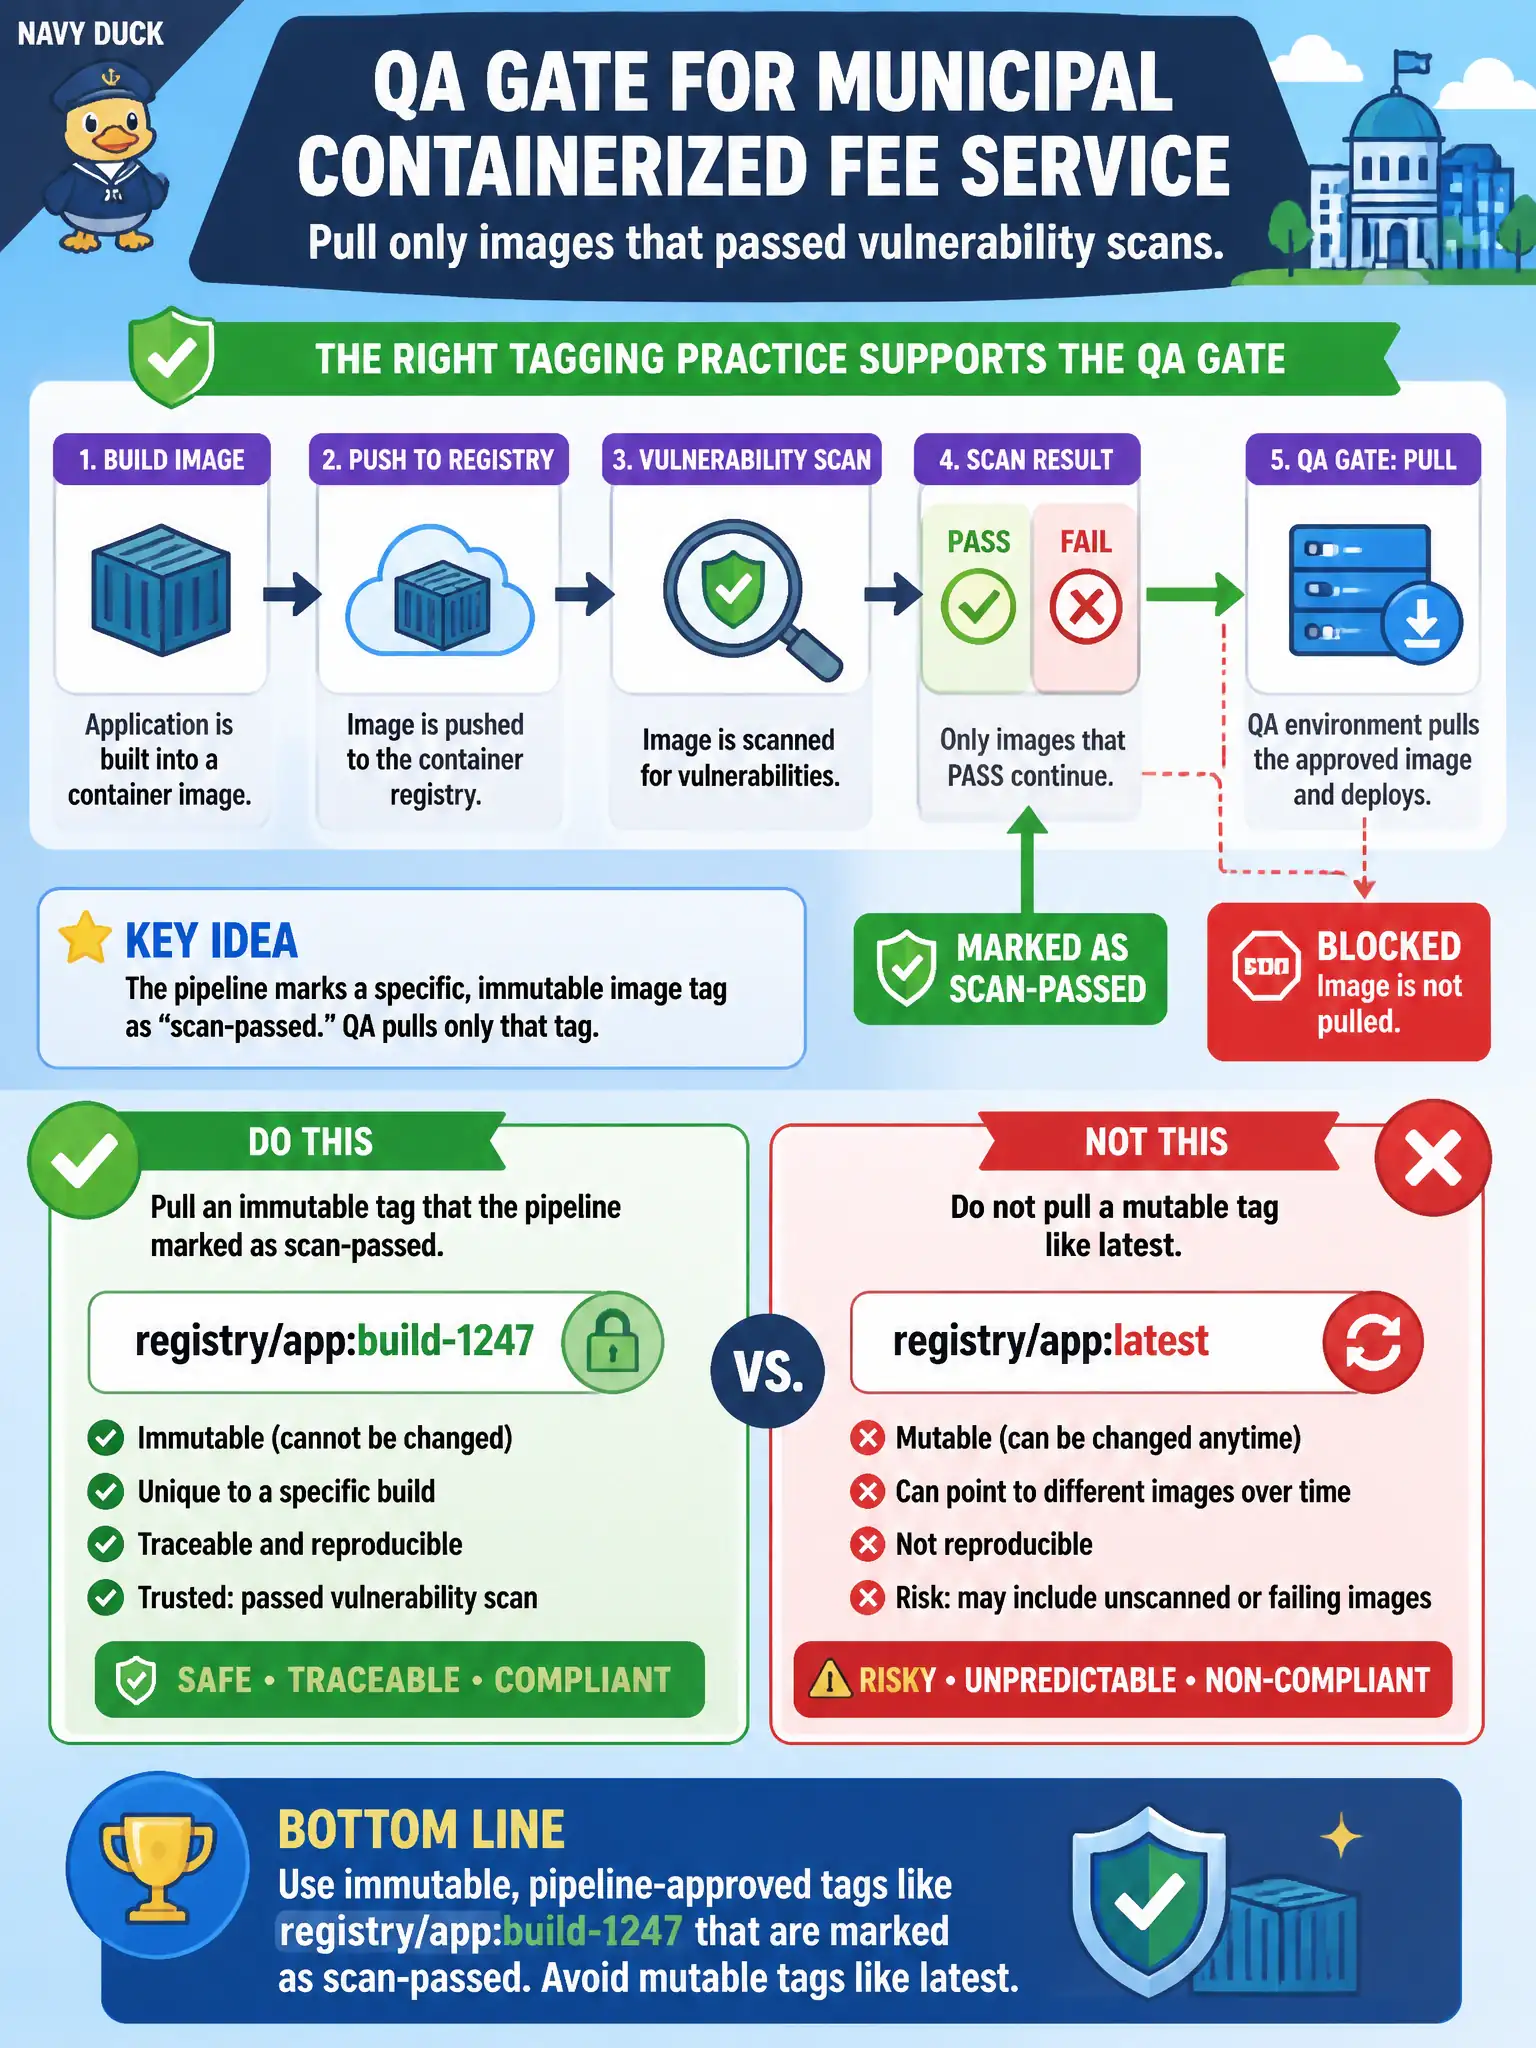
QA for a municipal containerized fee service must pull only images that passed vulnerability scans. Which tagging practice supports that gate?
Select an answer to reveal the explanation.
Short Explanation
Write the batch number on the jar—do not trust a sticker that just says “fresh.” Immutable build tags that passed scans are what QA should pull. Mutable latest keeps sliding under your feet.
Full Explanation
QA for a municipal containerized fee service must pull only images that passed vulnerability scans. Pull an immutable tag such as registry/app:build-1247 that the pipeline marked as scan-passed, not a mutable latest tag. Immutable, scan-gated tags create a chain of custody from build to QA for city fee containers and prevent "whatever finished building most recently" from slipping into staging unchecked.
Always deploying :latest so QA automatically receives whatever finished building most recently fails because latest is mutable and may point at an image that failed or never completed scanning. Retagging failed scan images as :qa so testers can still exercise them in staging fails conceptually by laundering known-vulnerable images into the QA path. Skipping image tags and copying layers by digest only after manual SSH onto build agents fails as an unauditable, non-pipeline practice.
Exam caveat: immutable tags must not be overwritten in the registry; if retagging is possible, prefer digest pins in the deploy manifest for the fee service. Operational check: confirm the pipeline promotes only scan-passed tags to the QA repository namespace, attempt to deploy a failed-scan image in a drill, and verify the gate blocks it.