
During a multi-day deployment, the management GUI remains logged in with the admin account on a shared jump host while the engineer steps away for the whole lunch break. What is the correct view of session hygiene for privileged management access?
Select an answer to reveal the explanation.
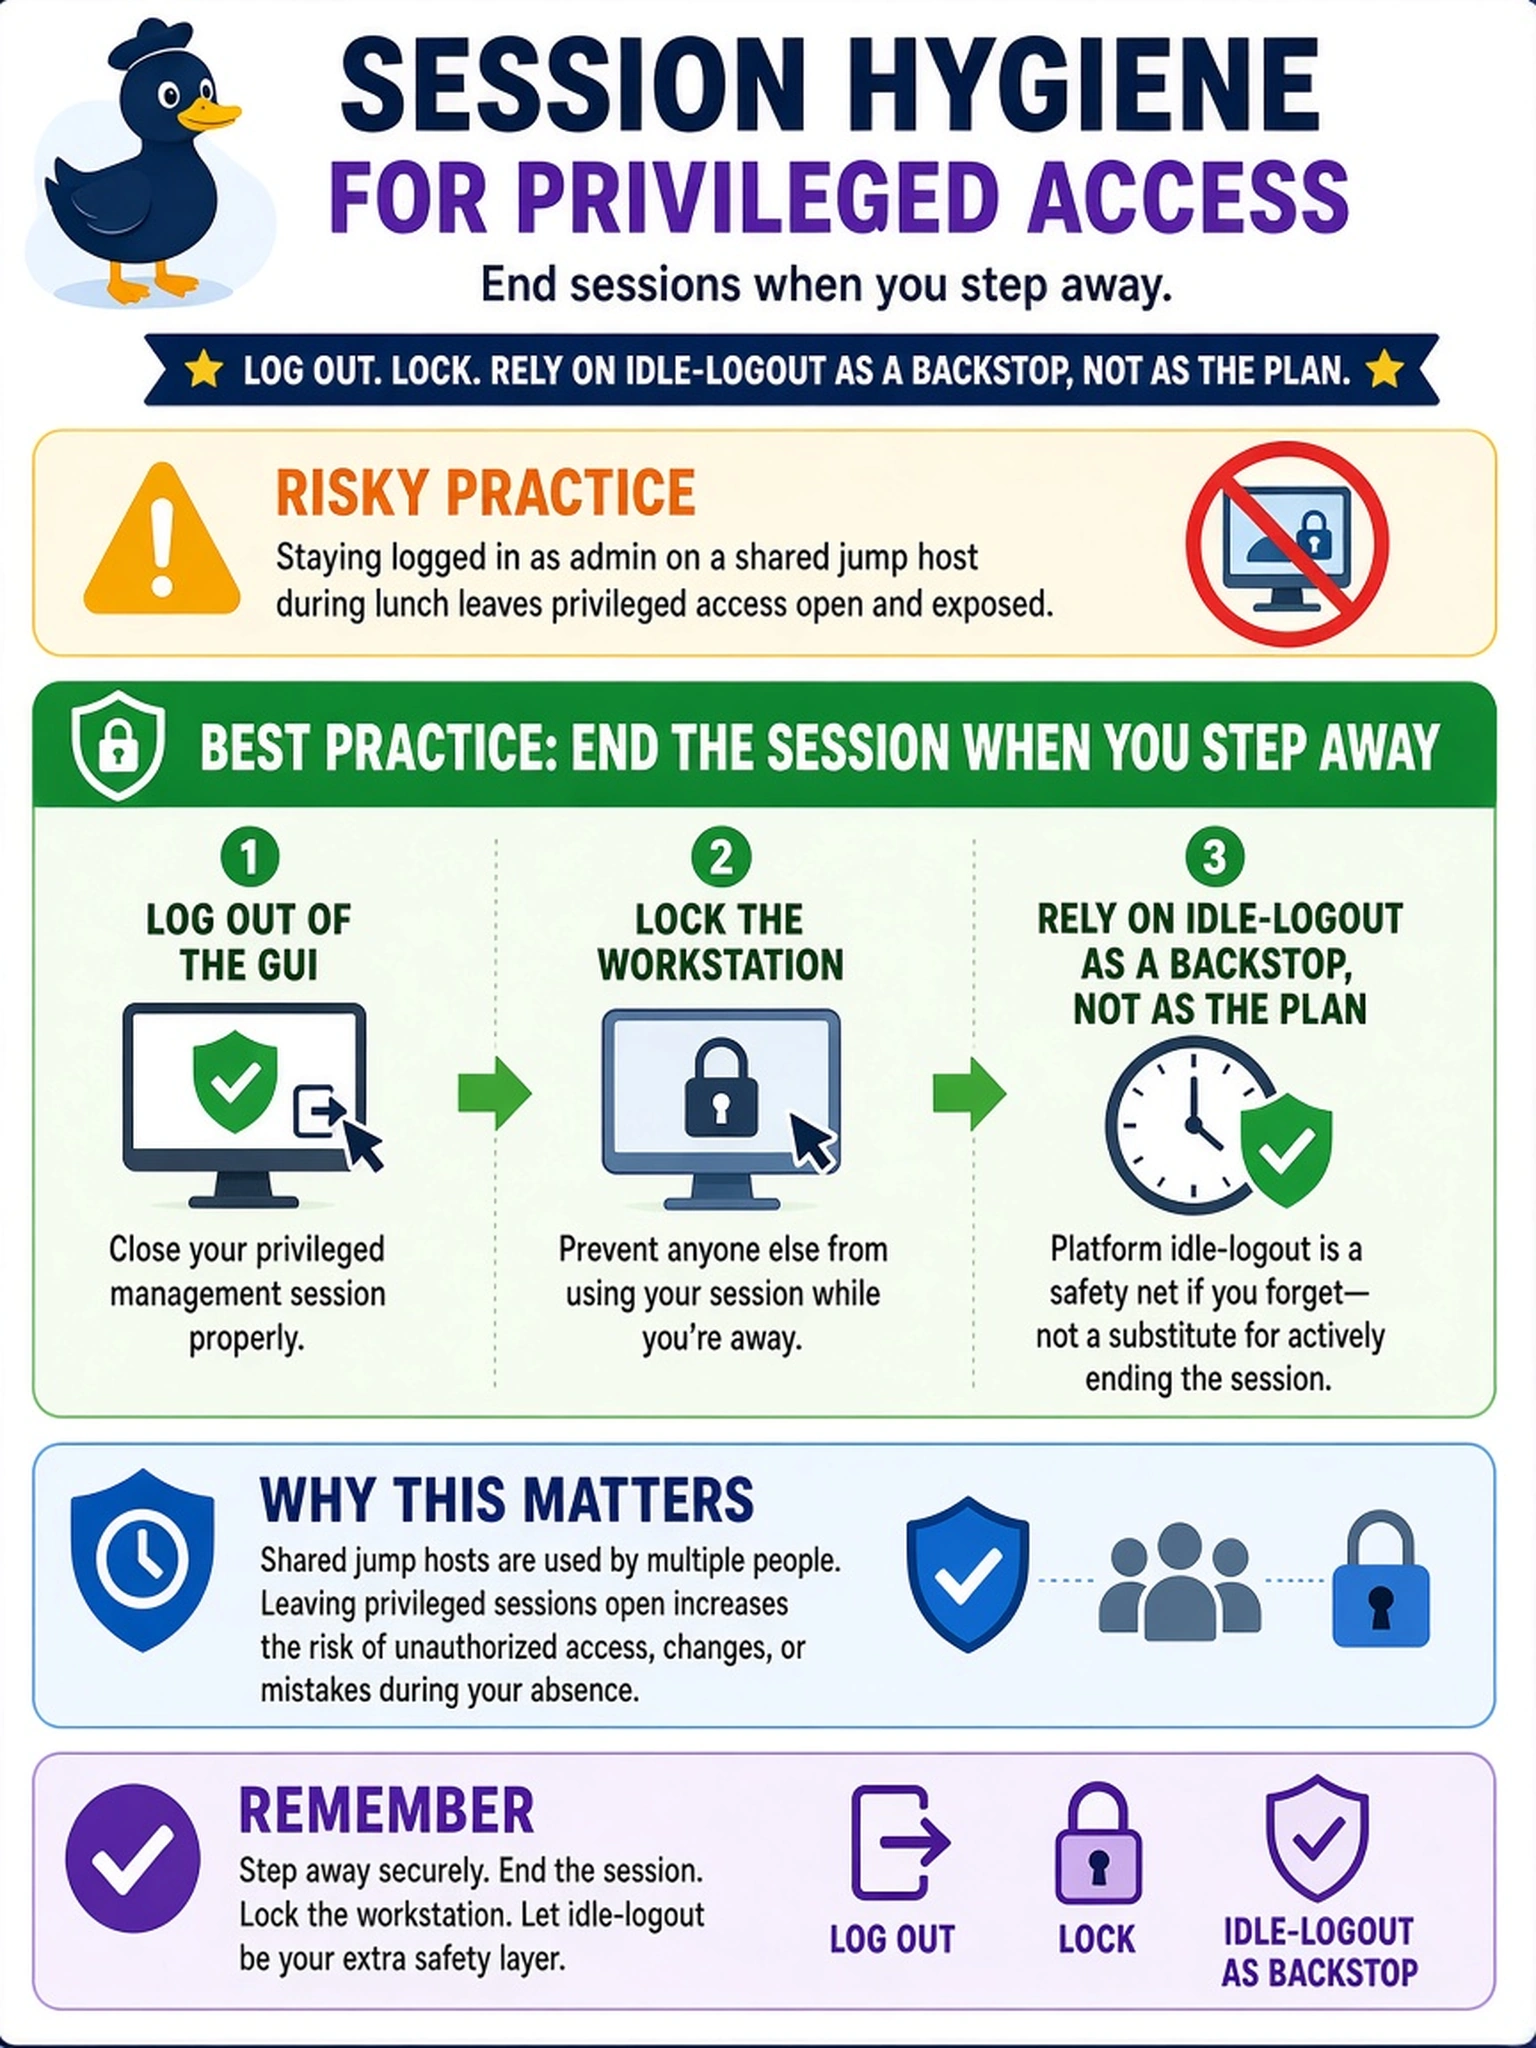
Short Explanation
An open admin session is a running car with the keys in the ignition — 'just grabbing lunch' is how every story about a hijacked session starts. The management network keeps strangers out, but an unlocked console hands your badge to whoever walks past. Log out when you step away, and lock that jump host.
Full Explanation
The correct view is that privileged sessions should be ended when you step away — log out of the GUI and lock the workstation, relying on the platform's idle-logout behavior as a backstop, not as the plan. Privileged management session is an authenticated path into the system holding the customer's backup estate, and that path is only as controlled as the human in front of it. The platform's idle timeout serves as a backstop rather than the plan, because a deployed but never-verified timeout is itself an assumption. The view that it is acceptable because the jump host is already inside the management network, so the main threat is network interception rather than someone using the logged-in admin GUI, fails by concept: a jump host inside the management network is precisely where an adversary with physical access or a passing keyboard wants to be, and VLAN membership controls reachability, not who is authenticated at the console. The view that it is acceptable because a management VLAN authenticates everyone on it by placement alone, so an open admin session inside that supposedly trusted segment grants nobody anything that the machine's location has not already implicitly authorized, fails for the same reason — segmentation is not identity. The view that it is acceptable if the idle browser is switched to a read-only account, because dropping to a lesser identity after the fact converts the open admin session into a safe one, is wrong because switching an already-open admin browser to a read-only account does not undo the elevated session that exists until it times out or is logged out; least privilege is broken the moment the session started and is not repaired by what you click afterward. Exam caveat: idle-timeout behavior is a platform and browser setting worth confirming during deployment, since long or zero defaults silently defeat the backstop. Operational check: verify the management GUI's session idle-logout behavior, use the jump host's lock policy, and make logout the last keystroke of every work session.