
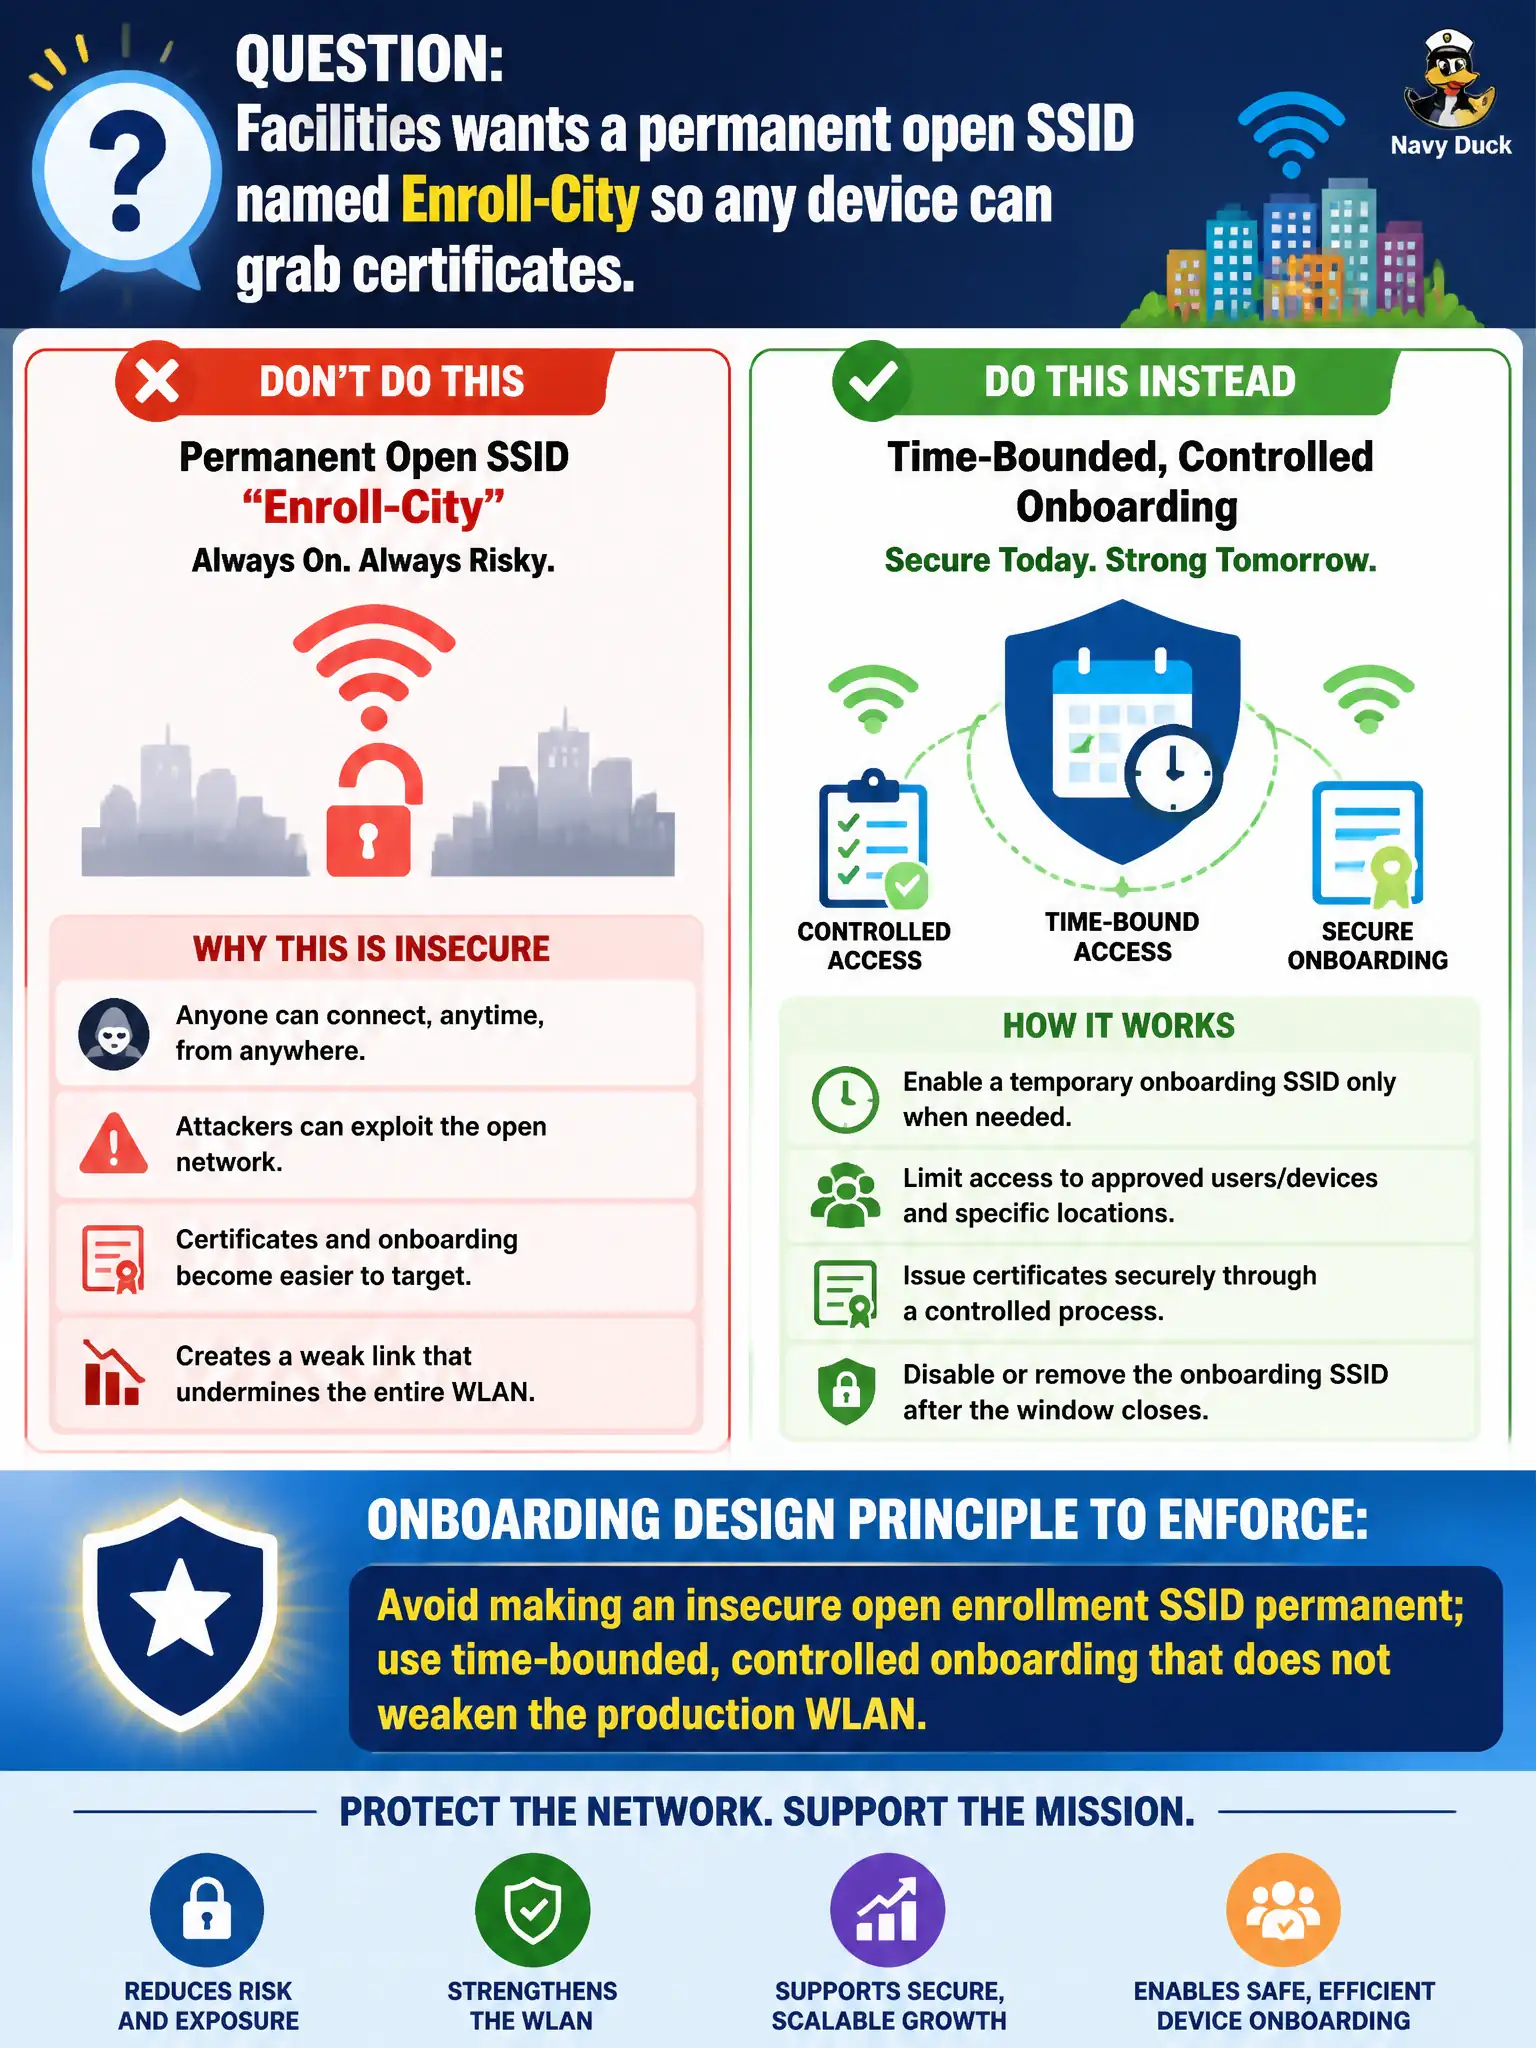
Facilities wants a permanent open SSID named Enroll-City so any device can grab certificates. What onboarding design principle should security enforce instead?
Select an answer to reveal the explanation.
Short Explanation
A forever-open Enroll-City SSID is like leaving the loading dock unlocked because someone might need a badge later. Controlled, short-lived onboarding beats a permanent soft underbelly next to production. Parking finance on that dock is worse.
Full Explanation
Facilities requesting a permanent open SSID named Enroll-City for any device to obtain certificates must be guided by the security principle of avoiding insecure open enrollment SSIDs as permanent fixtures. Instead, onboarding should be time-bounded and controlled, ensuring that temporary open networks do not weaken the security posture of the production WLAN. Permanent open SSIDs expose the network to unauthorized access and attacks, as they lack encryption and authentication. Keeping the open enrollment SSID forever and placing sensitive finance servers on it is a critical security risk, exposing sensitive resources to anyone connecting to the open network. Broadcasting the same open SSID outdoors with maximum power invites uncontrolled device enrollment and potential attackers, further degrading security. Disabling all encryption on staff SSIDs until enrollment completes removes essential protections and increases risk. The scope of this principle applies to municipal networks where device onboarding must balance ease of use with security. Operationally, confirm that enrollment SSIDs are temporary, isolated from production resources, and disabled after onboarding periods, maintaining a secure WLAN environment.