
A municipal WLAN policy lists only the CISO as owner; network operations never receives updates. Which stakeholder gap should be fixed?
Select an answer to reveal the explanation.
Short Explanation
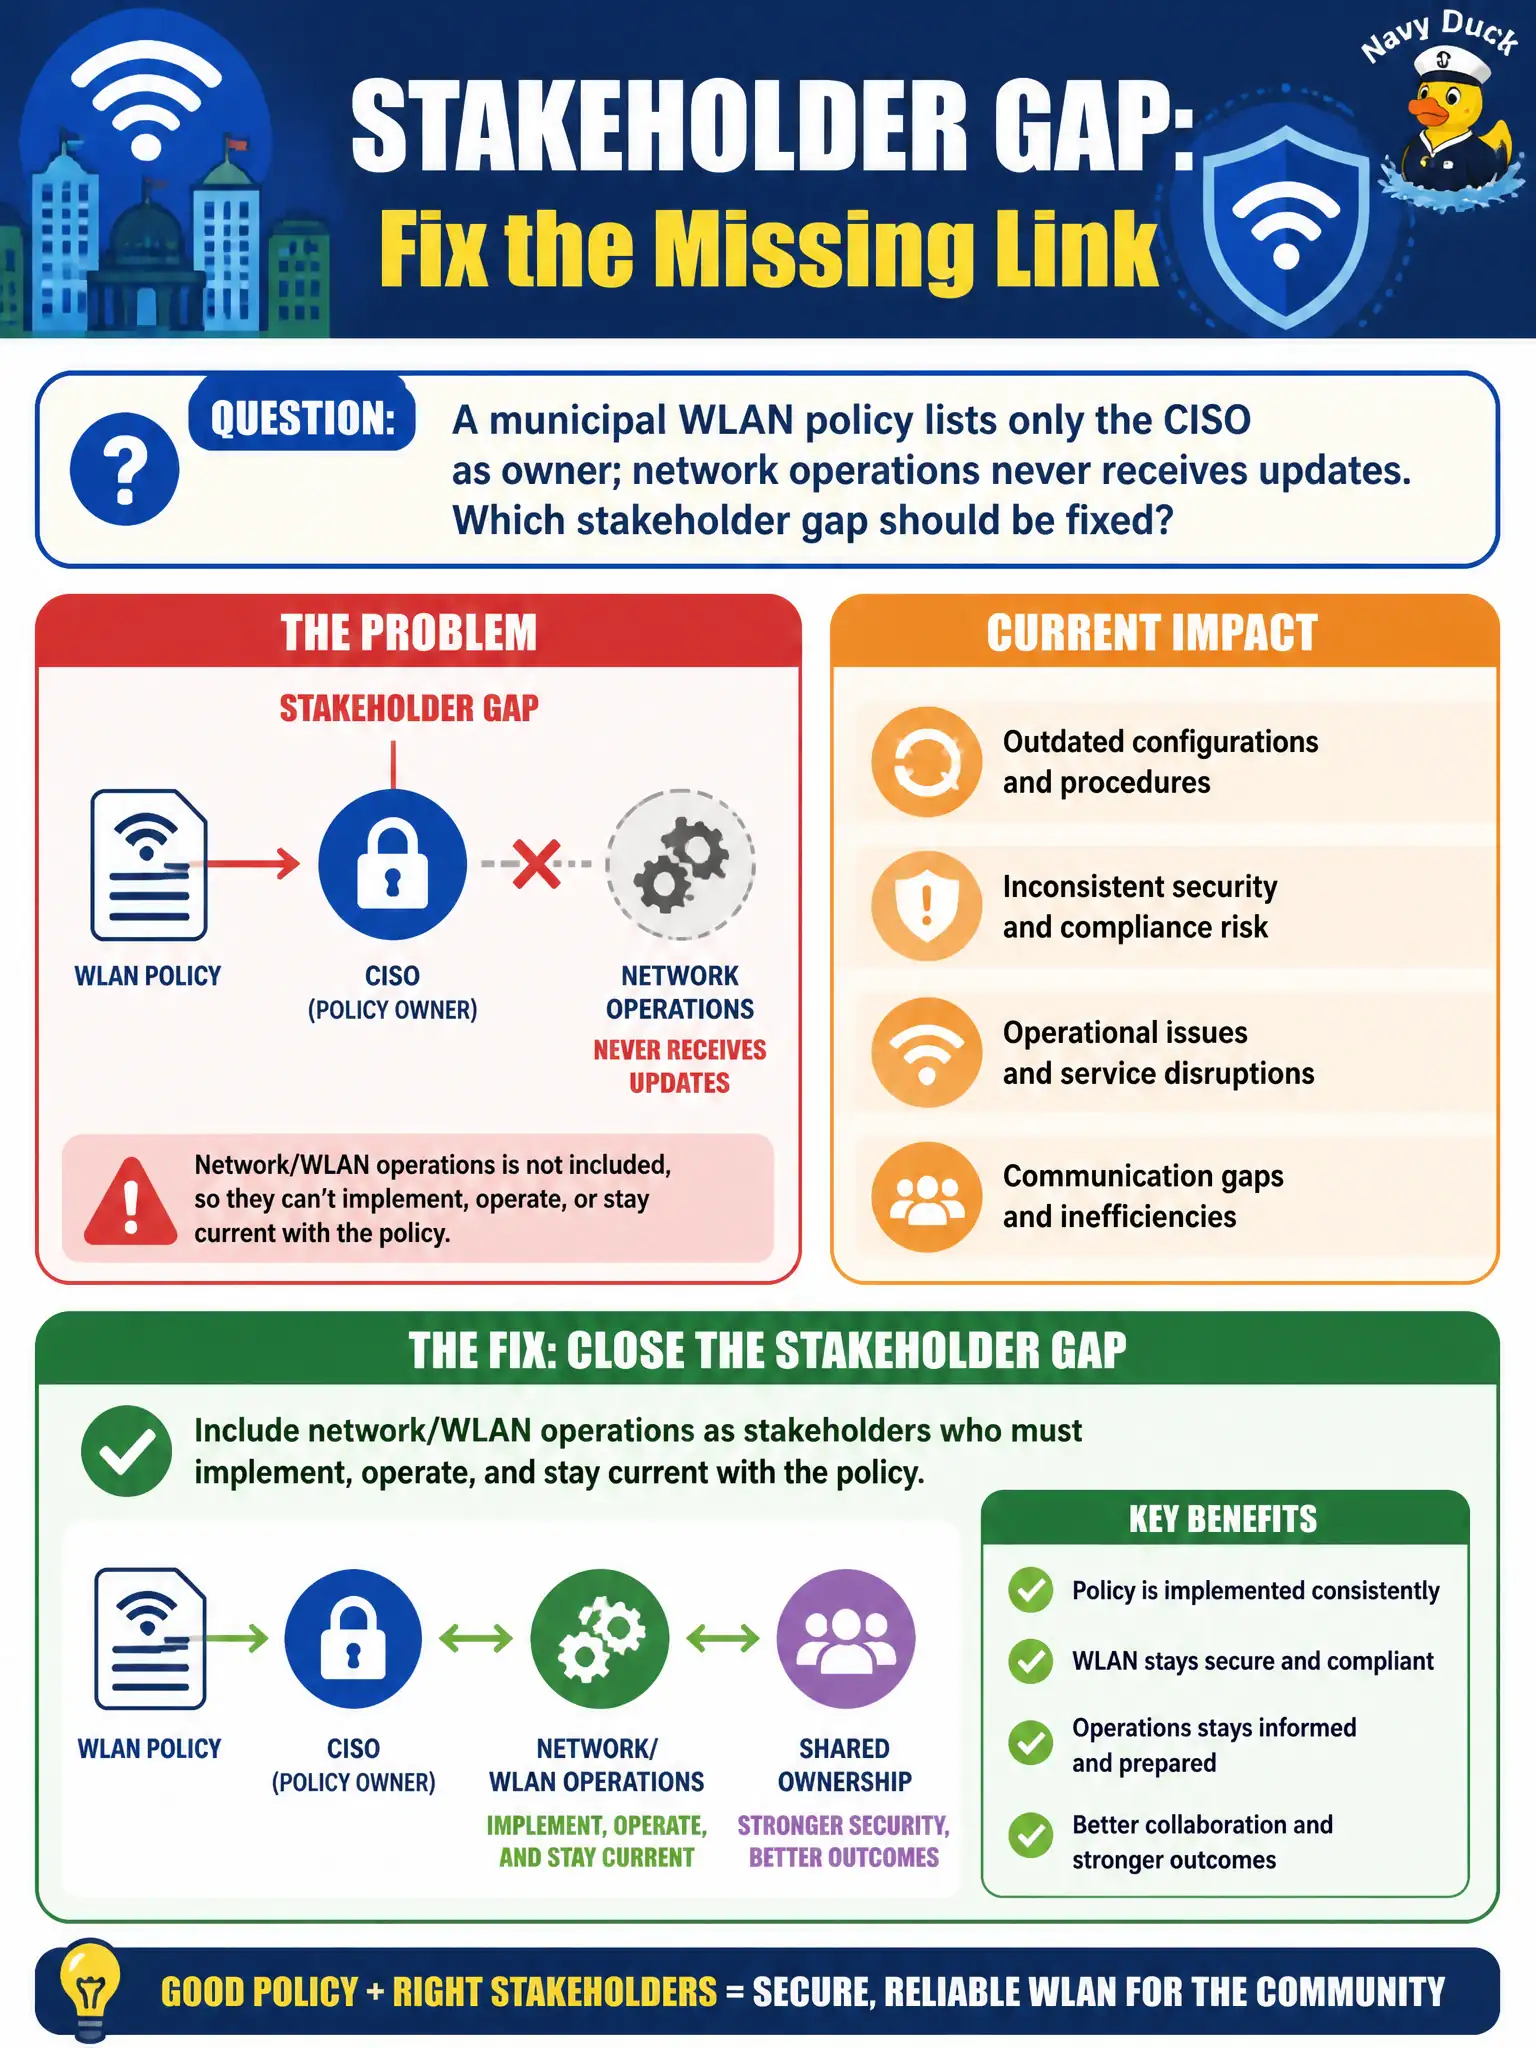
If ops never sees the policy, the radios won't match the paperwork. Put WLAN operations on the stakeholder list so the people who type the configs get the updates.
Full Explanation
When a municipal WLAN policy lists only the CISO as owner and network operations never receives updates, the stakeholder gap to fix is inclusion of network and WLAN operations as stakeholders who must implement, operate, and stay current with the policy. Security ownership without an implementing audience produces shelfware: SSID templates, exception handling, and monitoring stay misaligned with the written controls. Adding only external marketing agencies as sole implementers mismatches skills and accountability for infrastructure security. Removing all owners so nobody is accountable guarantees drift. Replacing operations with anonymous internet commenters destroys chain of responsibility. A healthy model keeps security as policy owner while operations is a required implementing stakeholder on distribution, change control, and exception review. Exam caveat: RACI may assign Accountable to security leadership and Responsible to WLAN operations; both boxes must be filled. Operational check: add WLAN operations to the policy distribution list and RACI, require acknowledgment of updates, include operations in exception boards, and periodically verify controller SSID templates and admin practices match the current approved policy version.