
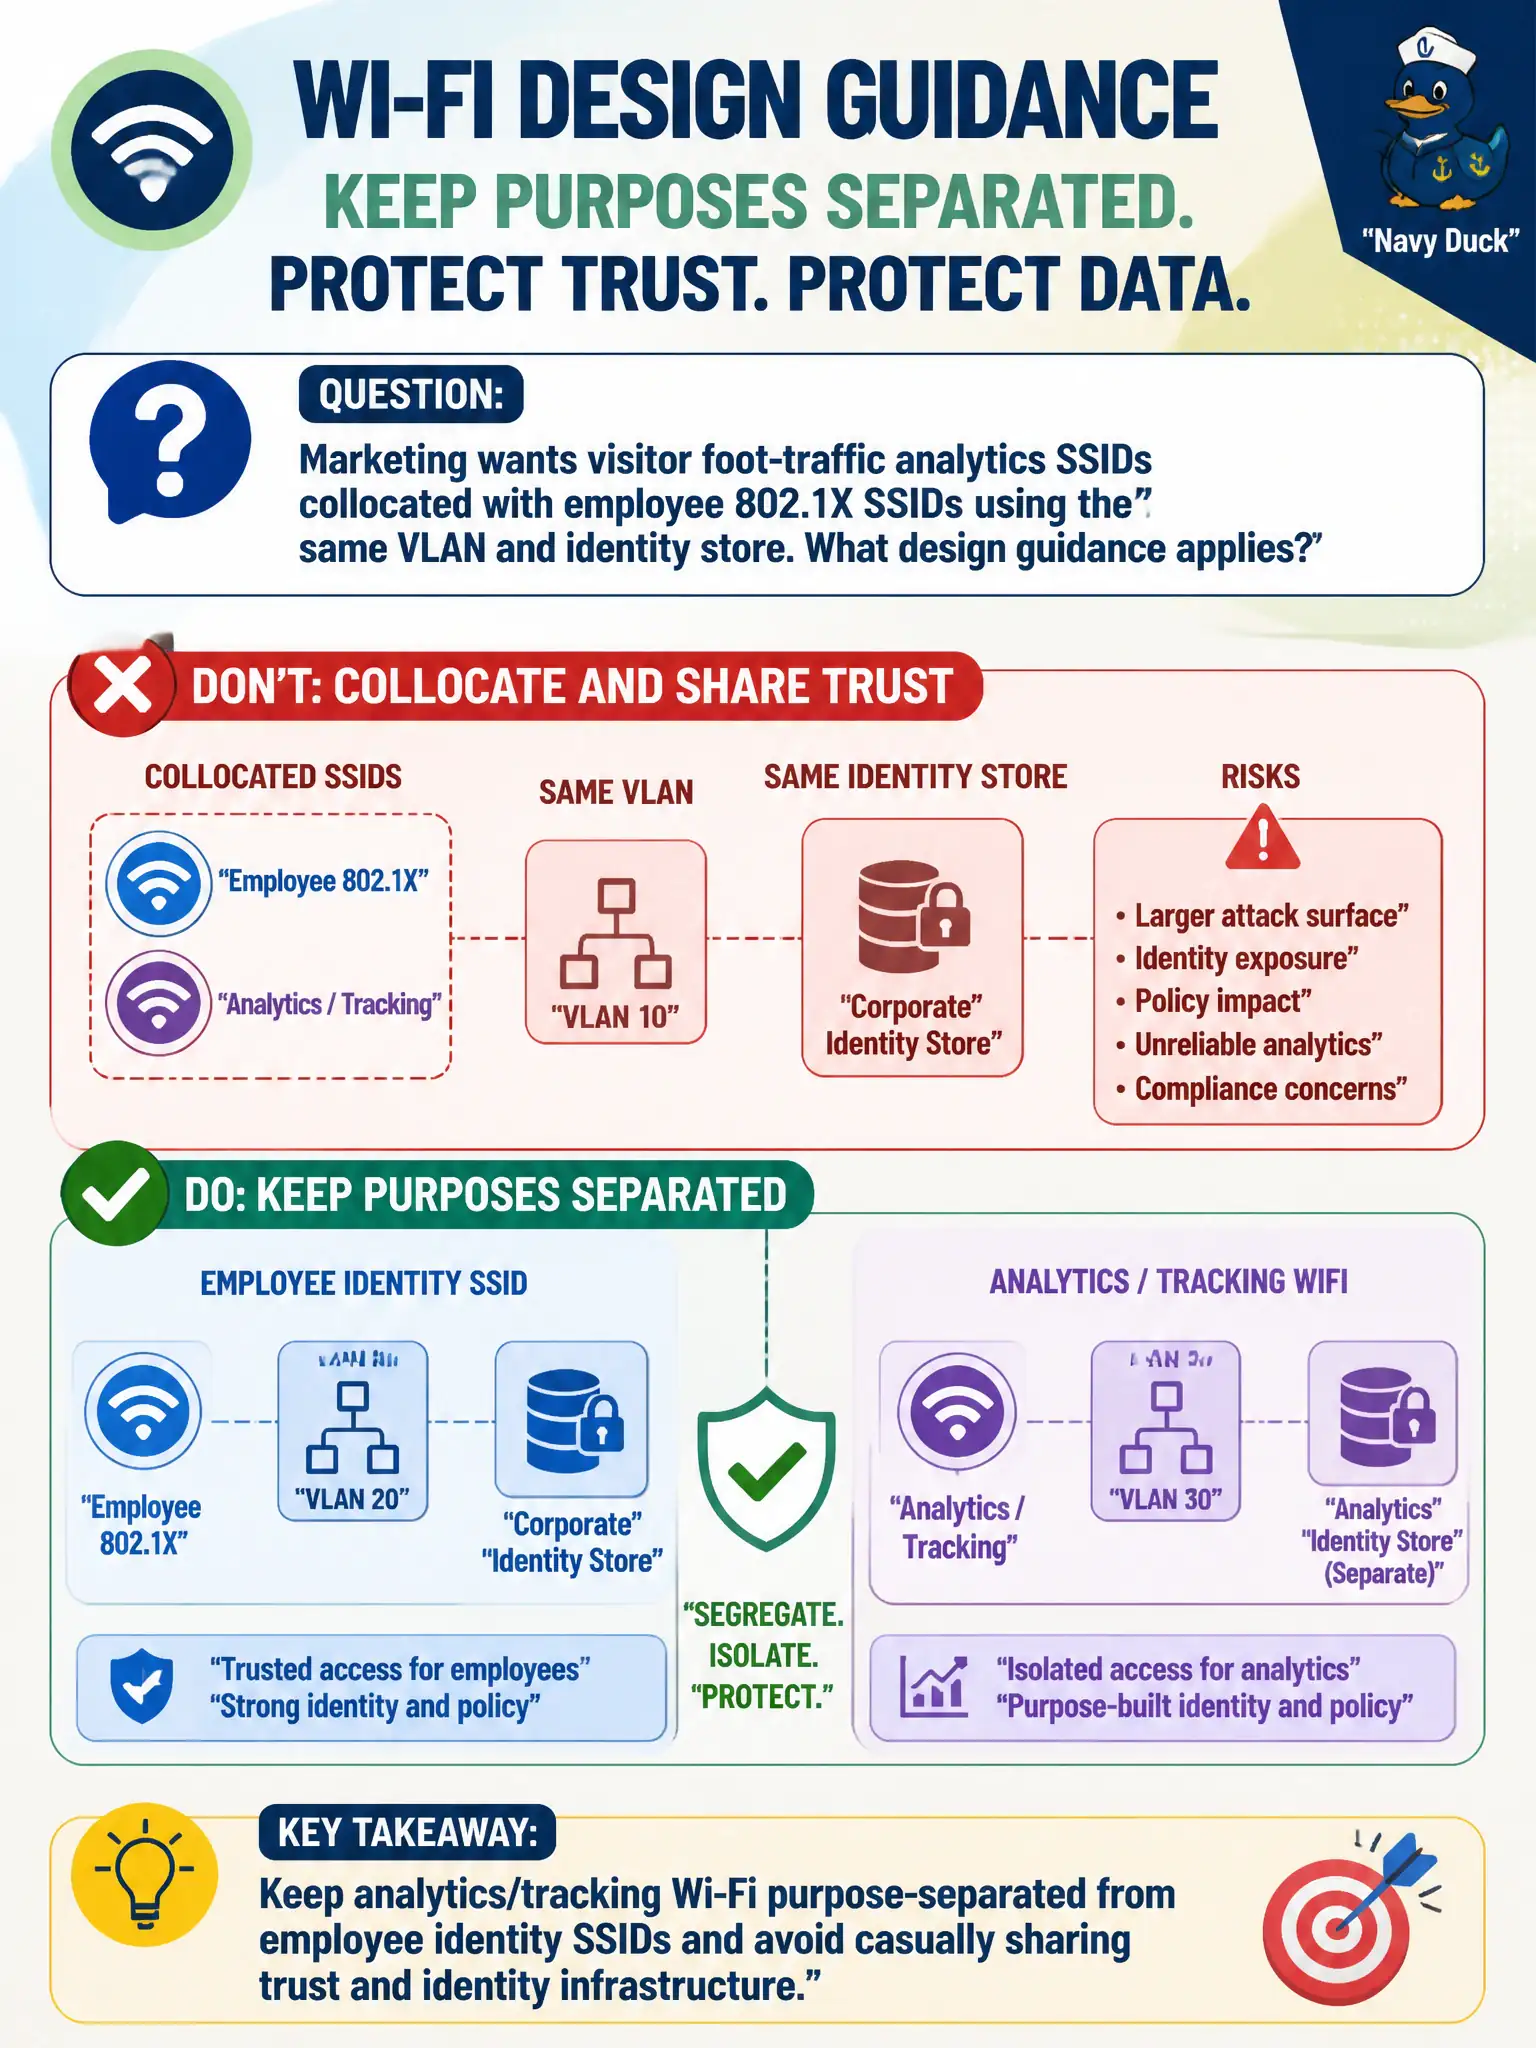
Marketing wants visitor foot-traffic analytics SSIDs collocated with employee 802.1X SSIDs using the same VLAN and identity store. What design guidance applies?
Select an answer to reveal the explanation.
Short Explanation
Foot-traffic Wi-Fi and employee identity Wi-Fi are different animals—keep their trust domains apart. Mixing analytics open junk with 802.1X staff SSIDs is how purpose creep becomes a breach story.
Full Explanation
Marketing wanting visitor foot-traffic analytics SSIDs collocated with employee 802.1X SSIDs using the same VLAN and identity store should be refused on purpose-separation grounds: keep analytics/tracking Wi-Fi purpose-separated from employee identity SSIDs and avoid casually sharing trust and identity infrastructure. Analytics goals do not justify blending probe/visitor collection paths with staff AAA. Civic privacy and security both suffer when marketing Wi-Fi piggybacks on employee identity systems.
Merging analytics probes into the domain-admin SSID to enrich SIEM user records contaminates a privileged network. Forcing employees to join the analytics open SSID for accurate badge correlation weakens staff security. Disabling encryption on employee SSIDs so analytics vendors can decode 802.1X inner identities is an egregious confidentiality failure.
Exam caveat: even separated analytics Wi-Fi may trigger privacy policy and retention rules—coordinate with counsel. Operational check: place analytics on its own SSID/VLAN without employee IdP coupling, confirm no route into staff identity stores, and document data retention for probe/analytics telemetry. In municipal WLAN programs, capture the decision in the wireless standard and re-check it at change review so the next project inherits the same control bar instead of rediscovering the failure during an outage.