
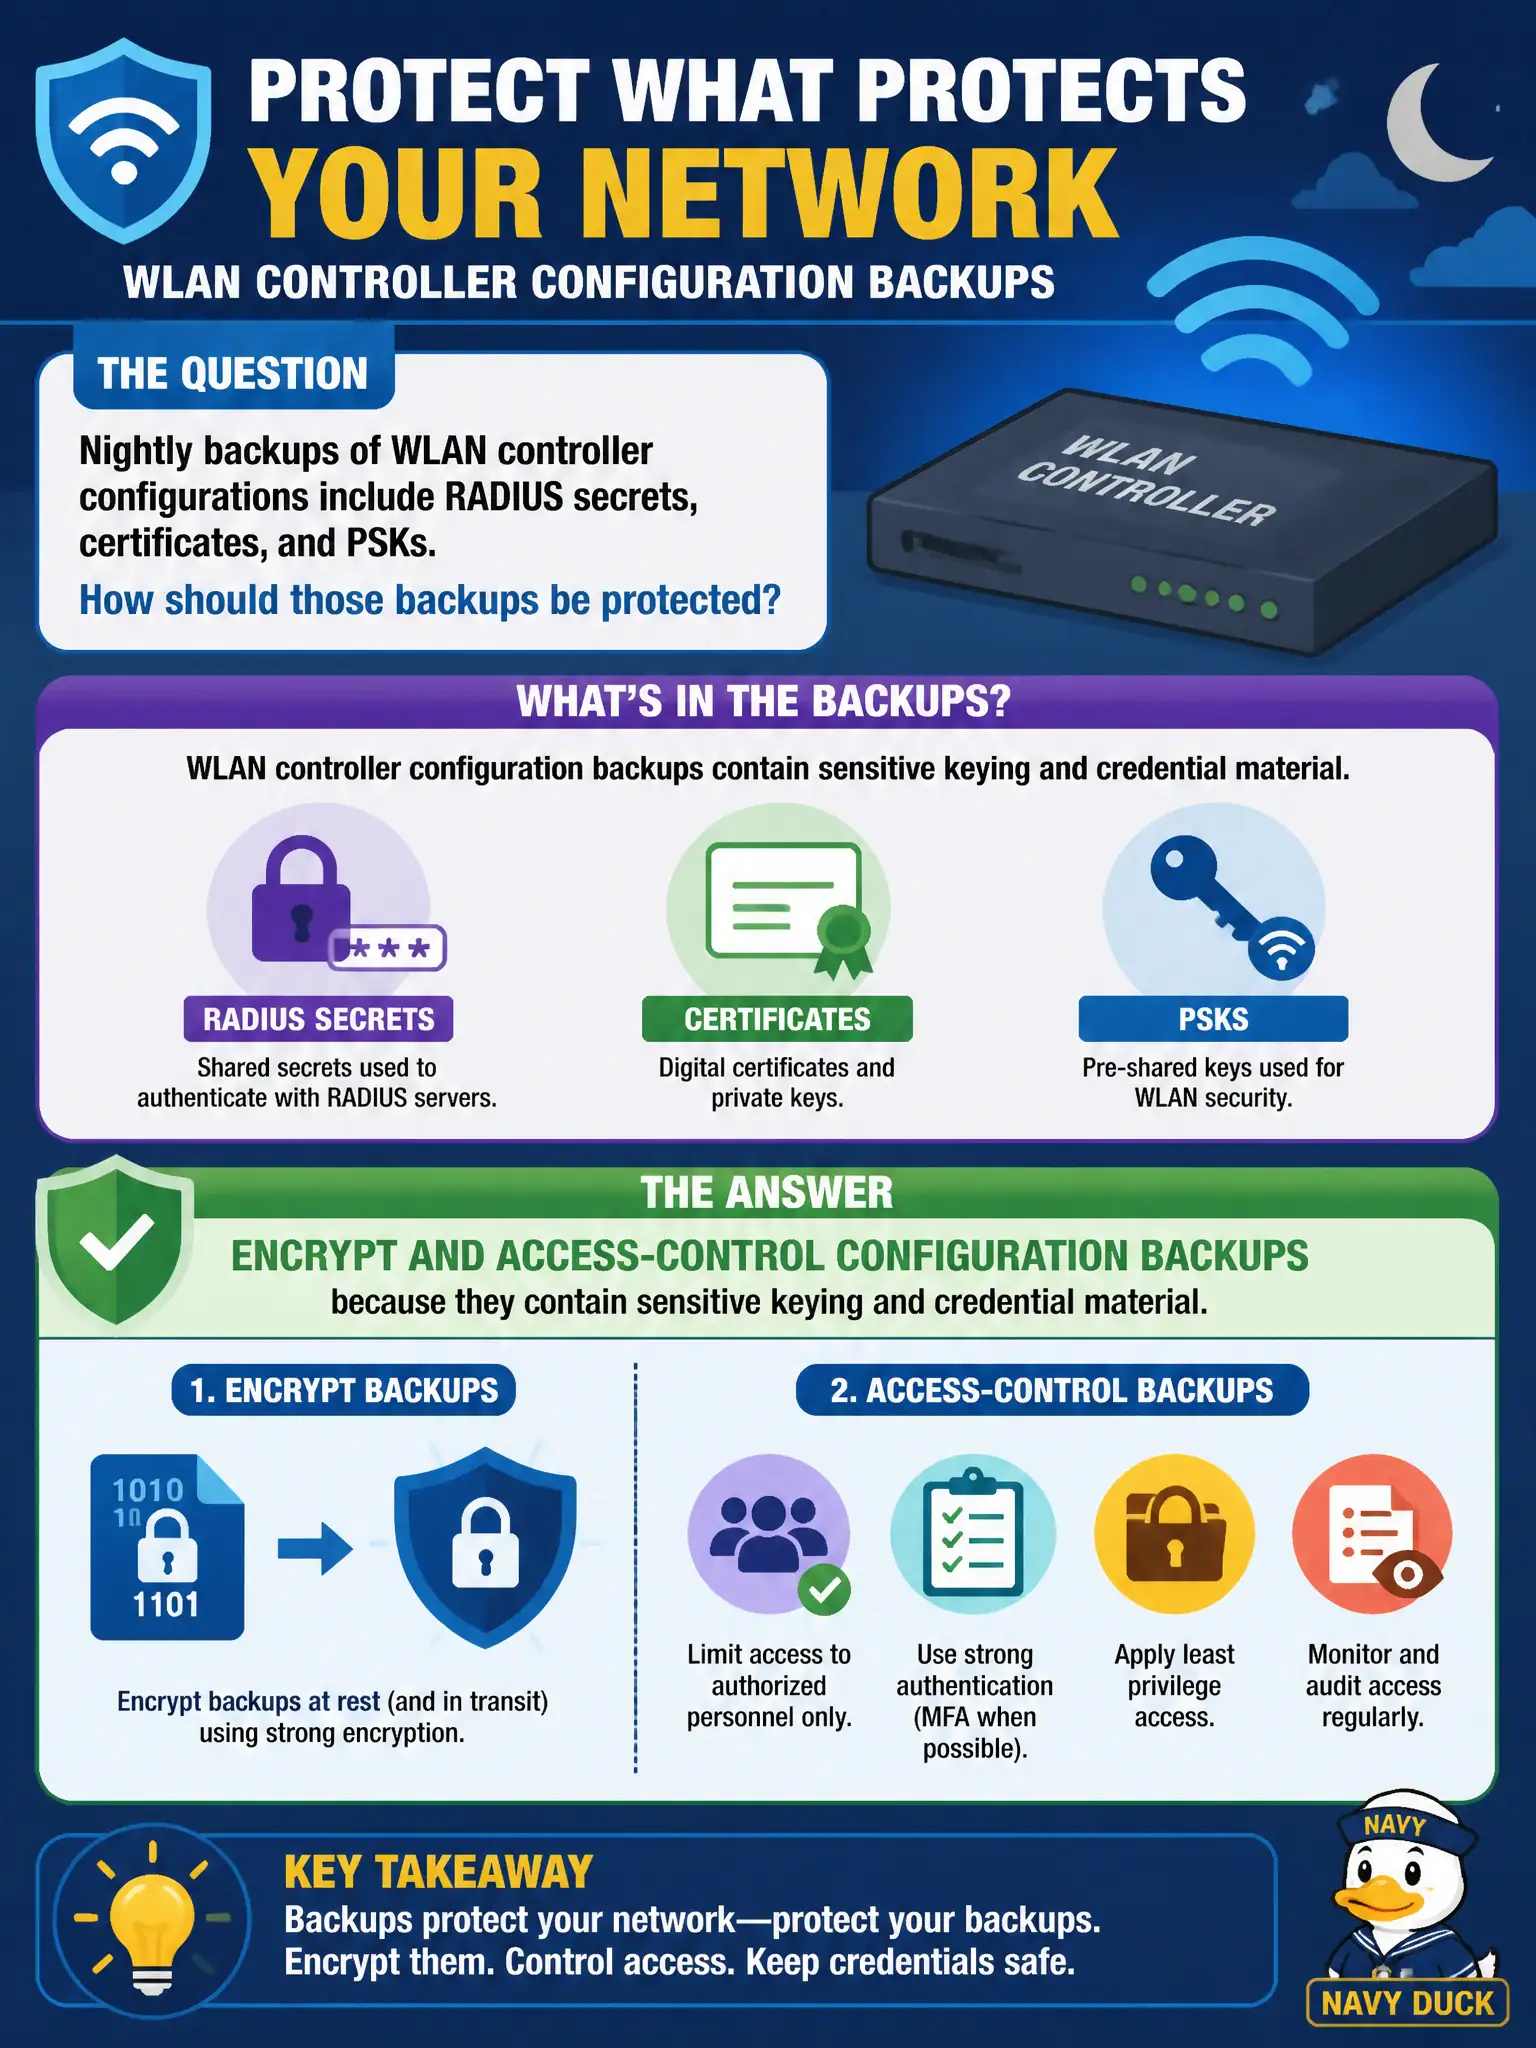
Nightly backups of WLAN controller configurations include RADIUS secrets, certificates, and PSKs. How should those backups be protected?
Select an answer to reveal the explanation.
Short Explanation
Controller backups are a keyring in a suitcase—encrypt them and lock who can open them. Guest shares and public email ZIPs are gift wrapping for an attacker.
Full Explanation
Nightly backups of WLAN controller configurations that include RADIUS secrets, certificates, and PSKs must be encrypted and access-controlled because they contain sensitive keying and credential material. A plaintext backup is a portable keys-to-the-kingdom archive. Civic DR practices that ignore backup confidentiality create a quieter, worse breach than many RF attacks.
Storing plaintext backups on the guest file share for easy contractor access exposes secrets broadly. Emailing weekly unencrypted ZIPs to a public distribution list for DR readiness publishes credentials. Omitting backups entirely so stolen controllers have no restore path trades confidentiality for catastrophic recovery failure.
Exam caveat: protect backup media/object storage with least-privilege IAM and test restores without widening read access. Operational check: verify backup encryption at rest, restrict who can download controller backups, and perform a restore test into an isolated lab without granting guest-network readability. In municipal WLAN programs, capture the decision in the wireless standard and re-check it at change review so the next project inherits the same control bar instead of rediscovering the failure during an outage. In municipal WLAN programs, capture the decision in the wireless standard and re-check it at change review so the next project inherits the same control bar instead of rediscovering the failure during an outage.