
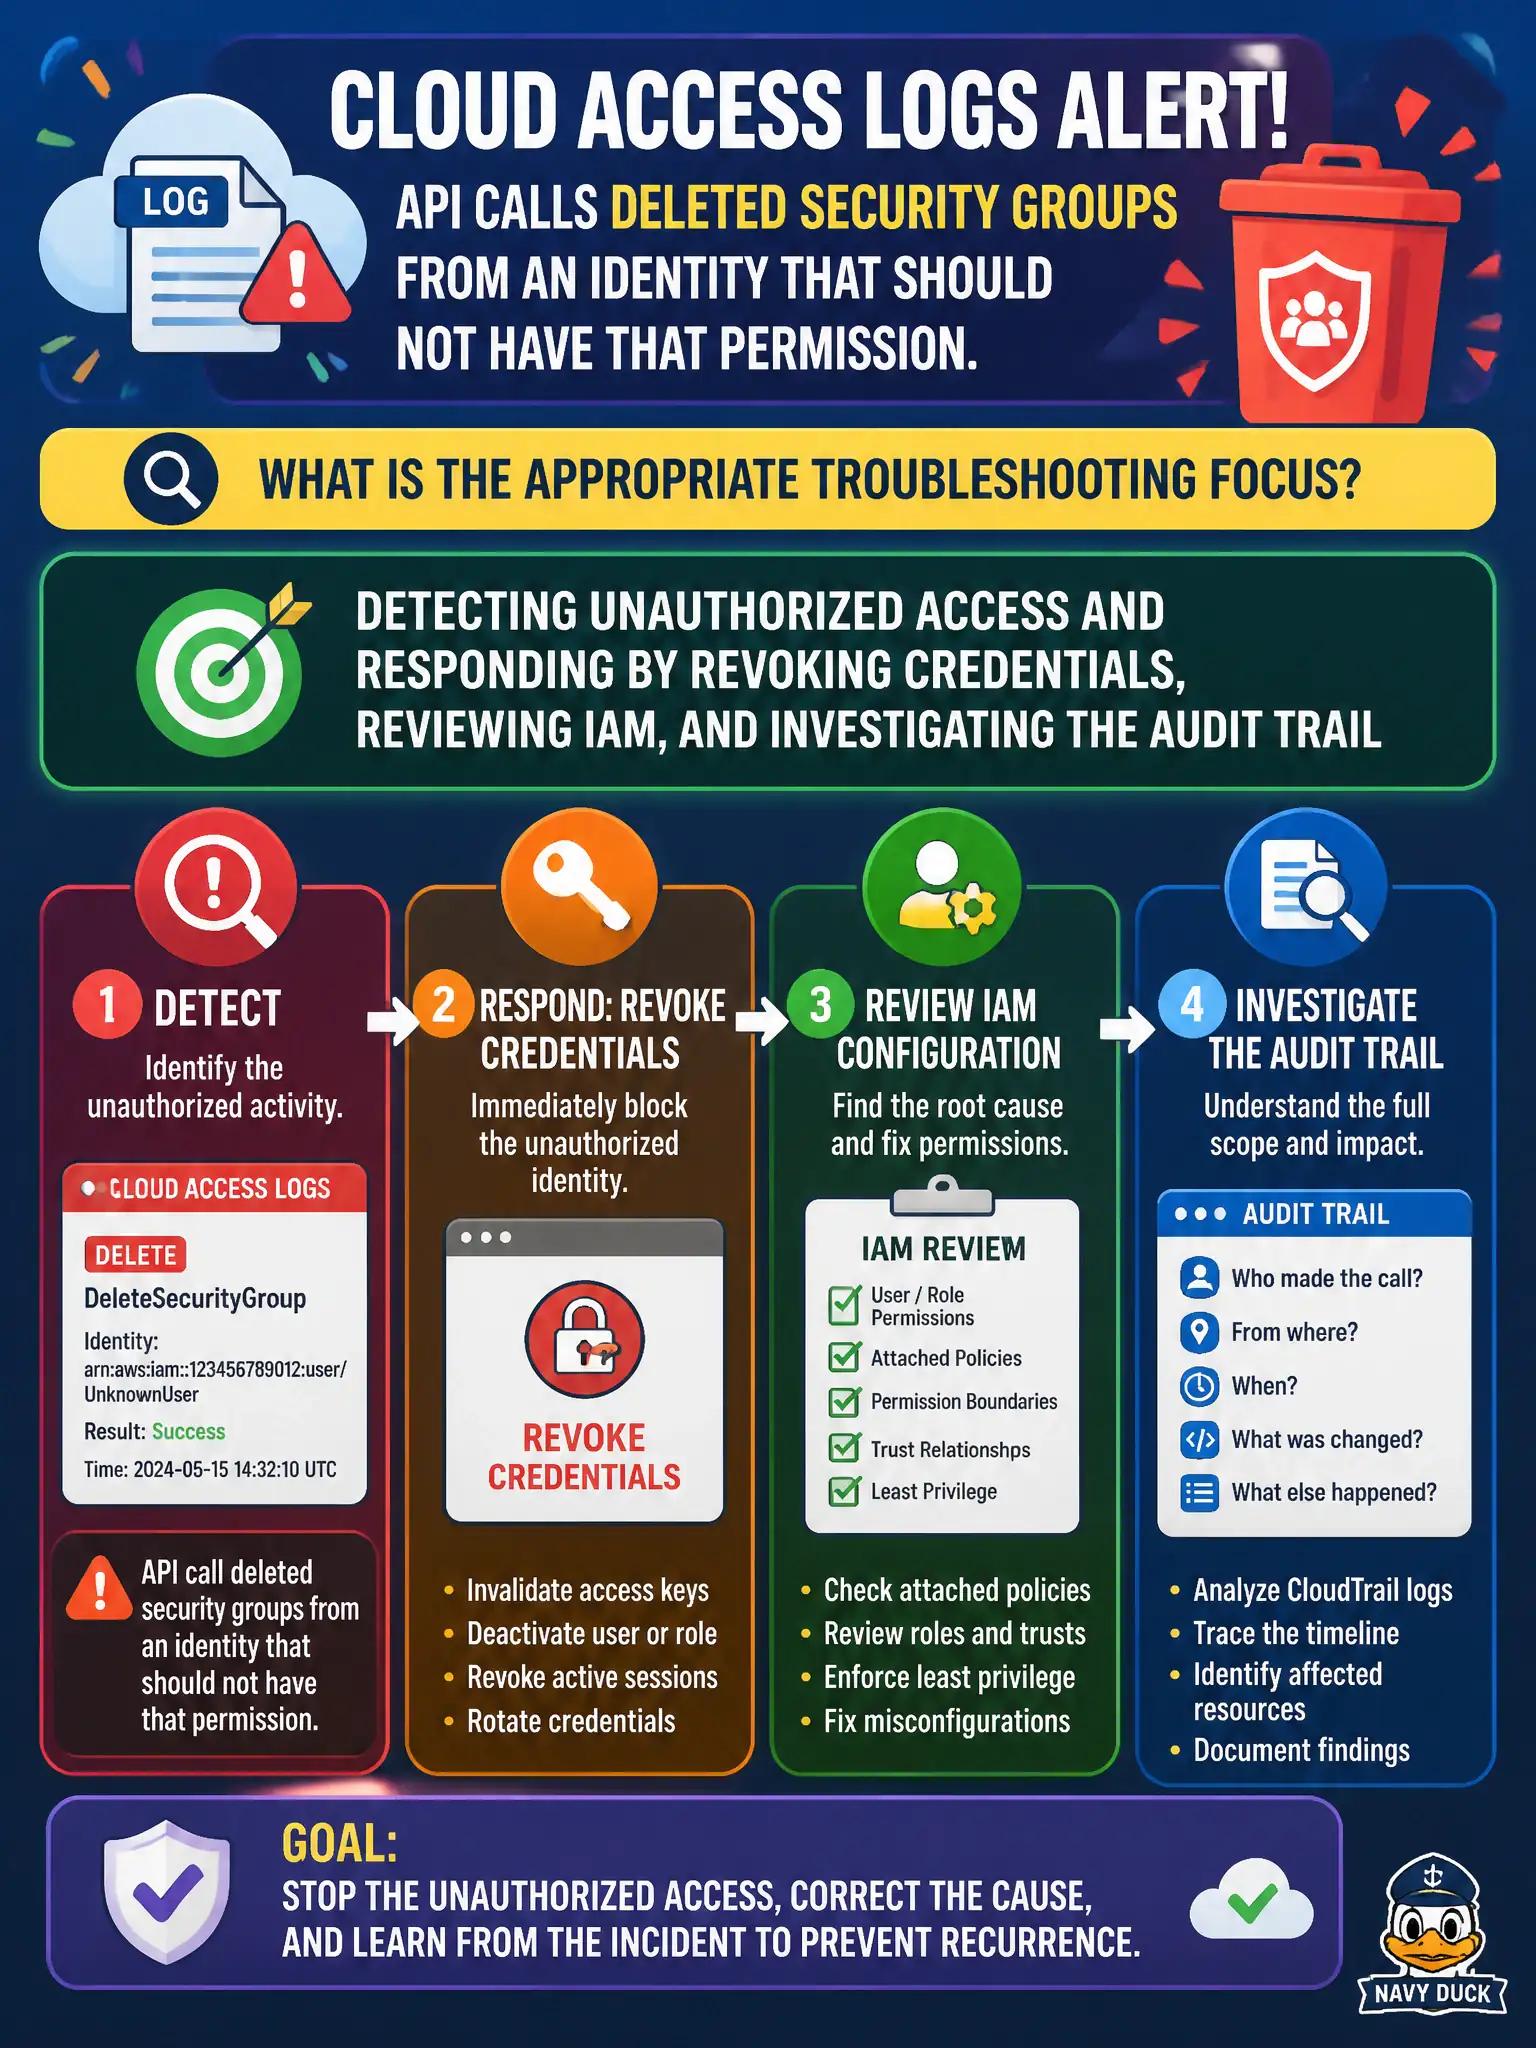
Cloud access logs show API calls that delete security groups from an identity that should not have that permission. What is the appropriate troubleshooting focus?
Select an answer to reveal the explanation.
Short Explanation
Logs showing deletes from an identity that should be read-only are a break-in alarm, not a CDN problem. Revoke what that identity can use, tighten IAM, and walk the audit trail.
Full Explanation
Cloud access logs showing API calls that delete security groups from an identity that should not have that permission require detecting unauthorized access and responding by revoking credentials, reviewing IAM, and investigating the audit trail. Unauthorized control-plane changes are high-priority civic security events. Increasing CDN TTLs to reduce origin load does not address illicit security-group deletions. Converting all databases from relational to key-value stores is unrelated. Disabling NTP across the fleet to force reauthentication harms SSO and does not contain compromised identities. Exam caveat: preserve logs before containment steps that might interrupt collection; evidence retention is part of municipal incident response. Operational check: disable or rotate the identity's credentials, restore required security groups from IaC, analyze audit events for blast radius, tighten IAM, notify stakeholders, and complete a post-incident review. In municipal cloud operations, record the chosen control and the rejected alternatives in the change or incident ticket so future on-call staff understand which failure modes were avoided for city services. Re-validate after the next maintenance window that the same decision still holds under current provider limits, identity bindings, and application versions used by the civic platform team.