
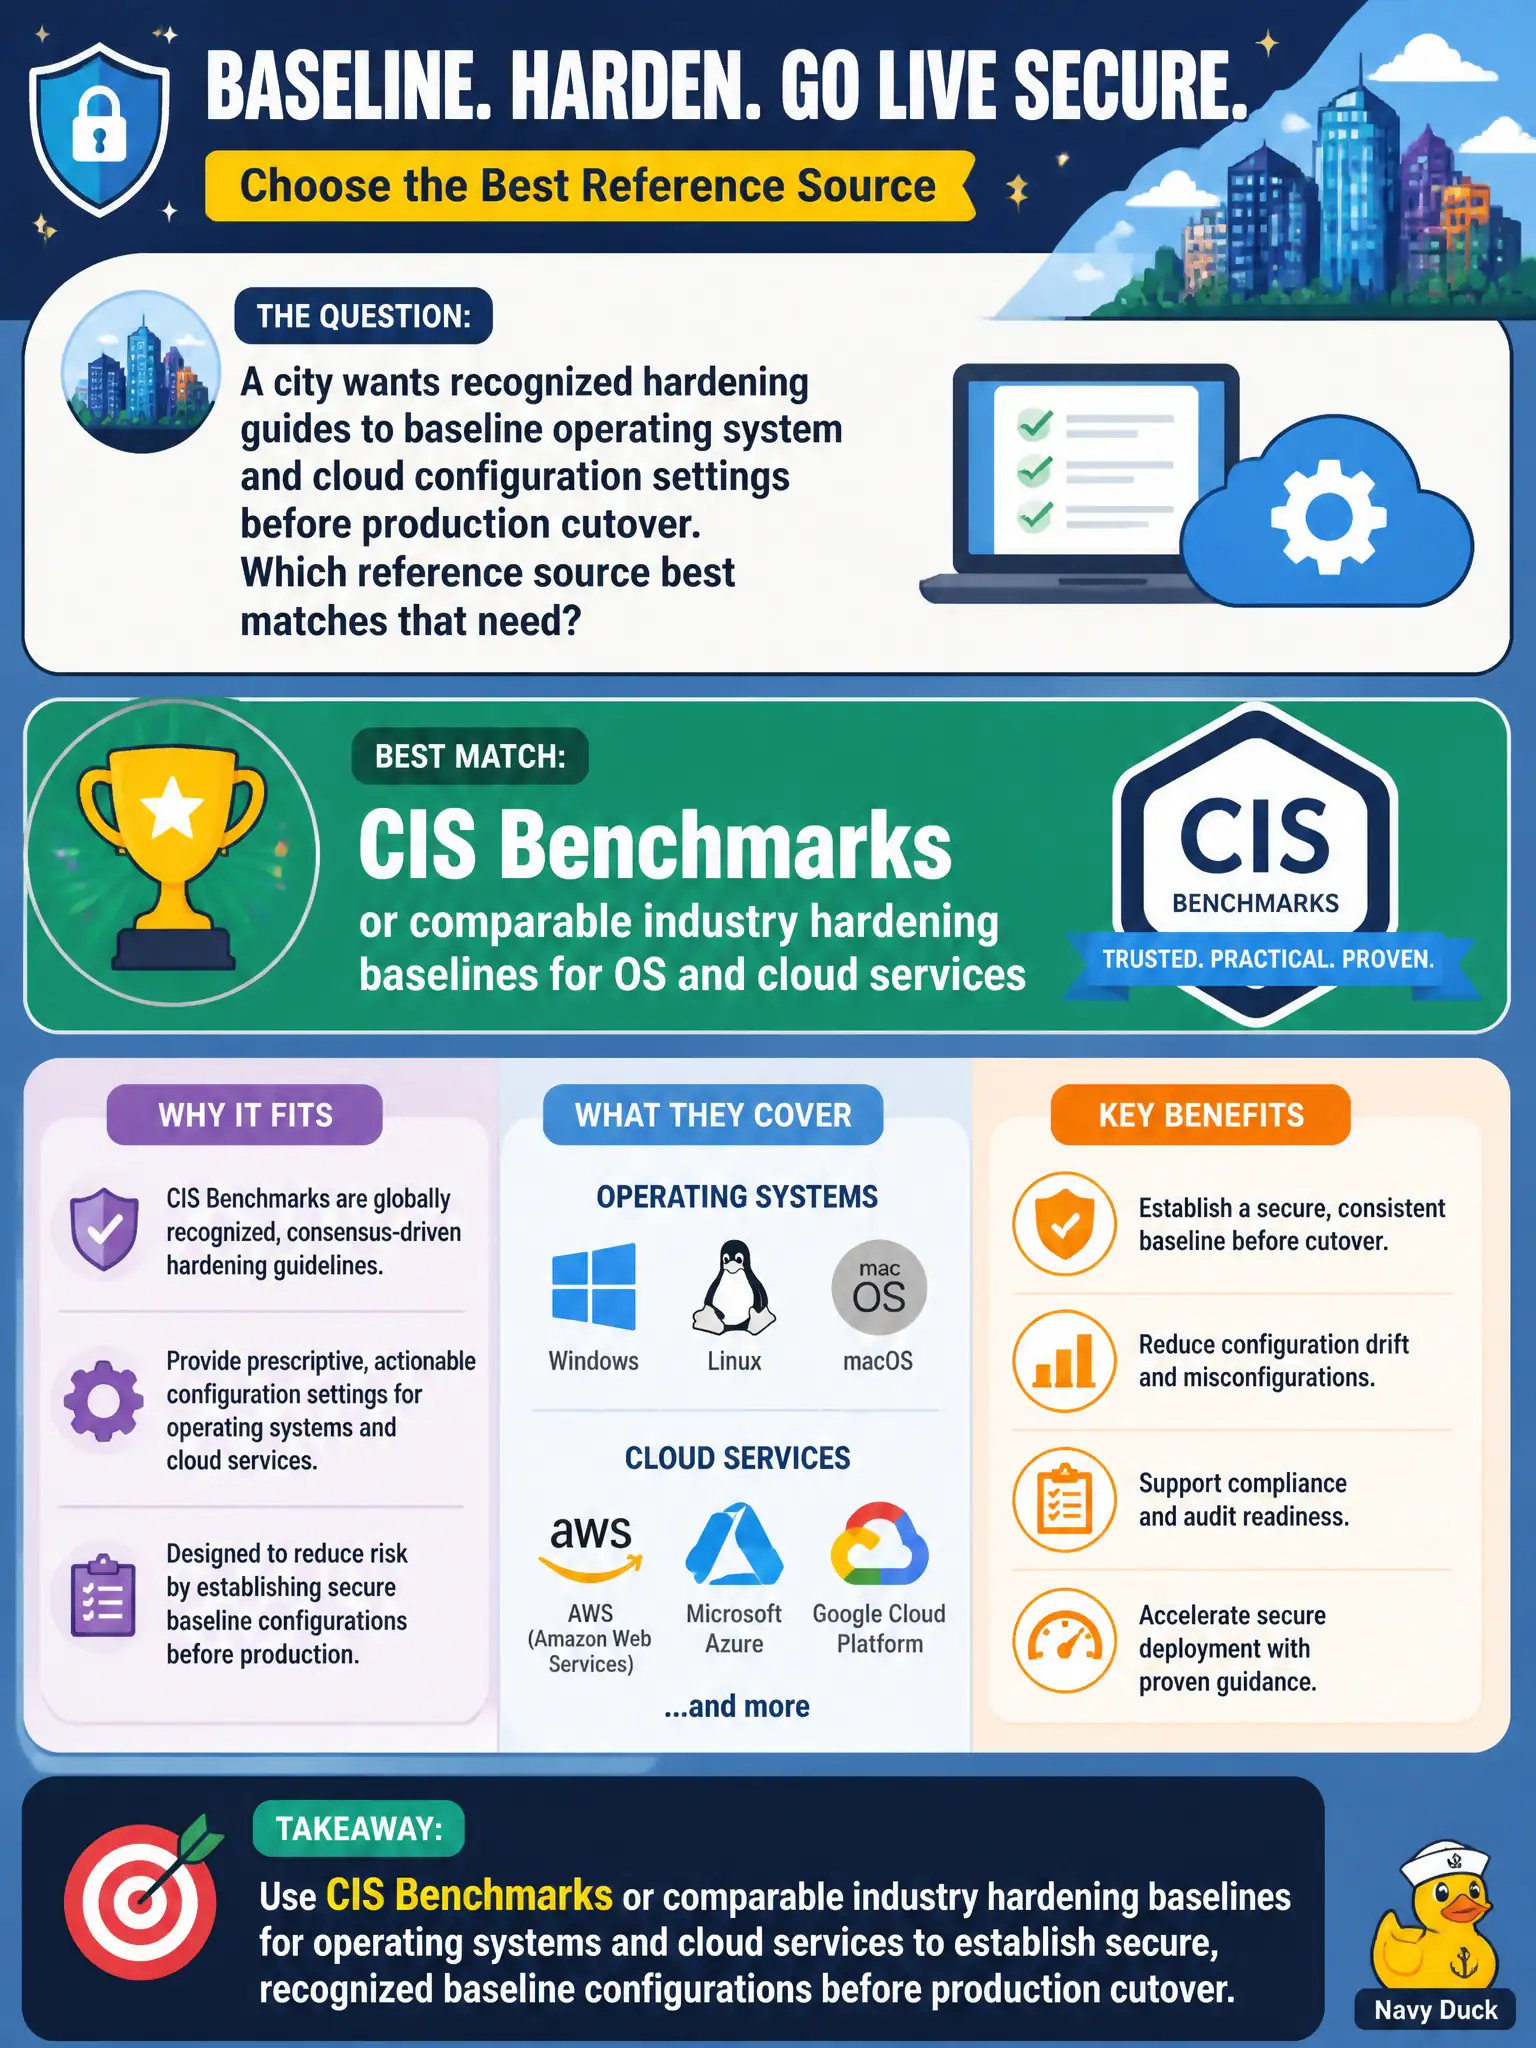
A city wants recognized hardening guides to baseline operating system and cloud configuration settings before production cutover. Which reference source best matches that need?
Select an answer to reveal the explanation.
Short Explanation
You would not rebuild city hall plumbing from a random comment thread—use a recognized playbook. CIS Benchmarks (and similar consensus guides) give versioned, practical hardening baselines for OS and cloud configs. Marketing decks and unverified forum tips are not that playbook.
Full Explanation
CIS Benchmarks and comparable industry hardening baselines provide versioned, consensus-oriented configuration recommendations for operating systems and cloud services. A city that wants recognized hardening guides before production cutover should use those baselines to set secure defaults rather than improvised advice. Standardized benchmarks improve consistency across municipal teams and vendors.
Random blog posts without versioned controls lack reliability. Vendor marketing slides that omit concrete configuration recommendations do not form a baseline. Unreviewed chat-forum checklists that contradict each other weekly are not authoritative.
Exam caveat: CIS is the frequently cited example; vendor security baselines and STIGs appear in some environments too. Benchmarks guide configuration—they still need tailoring and exception handling.
Operational check: select CIS profiles for the OS/cloud services in scope, assess current configs, remediate gaps in non-prod, bake controls into golden images/IaC, and re-scan before citizen-facing cutover. Store exception tickets with compensating controls for any waived recommendations.
Version-pin the CIS benchmark profile used for each image family in the city’s IaC repo so rebuilds remain reproducible and auditors can see which hardening revision underpinned a given citizen-facing release.