
A county septic-inspection study sheet still labels a §3.2.2 row as “data exfiltration.” Which v1.1 name should the candidate select for that row on the exam?
Select an answer to reveal the explanation.
Short Explanation
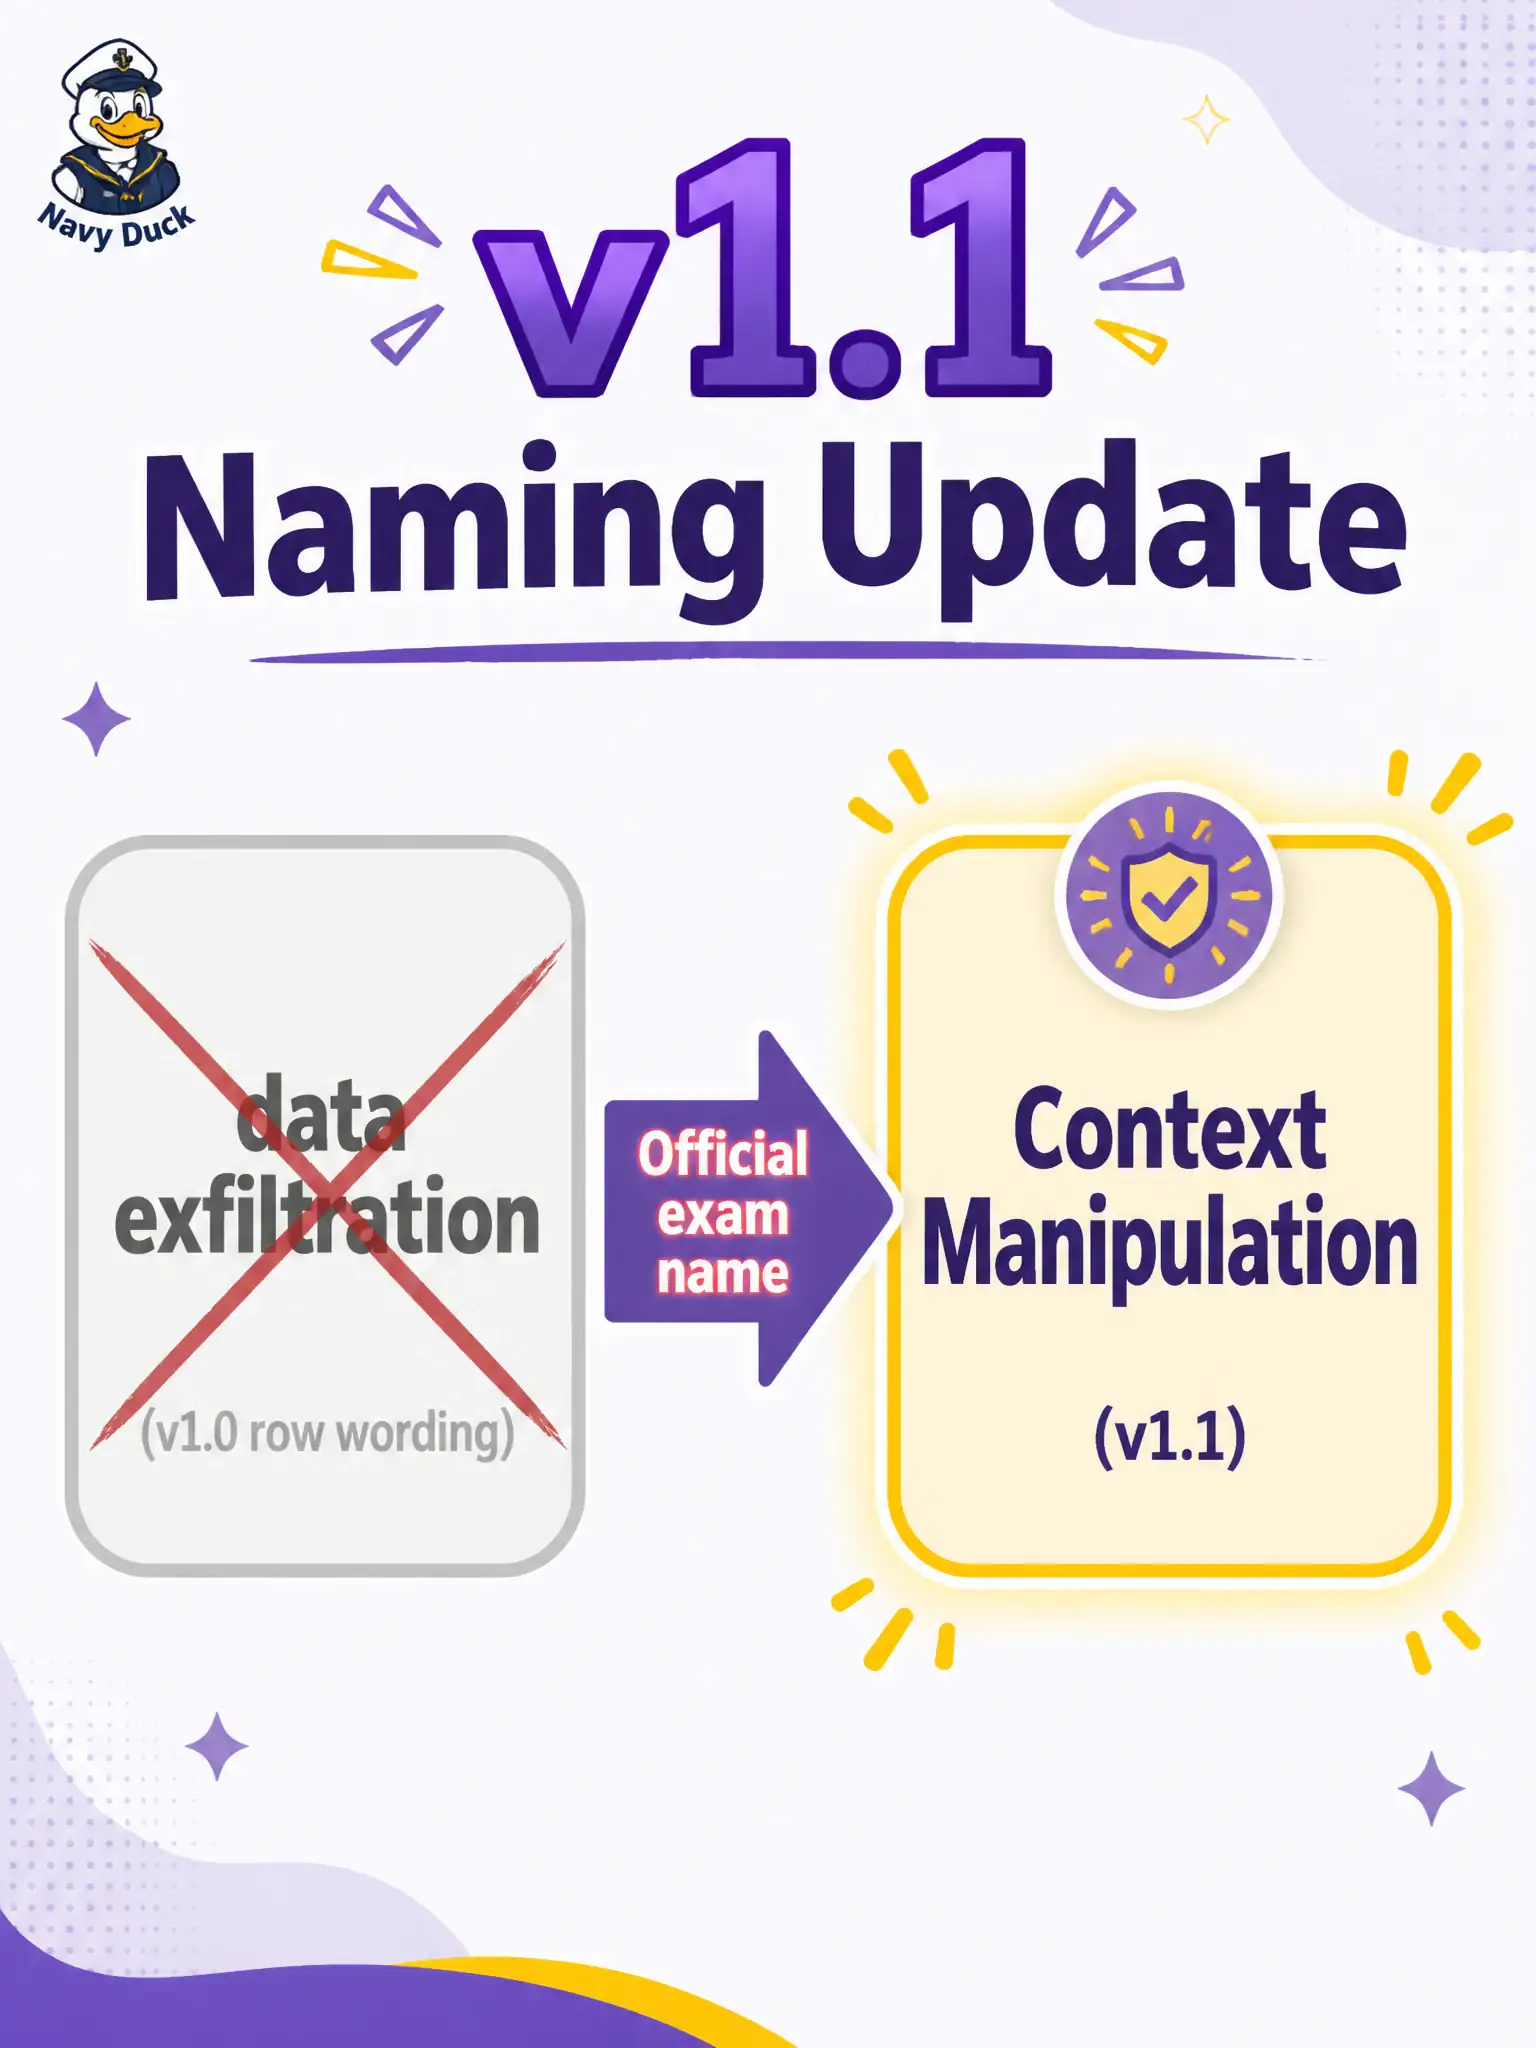
Study sheets lag; the exam follows v1.1. For that row, say context manipulation — not the retired “data exfiltration” label. Same neighborhood of risk, updated official name.
Full Explanation
County septic-inspection study sheets sometimes lag syllabus renames. For the §3.2.2-style row formerly labeled “data exfiltration,” candidates should select context manipulation—the official v1.1 name for that vector. The exam follows current syllabus wording even when older handouts keep the retired label.
Keeping “data exfiltration” because v1.0 wording remains official fails by concept: v1.1 updates the examinable name. Choosing malicious code generation fails because leakage symptoms are not the same as dangerous generated executables. Temperature seeding as a privacy metric that replaced §3.2.2 fails because temperature/seed controls are reproducibility tools, not the renamed security vector.
Exam caveat: the underlying neighborhood of risk may feel familiar; the tested skill is using the official v1.1 label. Do not invent hybrid names on the answer sheet.
Operational check: scrub septic-course decks and flashcards to say context manipulation; add a one-line “formerly called data exfiltration in older notes” so learners map old materials without using the retired term as the exam answer. Align internal security tickets to the same four-vector vocabulary. In septic-inspection training rooms, post a v1.0→v1.1 rename strip so proctors and candidates share the same official label during practice exams and after-action reviews.