
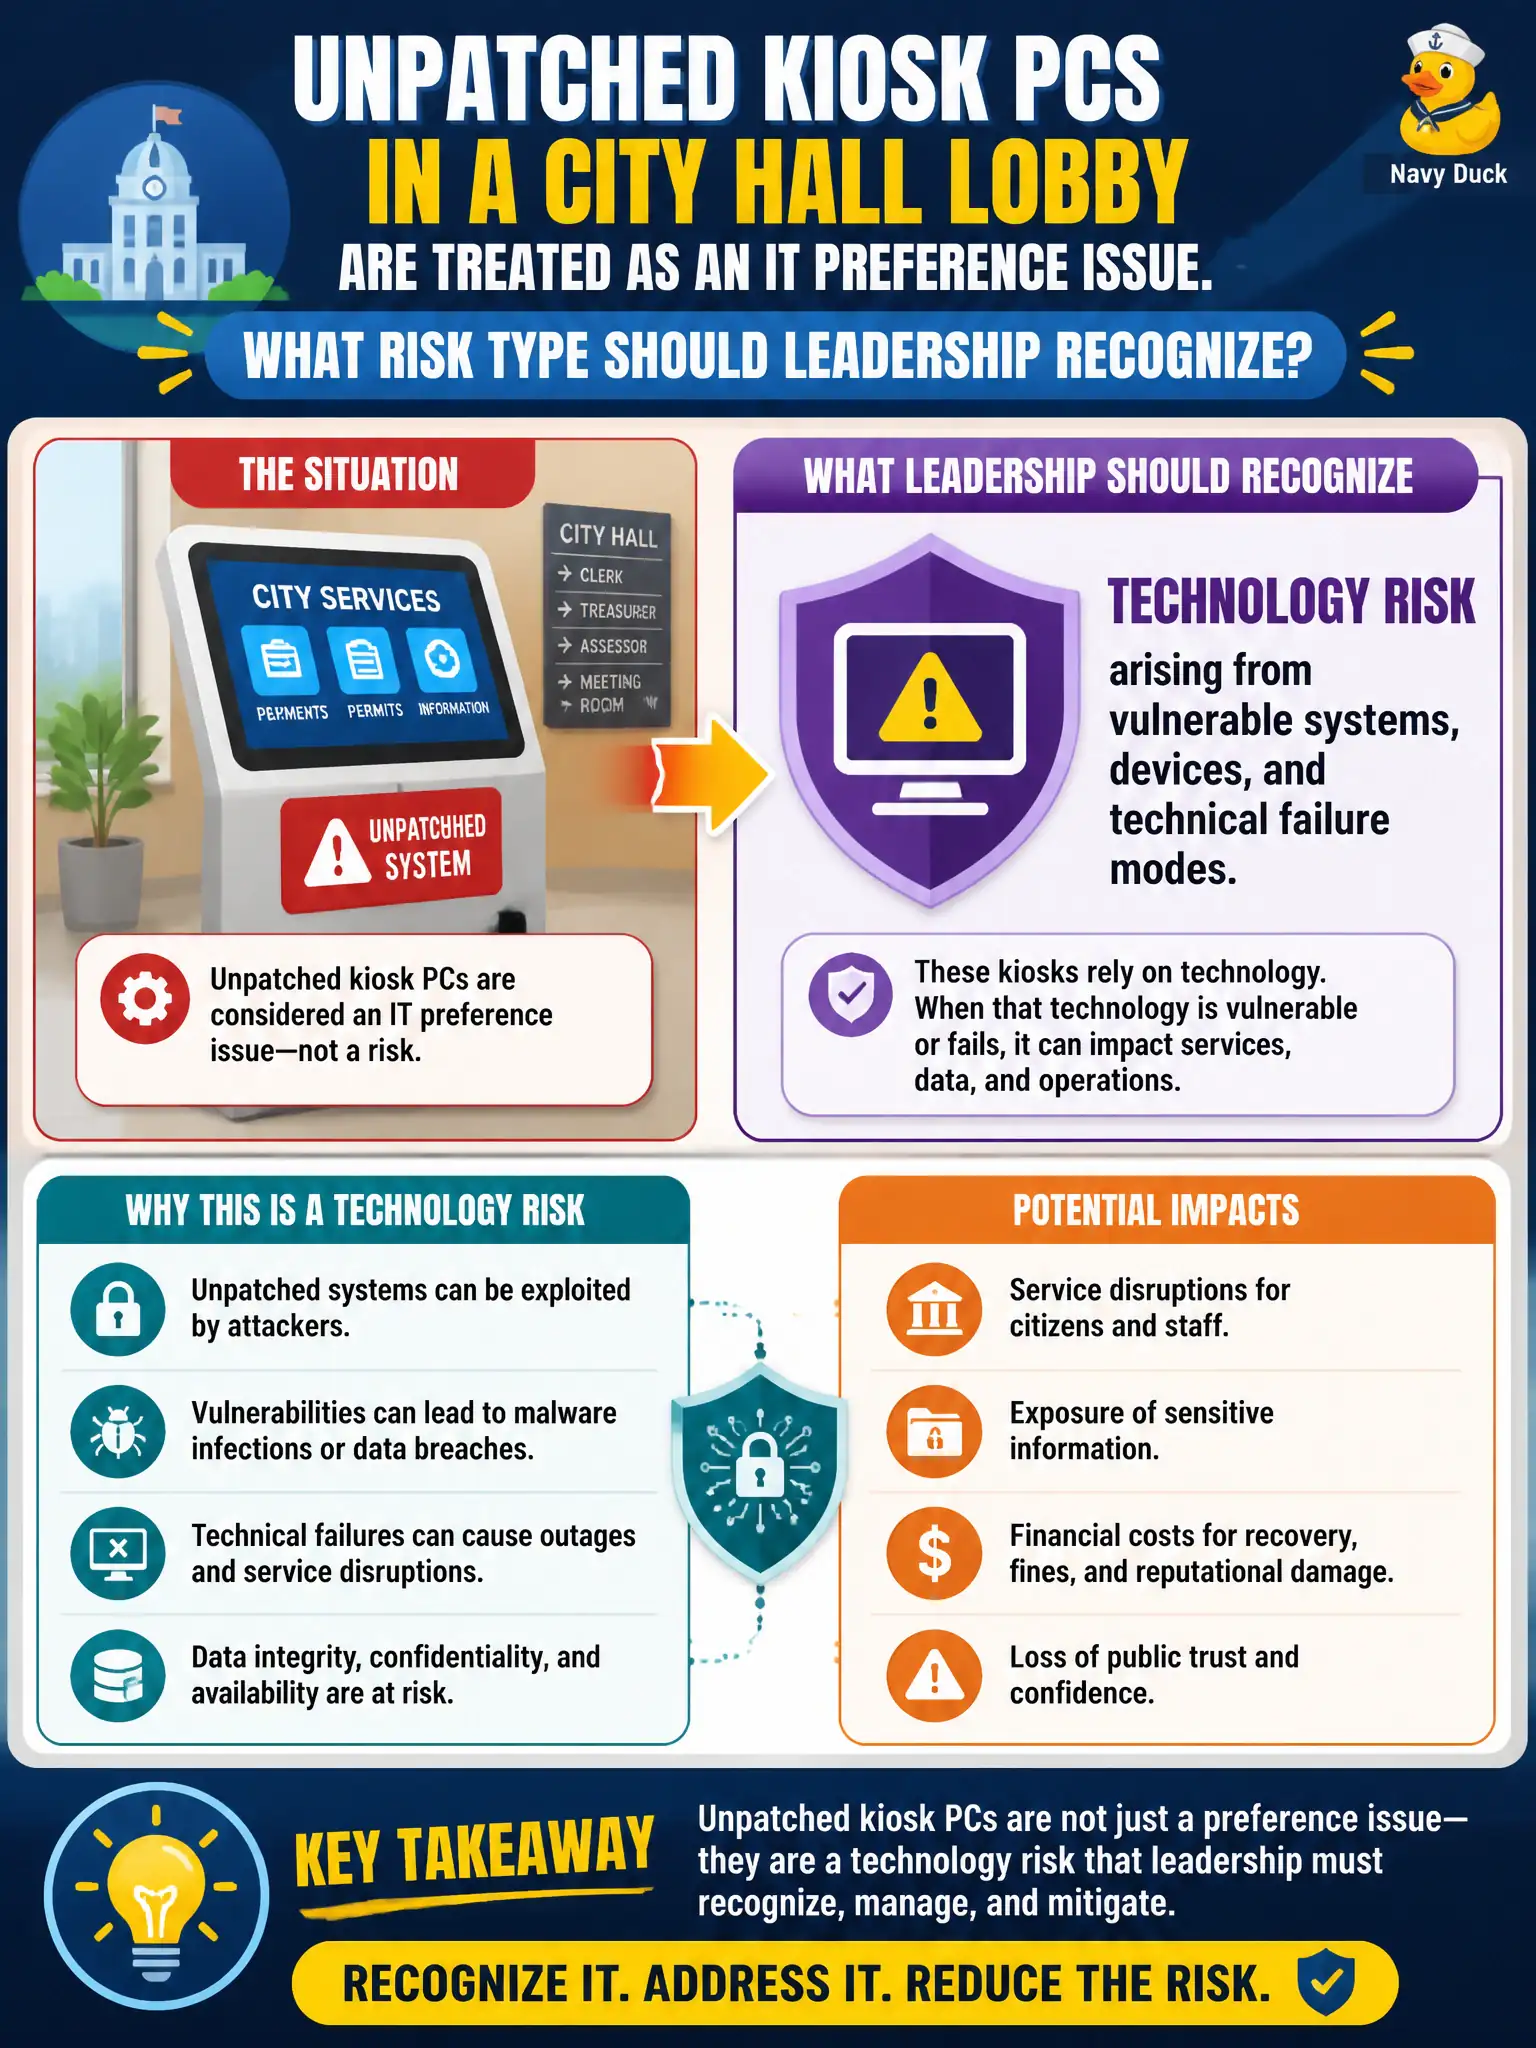
Unpatched kiosk PCs in a city hall lobby are treated as an IT preference issue. What risk type should leadership recognize?
Select an answer to reveal the explanation.
Short Explanation
Unpatched lobby kiosks are not a taste debate—they are open doors on the network. That is technology risk sitting in plain sight.
Full Explanation
Unpatched kiosk PCs in a city hall lobby are technology risk arising from vulnerable systems, devices, and technical failure or exploit modes—not a mere IT preference. Treating them only as personnel risk because visitors touch keyboards misses patch and configuration exposure. Calling them environmental because lobby temperature affects uptime misfiles the dominant threat. Limiting them to supplier warranty issues ignores ongoing vulnerability management the city owns. Exam caveat: vulnerable public-facing systems are technology risks requiring hardening and patching. Operational check: inventory lobby kiosks, apply baseline hardening and patch SLAs, segment them on the network, and add a technology-risk row with an IT owner and residual after controls. Verify after the next Patch Tuesday that civic kiosks remain in compliance. In municipal practice, record the rationale in the risk procedure or committee minutes so future staff apply the same rule under budget pressure. Re-validate after the next seasonal peak or org-chart change to confirm the civic control still holds as designed for residents and staff. In municipal practice, record the rationale in the risk procedure or committee minutes so future staff apply the same rule under budget pressure. Re-validate after the next seasonal peak or org-chart change to confirm the civic control still holds as designed for residents and staff.