
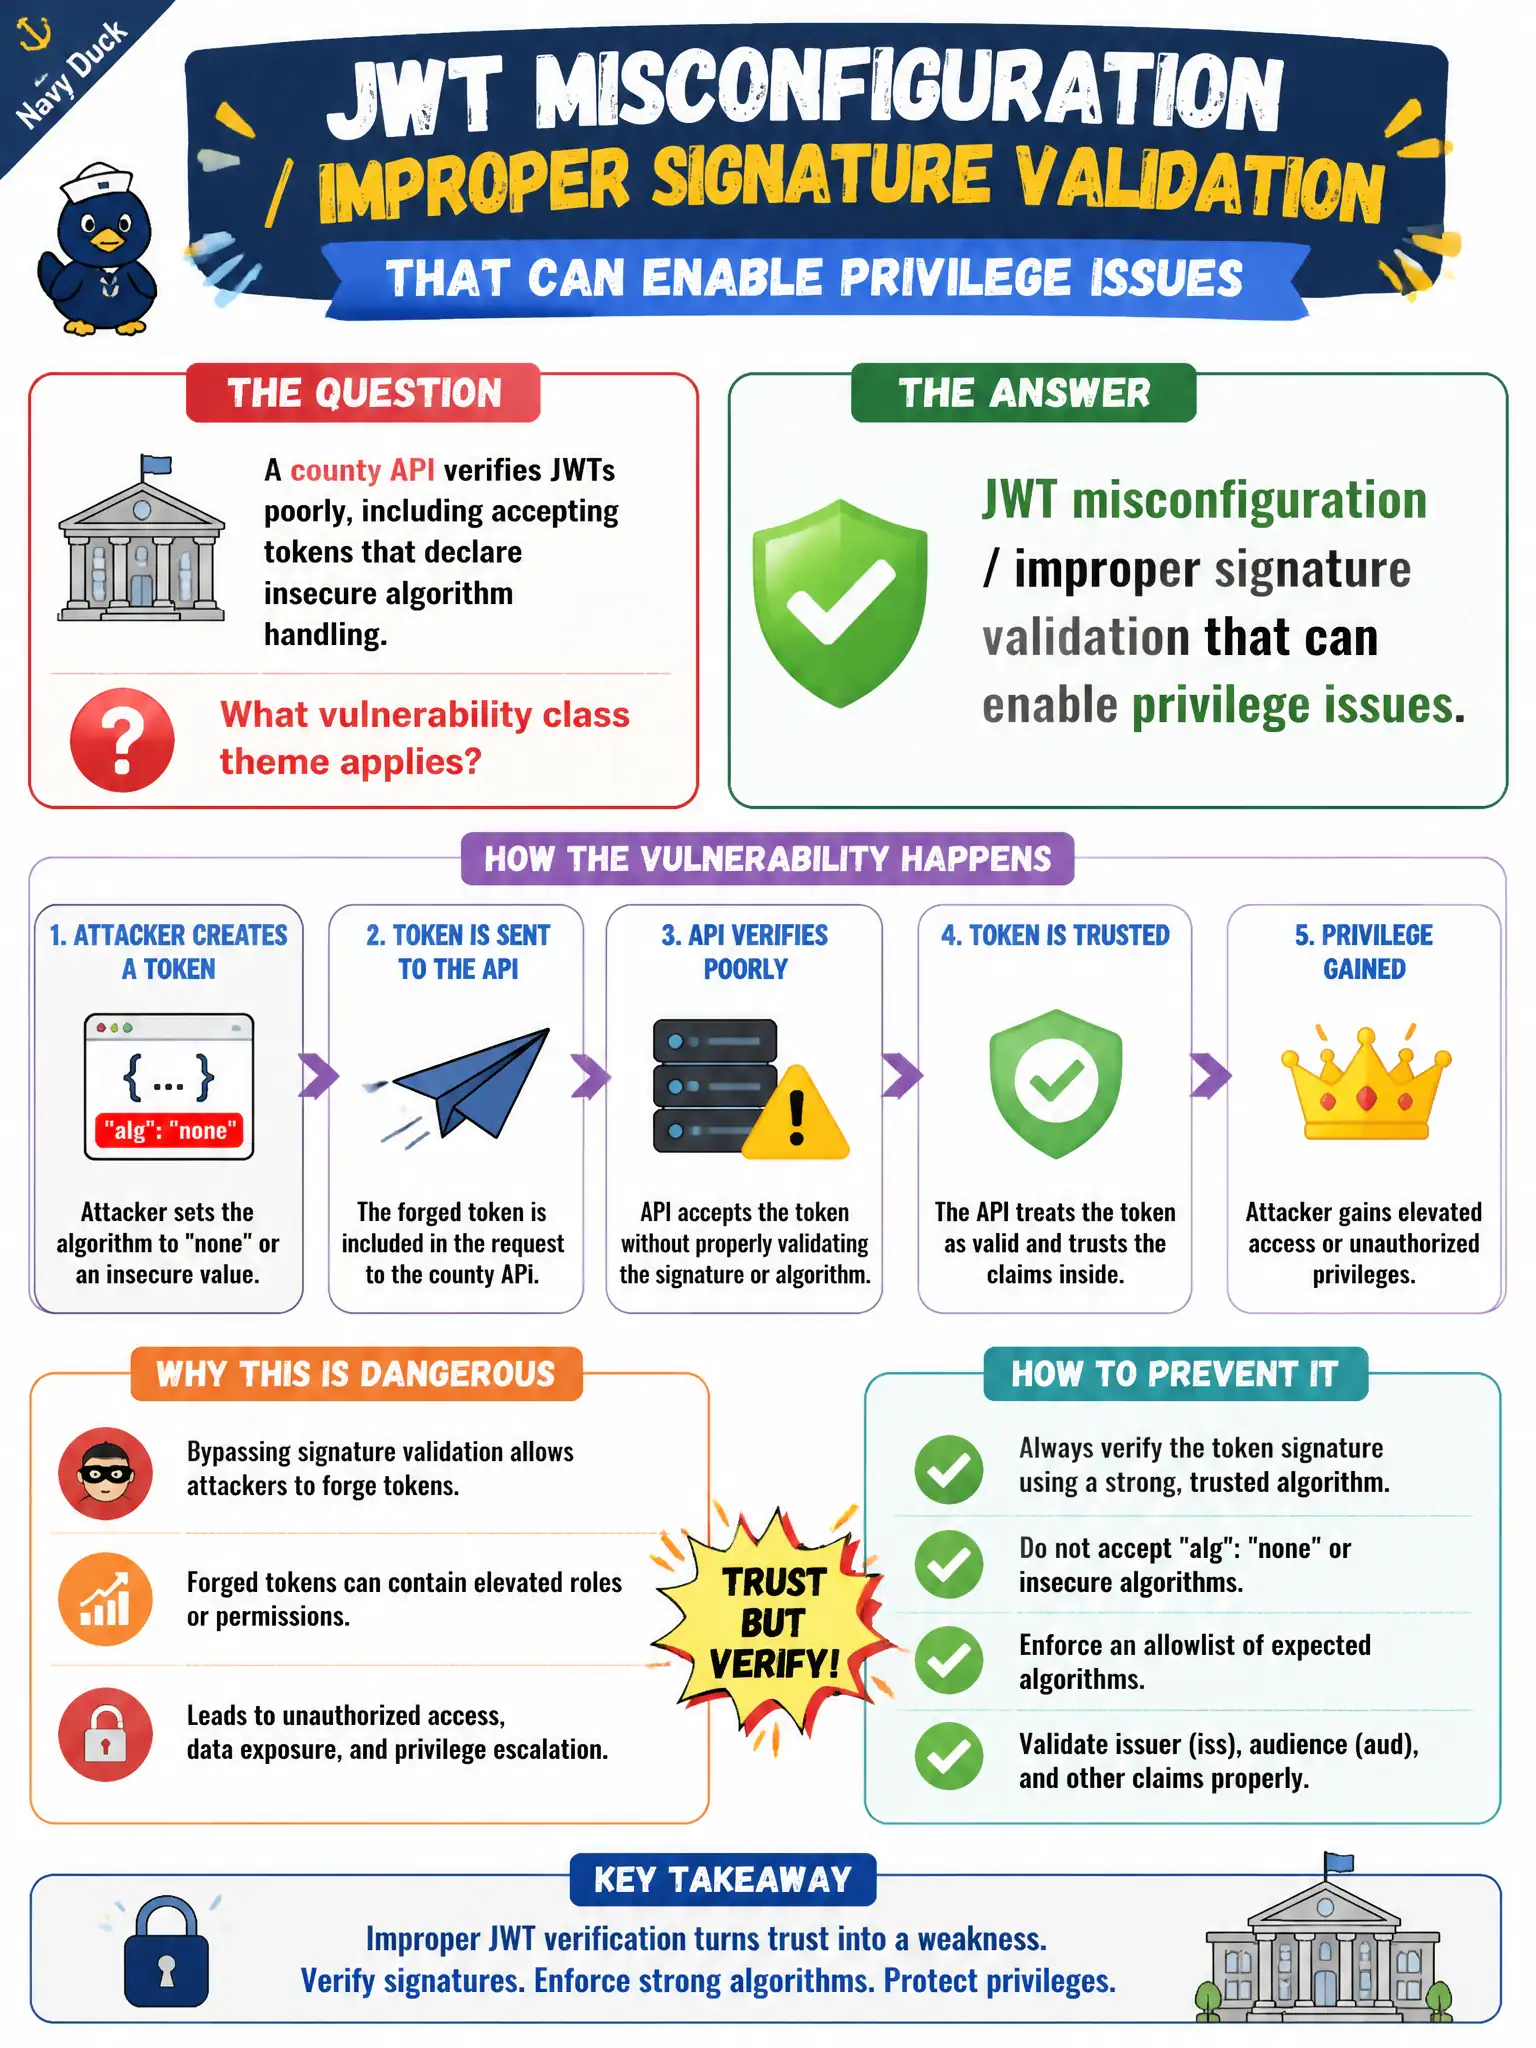
A county API verifies JWTs poorly, including accepting tokens that declare insecure algorithm handling. What vulnerability class theme applies?
Select an answer to reveal the explanation.
Short Explanation
A badge reader that believes any sticker saying "signed" is not a badge reader. Weak JWT checks — including bad algorithm handling — let forged claims slide. Stay on the misconfig class; no need for exploit recipes.
Full Explanation
JWT misconfiguration / improper signature validation can enable privilege issues when an API accepts tokens that declare insecure algorithm handling or otherwise fails to verify signatures correctly. A county API that verifies JWTs poorly may accept forged or altered claims—undermining authentication for municipal services that trust those tokens.
Perfect validation does not ignore alg handling carelessly; secure libraries constrain algorithms. Missing robots meta tags and BGP leaks are unrelated.
Exam caveat: allowlist algorithms (typically strong asymmetric/HMAC as designed), verify signatures with proper keys, and validate iss/aud/exp. CPTS token questions target alg confusion and verification gaps conceptually without exploit kits.
Operational check: review JWT library settings for the county API, reject insecure alg declarations, validate claims, attempt only authorized negative tests under RoE, and confirm forged tokens fail closed. Rotate signing keys on a county schedule and pin expected algorithms in gateway policy so library upgrades cannot quietly reintroduce weak JWT handling. Algorithm allowlists in gateway policy catch JWT library misconfiguration before county release.