
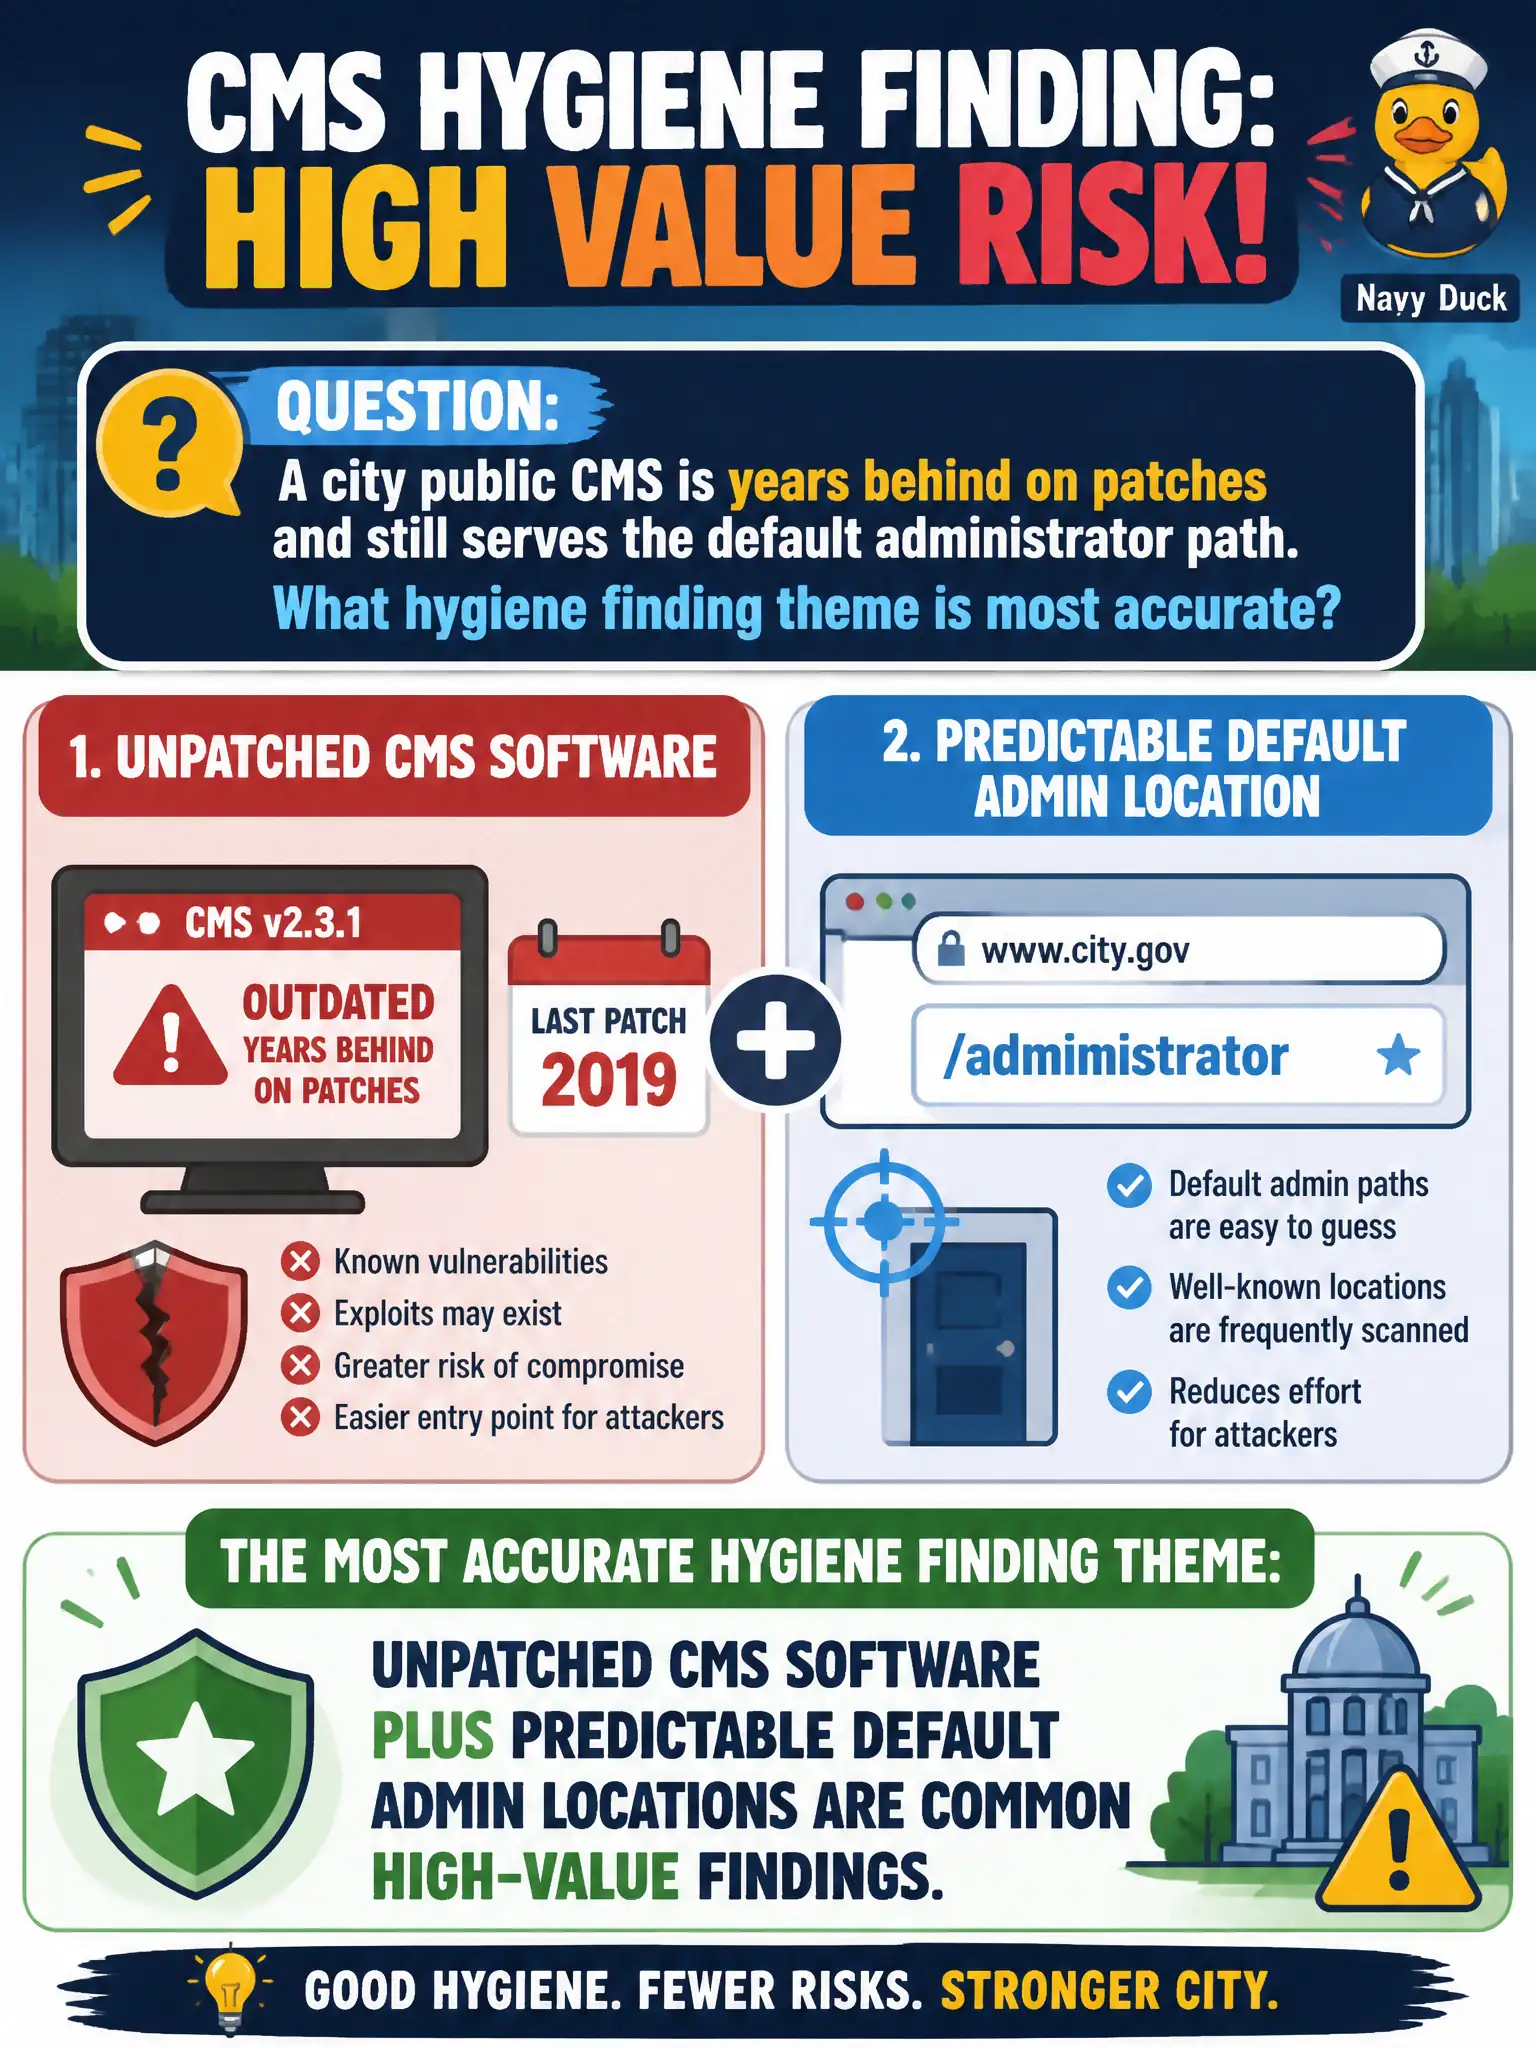
A city public CMS is years behind on patches and still serves the default administrator path. What hygiene finding theme is most accurate?
Select an answer to reveal the explanation.
Short Explanation
Old software with the welcome mat still labeled Admin is how opportunistic attackers win lazy points. Patch debt plus default paths is everyday CMS hygiene trouble. Hide-the-version is not a substitute for updates.
Full Explanation
Unpatched CMS software plus predictable default administrator paths are common high-value findings. A city public CMS years behind on patches that still serves the default admin location combines known vulnerability exposure with easy discovery of the management interface—classic hygiene failures that routinely lead to civic website compromise.
Hiding the version string does not make default admin paths harmless. A WAF virtual patch somewhere does not make CMS patching irrelevant as a theme. Public sites need patch management regardless of mobile apps.
Exam caveat: prioritize internet-facing CMS patching and admin-path hardening (restrict networks, MFA, rename/disable defaults). CPTS common-app questions reward recognizing unpatched CMS as high impact for municipalities.
Operational check: inventory CMS version vs upstream advisories, patch or isolate, restrict admin paths to VPN/bastion, remove default locations where feasible, and continuously monitor the public civic site for outdated components. Subscribe the city CMS to upstream security announcements and schedule patch windows like any other internet-facing civic production system. Default admin URLs on city CMS instances should be restricted or removed as standard hygiene.