
A library IT team uses one shared local administrator password across the entire workstation fleet. After compromising that password on one host, what privilege impact should the tester highlight?
Select an answer to reveal the explanation.
Short Explanation
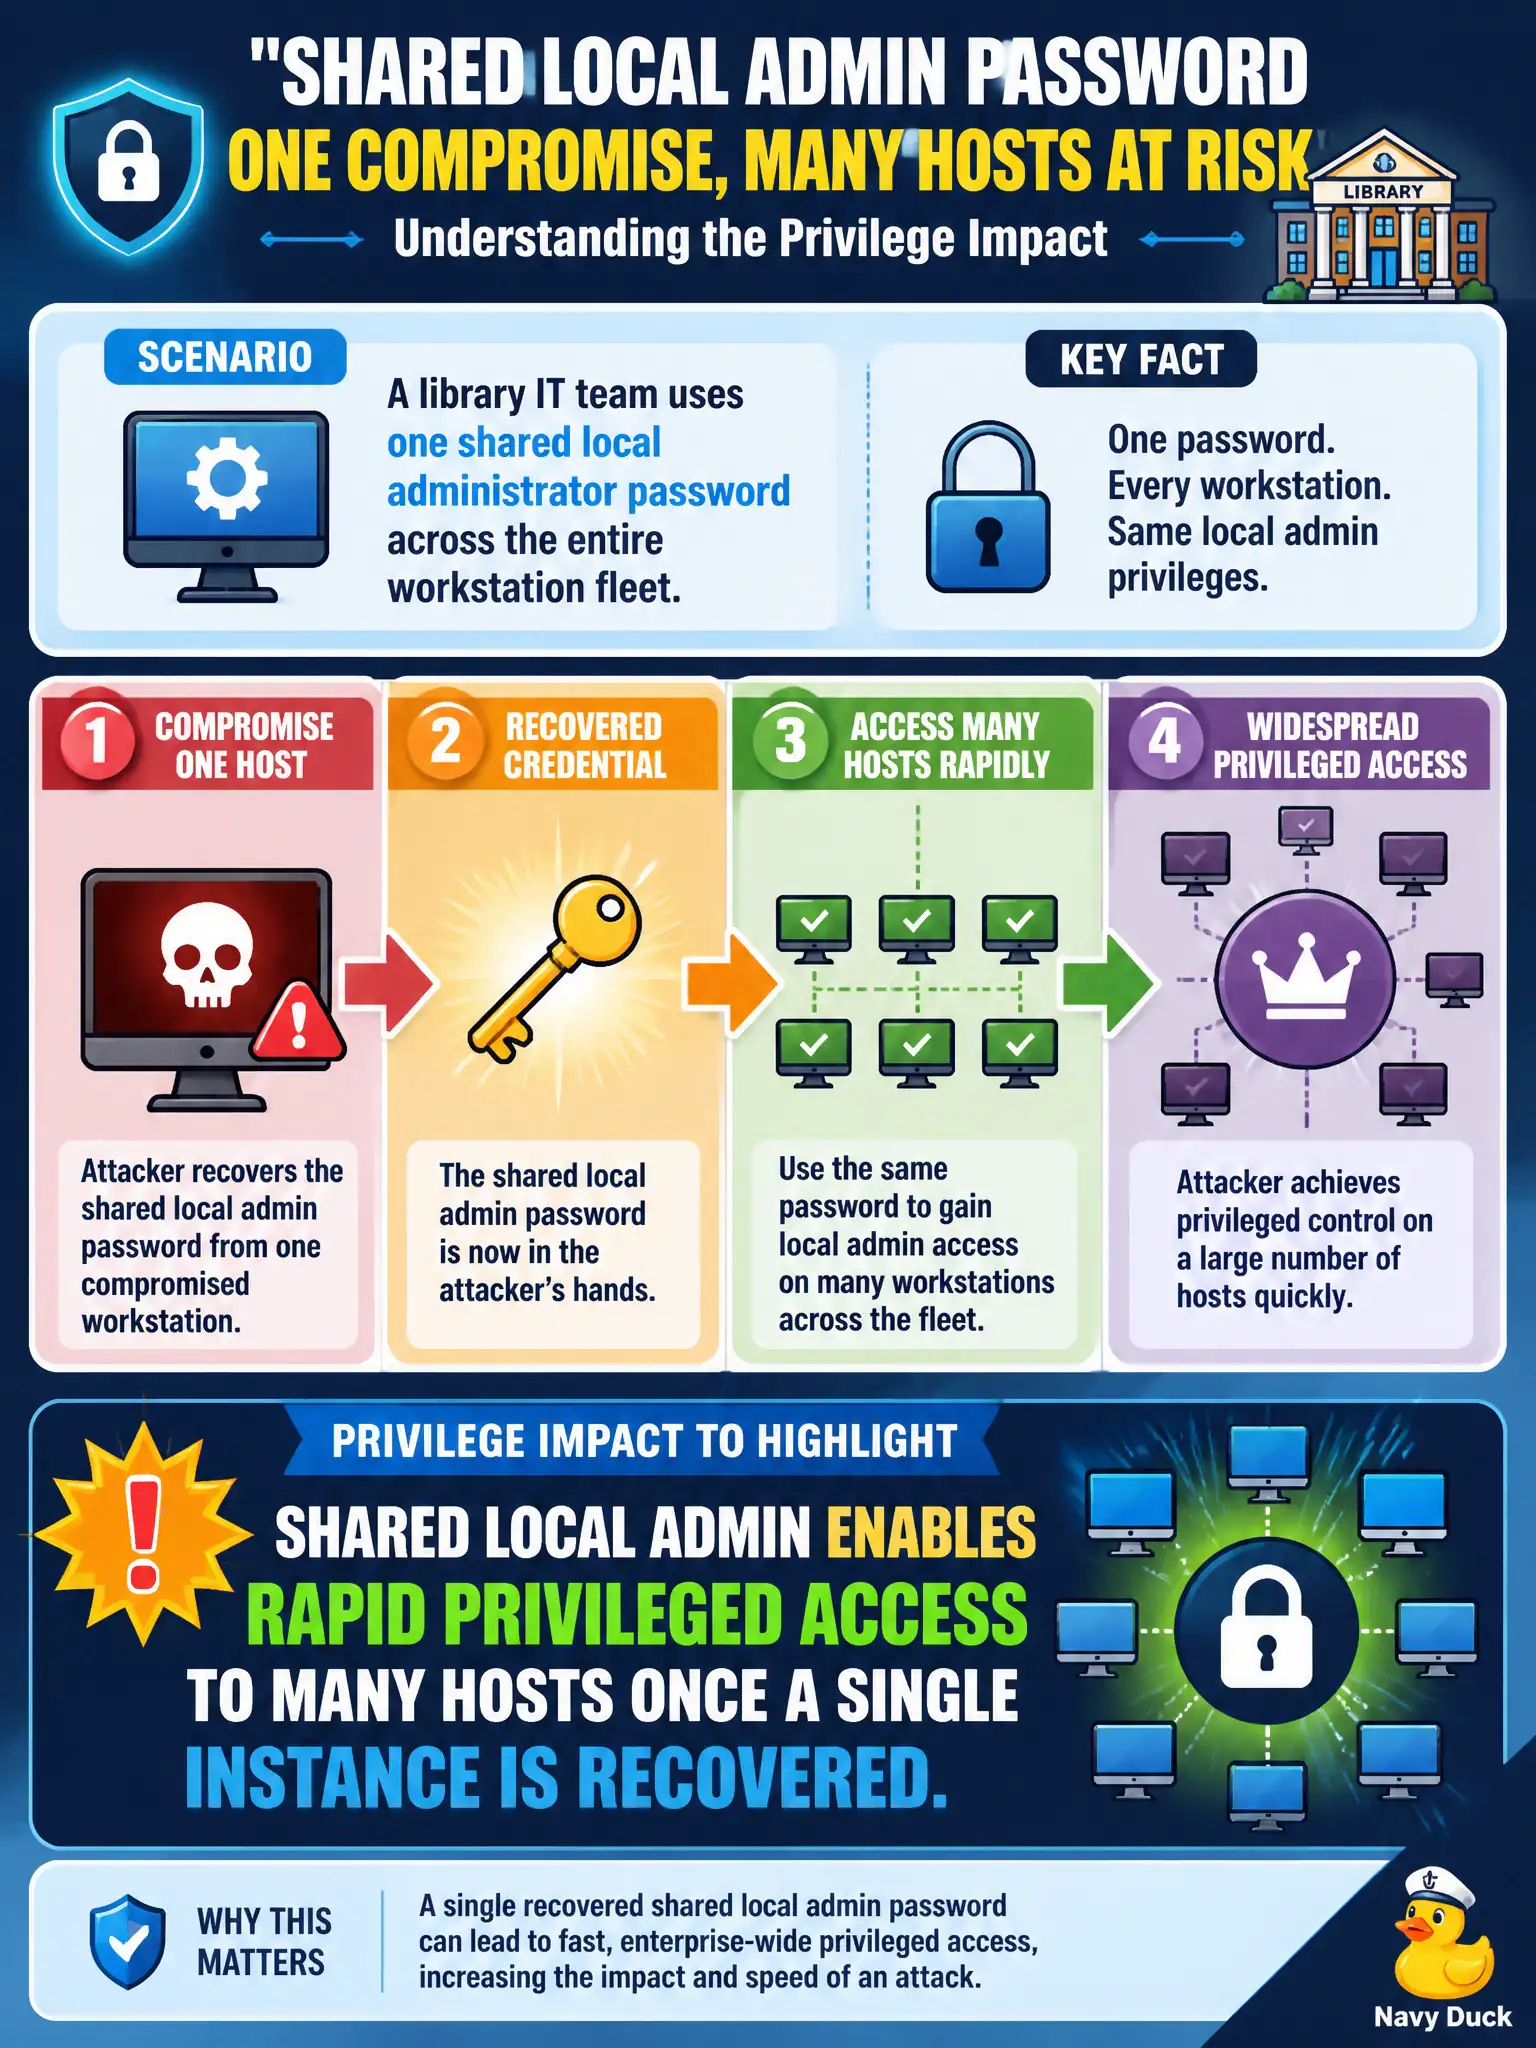
One shared local admin password is a skeleton key hanging on every door in the building. Crack or recover it once and the whole floor opens—huge lateral and priv impact. That is exactly why unique per-host local admin secrets matter.
Full Explanation
When a library IT team uses one shared local administrator password across the workstation fleet, recovering that password on one host enables rapid privileged access to many machines. Shared local admin is a lateral-movement and mass-compromise multiplier for civic endpoints.
Shared local admin passwords are not limited to printers and can open interactive privileged sessions. Absence of LAPS does not make passwords automatically unique per host. Fleet-wide reuse is not required by Active Directory and can be remediated with randomized local admin solutions.
Exam caveat: pair the finding with credential hygiene and LAPS-class remediation rather than only host-by-host password changes that drift again.
Operational check: demonstrate reuse impact conceptually with authorized hosts, recommend LAPS or equivalent, and highlight how many library workstations share the secret in the report's attack-path section. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same finding class still applies under the estate's current patch and configuration baseline.