
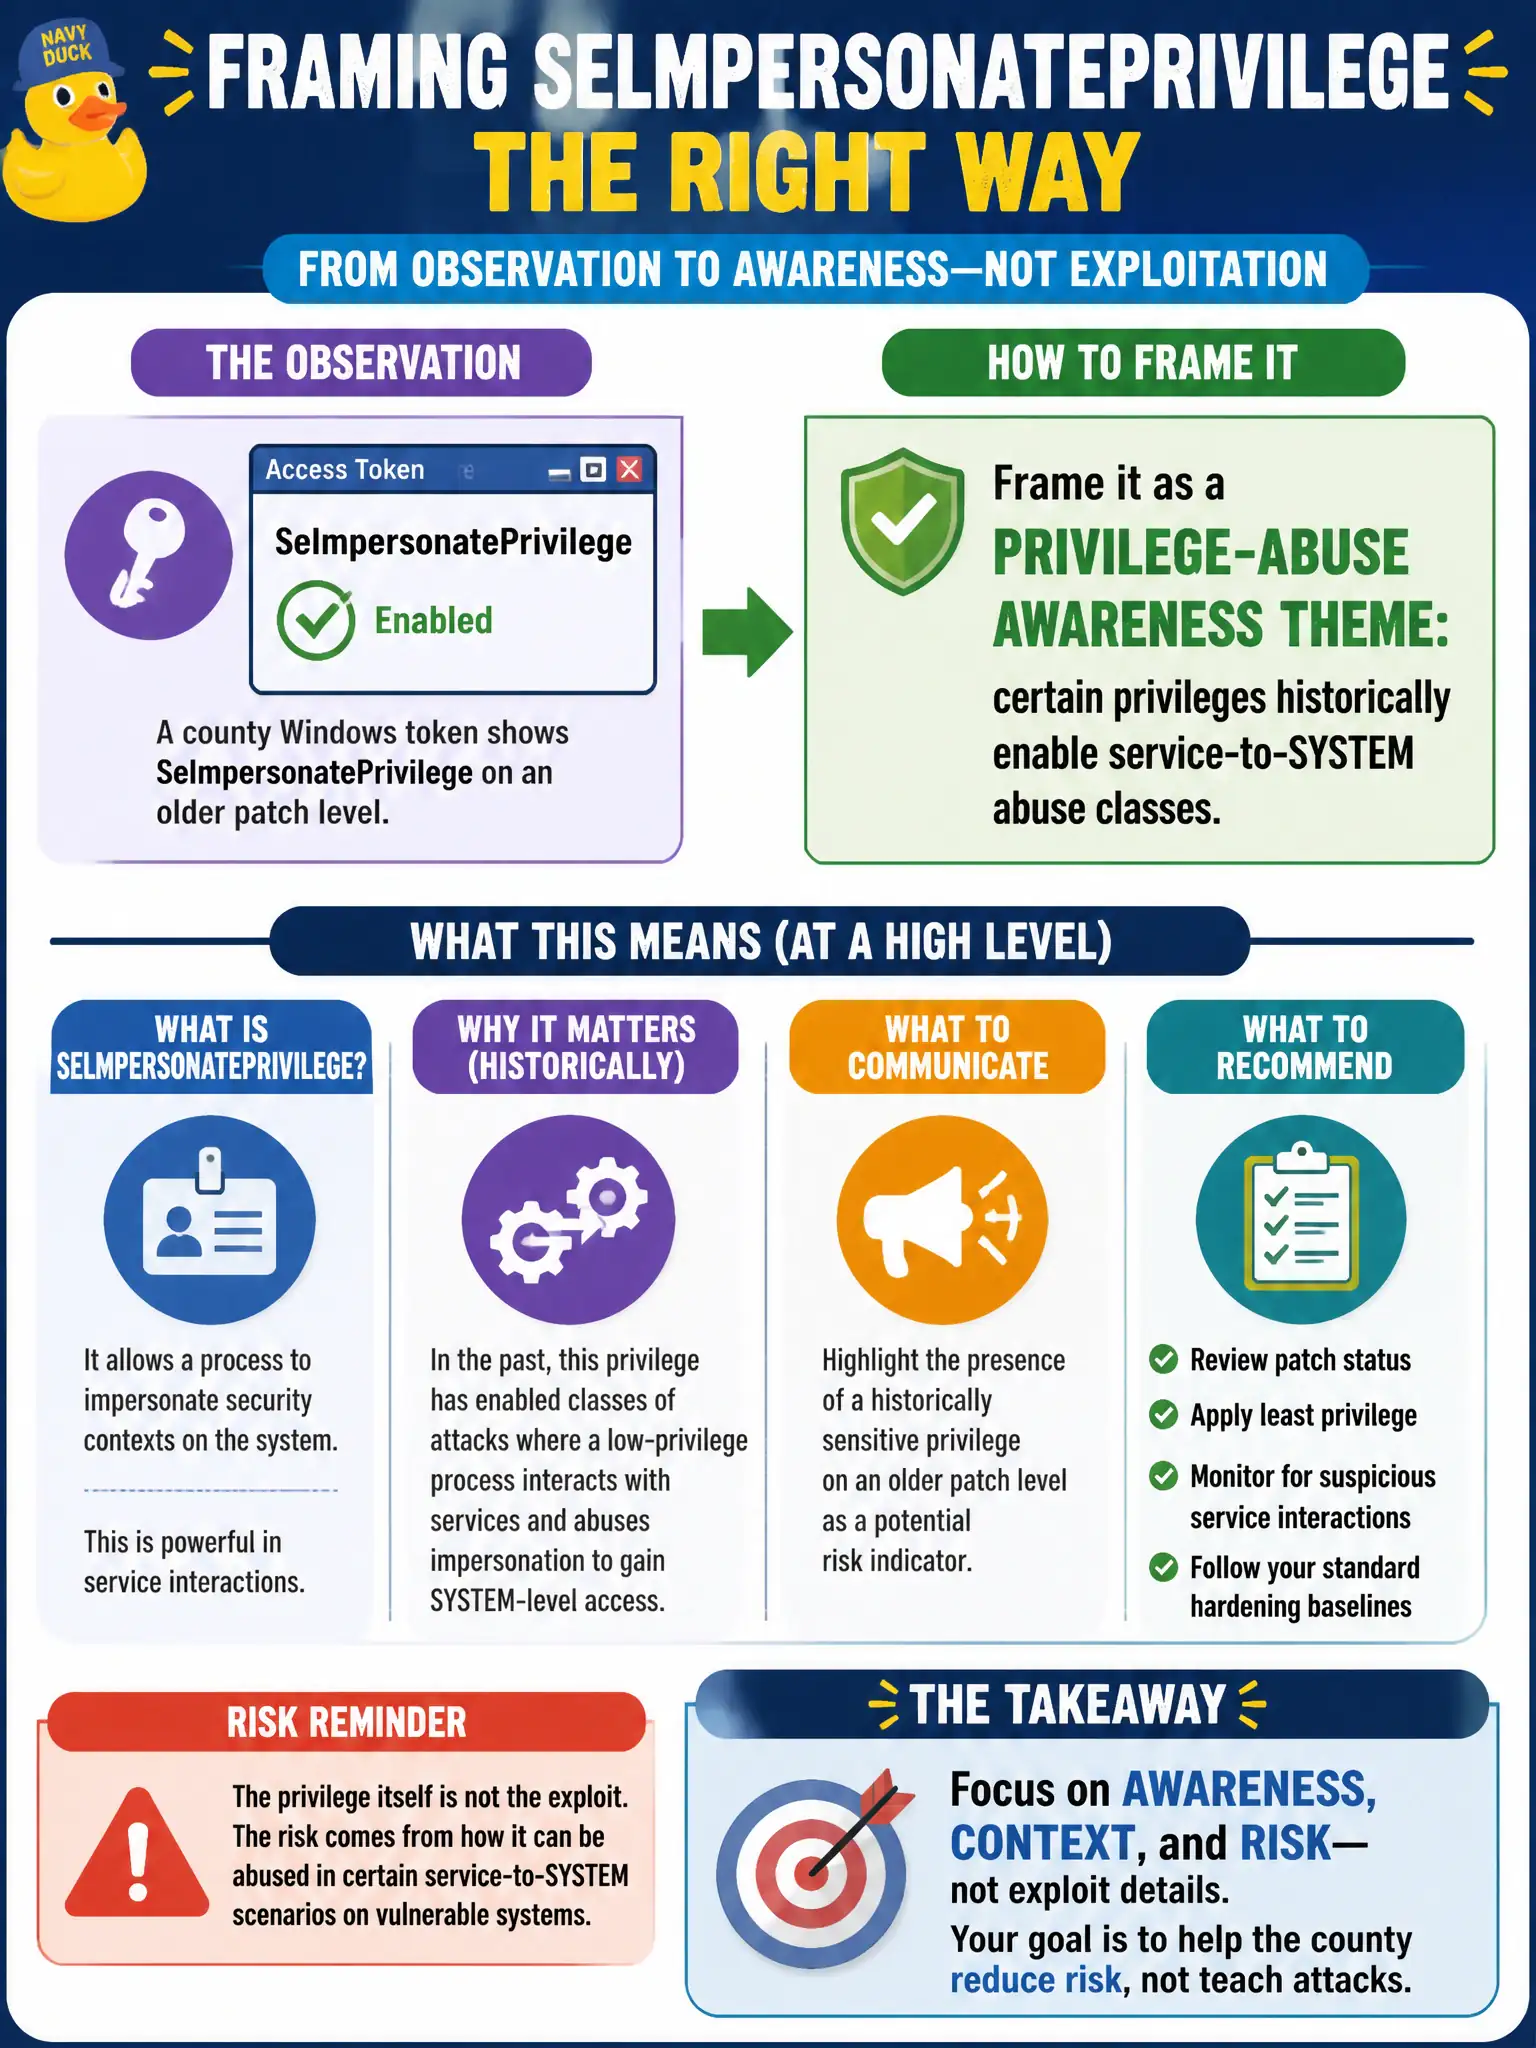
A county Windows token shows SeImpersonatePrivilege on an older patch level. How should the tester frame that privilege without diving into exploit steps?
Select an answer to reveal the explanation.
Short Explanation
SeImpersonatePrivilege is a special badge that historically let some service-context tricks climb toward SYSTEM on vulnerable builds. Spotting it is awareness, not an automatic Domain Admin trophy. Note the privilege and patch posture; do not treat it as a Windows wallpaper setting.
Full Explanation
A county Windows token showing SeImpersonatePrivilege on an older patch level should be framed as a privilege-abuse awareness theme: certain privileges have historically enabled service-to-SYSTEM abuse classes. Testers note the privilege and patch context without diving into exploit step recipes in exam-style explanations.
The privilege alone does not prove the account is already Domain Admin. It is not a printer color-profile signature. It is not a Linux capability bit incapable of appearing on Windows tokens.
Exam caveat: patch level, service accounts, and available listeners change practical exploitability; report the privilege as enabling risk with environmental context.
Operational check: inspect token privileges on the foothold, record OS build, and discuss whether high-risk privileges are required for the civic service account's job. Prefer removing unnecessary privileges over relying solely on patching. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same finding class still applies under the estate's current patch and configuration baseline.