
A county IT manager points at a green vulnerability-scanner dashboard and says the annual penetration test is finished. What clarification should the assessor give?
Select an answer to reveal the explanation.
Short Explanation
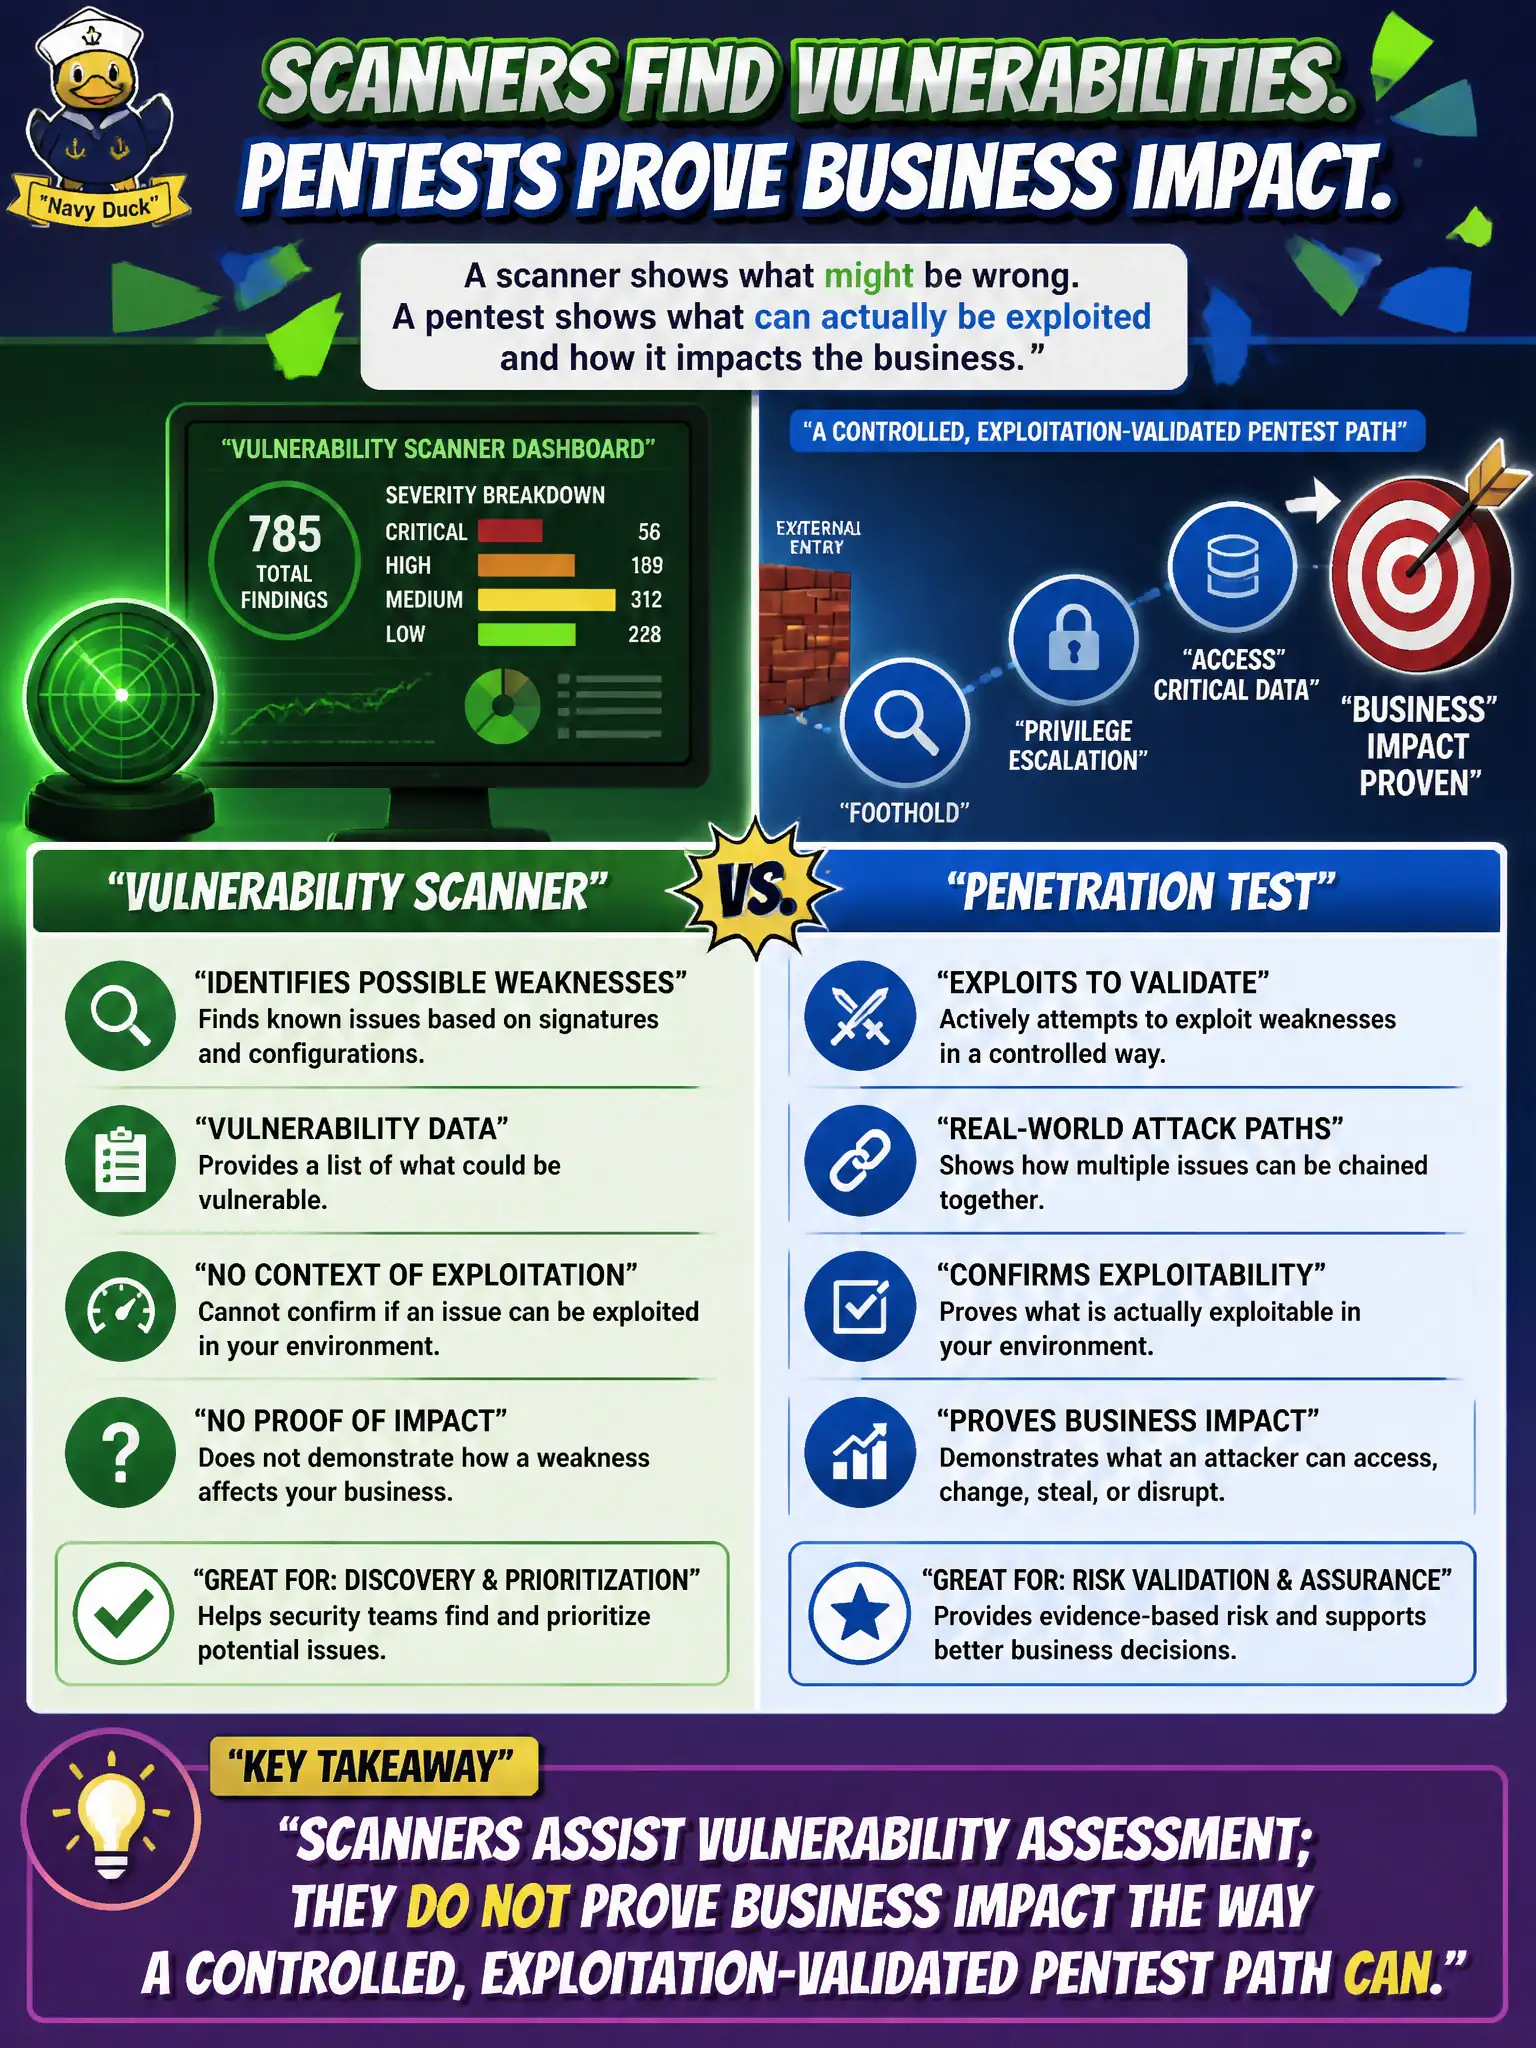
A green scanner light is like a smoke detector that did not beep—useful, but it is not a fire drill that walked every exit. VA finds candidates; a pentest shows what an attacker can actually chain under the RoE.
Full Explanation
A green vulnerability-scanner dashboard does not finish an annual penetration test for a county. Scanners assist vulnerability assessment; they do not prove business impact the way a controlled, exploitation-validated pentest path can. A green dashboard does not mean zero residual risk forever. Scanner greens do not depend on Metasploit as the engine to 'matter.' Penetration tests are not identical to VA scans merely because CVSS scores export to CSV. Exam caveat: CPTS-style thinking separates discovery tooling from validated attack paths and contextual impact. Operational check: explain to the IT manager which findings were only scanner-derived versus manually validated, propose authorized exploitation checks for high-risk items, and keep VA hygiene scheduled separately from periodic adversarial assessments. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services.