
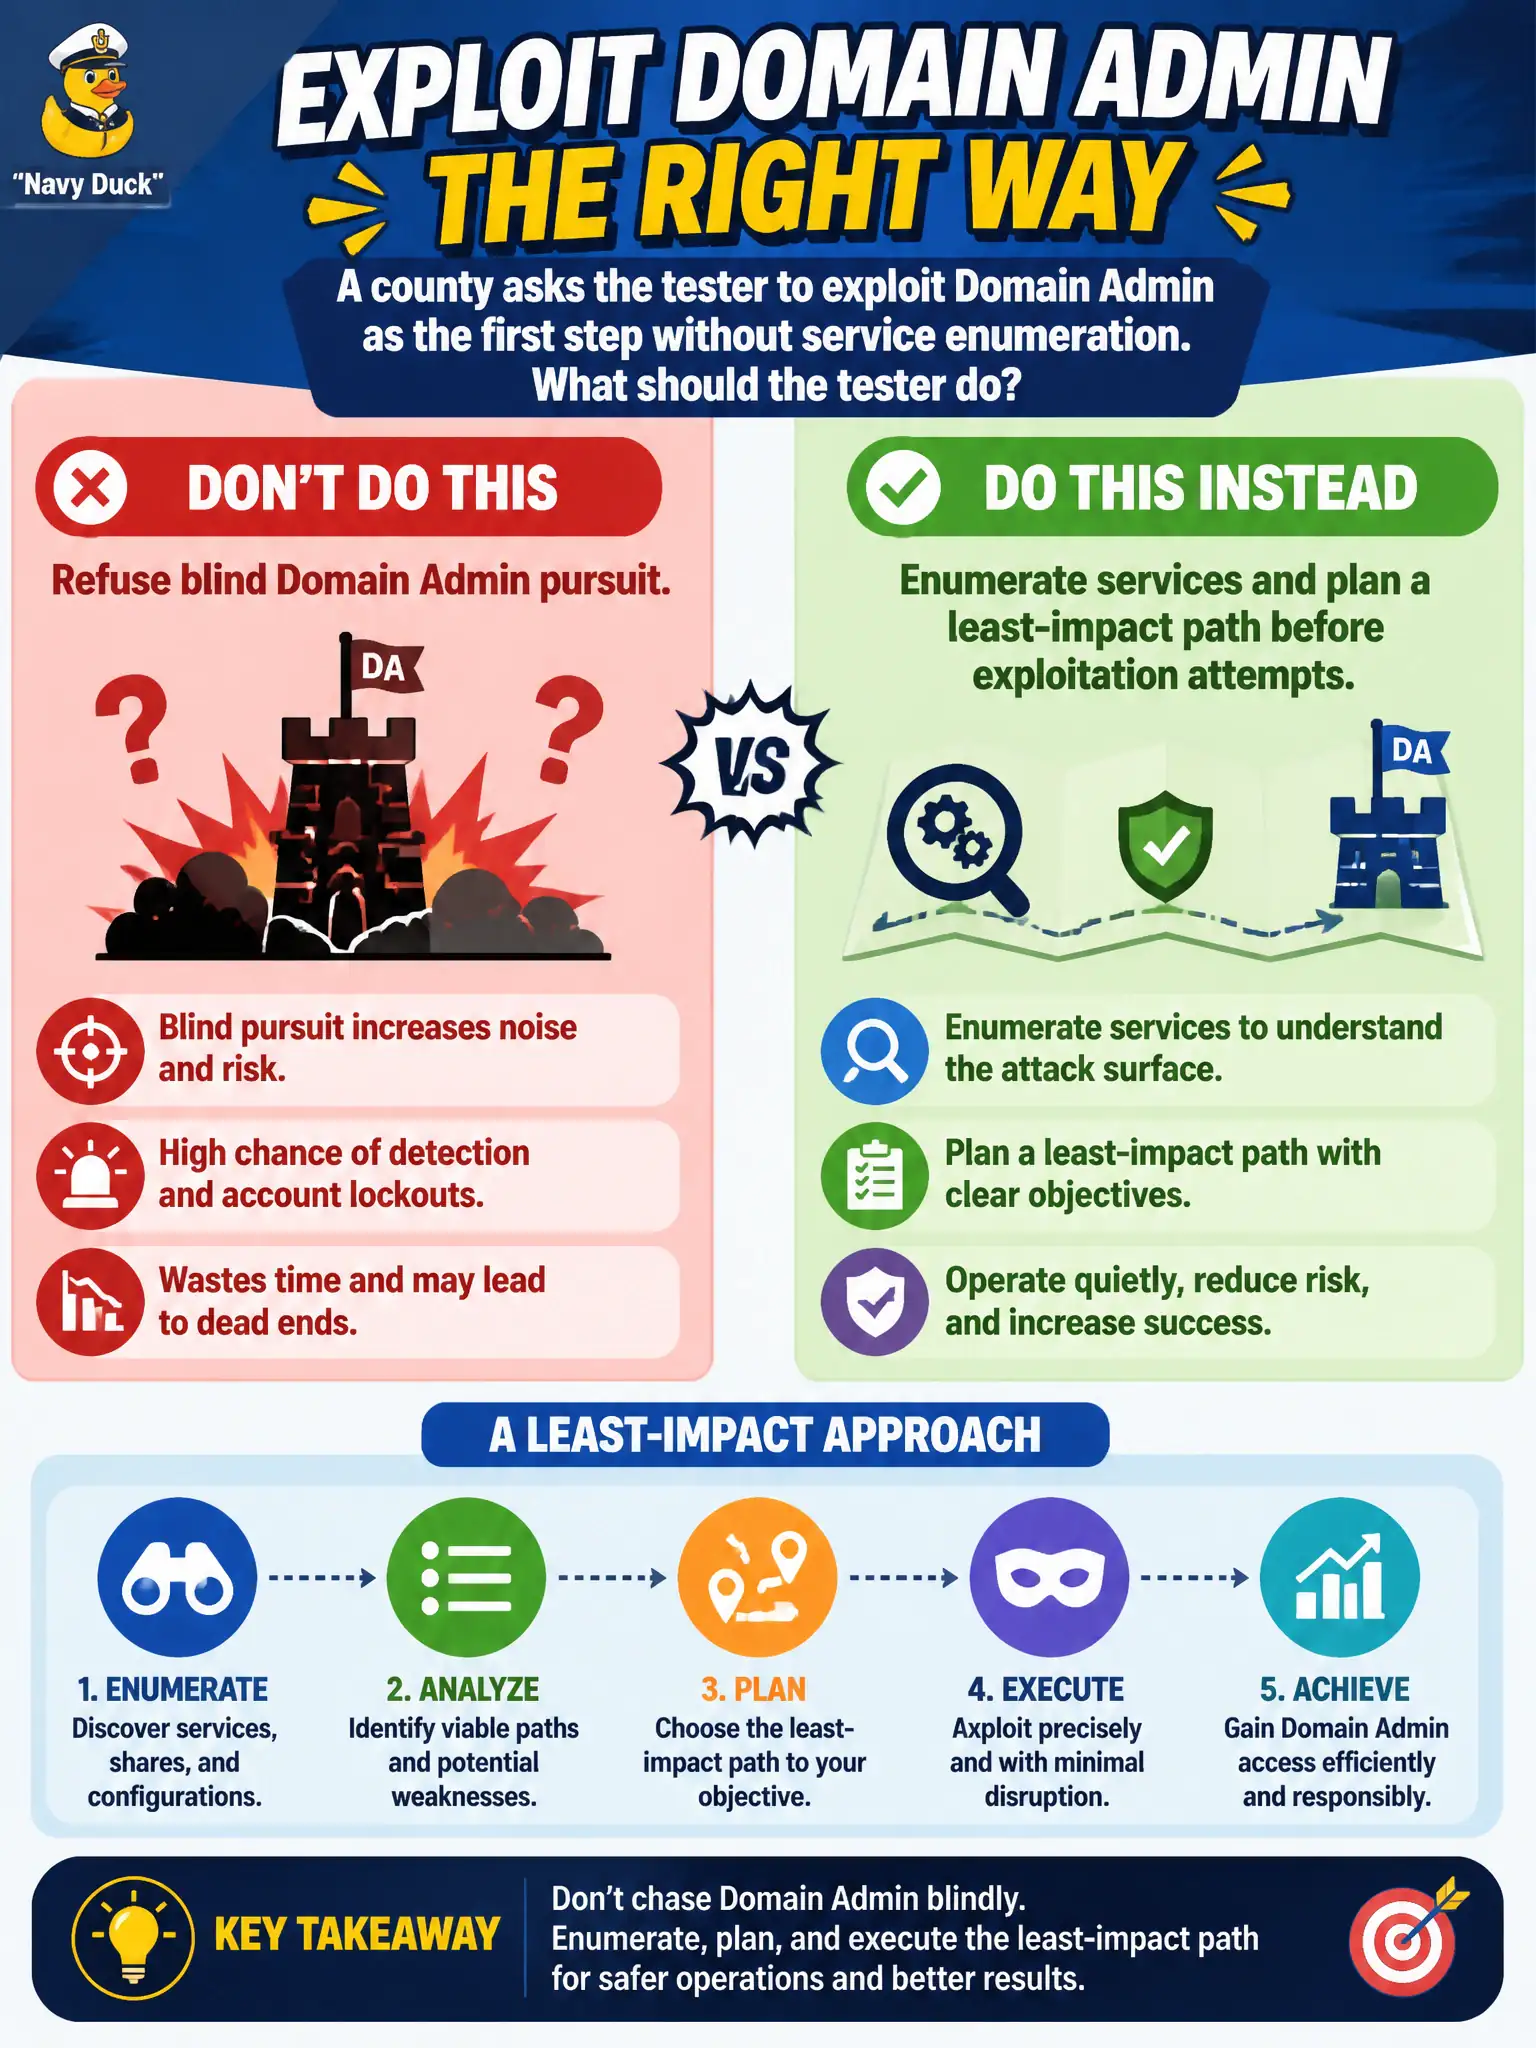
A county asks the tester to exploit Domain Admin as the first step without service enumeration. What should the tester do?
Select an answer to reveal the explanation.
Short Explanation
Charging straight at Domain Admin with no map is like kicking every door in a hallway hoping one is the vault. Enumerate, prioritize, and take the calmest path that still proves risk. Blind exploit spraying is how scopes and systems get hurt.
Full Explanation
If a county asks the tester to exploit Domain Admin as the first step without service enumeration, the tester should refuse blind Domain Admin pursuit and instead enumerate services and plan a least-impact path before exploitation attempts. Spraying popular exploit modules at every host until Domain Admin appears is noisy, unsafe, and unaligned with professional scoping for civic directories. Skipping enumeration because Domain Admin would make service details unnecessary inverts methodology: you need context to choose safe, relevant techniques and to explain impact. Beginning with domain-wide destructive tests to prove impact quickly to sponsors risks production harm and violates typical municipal RoE. Exam caveat: CPTS-style professionalism prioritizes enumeration-driven, least-impact paths over prestige objectives. Operational check: document current identity context, high-value services, and approved techniques; agree objectives with the sponsor in writing; only then attempt exploitation that supports demonstrated risk to agreed crown jewels. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services.