
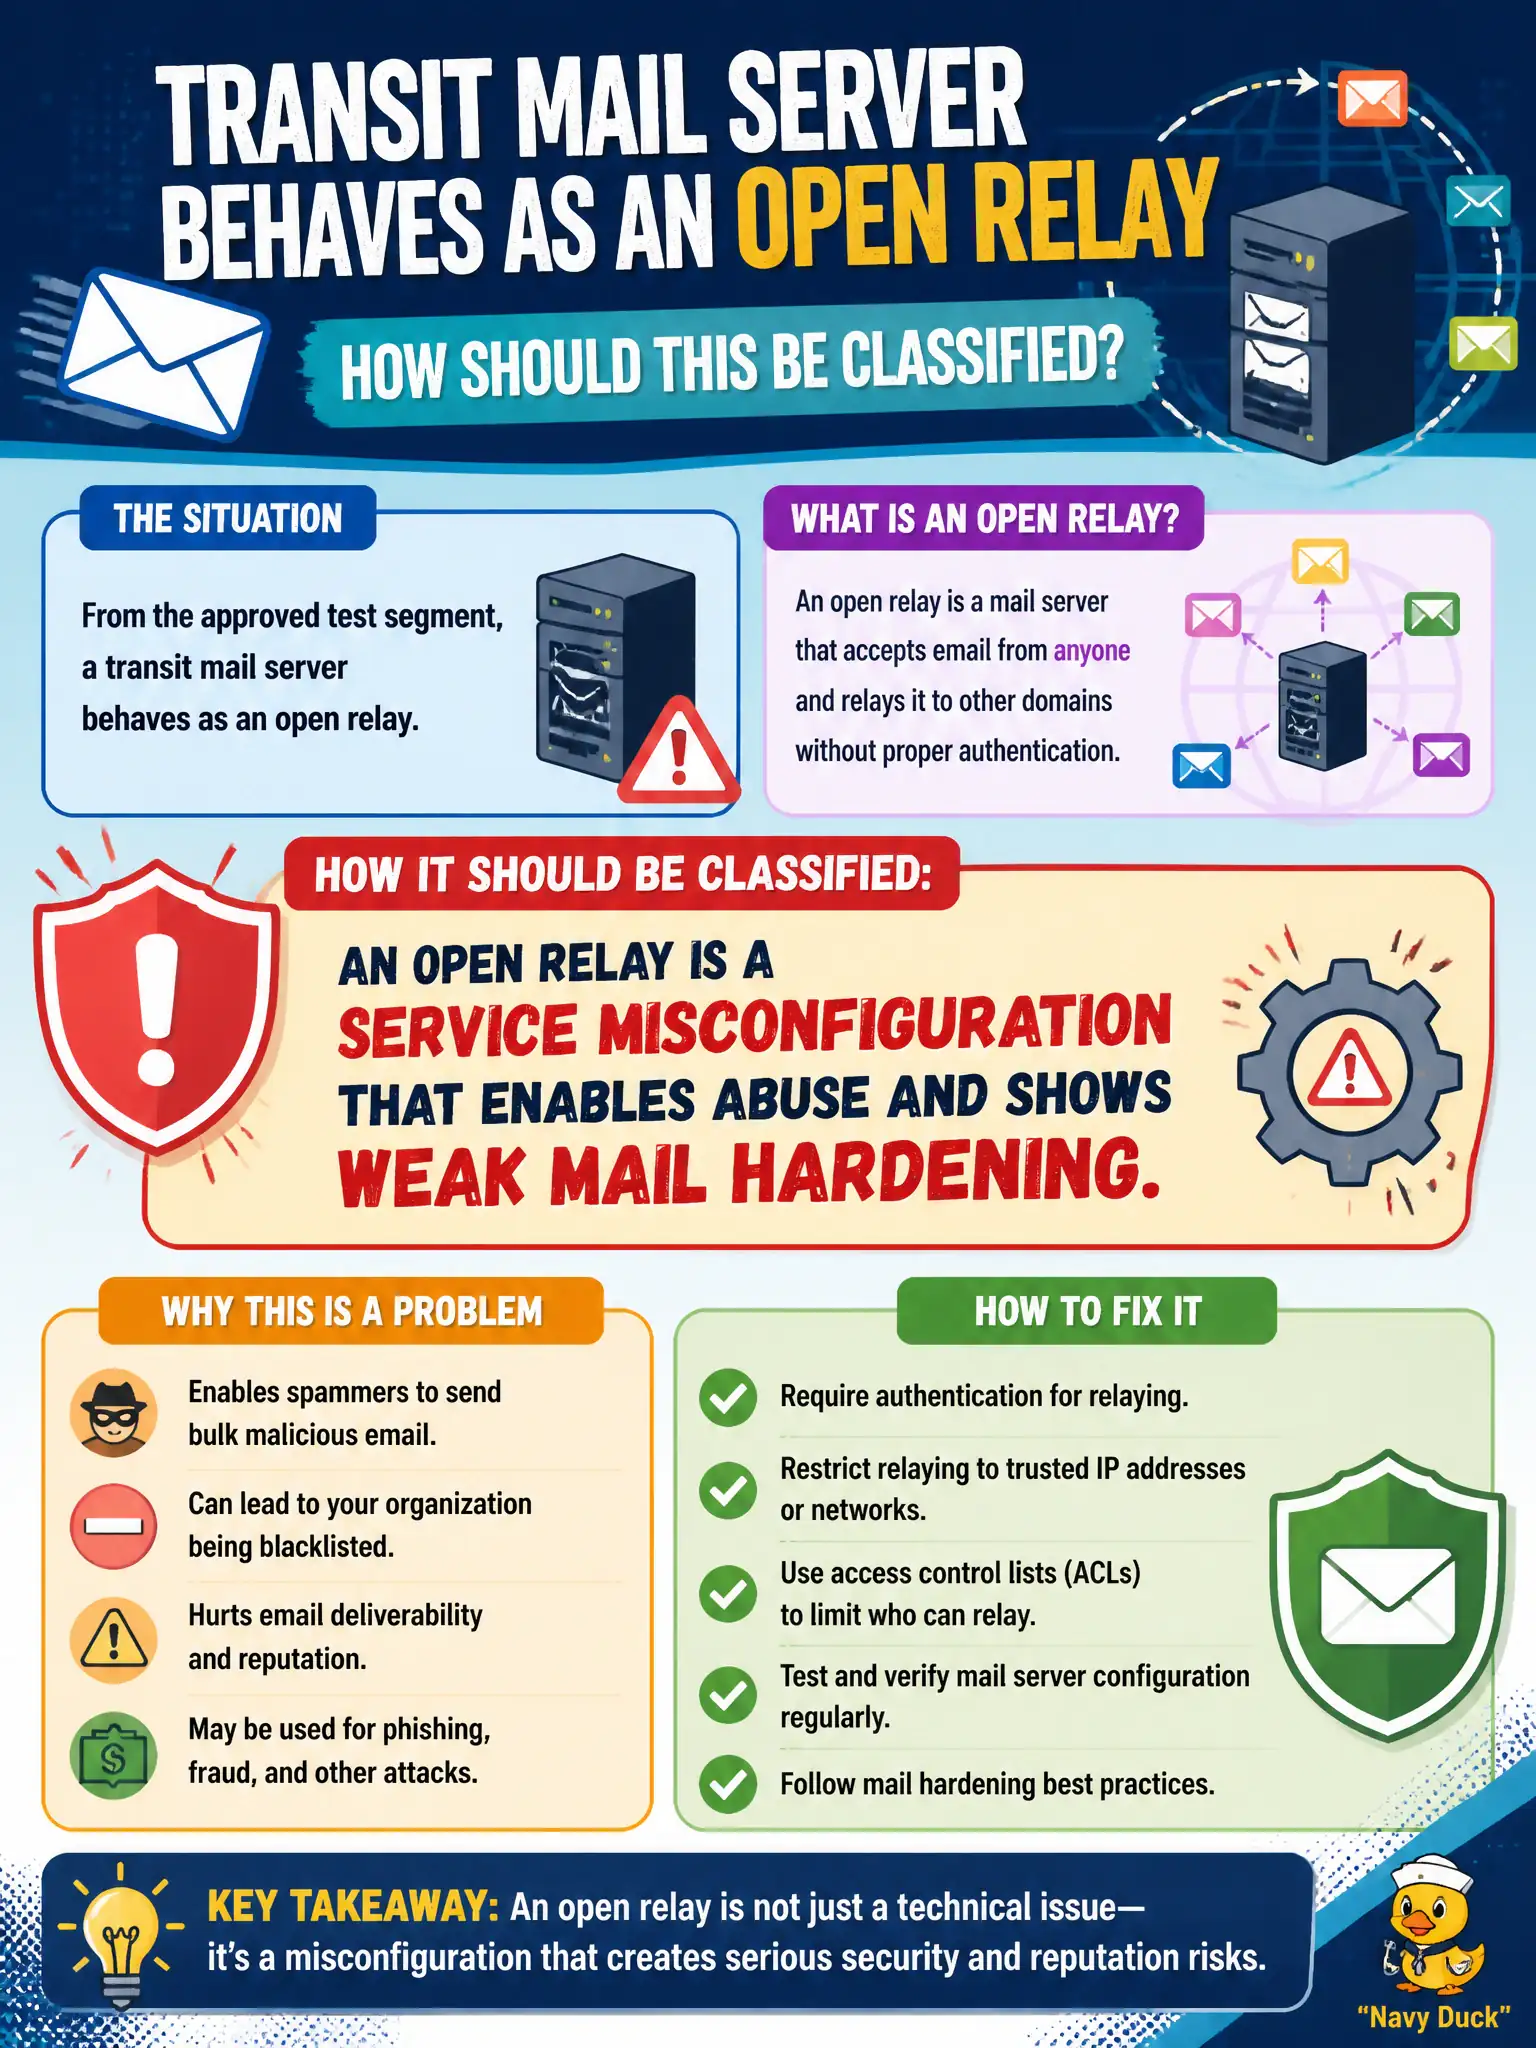
From the approved test segment, a transit mail server behaves as an open relay. How should this be classified?
Select an answer to reveal the explanation.
Short Explanation
An open relay is a postage machine that stamps anyone’s mail—sooner or later it gets abused. Even if you didn’t watch spam fly during the test, the misconfig is the problem. Harden who can relay; don’t wait for the complaint pile.
Full Explanation
From the approved test segment, a transit mail server that behaves as an open relay should be classified as a service misconfiguration that enables abuse and shows weak mail hardening. Open relays are not a networking convenience to omit from security reports; they enable spam and phishing infrastructure abuse that can damage municipal reputation and blocklists. Limiting mail-relay findings to cloud SaaS tenants invents an on-prem exemption that does not exist. Absence of observed spam during the short test window does not prove the relay is closed—abuse may occur outside the engagement. Exam caveat: demonstrate relay behavior with authorized, non-destructive tests that do not send unsolicited mail to the public. Operational check: document the permitted test that shows third-party relay acceptance, recommend authentication and relay restriction to legitimate transit mail clients, and verify outbound reputation monitoring with the city’s messaging team after remediation. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services.