
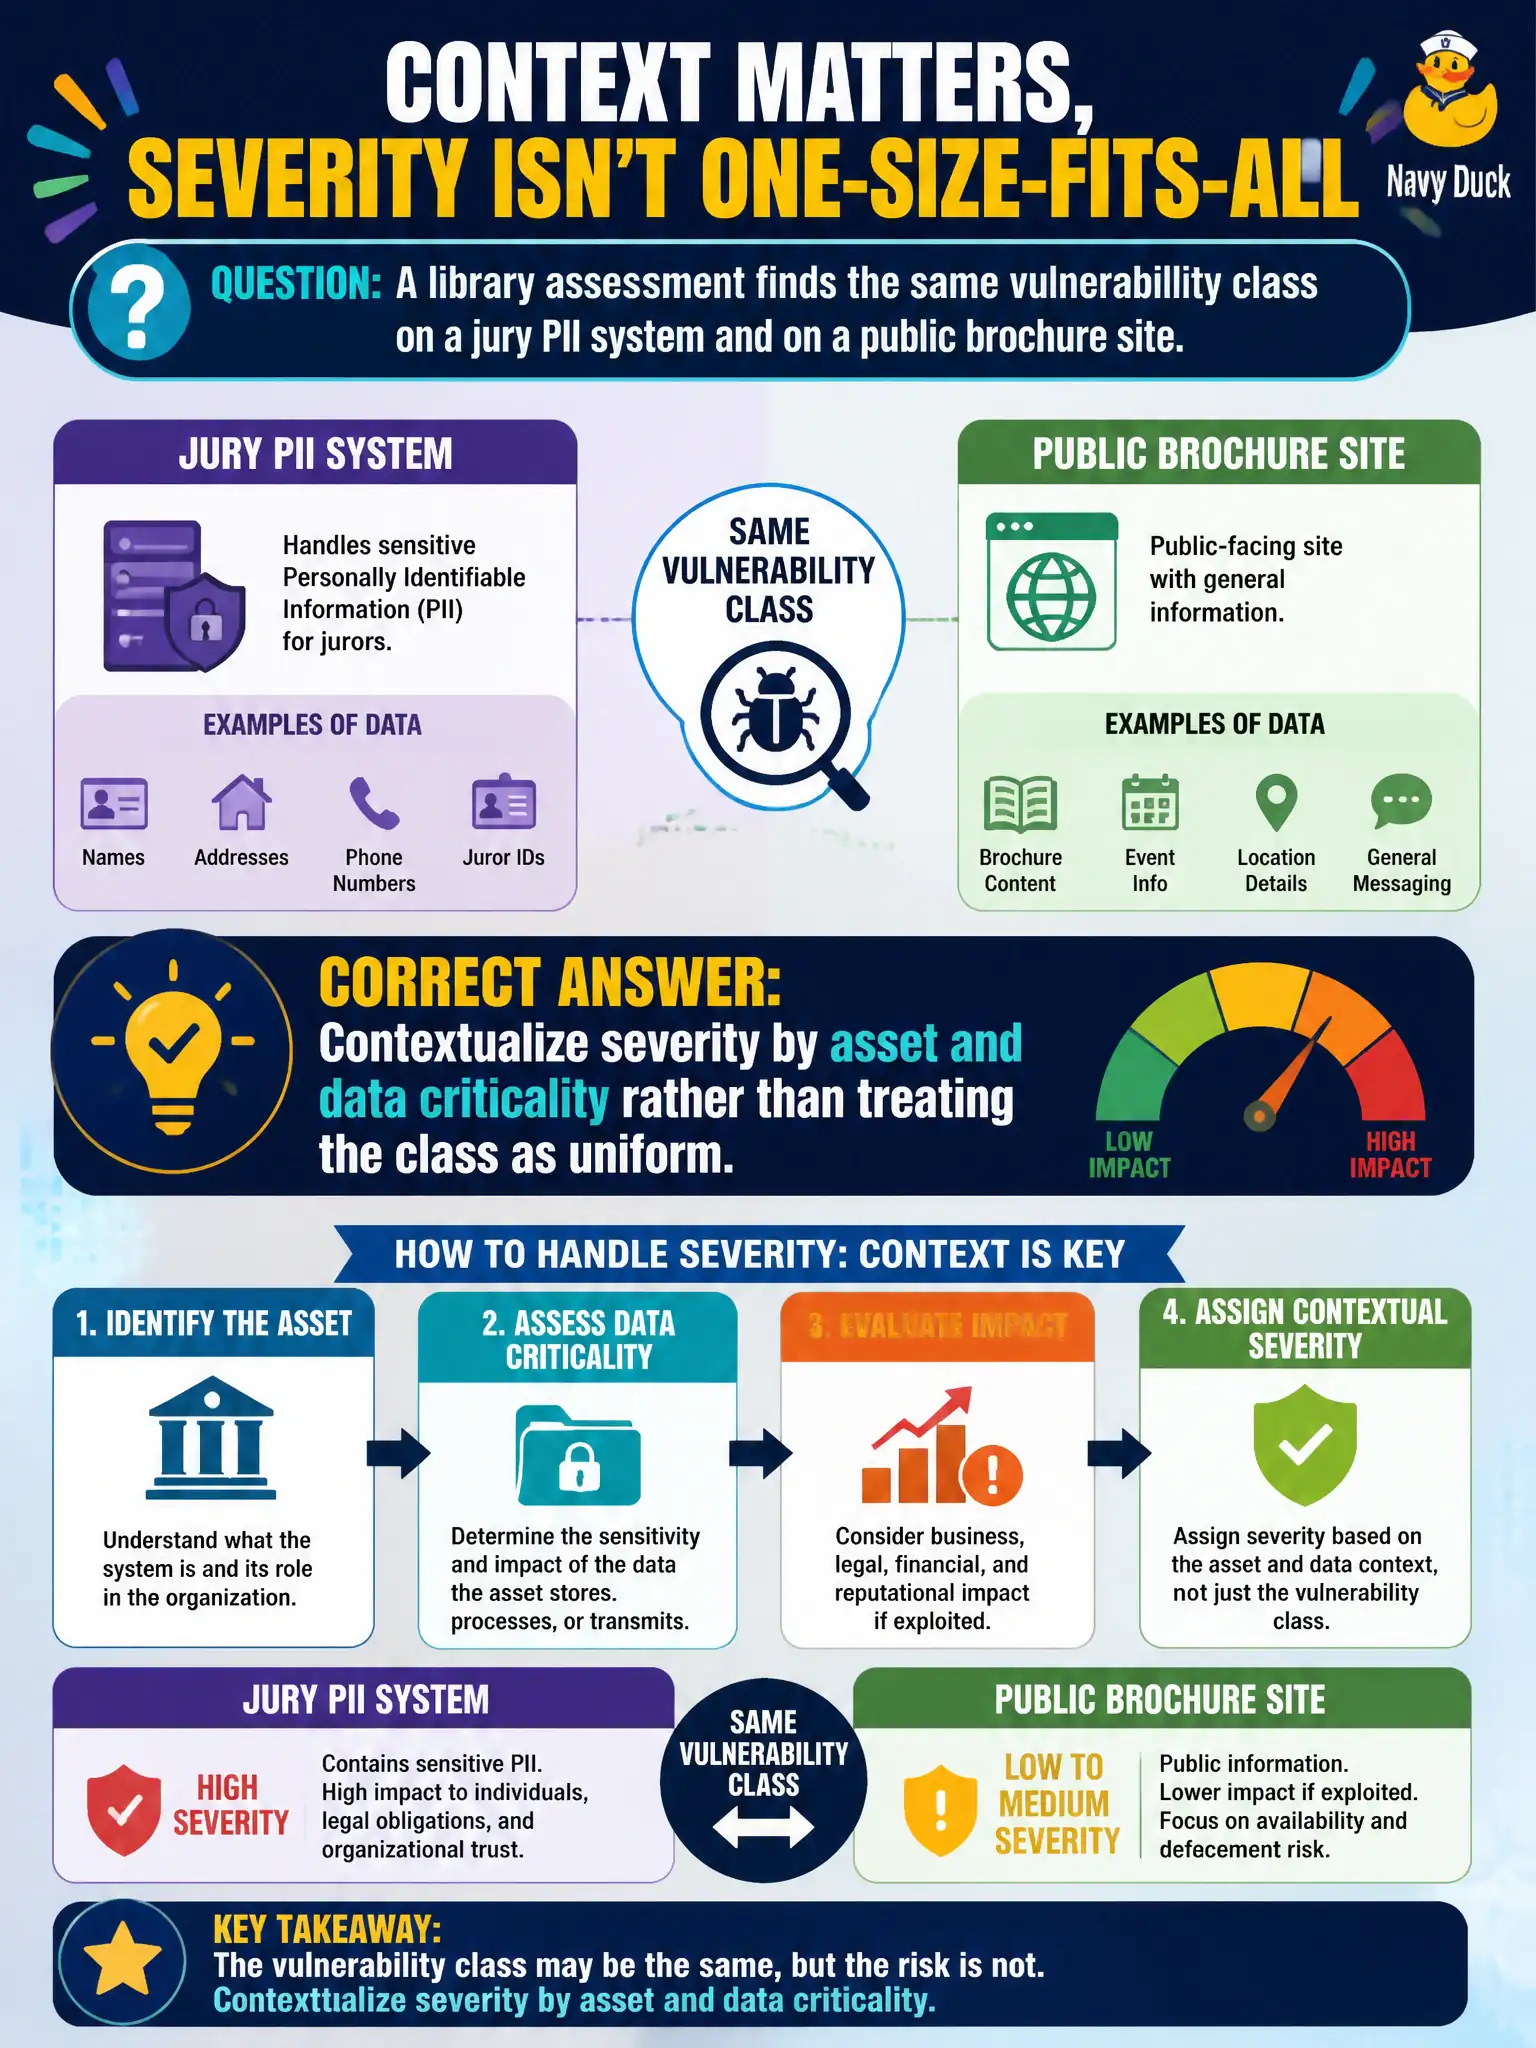
A library assessment finds the same vulnerability class on a jury PII system and on a public brochure site. How should severity be handled?
Select an answer to reveal the explanation.
Short Explanation
Same hole, different treasure. A brochure site leak is annoying; a jury PII system leak is a crisis. Severity has to respect what the asset protects.
Full Explanation
When the same vulnerability class appears on a library jury PII system and on a public brochure site, severity must be contextualized by asset and data criticality rather than treating the class as uniform. Confidentiality impact on court-related PII outweighs identical technical bugs on low-sensitivity brochure content.
Always scoring both as identical criticals ignores environment. Downgrading the PII system because courts are 'low priority' inverts civic values. Skipping severity for CVE IDs alone fails prioritization needs.
Exam caveat: CVSS base scores still need environmental/narrative adjustment for municipal impact.
Operational check: score each instance with asset sensitivity notes, explain divergence to stakeholders, and prioritize the jury PII system remediation in the library's plan. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same finding class still applies under the estate's current patch and configuration baseline. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services.