
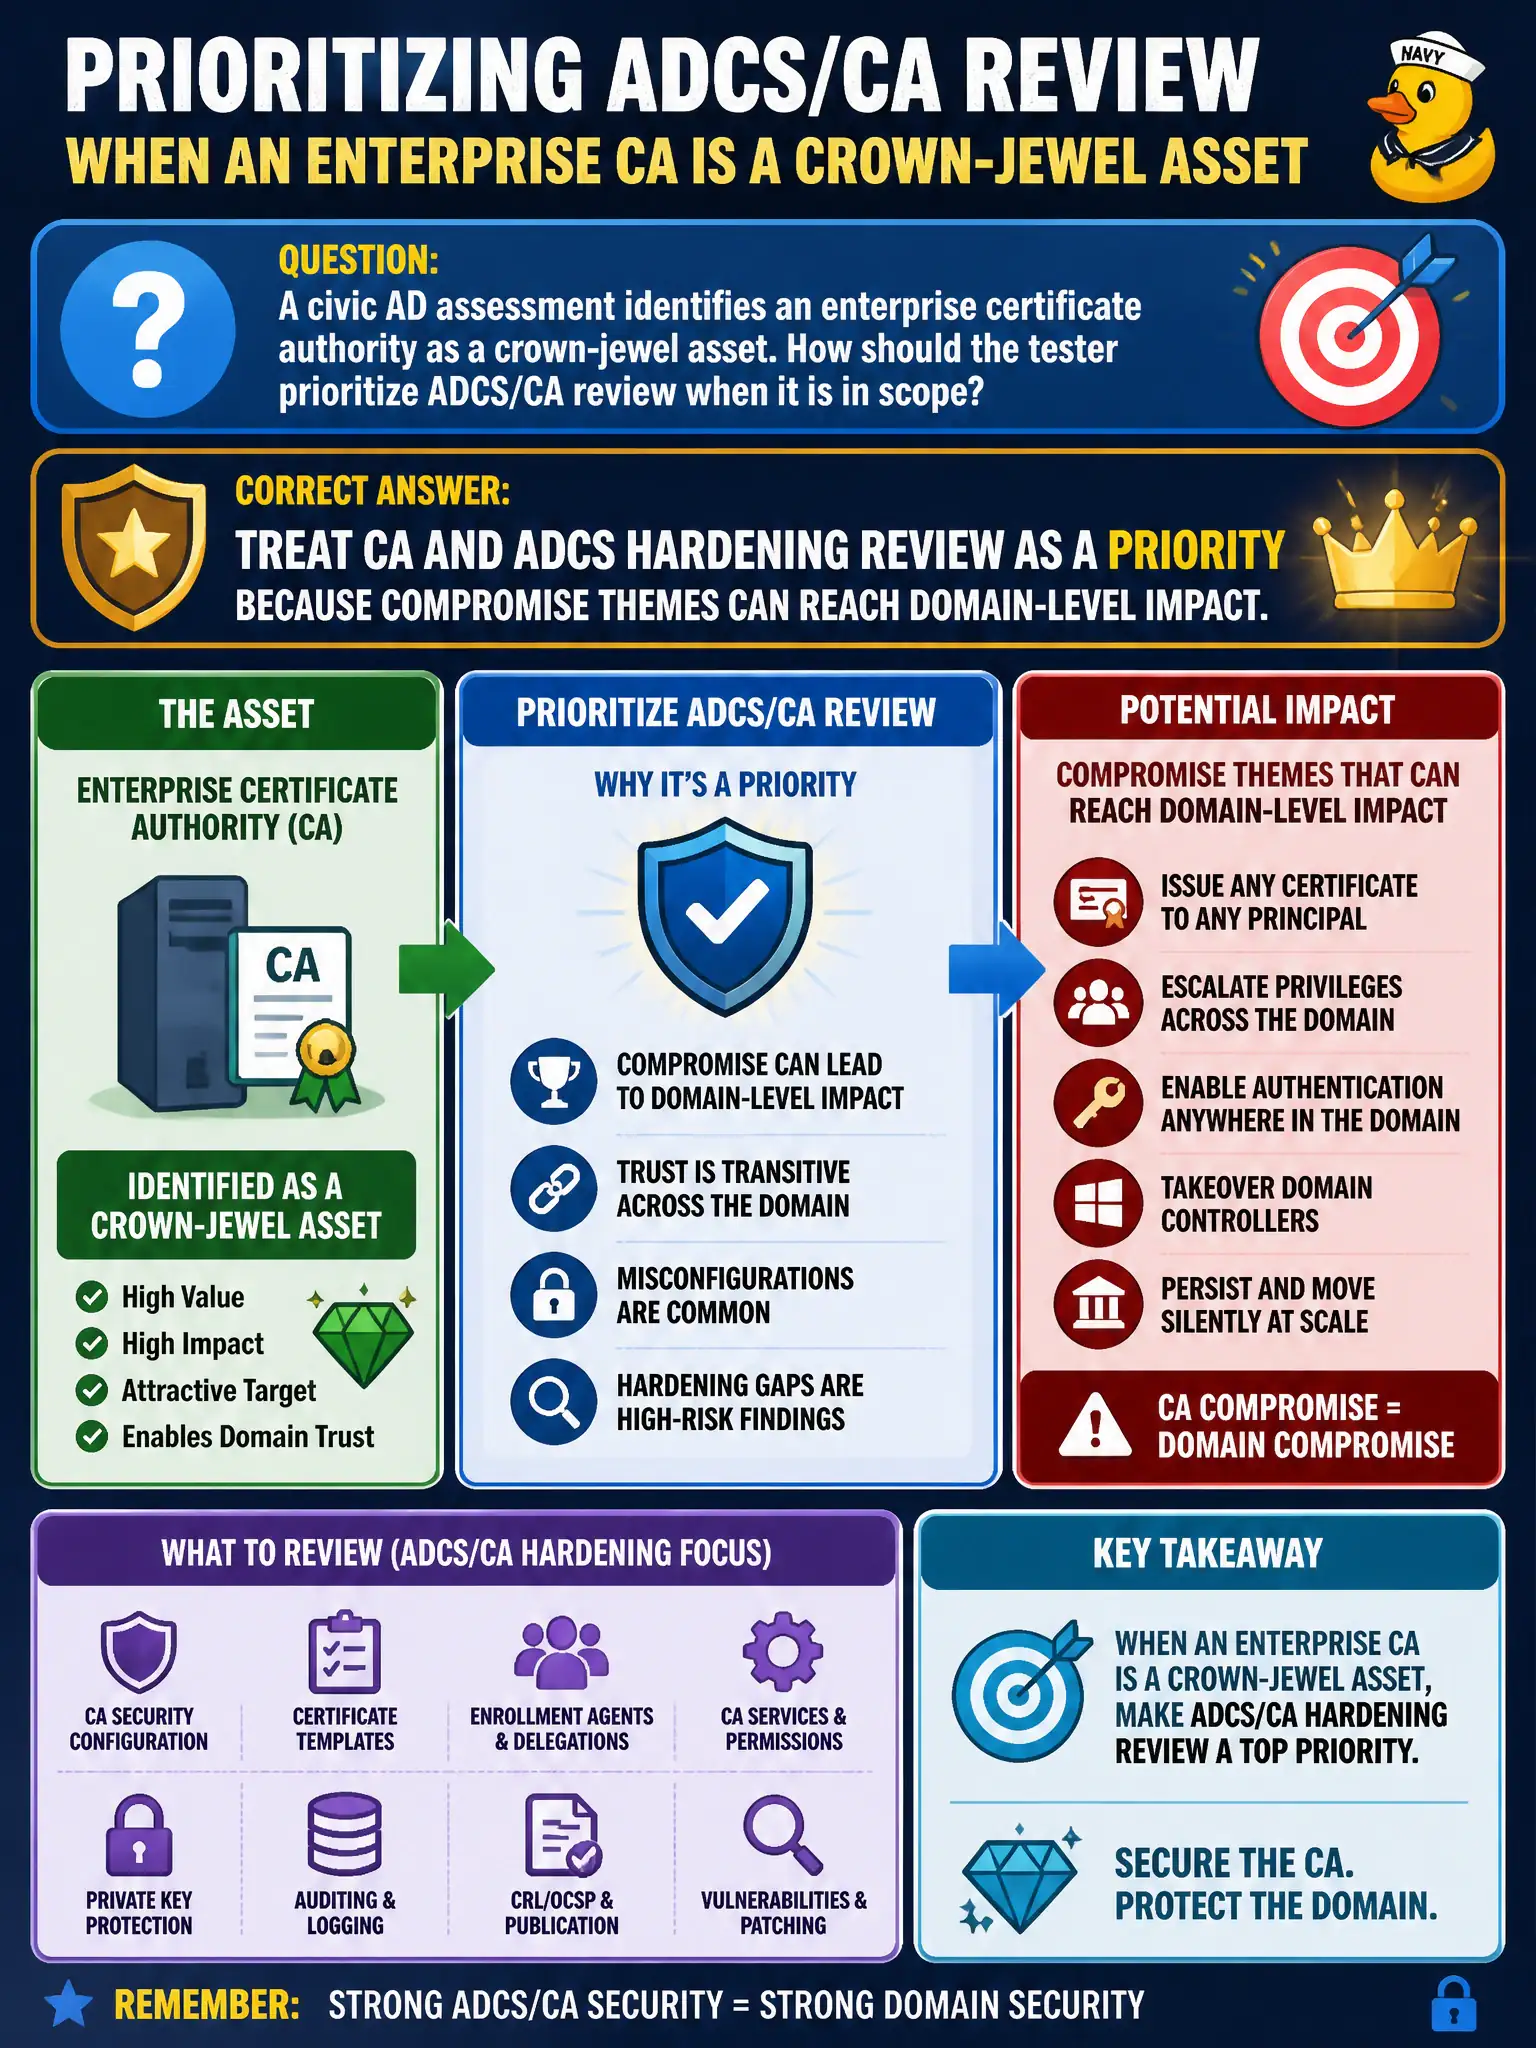
A civic AD assessment identifies an enterprise certificate authority as a crown-jewel asset. How should the tester prioritize ADCS/CA review when it is in scope?
Select an answer to reveal the explanation.
Short Explanation
A CA that the domain trusts is like a badge printer that can mint official credentials. If that printer is soft, the blast radius can rival domain compromise stories. When ADCS is present and in scope, it earns crown-jewel attention — not a shrug.
Full Explanation
When an enterprise certificate authority / ADCS is in scope, treat CA hardening review as a priority because certain certificate-service compromise themes can reach domain-level impact. For civic environments, the CA underpins authentication and encryption trust; weak templates, enrollment rights, or CA host controls can escalate beyond “just websites.”
Ignoring certificate services unless e-commerce exists understates ADCS risk in municipal AD. CAs are not limited to public website SSL with no domain-trust relevance. ADCS review belongs in Active Directory assessments when in scope, not only wireless surveys.
Exam caveat: prioritize ADCS findings by enrollment abuse potential and privilege impact while staying RoE-safe—describe classes of risk without delivering exploit recipes. CPTS AD crown-jewel lists often include CAs beside DCs.
Operational check: inventory enterprise CAs and sensitive templates, review who can enroll, harden CA hosts, and document residual domain-impact themes for the municipal PKI/AD owners. Add the enterprise CA to the county crown-jewel register alongside DCs, with patching and enrollment-rights reviews on a fixed civic identity calendar. Certificate enrollment rights deserve the same periodic ACL review cadence as Domain Admin membership.