
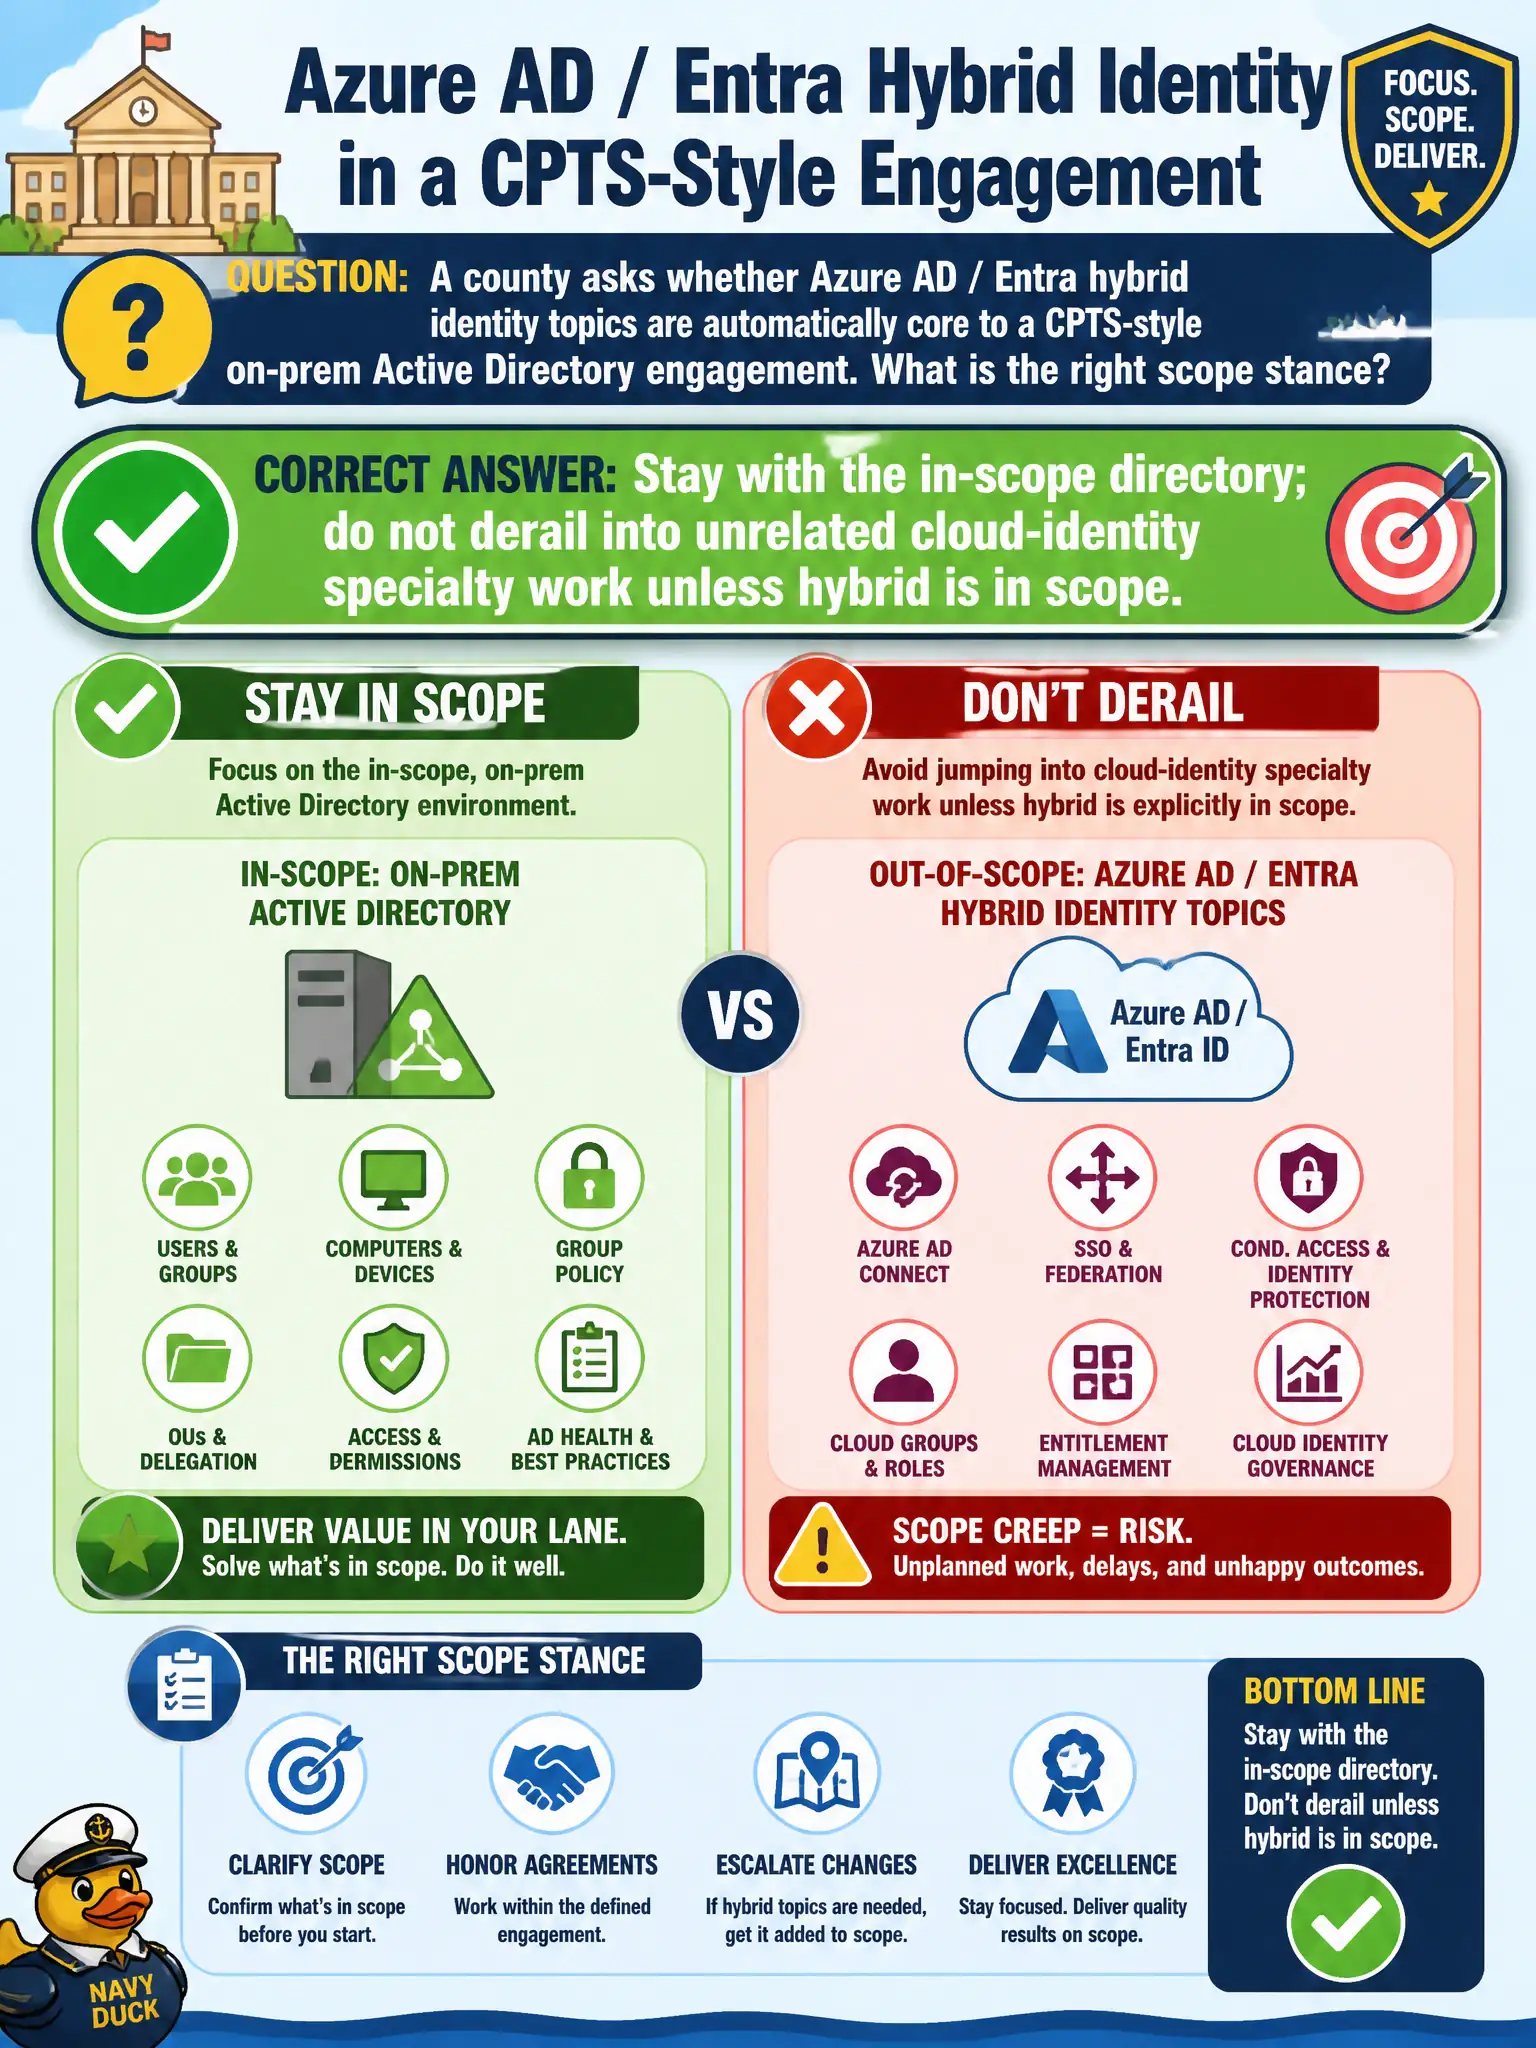
A county asks whether Azure AD / Entra hybrid identity topics are automatically core to a CPTS-style on-prem Active Directory engagement. What is the right scope stance?
Select an answer to reveal the explanation.
Short Explanation
Stay on the map you were hired to walk. If the RoE is on-prem AD paths, do not wander into a different cloud-identity exam just because hybrid exists somewhere. Scope first; specialty detours only when authorized.
Full Explanation
Scope discipline keeps CPTS-style on-prem Active Directory work useful. Unless hybrid identity is explicitly in scope, the tester should stay with the in-scope directory and not derail into unrelated Entra/Azure AD specialty work. A county asking about automatic inclusion of hybrid topics needs a clear stance: cover hybrid only when authorized and relevant to the agreed municipal boundaries.
On-prem AD findings are not obsolete; Kerberos, ACL, and delegation paths remain core. Hybrid themes do not replace all Kerberos and ACL analysis on every engagement. CPTS does not require full Microsoft 365 tenant takeover evidence for every AD report.
Exam caveat: read the RoE and target list; cloud-identity pivots without authorization are scope failures even if technically adjacent. Report hybrid observations as out-of-scope recommendations when they appear but were not authorized for deep testing.
Operational check: confirm written scope for on-prem vs hybrid, keep evidence collection inside that boundary, and note any hybrid risks as residual recommendations for the civic identity program if not tested. Keep hybrid recommendations crisp and separate so municipal sponsors can fund a follow-on Entra review without confusing this engagement’s evidence.