
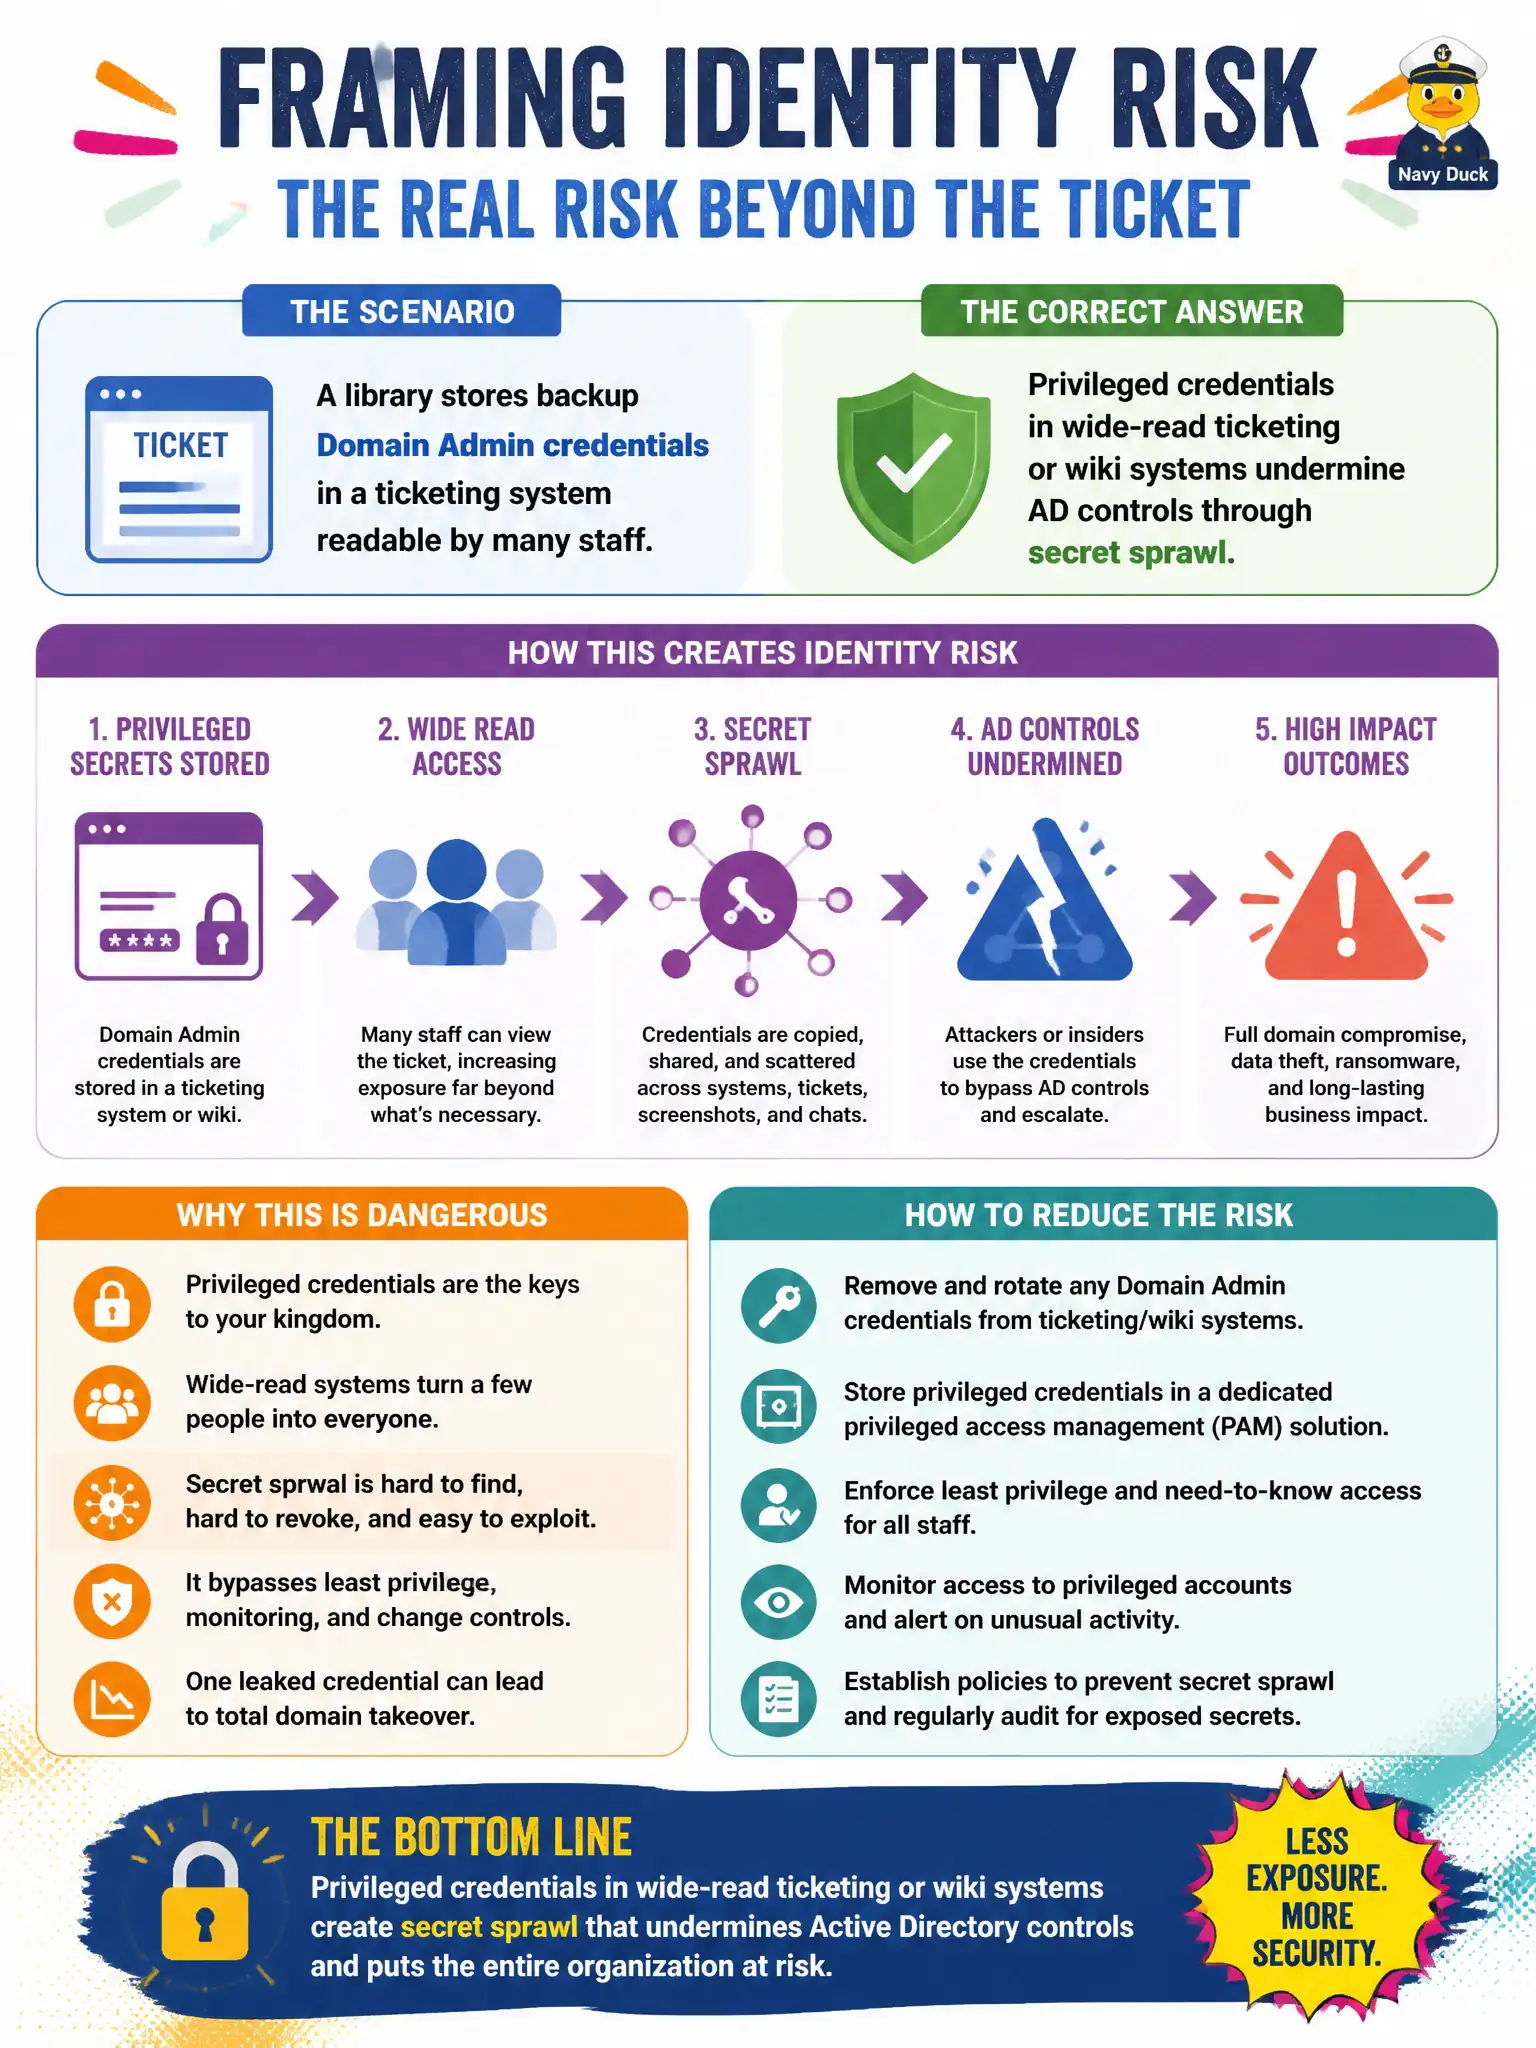
A library stores backup Domain Admin credentials in a ticketing system readable by many staff. How should identity risk be framed?
Select an answer to reveal the explanation.
Short Explanation
The strongest Domain Admin password still fails if it is taped to the break-room fridge — or a ticket queue everyone can open. Secret sprawl outside AD bypasses directory ACLs. Keep privileged creds in a real vault with tight ACL eyes.
Full Explanation
Privileged credentials stored in wide-read ticketing or wiki systems undermine Active Directory controls through secret sprawl. When a library parks backup Domain Admin passwords where many staff can read them, AD group membership and password complexity become irrelevant to anyone who opens the ticket—identity risk extends beyond the directory into the collaboration stack serving the same institution.
Secrets outside AD are highly relevant because attackers and insiders use them to authenticate as those AD principals. Marking a ticket “confidential” in the subject line does not enforce access control. Emailing backup DA passwords monthly is the opposite of good hygiene.
Exam caveat: report secret sprawl as an identity finding with AD impact even when the store is not NTDS. CPTS-style assessments should note where crown-jewel credentials live outside the directory.
Operational check: search ticketing/wiki for privileged secrets, rotate exposed DA credentials, move them into an approved vault with least privilege, and audit who previously had read access across the civic staff population. Secret sprawl findings should drive vault adoption for libraries and other civic orgs that historically stored admin passwords in tickets.