
A civic application service runs as Domain Admin without a strong justification. What recommendation aligns with AD least privilege?
Select an answer to reveal the explanation.
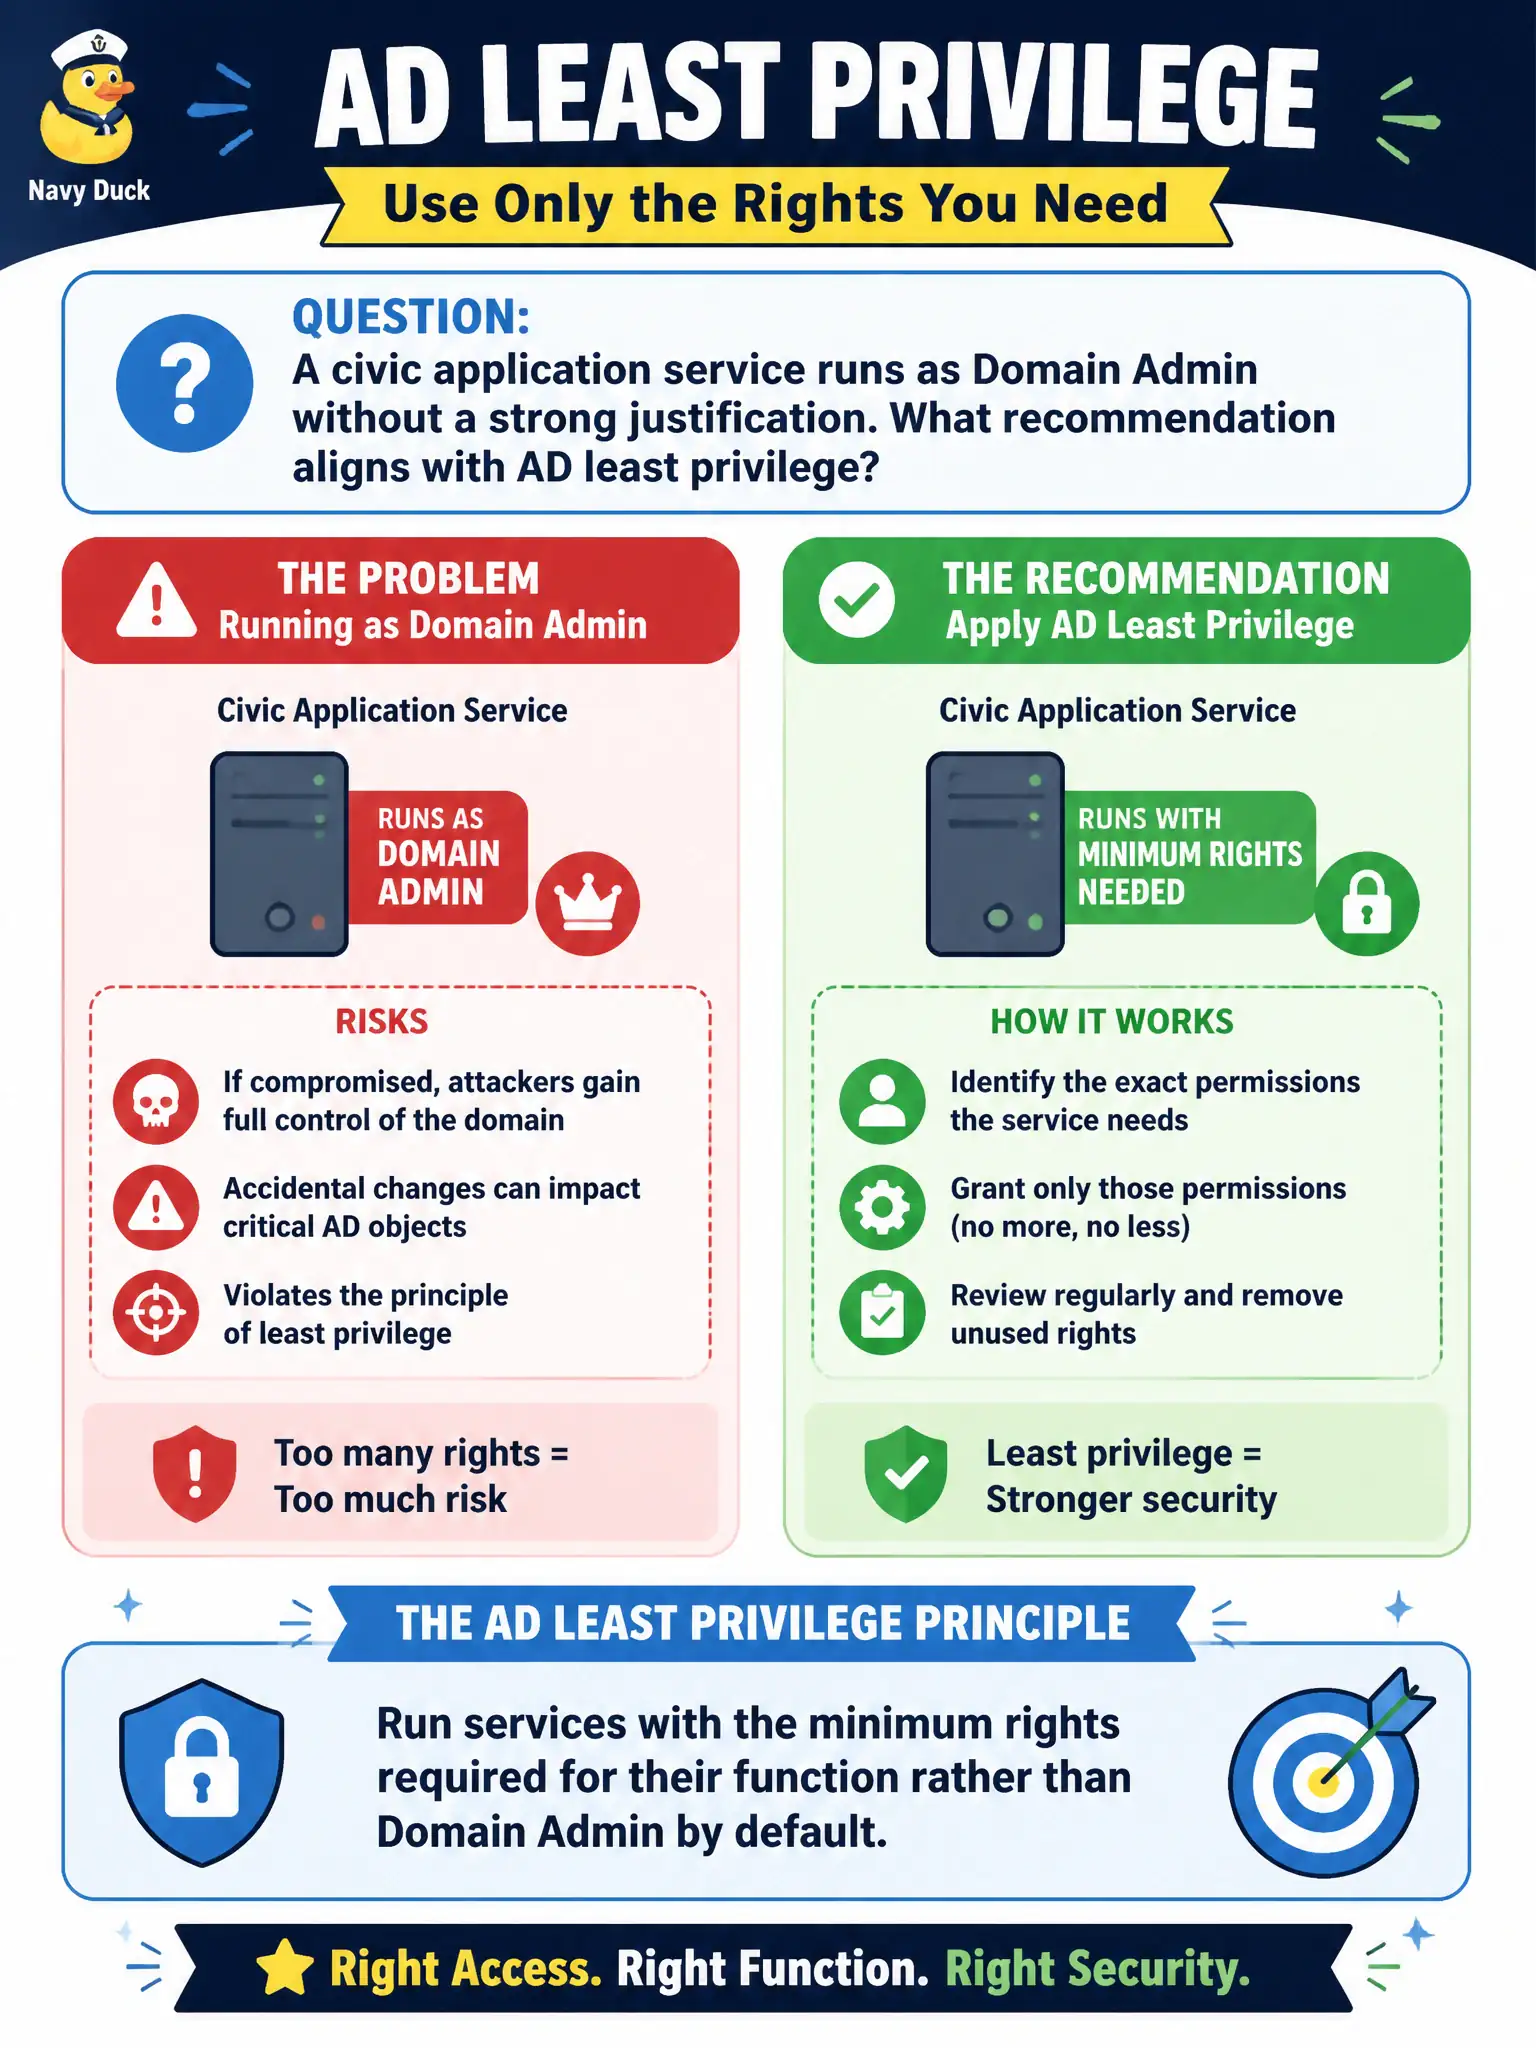
Short Explanation
A service that needs to print tickets does not need the keys to city hall. Domain Admin for ordinary app services is privilege theater gone wrong. Dial it down to what the job actually requires.
Full Explanation
When a civic application service runs as Domain Admin without strong justification, the recommendation that aligns with AD least privilege is to run services with the minimum rights required for their function rather than Domain Admin by default. Preferring Domain Admin for all services so troubleshooting never needs permission changes maximizes blast radius. Disabling the service account password so Domain Admin rights “cannot be abused” breaks authentication models and does not safely remove privilege. Granting Domain Admin to the service and every developer workstation for consistency is the opposite of tiering. Exam caveat: service identity privilege is a standing risk independent of patch level. Operational check: map required resources for the app, design a least-privilege service account or gMSA, remove DA membership, and verify the app still functions in a municipal staging OU before production cutover. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services. Re-validate the same judgment after the next change window so the control still holds under the city’s current tooling, identity posture, and RoE amendments.