
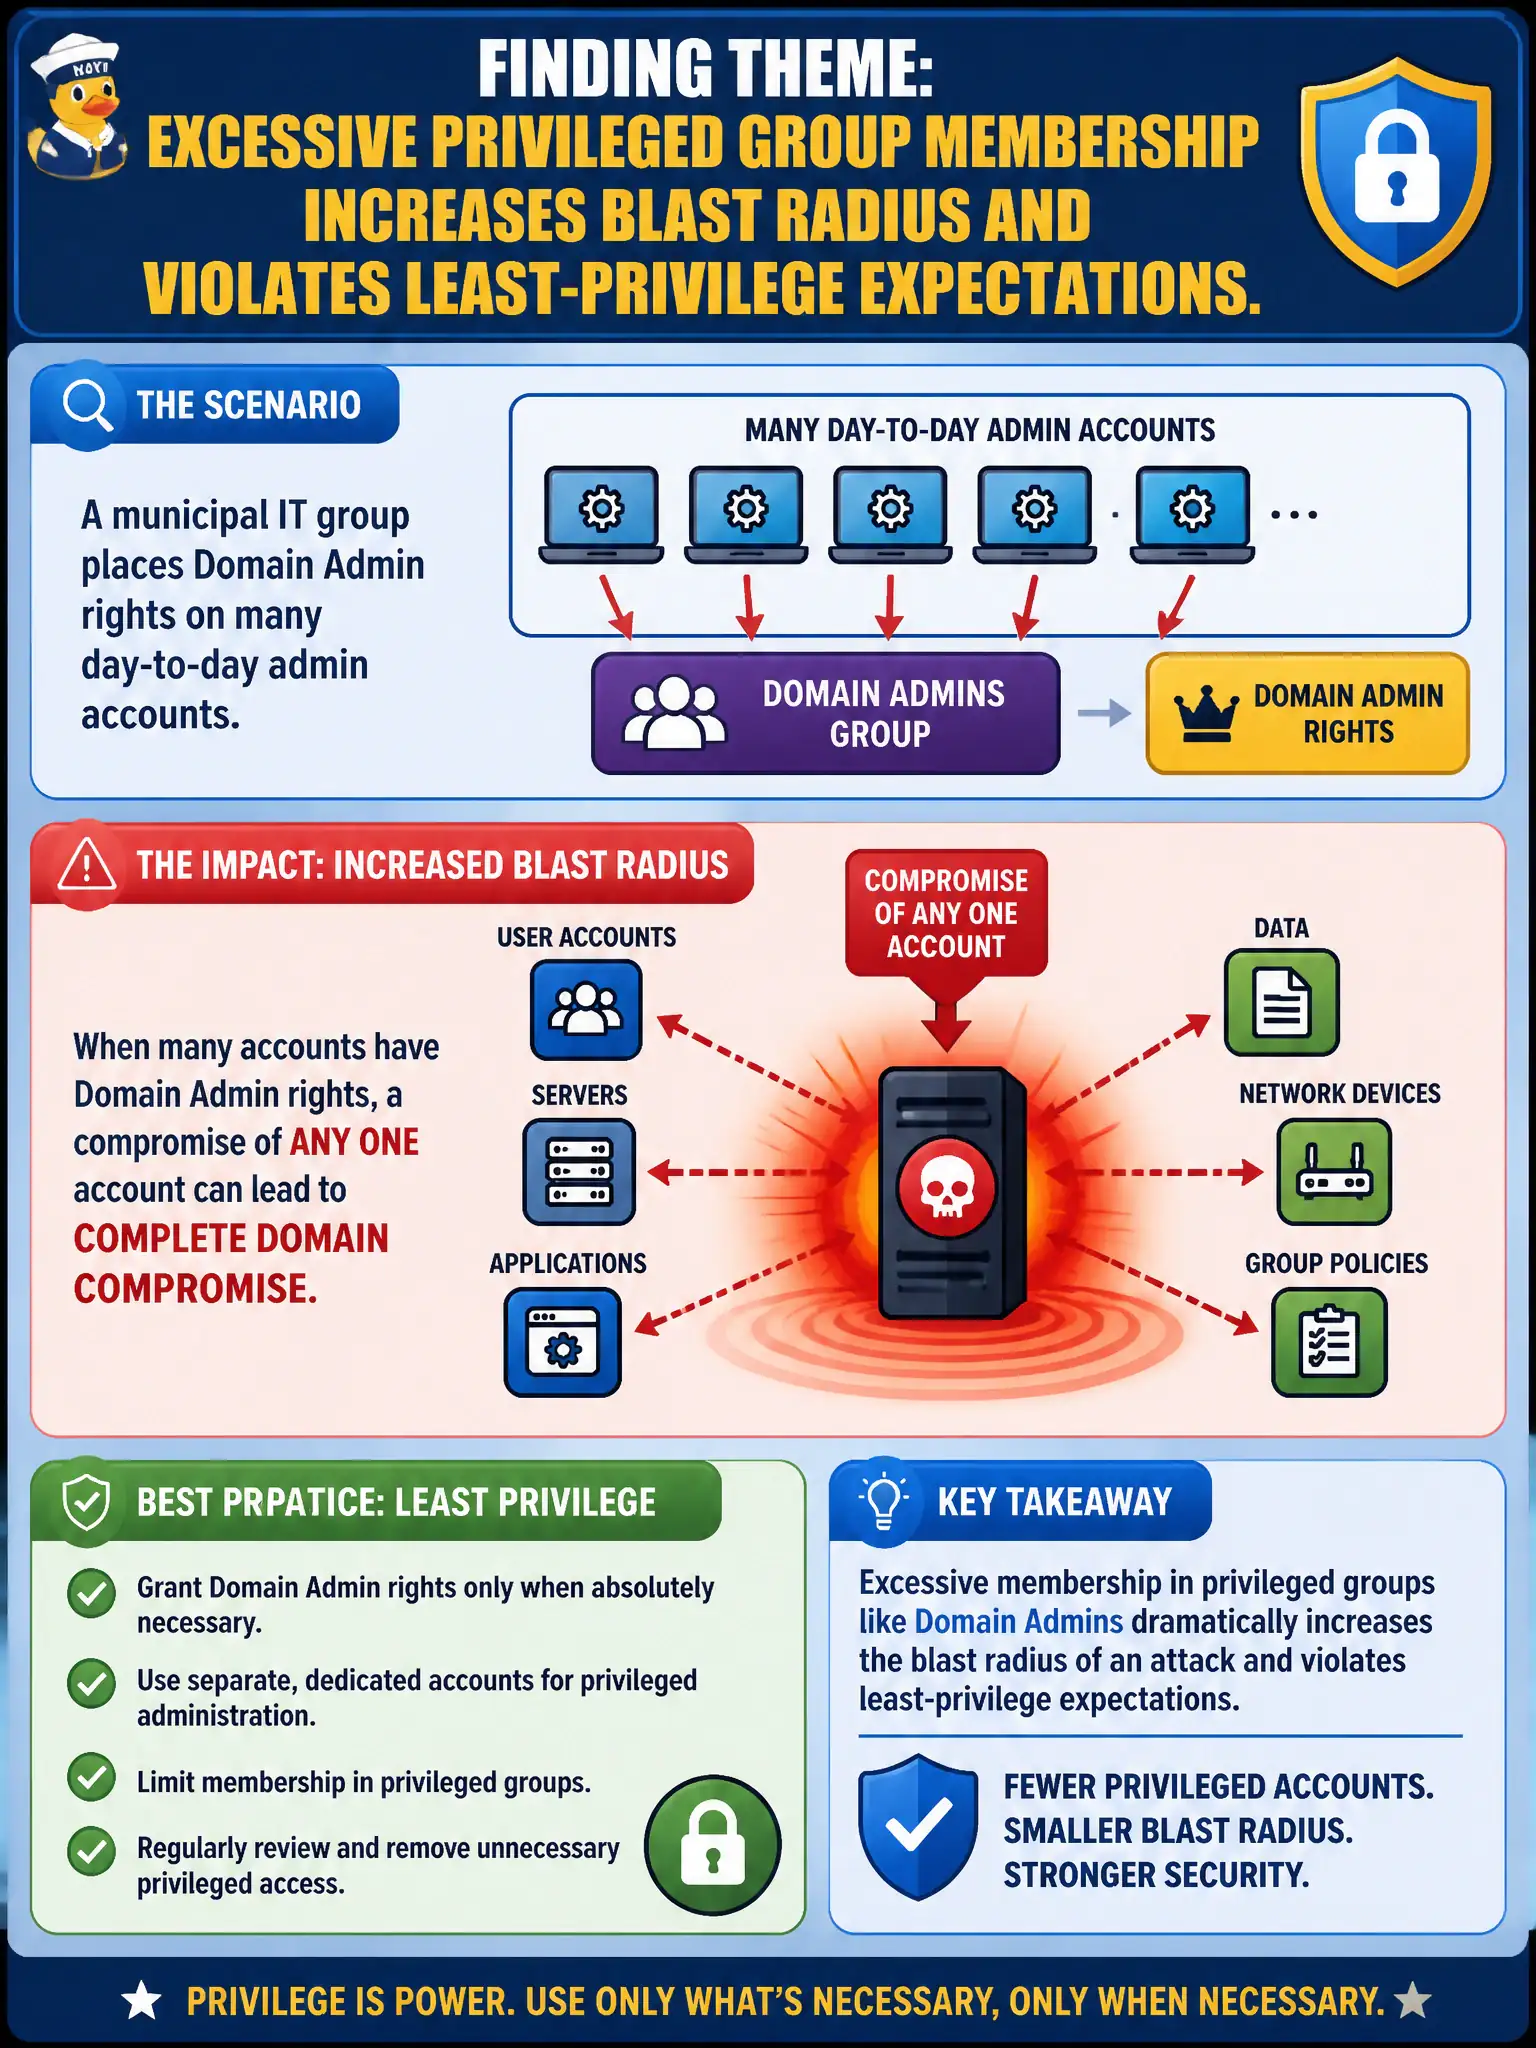
A municipal IT group places Domain Admin rights on many day-to-day admin accounts. What finding theme should the tester raise?
Select an answer to reveal the explanation.
Short Explanation
Domain Admin is a master key, not a daily coffee badge. When half the helpdesk carries that key for email and spreadsheets, one phish becomes an empire-wide problem. Shrink the privileged club.
Full Explanation
When a municipal IT group places Domain Admin rights on many day-to-day admin accounts, the tester should raise that excessive privileged group membership increases blast radius and violates least-privilege expectations. Excess Domain Admin membership is not required by Active Directory and can be reduced with tiering. Day-to-day Domain Admin use does not reduce blast radius compared with tiered admin models—it expands it. Domain Admin rights on workstations do not automatically enable BitLocker or close attack paths. Exam caveat: privileged group hygiene is a core AD finding theme independent of any single exploit. Operational check: enumerate Domain Admins and equivalent groups, identify daily-driver accounts that should be tiered, recommend separate privileged identities and PAWs, and track removal of standing DA rights for the city. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services. Re-validate the same judgment after the next change window so the control still holds under the city’s current tooling, identity posture, and RoE amendments.