
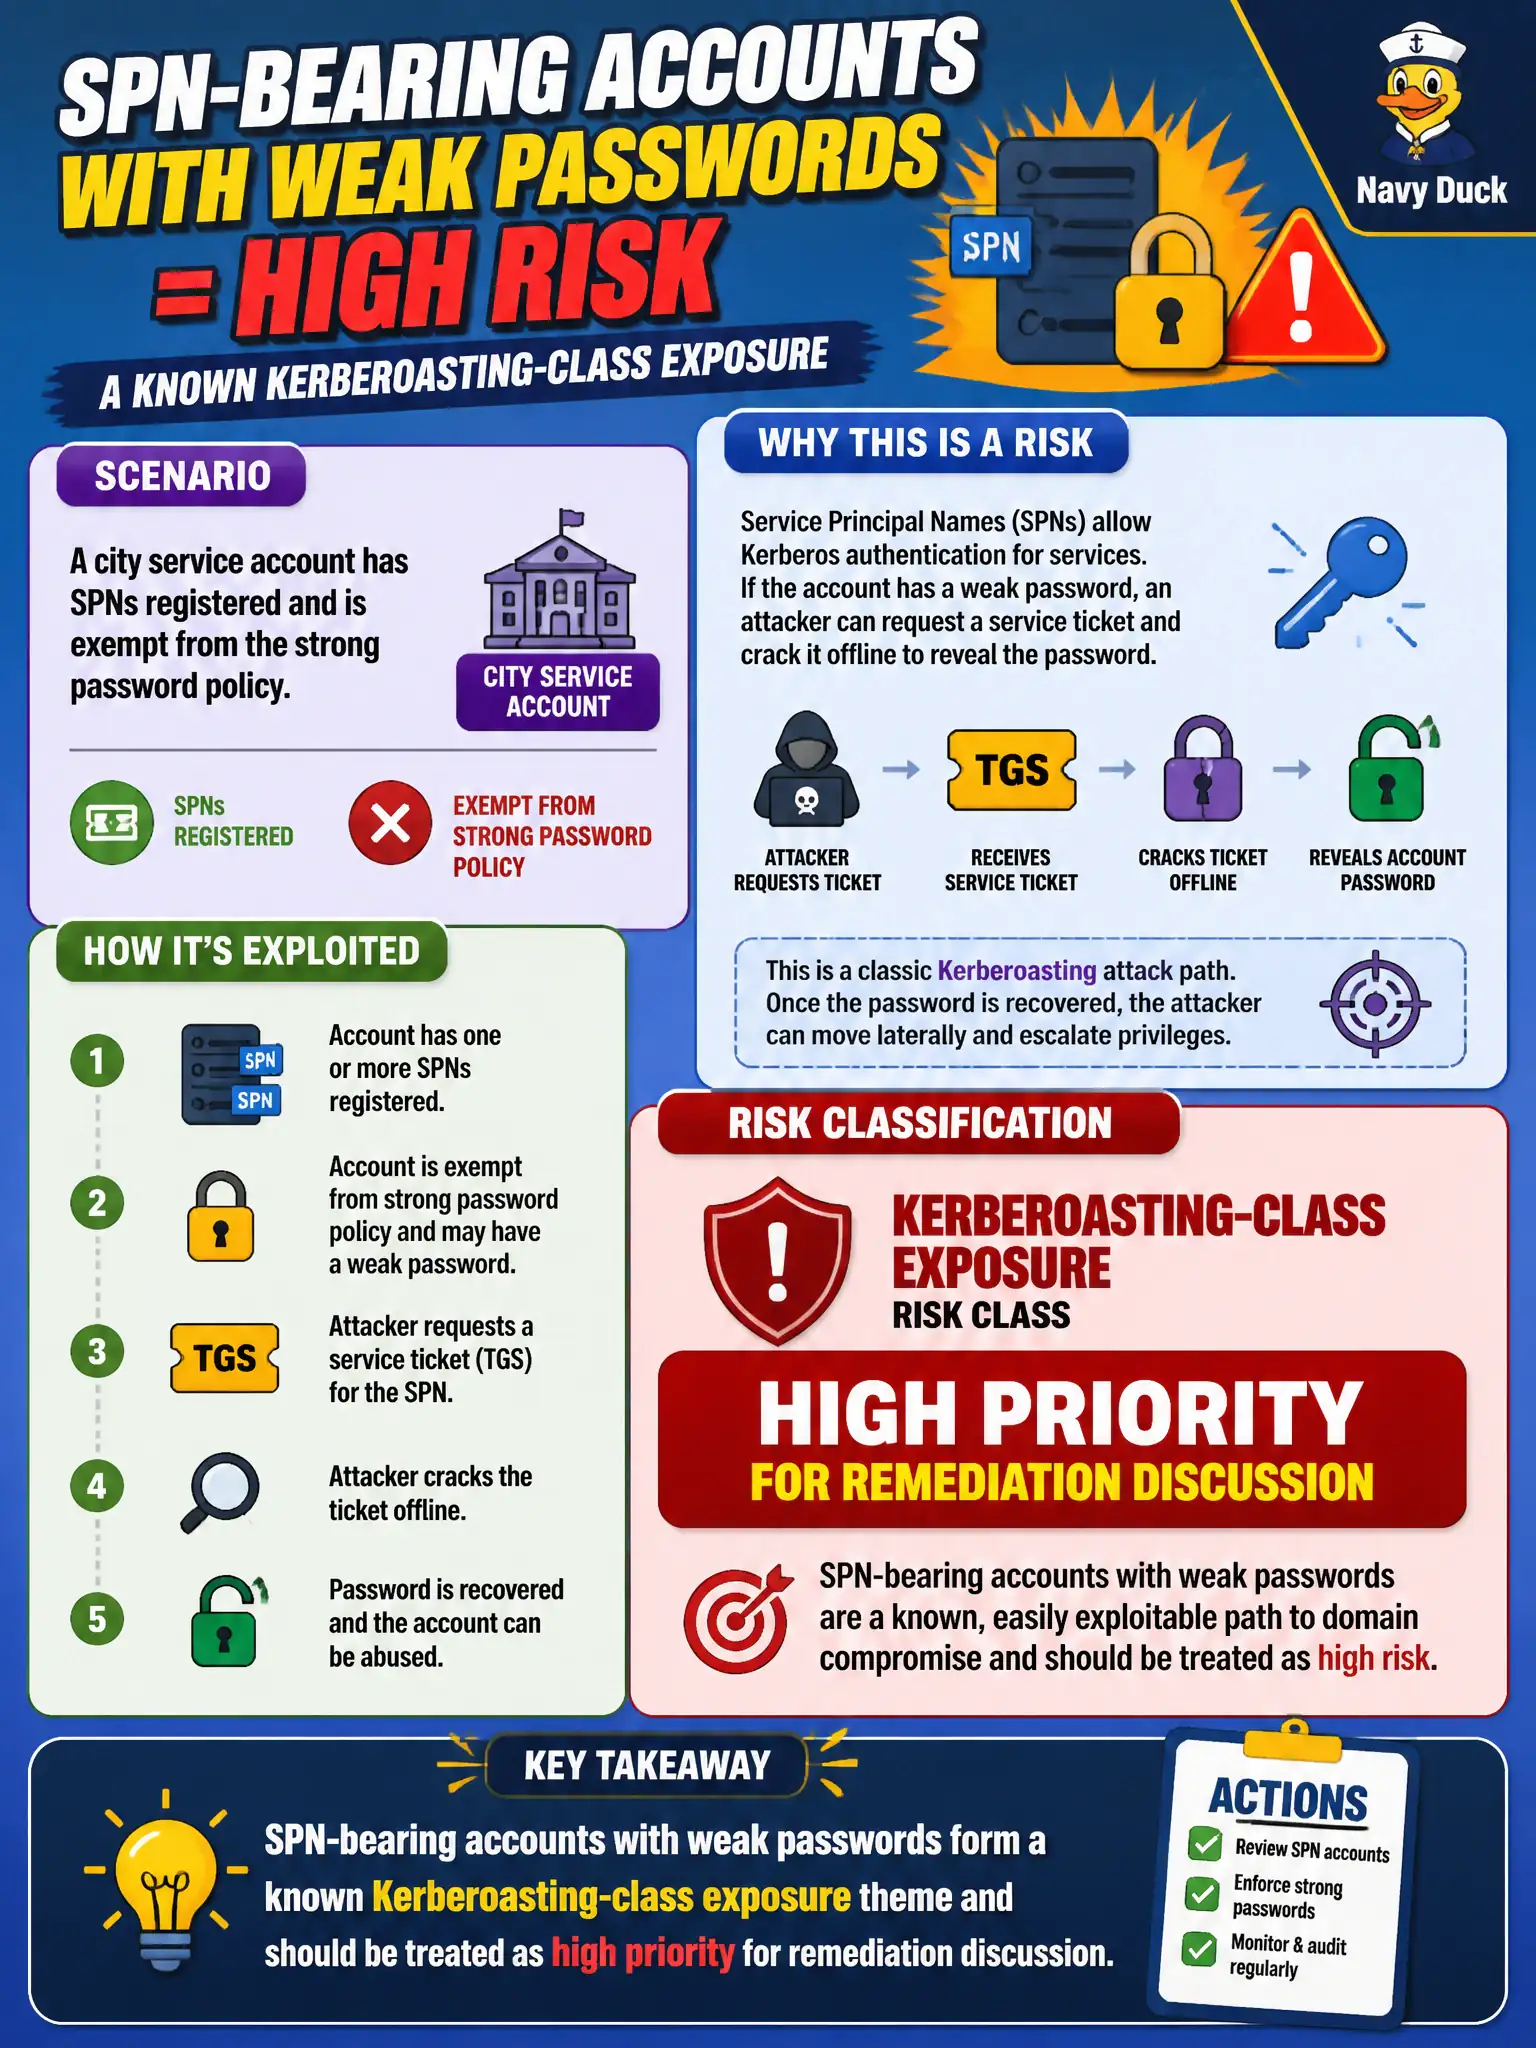
A city service account has SPNs registered and is exempt from the strong password policy. Which risk class should the tester highlight?
Select an answer to reveal the explanation.
Short Explanation
SPNs say 'this account runs a service,' and a weak password says 'please guess me.' Together they are a classic Kerberoast-shaped problem — no recipe required to know that combo is trouble.
Full Explanation
A city service account with SPNs that is exempt from the strong password policy should be highlighted as an SPN-bearing weak-password exposure theme associated with Kerberoasting-class risk and prioritized for remediation discussion. SPNs are not limited to printer discovery and can absolutely relate to credential risk for services. Password policy exemptions do not eliminate Kerberos-related concerns; they often worsen them. Service accounts with SPNs are not immune merely because they are not Domain Admins—service hash exposure can still unlock significant municipal access. Exam caveat: frame the class conceptually; do not paste step-by-step roasting recipes into citizen-facing reports. Operational check: inventory SPN-bearing accounts and policy exemptions, assess password strength controls, recommend long random managed passwords or gMSA where appropriate, and verify monitoring for suspicious ticket requests with the city SOC. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services. Re-validate the same judgment after the next change window so the control still holds under the city’s current tooling, identity posture, and RoE amendments.