
Contractors need access to a single internal web application. Today they connect through a full-network VPN that lets them reach every internal subnet once connected. The security team wants to apply zero trust principles without placing contractors on the internal network at all. Which approach BEST meets this goal?
Select an answer to reveal the explanation.
Short Explanation
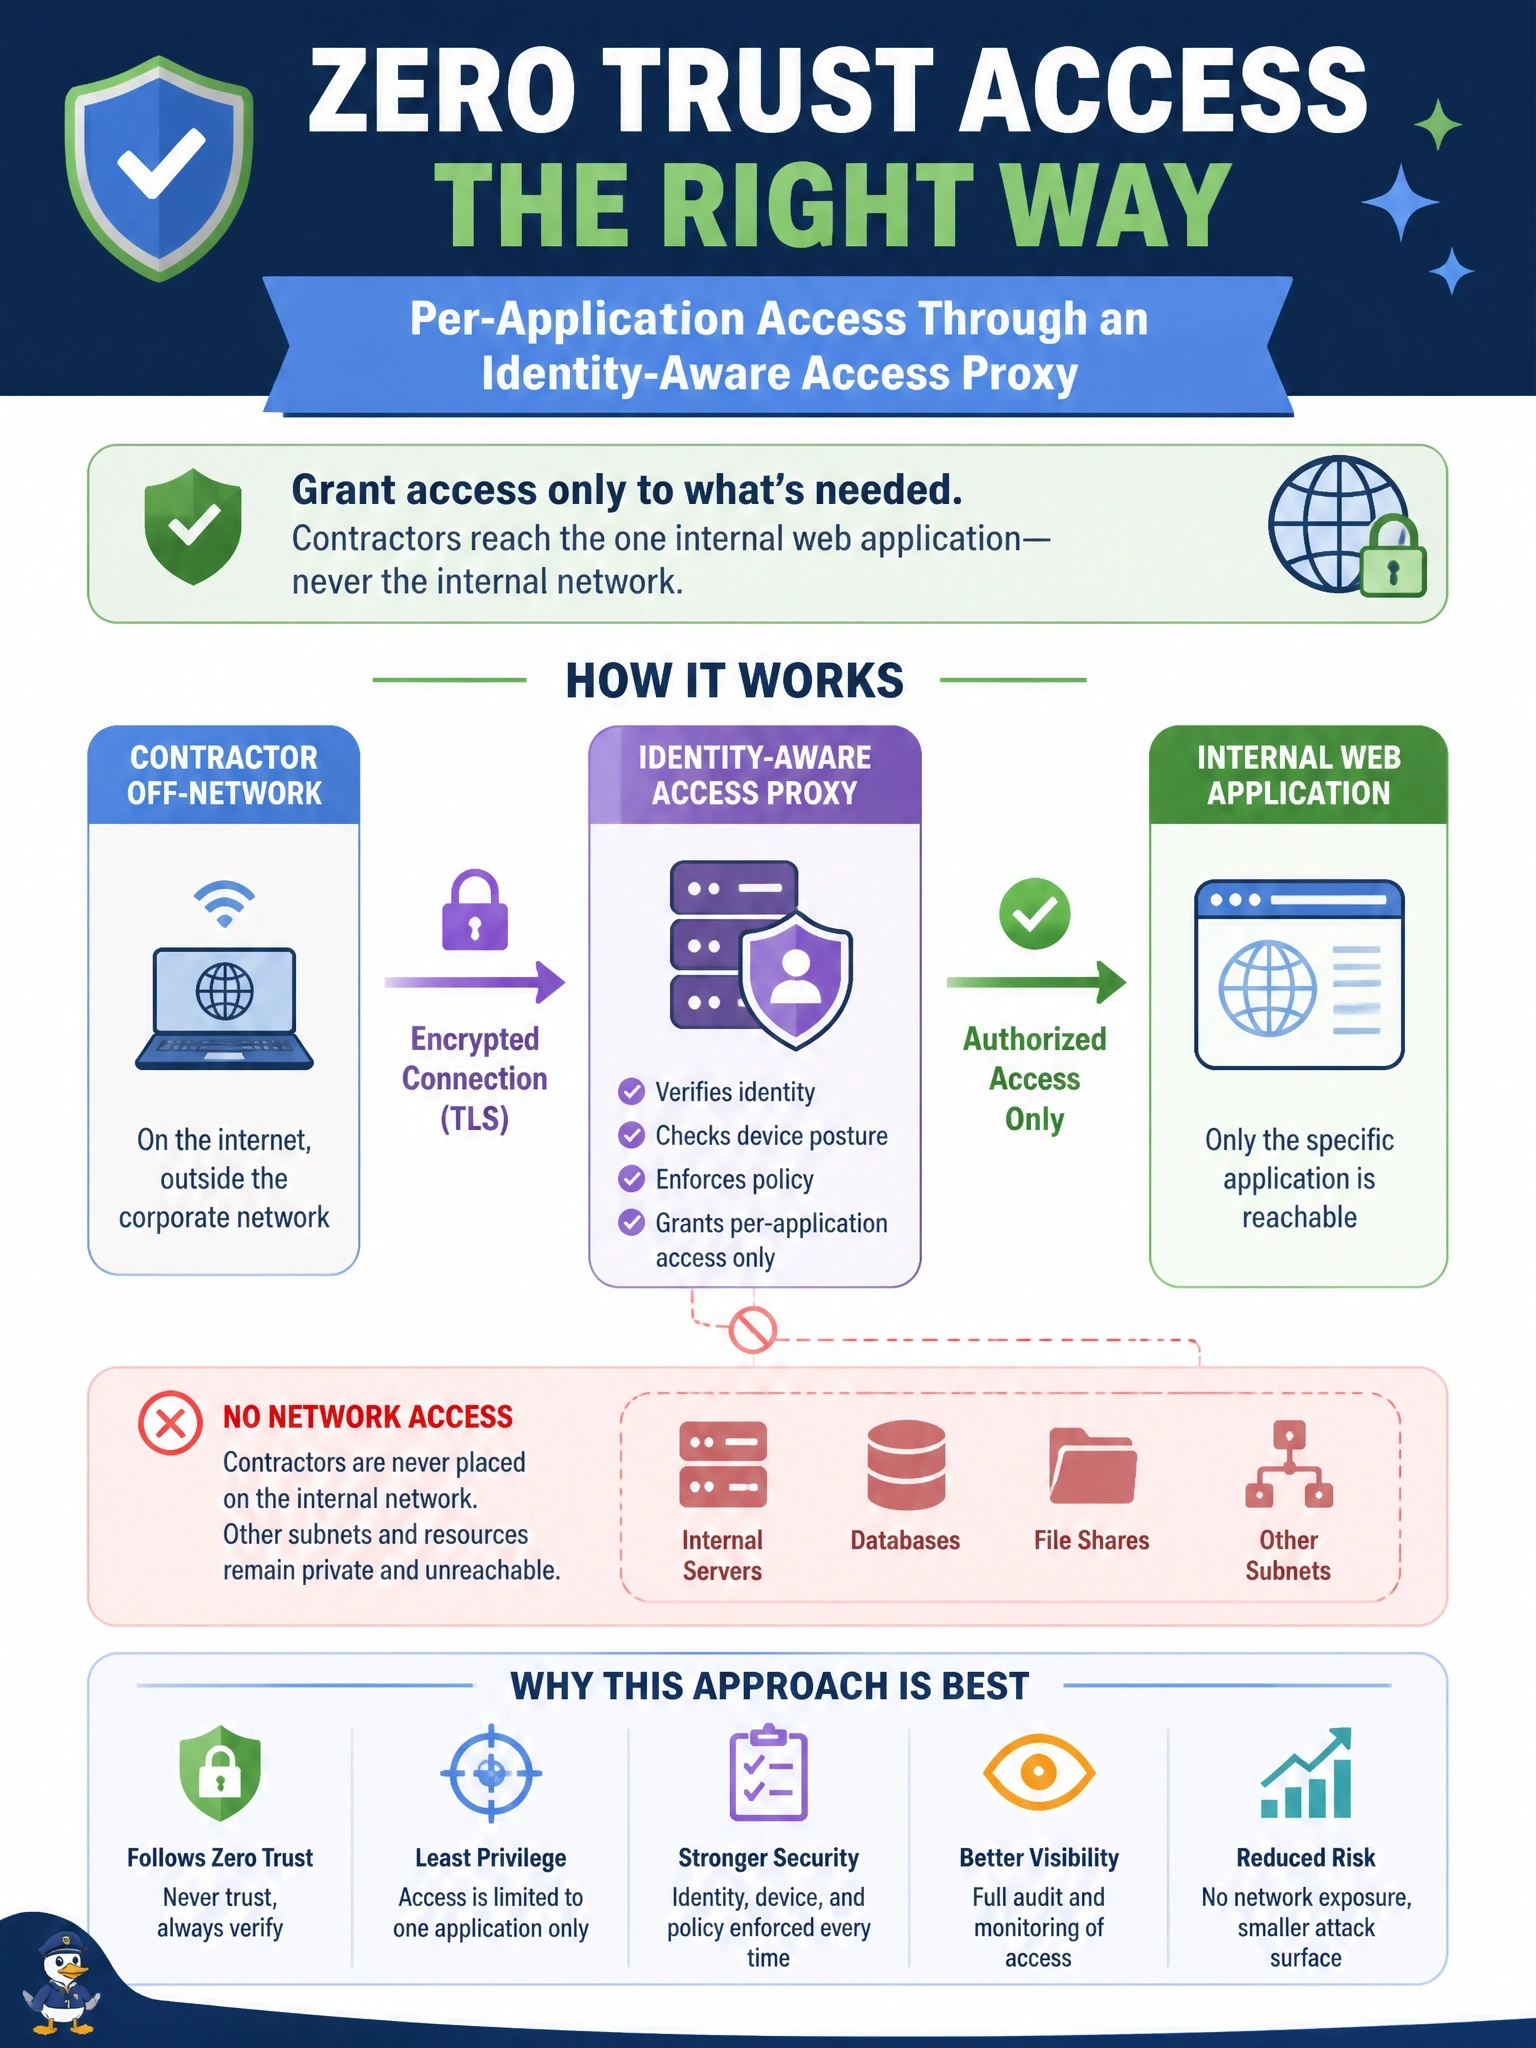
Why would you hand a contractor the master key when they only need one office? Per-application access through an identity-aware proxy lets them reach that one app and nothing else, and they never land on your network. Split tunneling's the trap; it changes what bypasses the VPN, not what they can reach inside.
Full Explanation
Zero trust application access control grants users access to specific applications rather than to network segments. An identity-aware access proxy, often called zero trust network access, authenticates the user, evaluates device and context policies, and then brokers a connection to the single authorized application, so the contractor never receives an address on the internal network and cannot discover or reach other systems. Keeping the full-network VPN with a stronger password improves authentication, but once connected the contractor still has broad network reach, which is the exposure the team wants to remove. A separate VLAN that can route to all subnets changes only where contractor traffic originates; it still places contractors on the internal network with access everywhere, so segmentation in name provides no restriction in practice. Split tunneling sends internet-bound traffic outside the VPN while internal traffic still uses it, so it does not limit which internal systems the contractor can reach and can reduce visibility into the contractor's other traffic. Exam caveat: per-application access also reduces the impact of a compromised contractor device, because an attacker on that device inherits access to one application rather than the network. Operational check: publish the application through the access proxy, restrict contractor policies to that application, remove contractor VPN entitlements, and verify contractors cannot reach any other internal address.