
A new firewall at a warehouse still has the vendor's default admin password and is about to be placed on the network. Which hardening step fits before it goes into production?
Select an answer to reveal the explanation.
Short Explanation
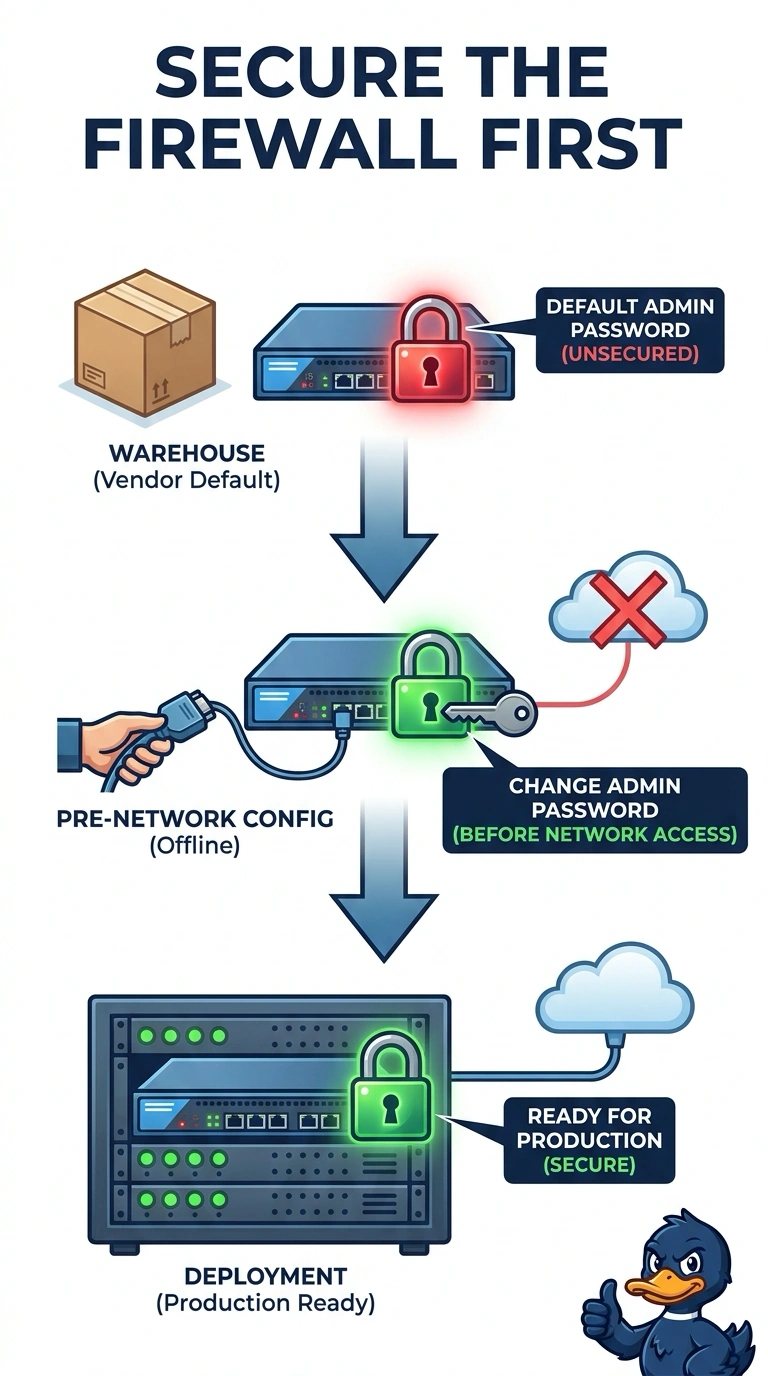
You would not leave the combination that was printed in the manual on a door you are about to open to the building. Change that default admin password before the firewall is reachable. Locking yourself out of every management path, sharing the printed combination, or weakening an unrelated wireless network does not harden this box.
Full Explanation
Device hardening includes replacing default credentials before a device is exposed, because those passwords are published and are scanned for. The warehouse firewall still has the vendor admin password and is about to join the network, so changing that password first is the step that fits. Disabling every management path, including the console, would leave the firewall unmanageable. You change the password and then restrict management to the admin network. You do not remove the only way to administer it. Posting the default password on the intranet shares a known secret with people who do not administer the firewall. WEP is a broken wireless security choice. Changing the guest Wi-Fi to WEP does not replace the firewall's admin password and makes the wireless network weaker. Exam caveat: changing the password is necessary and not sufficient. Management access should also be limited by source and, where you can, by MFA. Operational check: set a unique admin password, confirm the default no longer works, and restrict management to the admin subnet before you connect the outside interface.