
A city library must stop patrons from opening betting.example and must leave other entertainment sites available. Which control matches that narrow block?
Select an answer to reveal the explanation.
Short Explanation
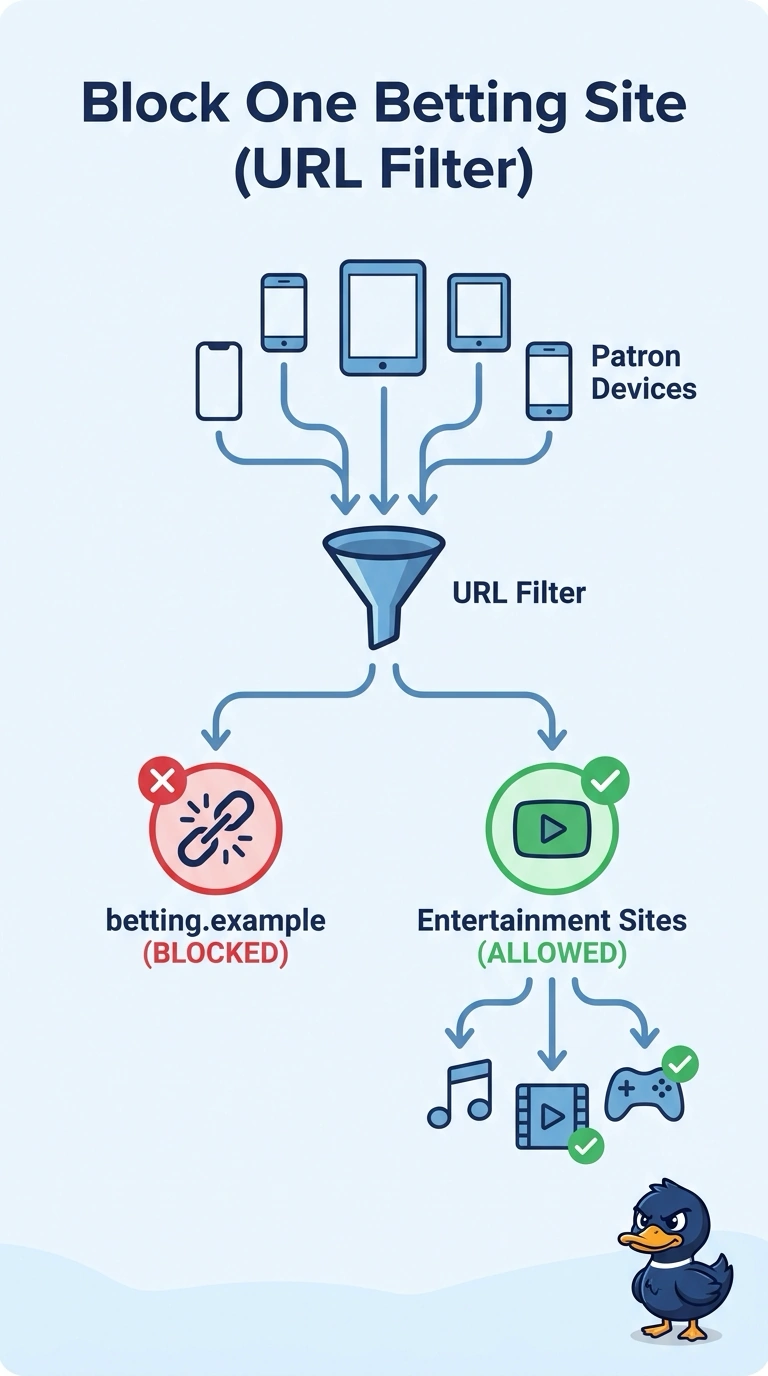
You want one name crossed off the list, not the whole entertainment shelf pulled down. A URL filter can block betting.example and leave the other entertainment sites alone. A category block, a ban on HTTPS, or a DNS block for the whole zone is wider than the one site.
Full Explanation
A URL filter can deny only betting.example. Other entertainment sites never hit the rule, which is the narrow control the library described. A category filter blocks a whole group and would sweep up sites the library meant to leave alone. Blocking HTTPS takes down every encrypted site, including the ones that should stay available. A DNS block for the entertainment zone is the tempting twin because it can stop the betting name. It also stops every other name in that zone, which is wider than the request. Exam caveat: a URL filter sees the name only if the session exposes it, through the host header or inspection the library is allowed to do. Operational check: from a patron network, confirm betting.example is denied and two other entertainment sites still load. Log the blocked name so a later request to widen the rule is a choice, not an accident. Open two allowed entertainment sites from the same patron network after the block is in place. Record the allowed sites in the change so the narrow rule stays narrow.