
City hall already sends firewall, VPN gateway, and server logs to a collector. The team now needs those logs correlated, with one alert when they form an incident. Which system adds that?
Select an answer to reveal the explanation.
Short Explanation
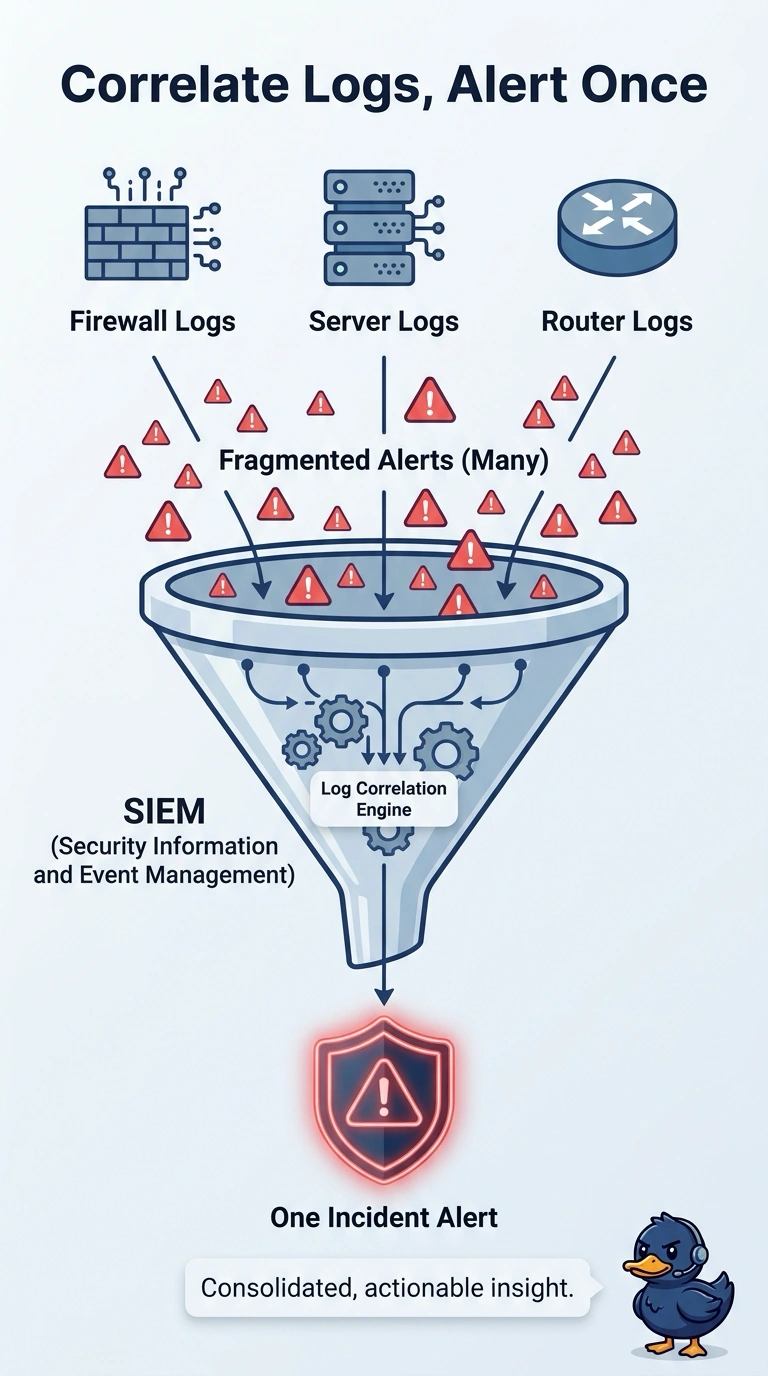
A pile of notebooks is not a detective. You already have the logs in one collector, and you still need something that reads them together and raises one alert when they add up to an incident, which is a SIEM. The collector alone, a flow counter, or a packet sensor that never opens those logs does not make the connection.
Full Explanation
A security information and event management system correlates logs from many sources so the team gets one incident alert instead of unrelated lines. City hall already has firewall, VPN, and server logs arriving at a collector. The missing piece is that correlation, which is what the SIEM adds. The syslog collector stores the messages and is already in place. Storage does not decide that three lines are one incident. NetFlow is the tempting twin because it is also a collector. It counts conversations, and it does not correlate the device logs the stem already has. An intrusion detection sensor on a mirror watches packets. It can raise its own alerts, and it does not read the logs sitting in the collector. Exam caveat: a SIEM is only as good as the logs it receives and the rules someone writes. Pointing the collector at it without use cases produces a second unread copy. Operational check: generate a known pattern across the firewall and a server, and confirm the SIEM opens one incident rather than three unrelated messages.