
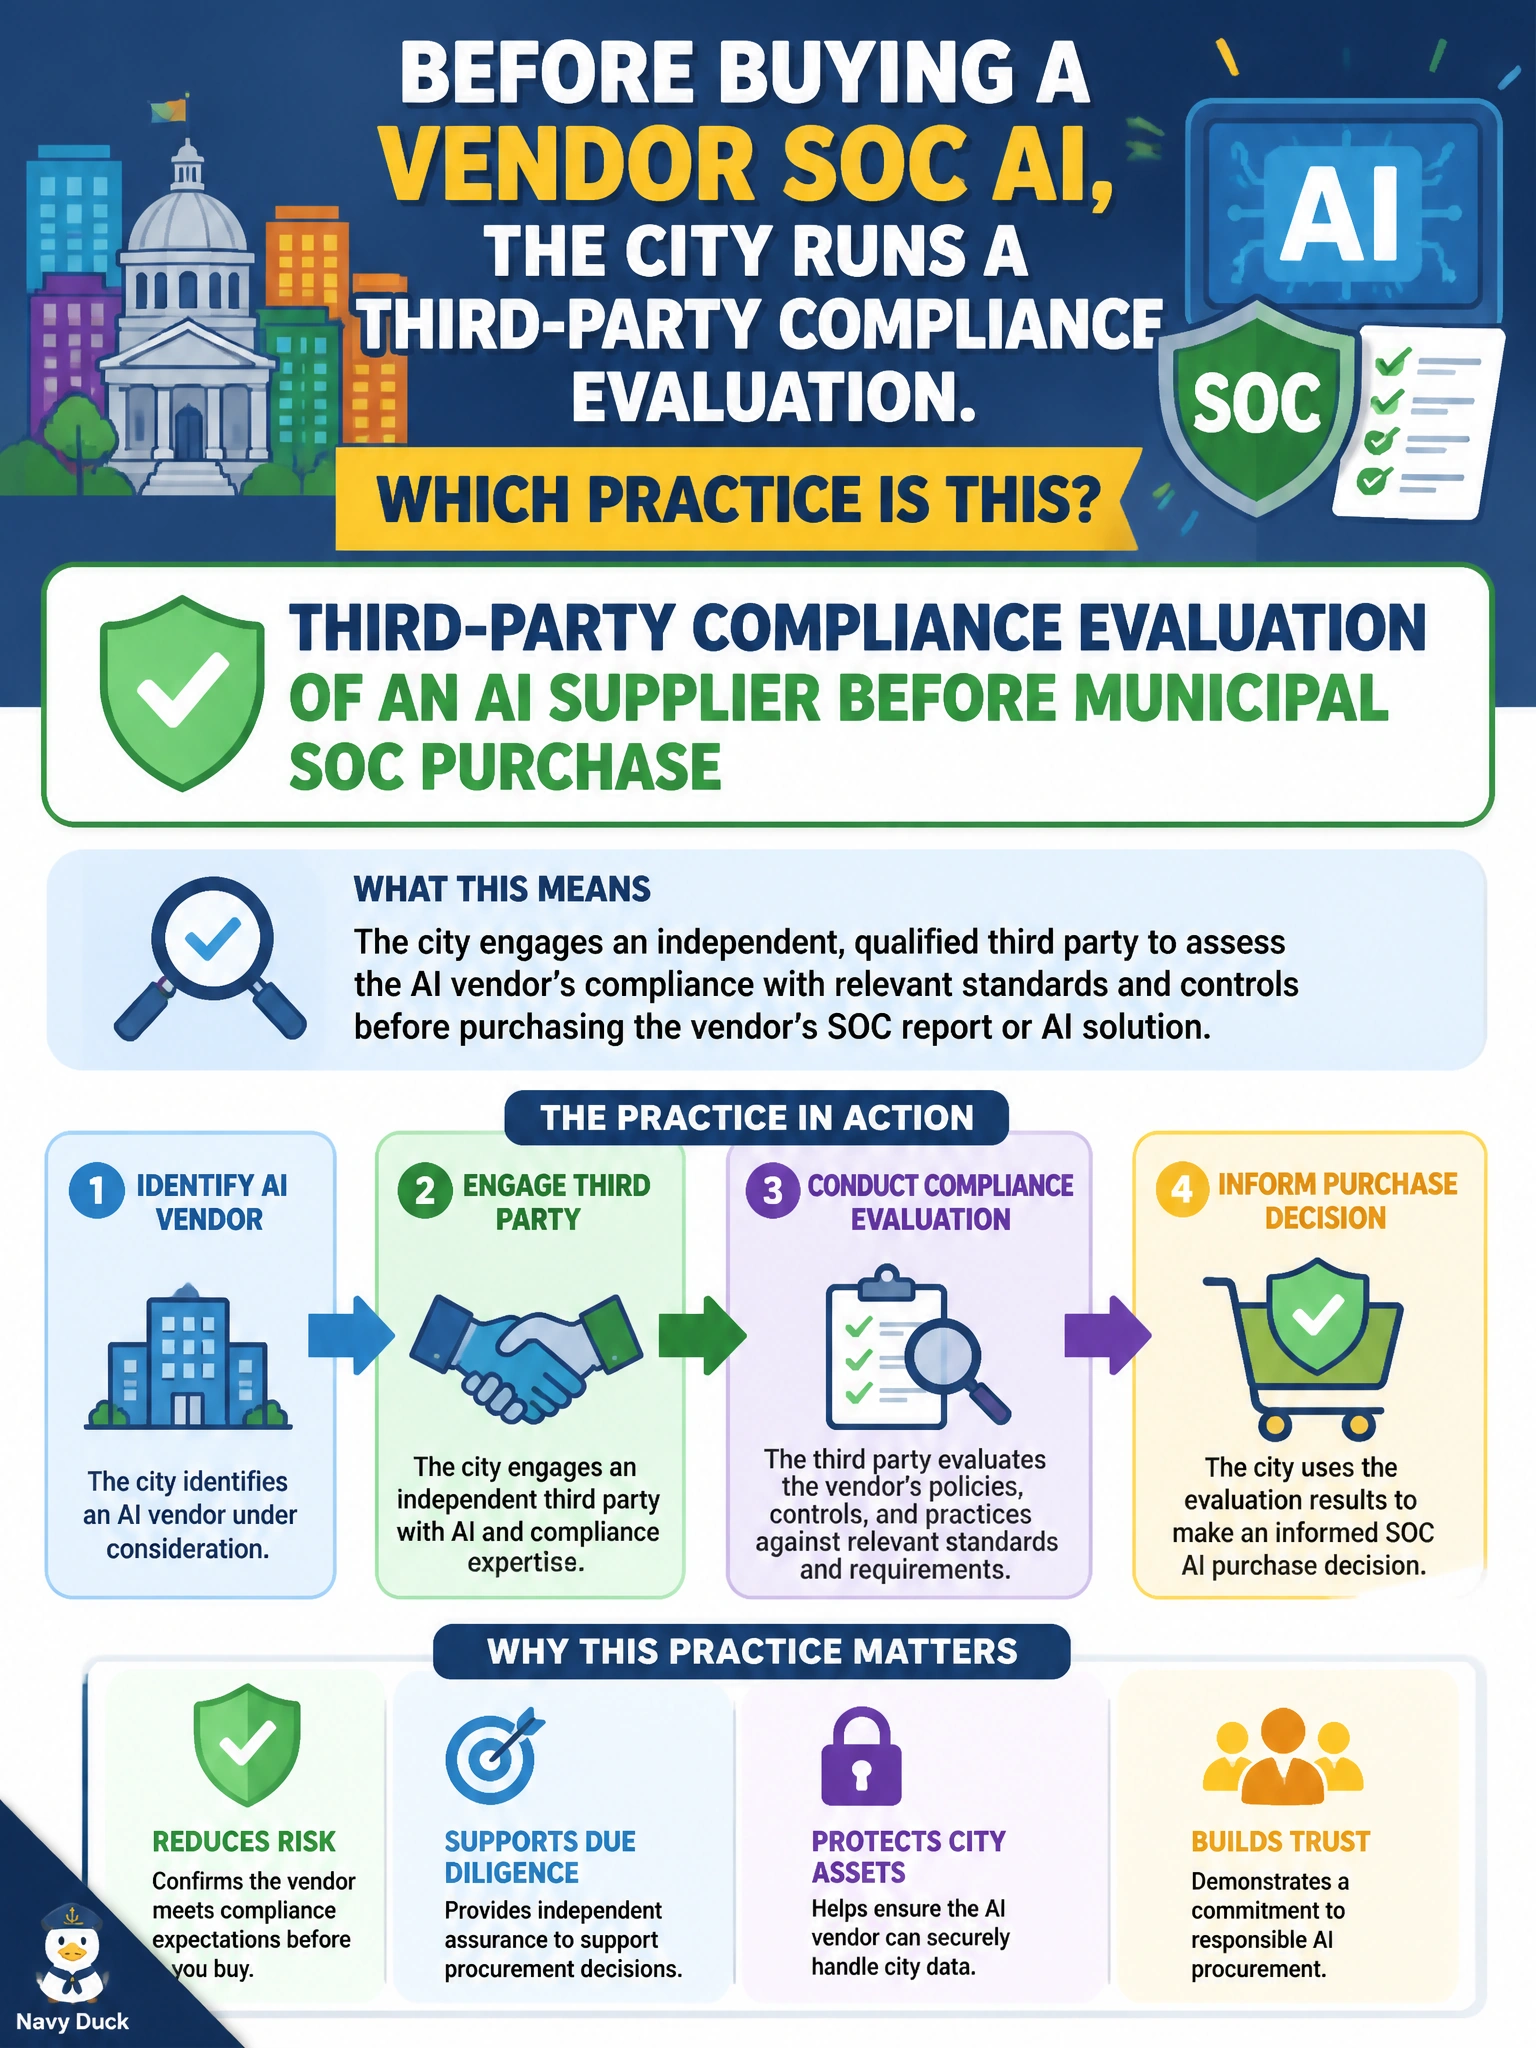
Before buying a vendor SOC AI, the city runs a third-party compliance evaluation. Which practice is this?
Select an answer to reveal the explanation.
Short Explanation
Before the city buys SOC AI, you'll need a third-party compliance evaluation because it's about meeting regulatory expectations. An evaluation after you buy comes too late, one during operations doesn't inform your purchase, and one of a subcontractor checks the wrong party, so none of them prove compliance before you buy.
Full Explanation
Third-party compliance evaluations assess whether AI suppliers meet organizational and regulatory expectations before purchase. Running such an evaluation before a municipal SOC AI buy is correct practice: SOC tooling sees sensitive telemetry and detections, so the city needs independent or structured review of security, privacy, subprocessors, and control attestations—not just third-party compliance evaluation of an AI supplier after municipal SOC purchase, which comes too late to inform the purchase decision rather than providing pre-purchase assurance. Third-party compliance evaluation after municipal SOC purchase, during municipal SOC operations, and of an AI subcontractor are mistimed or mis-scoped variants at best, not substitutes for evaluation.
Third-party compliance evaluation of an AI supplier after municipal SOC purchase fails by timing: a post-purchase review does not provide pre-purchase assurance of whether the supplier meets municipal regulatory and control expectations before the city commits. Third-party compliance evaluation of an AI supplier during municipal SOC operations fails because ongoing operational oversight is not independent evidence for the pre-purchase decision and does not satisfy this city’s obligations before award. Relying on third-party compliance evaluation of an AI subcontractor before municipal SOC purchase fails differently—reviewing a subcontractor is a different scope, not a pre-purchase compliance evaluation of the AI supplier itself.
Exam caveat: third-party compliance evaluation is a pre-purchase supplier assurance activity—distinct from evaluation after municipal SOC purchase, during municipal SOC operations, or of an AI subcontractor. SOC AI intensifies the need because of sensitive operational data.
Operational check: complete a structured supplier compliance review (questionnaires, attestations, residual-risk sign-off) before awarding municipal SOC AI, and retain evidence for auditors.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.