
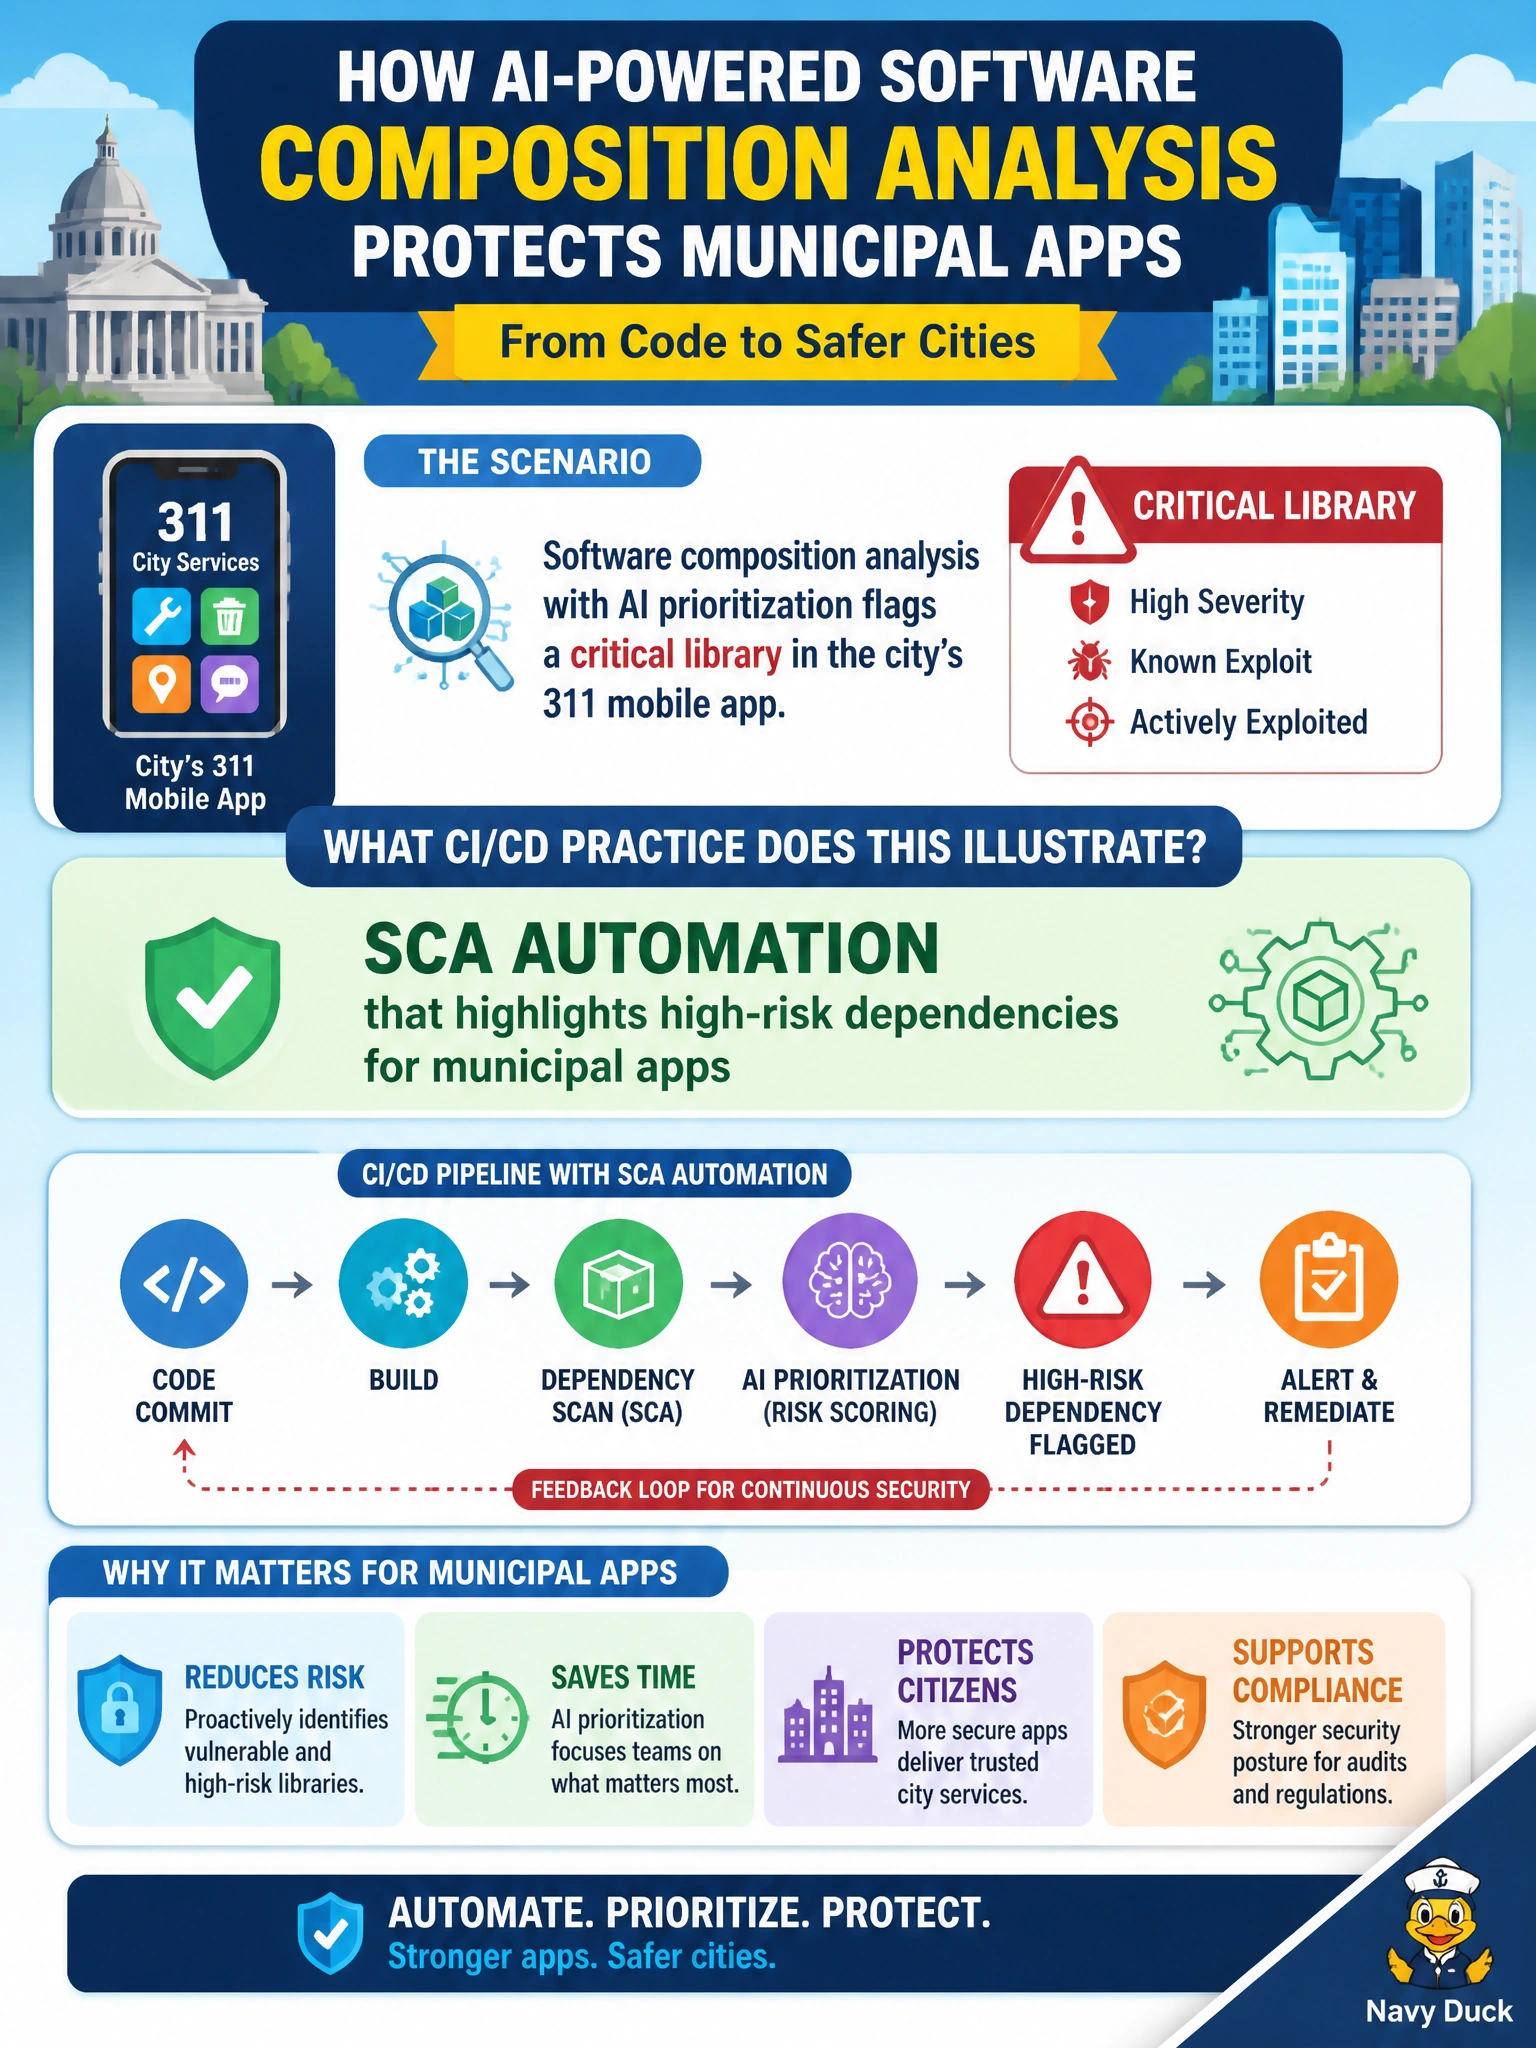
Software composition analysis with AI prioritization flags a critical library in the city’s 311 mobile app. What CI/CD practice does this illustrate?
Select an answer to reveal the explanation.
Short Explanation
SCA with AI ranking is the 311 app’s ‘which library will burn us first’ radar — surface the critical dep, then patch. Relying on SAST for custom code, DAST on the running app, or just an SBOM won’t show you which third-party library needs urgent patching in the pipeline.
Full Explanation
Software composition analysis (SCA) automation that highlights high-risk dependencies for municipal apps illustrates a CI/CD supply-chain practice: inventory third-party libraries, map known vulnerabilities, and use AI prioritization to surface the packages most likely to matter for exploitability and business impact. When SCA flags a critical library in the city’s 311 mobile app, the pipeline is doing its job—turning opaque dependency trees into actionable risk for a resident-facing service. That works because modern apps are mostly assembled from packages; without SCA, municipal teams cannot systematically see which transitive components threaten confidentiality or availability of civic channels. SAST automation that reviews custom source code for municipal apps fails because it scans code you wrote, not the third-party libraries whose vulnerabilities SCA is meant to surface in the 311 app. DAST automation that probes running municipal apps for exploitable behavior fails because it tests a live application from the outside; it does not inventory dependencies or flag a critical library in the app’s supply chain. SBOM generation that inventories approved dependencies for municipal releases fails because it lists what is included but does not prioritize or flag a critical vulnerability for immediate remediation in the CI/CD pipeline. Exam caveat: “critical” CVSS alone can mis-rank risk; reachability, exploit maturity, and whether the 311 app actually exercises the vulnerable code path should influence remediation order. Operational check: fail builds on unresolved critical reachable issues for the 311 app, maintain an SBOM, assign owners for top dependencies, and verify patches in staging before forcing production upgrades that could break resident mobile workflows.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.