
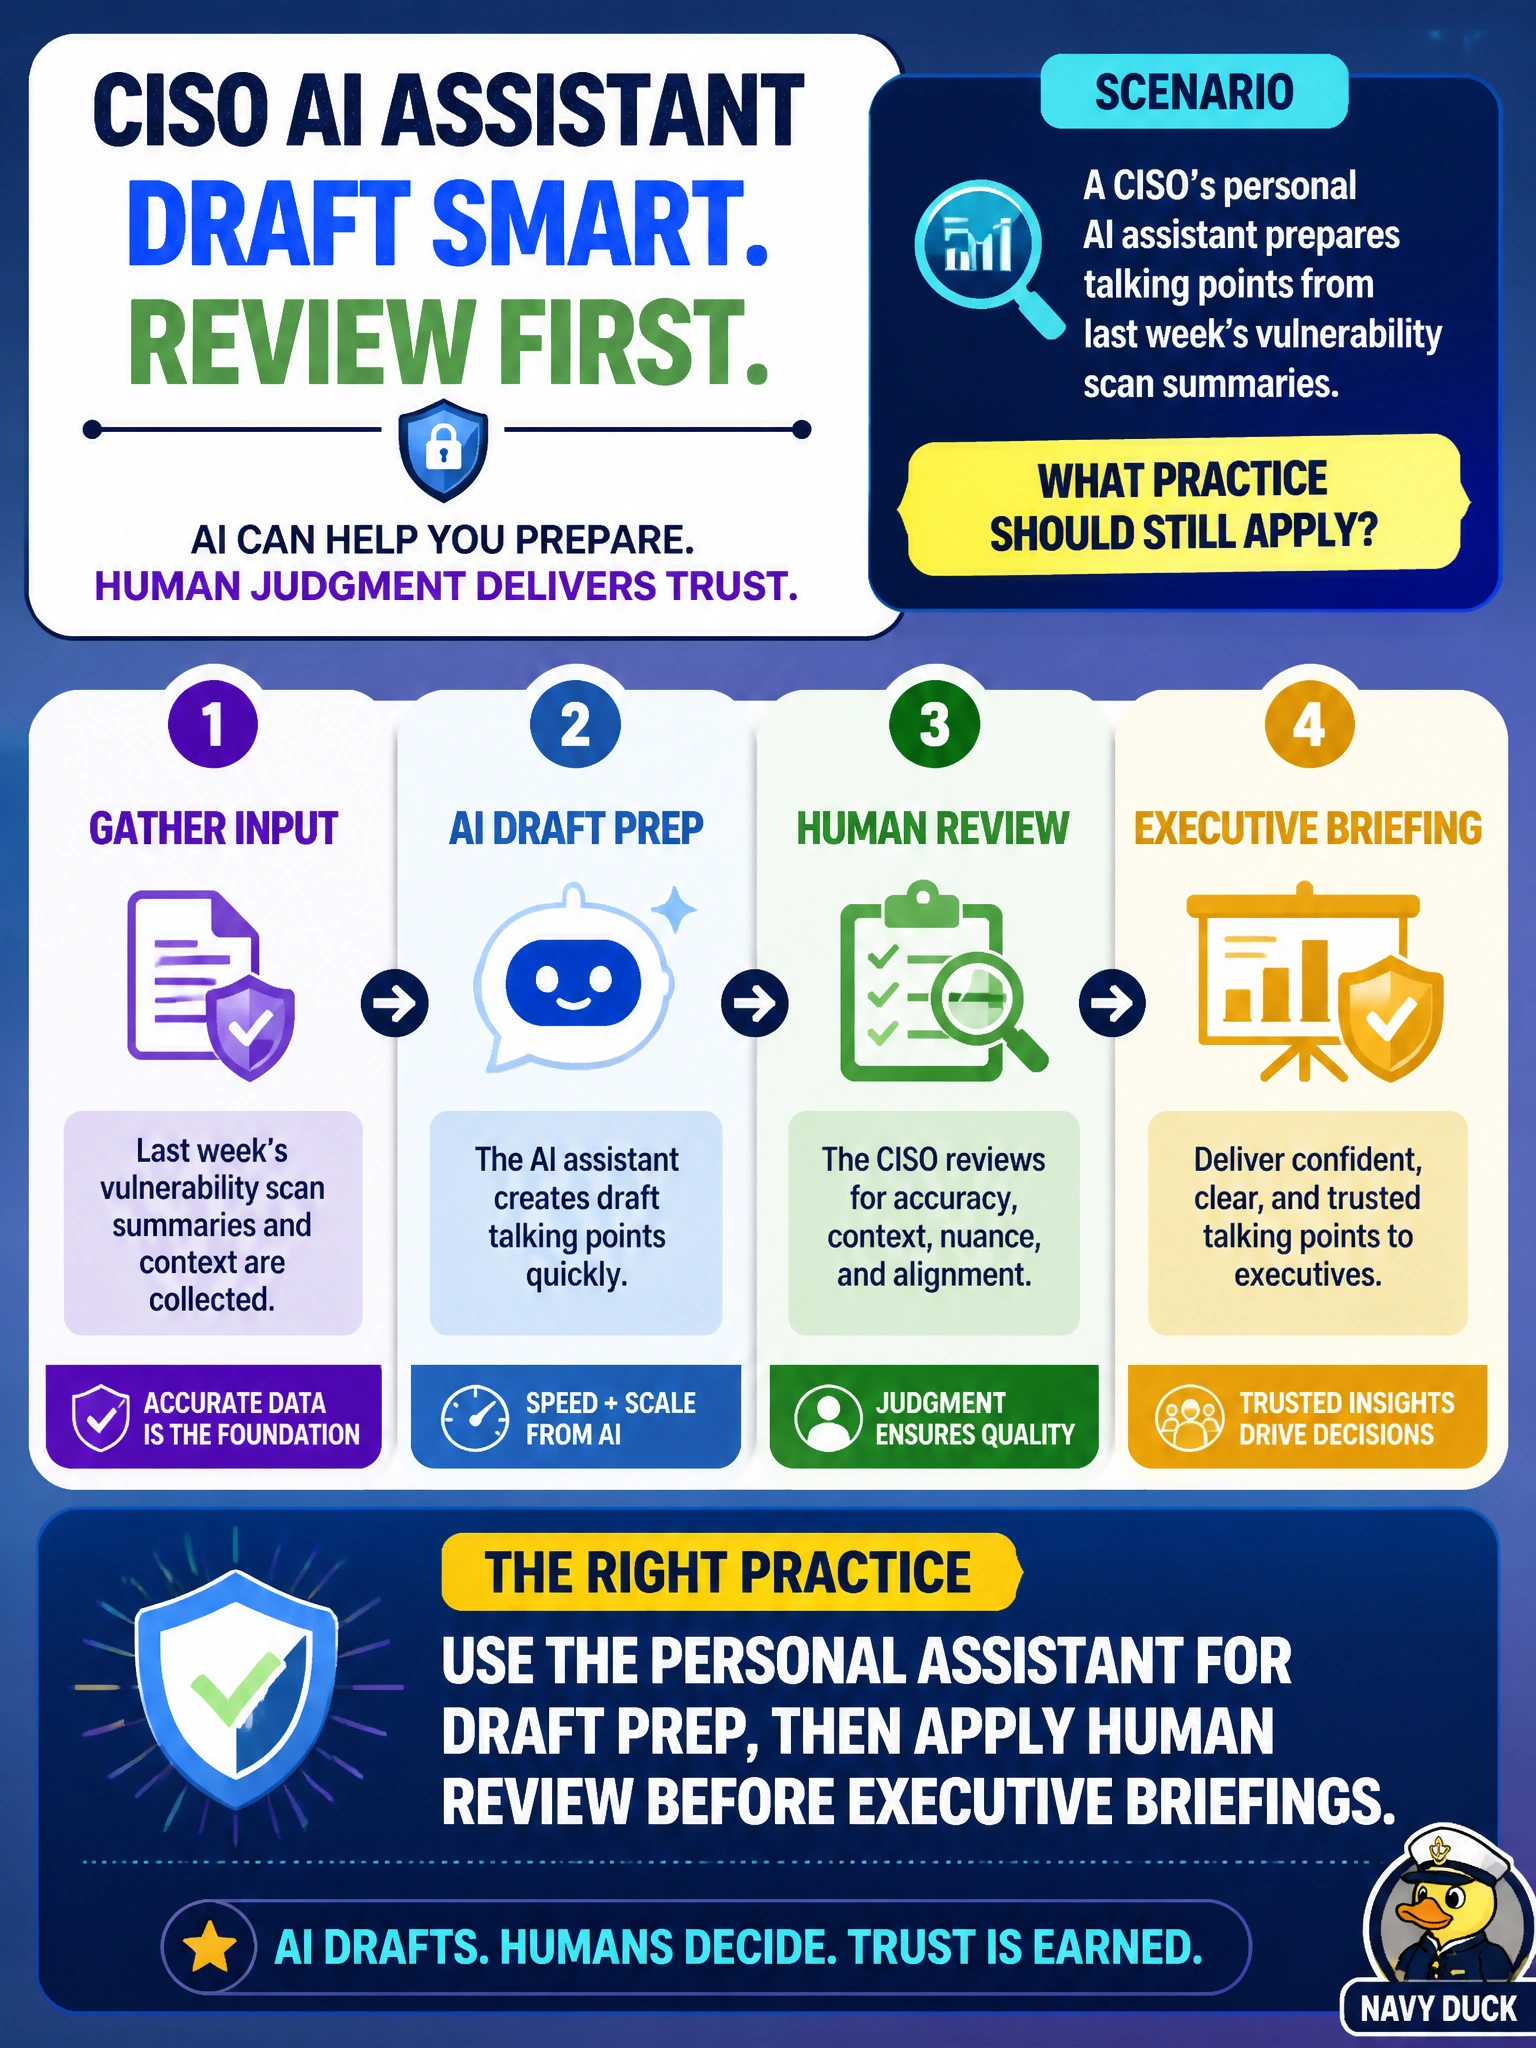
A CISO’s personal AI assistant prepares talking points from last week’s vulnerability scan summaries. What practice should still apply?
Select an answer to reveal the explanation.
Short Explanation
You can use it for draft talking points if you'll review them before the briefing, but that review doesn't turn drafts into remediation tickets. Don't finalize GRC metrics from them and don't store briefing points as audit evidence — they're still not validated metrics or safely stored records.
Full Explanation
Using a CISO’s personal AI assistant to prepare talking points from vulnerability scan summaries, then applying human review before executive briefings, is correct because draft assistance is appropriate while unreviewed publication or privileged action is not. Domain 3 expects AI-assisted preparation with oversight: leaders gain speed, but accountability for accuracy and tone remains human. Municipal executive briefings influence budget, public messaging, and council scrutiny, so validation is mandatory.
Using the personal assistant for draft prep, then applying human review before issuing remediation tickets fails because briefing drafts reviewed for executive tone are not vetted remediation instructions, and issuing them as tickets can create inaccurate tracking, misassigned fixes, and accountability gaps. Using the personal assistant for draft prep, then applying human review before finalizing GRC metrics fails because AI drafts reviewed for briefing clarity are not validated metrics, and finalizing them as such can mislead oversight and produce flawed security decisions. Using the personal assistant for draft prep, then applying human review before storing audit evidence fails because a personal assistant’s chat history is not a system of record; human review does not add proper access controls, audit trails, and retention safeguards for vulnerability data.
Exam caveat: personal assistants may retain prompts in vendor logs; CISOs should avoid pasting highly sensitive vuln details that identify exploitable municipal targets into consumer-grade tools without an approved enterprise path. Operational check: use an approved, logged enterprise assistant for scan-summary prep when possible, strip asset-critical exploit details from prompts, and require the CISO or delegate to fact-check every talking point against the scan report before the briefing.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.