
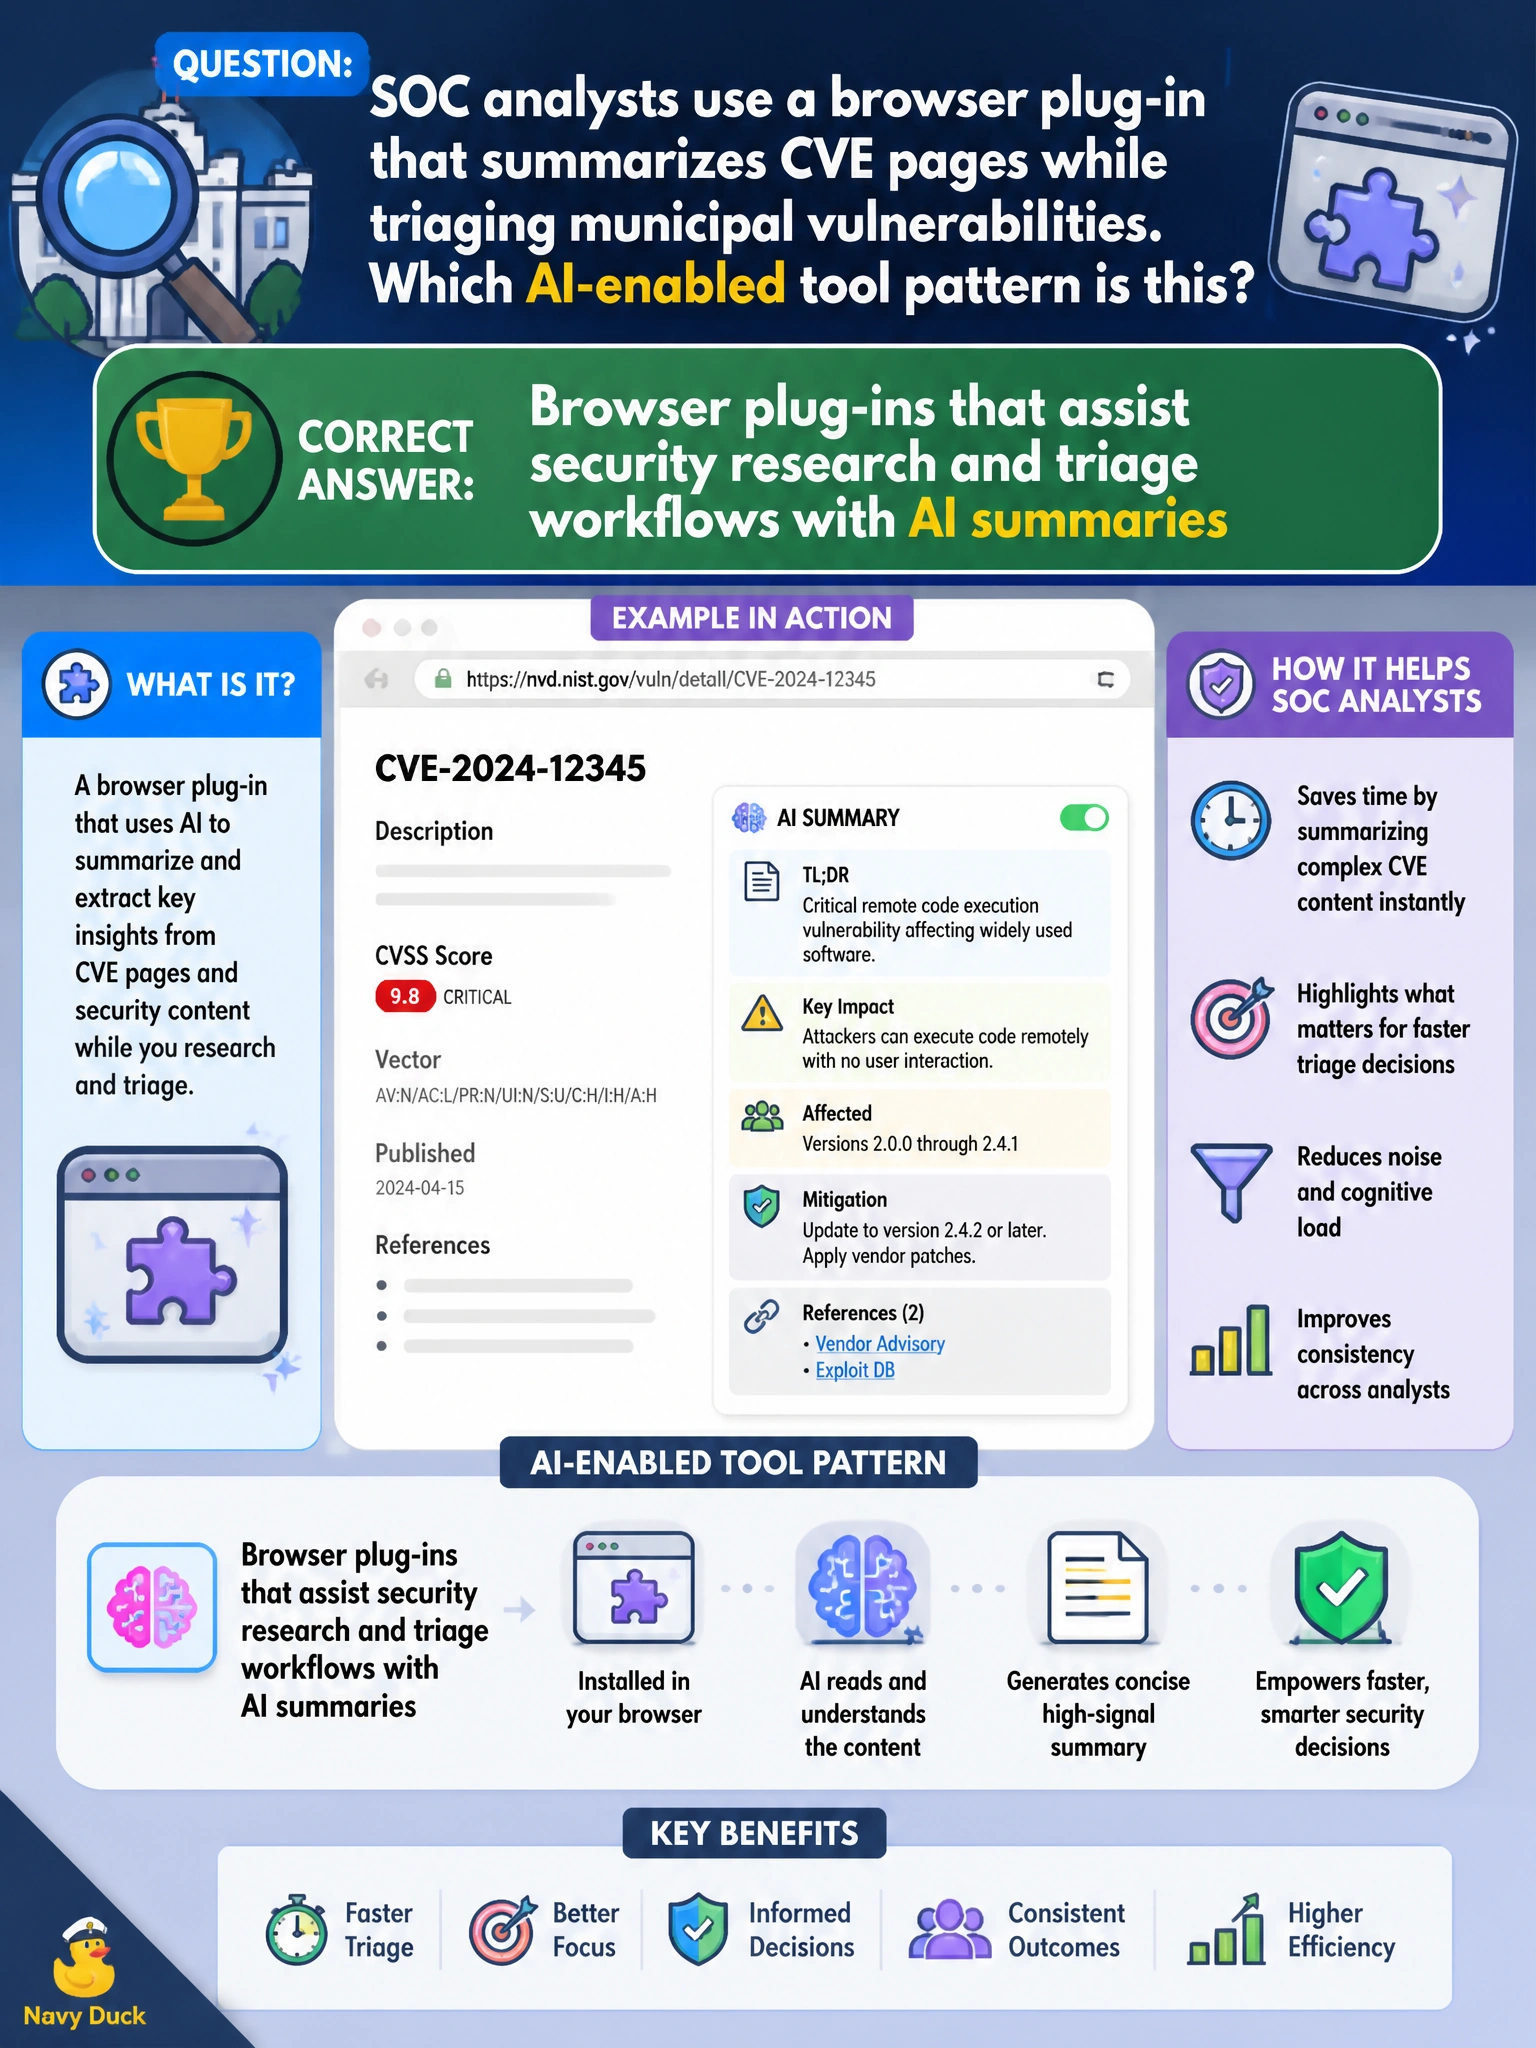
SOC analysts use a browser plug-in that summarizes CVE pages while triaging municipal vulnerabilities. Which AI-enabled tool pattern is this?
Select an answer to reveal the explanation.
Short Explanation
A browser add-on that digests CVE pages is AI helping triage—faster reading, still needs a human check. Other plug-ins that correlate network telemetry or prioritize workstation patches don't give you CVE page summaries for triage. You'll find plug-ins that provide EDR containment guidance help you respond, but they aren't reading advisories for you.
Full Explanation
SOC analysts using a browser plug-in that summarizes CVE pages while triaging municipal vulnerabilities illustrates browser plug-ins that assist security research and triage with AI summaries because the pattern accelerates advisory comprehension while leaving verification with the analyst. Domain 3 covers AI-enabled security tasks that speed reading and correlation without replacing accountability. Civic SOCs facing high advisory volume benefit from faster first-pass understanding of CVEs affecting city systems. Browser plug-ins that provide EDR containment guidance for triage workflows with AI summaries fail because providing EDR containment guidance is a response aid, not a CVE page summarization aid for triage; they do not provide the research summaries described in the correct option. Browser plug-ins that correlate network telemetry for triage workflows with AI summaries fail because correlating network telemetry is different from summarizing CVE pages for analyst triage; they do not provide the research summaries described in the correct option. Browser plug-ins that prioritize workstation patches for triage workflows with AI summaries fail because prioritizing workstation patches is not the same as summarizing CVE pages during triage. Exam caveat: summarizers can omit severity nuances, affected version ranges, or exploit preconditions; acting on a summary alone can mis-prioritize municipal patching. Operational check: treat AI summaries as drafts, click through to the primary advisory for assets in inventory, record the CVE ID and affected product versions in the ticket, and prohibit closing a vulnerability item based solely on chatbot text without a human confirmation of applicability.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.