
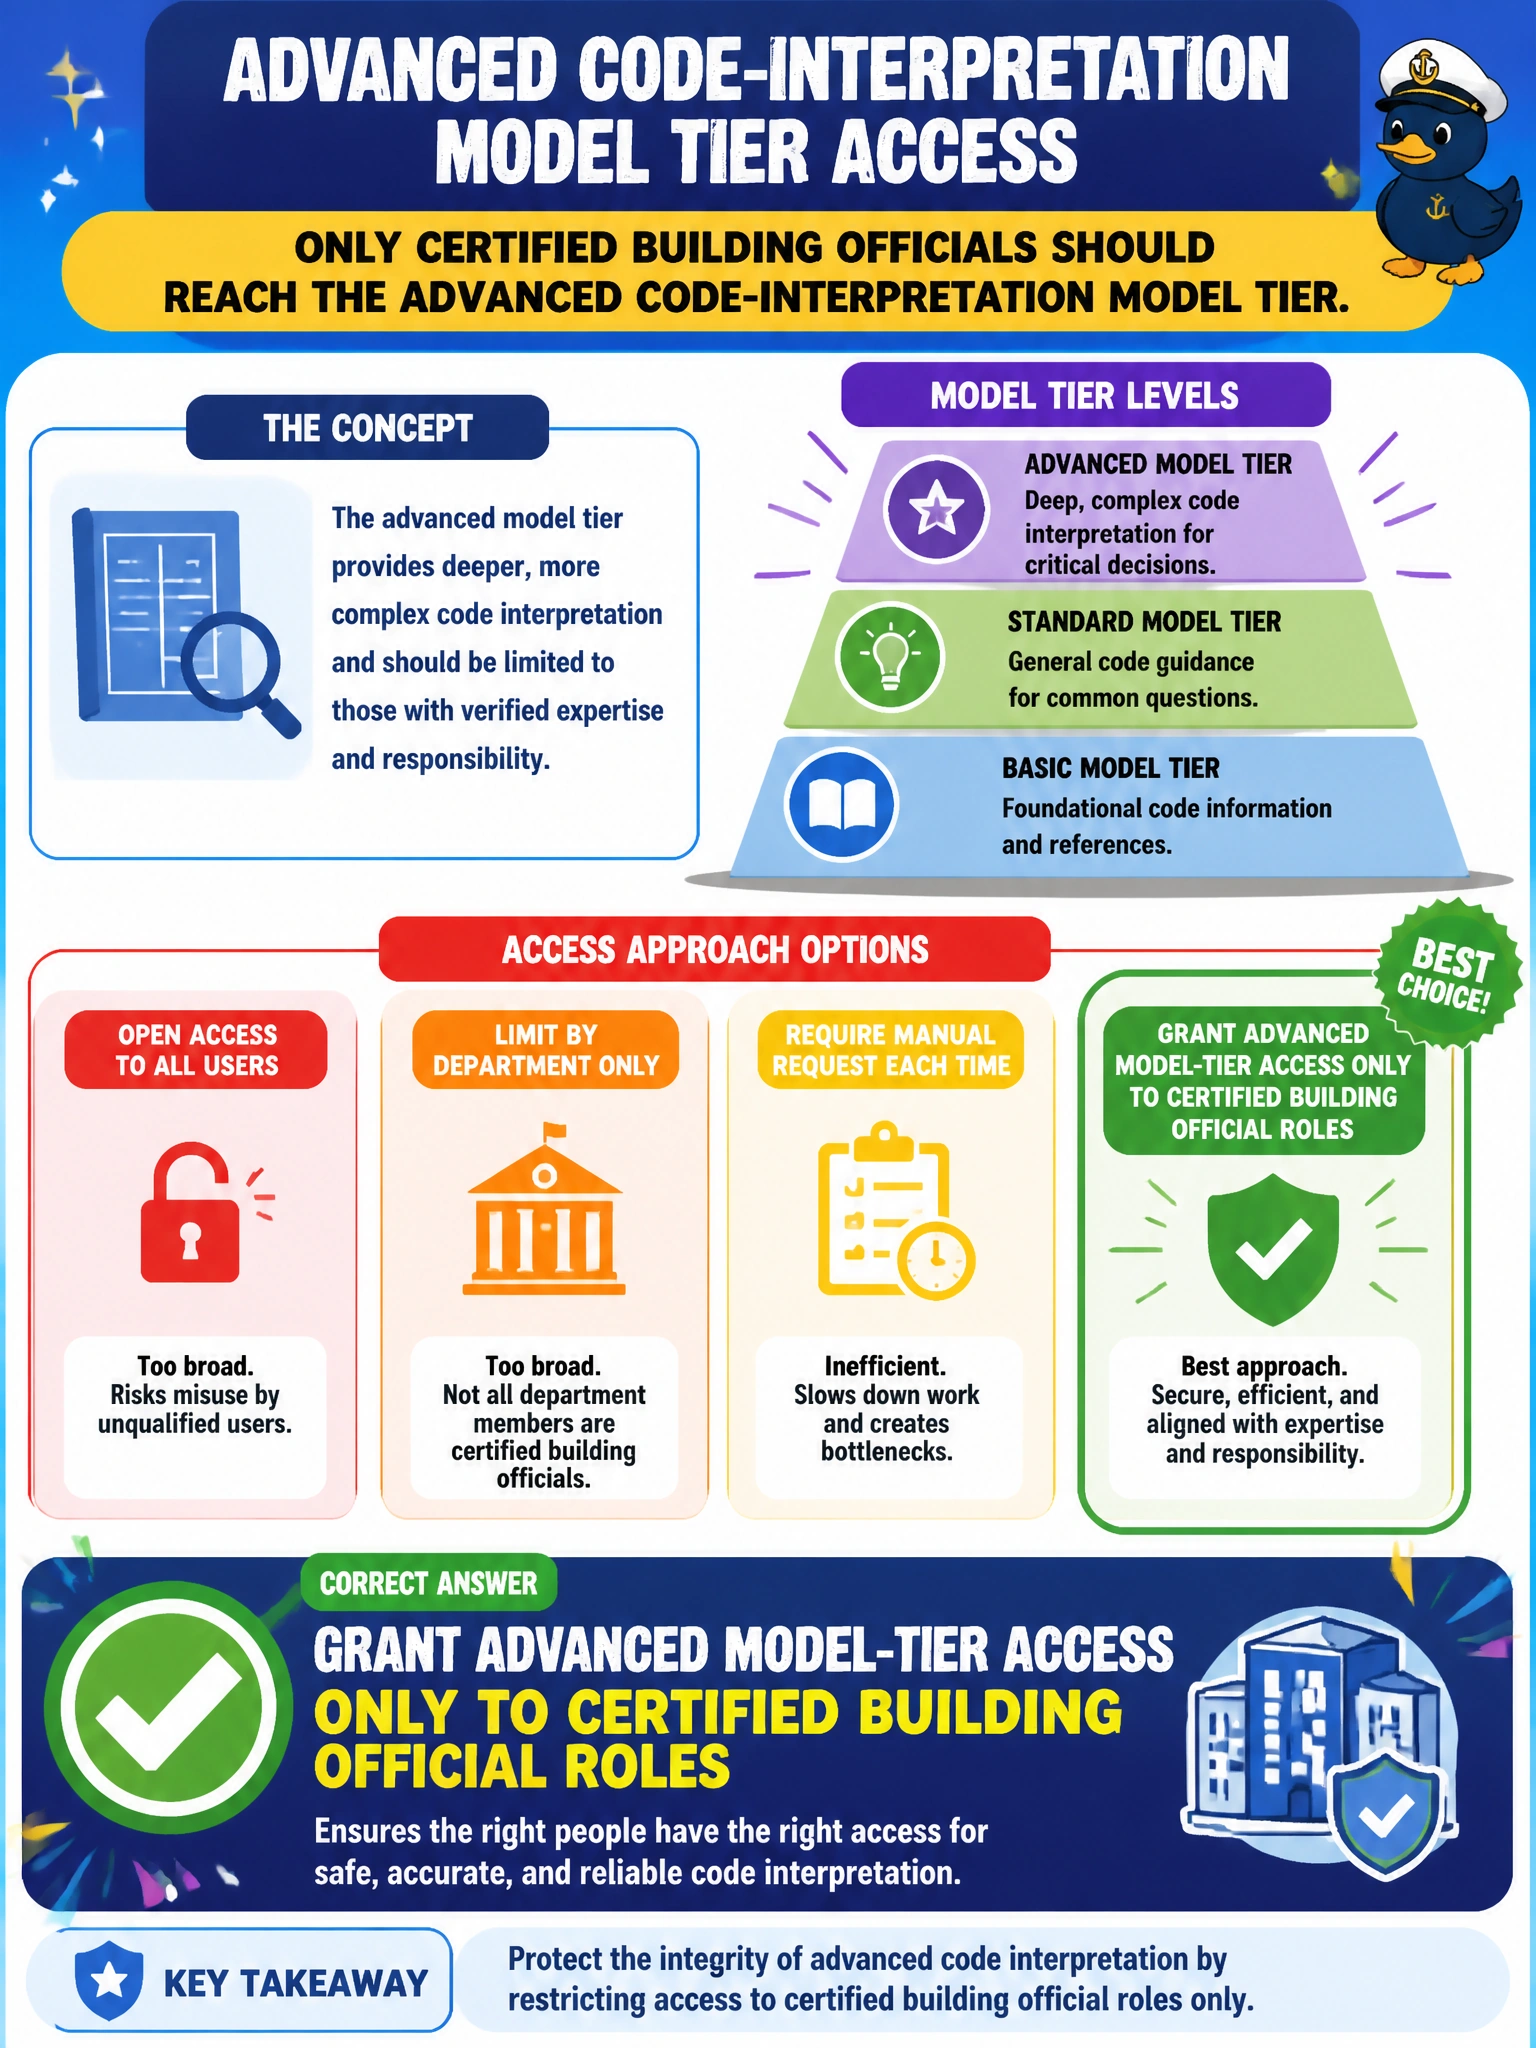
Only certified building officials should reach the advanced code-interpretation model tier. Which access approach best fits?
Select an answer to reveal the explanation.
Short Explanation
Advanced code brains are for people who actually interpret code for a living. You'll give that tier to the certified role itself — not to individual accounts, not through delegates only, and not to a cached copy of the role. If the role isn't currently certified, it doesn't get the privileged tier.
Full Explanation
Granting advanced model-tier access only to certified building official roles is the least-privilege approach for an advanced code-interpretation model. Model access controls decide which municipal roles may invoke privileged tiers. Advanced code interpretation can influence permit decisions and sensitive building determinations; limiting that tier to certified building officials reduces unauthorized use, incorrect reliance by unqualified staff, and disclosure of privileged model capabilities outside the intended civic role set.
Granting advanced model-tier access only to certified building official accounts fails because direct account-level grants bypass role-based enforcement; individual accounts persist and must be managed manually and do not automatically track current certification, which is the opposite of restricting the tier to the currently certified role. Granting advanced model-tier access only via certified building official delegates fails because it denies direct access to the certified officials themselves and routes the privileged capability through delegates who do not hold the building-official certification the stem reserves it for. Granting advanced model-tier access only to cached certified building official roles fails because a cached copy can be stale and continue to list holders who are no longer currently certified, allowing outdated membership to reach a privileged capability scoped to authoritative current certification.
Exam caveat: Privileged model tiers follow role-based least privilege. Account-based grants, delegate-only paths, and cached-role grants are classic wrong answers when the stem names a specific certified role.
Operational check: Map the advanced code-interpretation tier to certified building official roles only, attempt invoke from an account-only grant without the role, via a delegate-only path, and from a cached role entry (all denied), confirm a certified official succeeds, and ensure no non-role grant is used for that tier.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.