
Transit wants launch hardening for a fare bot using layered gateway defenses. Which approach best combines complementary controls?
Select an answer to reveal the explanation.
Short Explanation
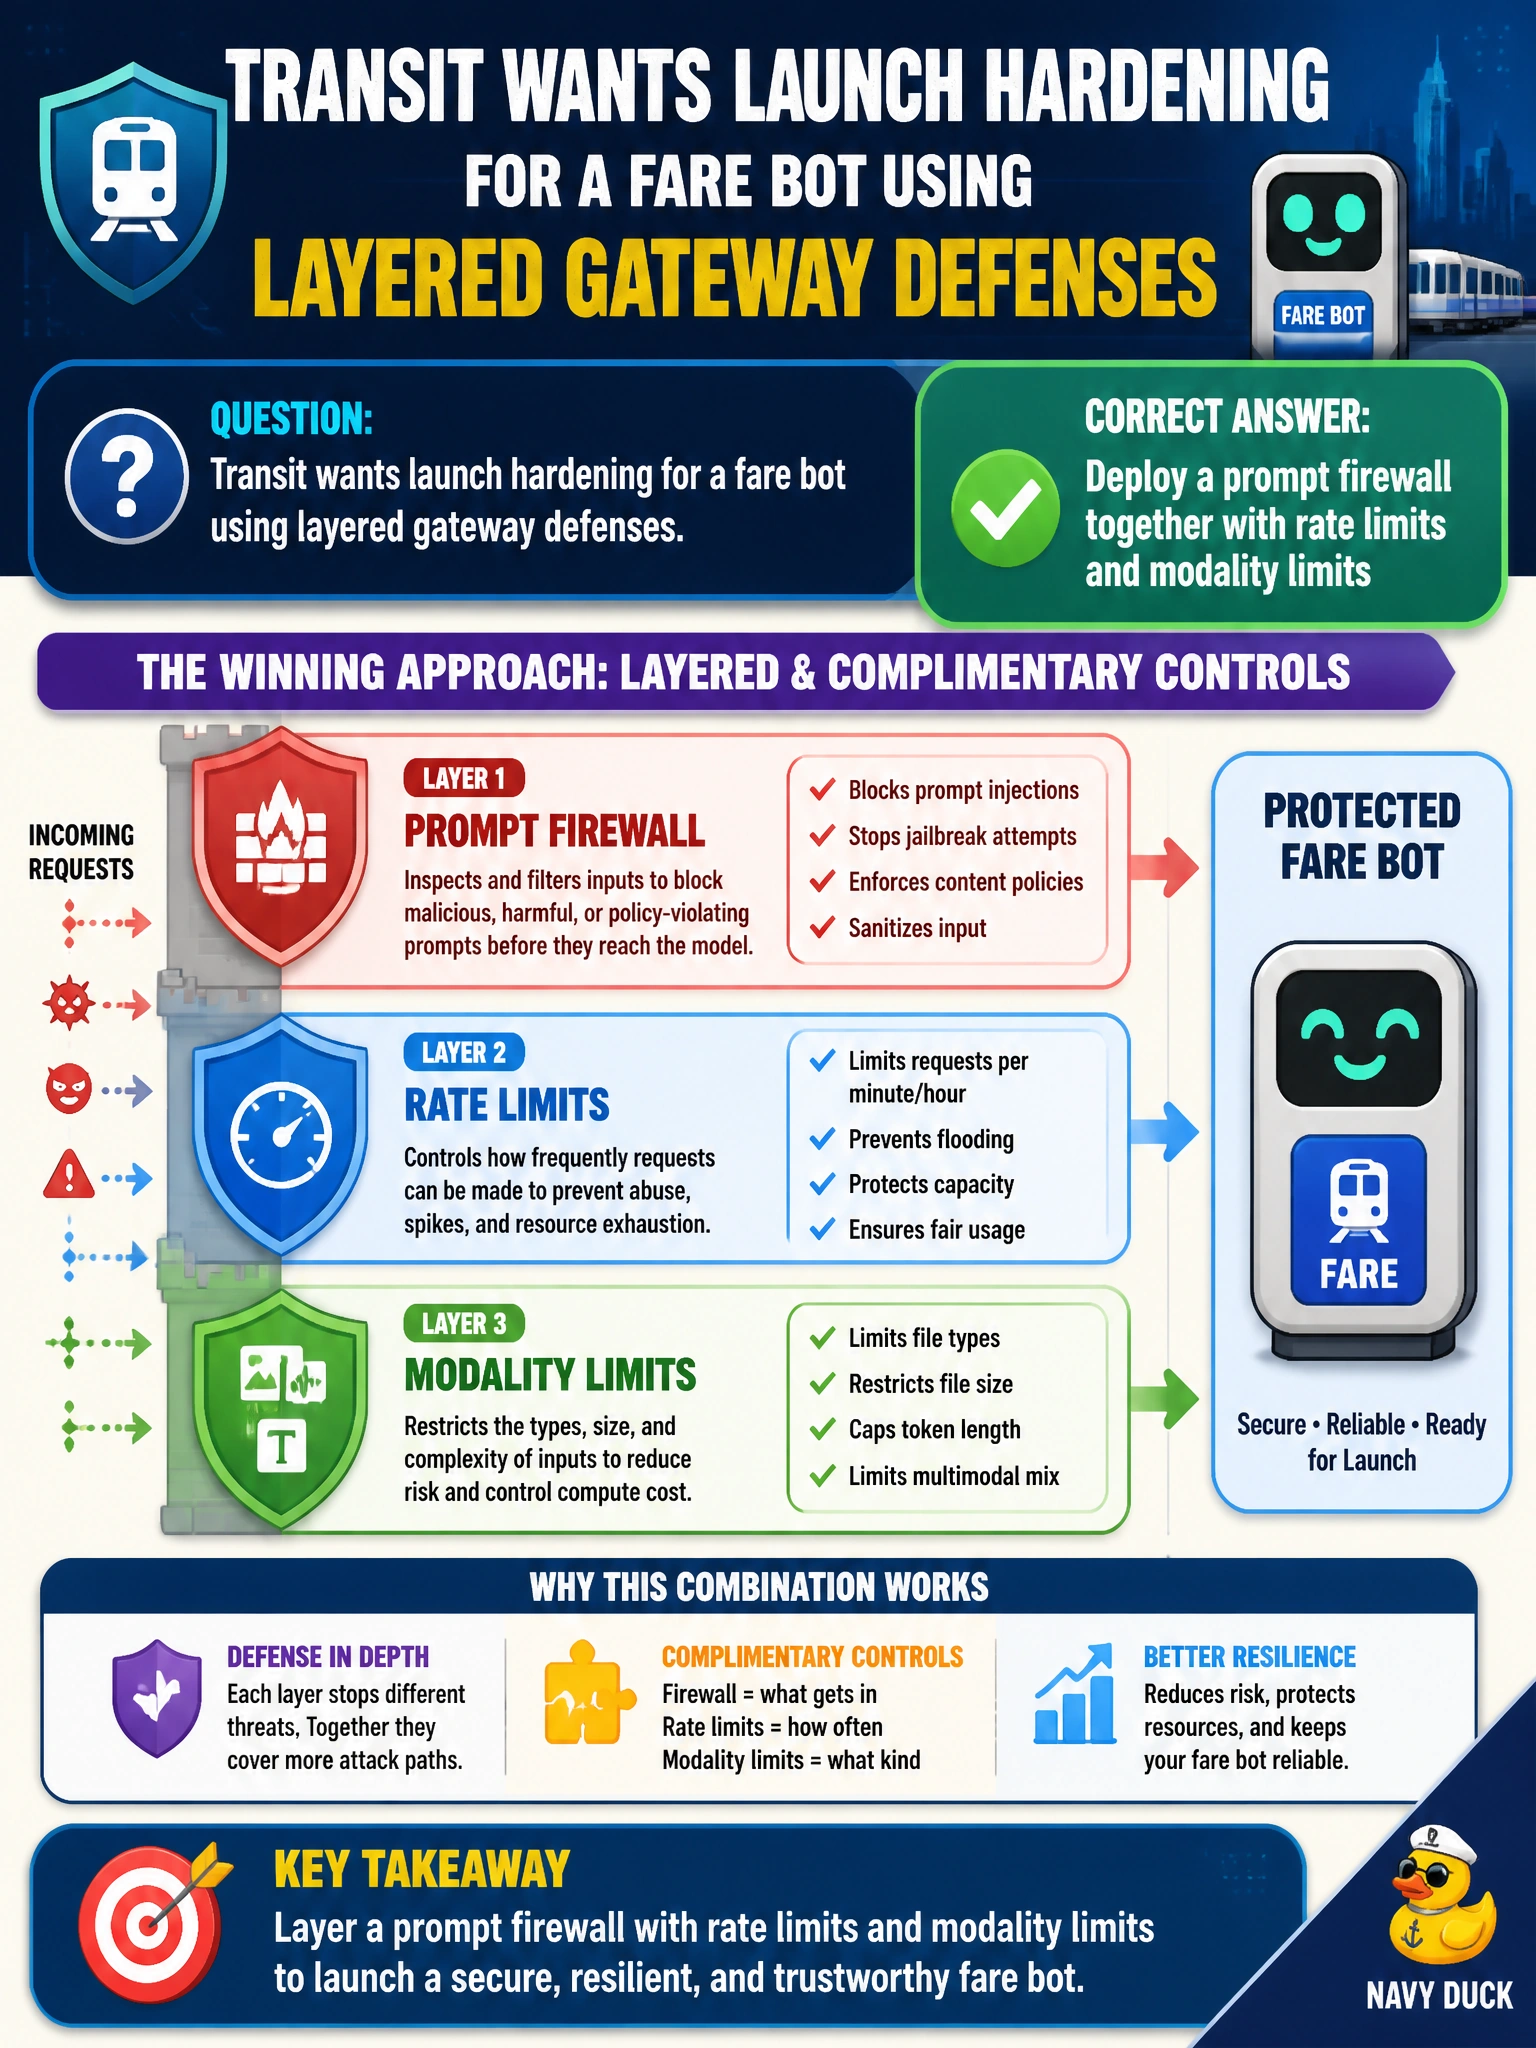
One lock is nice; a firewall, a speed bump, and a media filter are better. Layering a prompt firewall with rate and modality limits hardens the fare bot at launch. You can't block injections and risky uploads with authentication checks, request signing, and token quotas alone.
Full Explanation
Deploying a prompt firewall together with rate limits and modality limits best combines complementary gateway defenses for transit fare-bot launch hardening. Defense in depth at the AI edge means malicious instructions are filtered by a prompt firewall, request volume is constrained by rate limits, and inappropriate input types are blocked by modality limits. Together those controls reduce prompt injection, flooding, and risky multimodal abuse against a public-facing municipal transit assistant at go-live.
Enforcing authentication checks with request signing and token quotas fails because verifying identity and message integrity with capped usage does not filter malicious instructions or block disallowed modalities at the gateway. Configuring input sanitization with jailbreak detection and PII redaction fails because it stacks content-cleaning controls only and provides no rate limiting or modality blocking to complement prompt filtering against flooding and multimodal abuse. Applying model alignment tuning with safety evaluations and policy reviews fails because it hardens base-model behavior and governance offline rather than enforcing inbound gateway controls—prompt filtering, rate limits, and modality limits—required at launch.
Exam caveat: Launch hardening questions often reward layered gateway controls over single soft measures. Pair content filtering (prompt firewall) with volume and modality constraints; model alignment tuning with safety evaluations and policy reviews are pre-deployment controls, not gateway hardening steps.
Operational check: Before fare-bot launch, enable prompt-firewall rules, per-client rate limits, and modality policy; attempt an injection-style prompt, a burst flood, and a disallowed media upload; confirm each is blocked; and confirm that model alignment tuning with safety evaluations and policy reviews is not used in place of inbound gateway controls.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.