
A SOC analyst reviews a scan report showing an Apache server exposes version details, enables TRACE, and omits X-Content-Type-Options and X-Frame-Options. The application code team says the web app itself has no code defects. Which vulnerability scanning method should the analyst request to validate these findings?
Select an answer to reveal the explanation.
Short Explanation
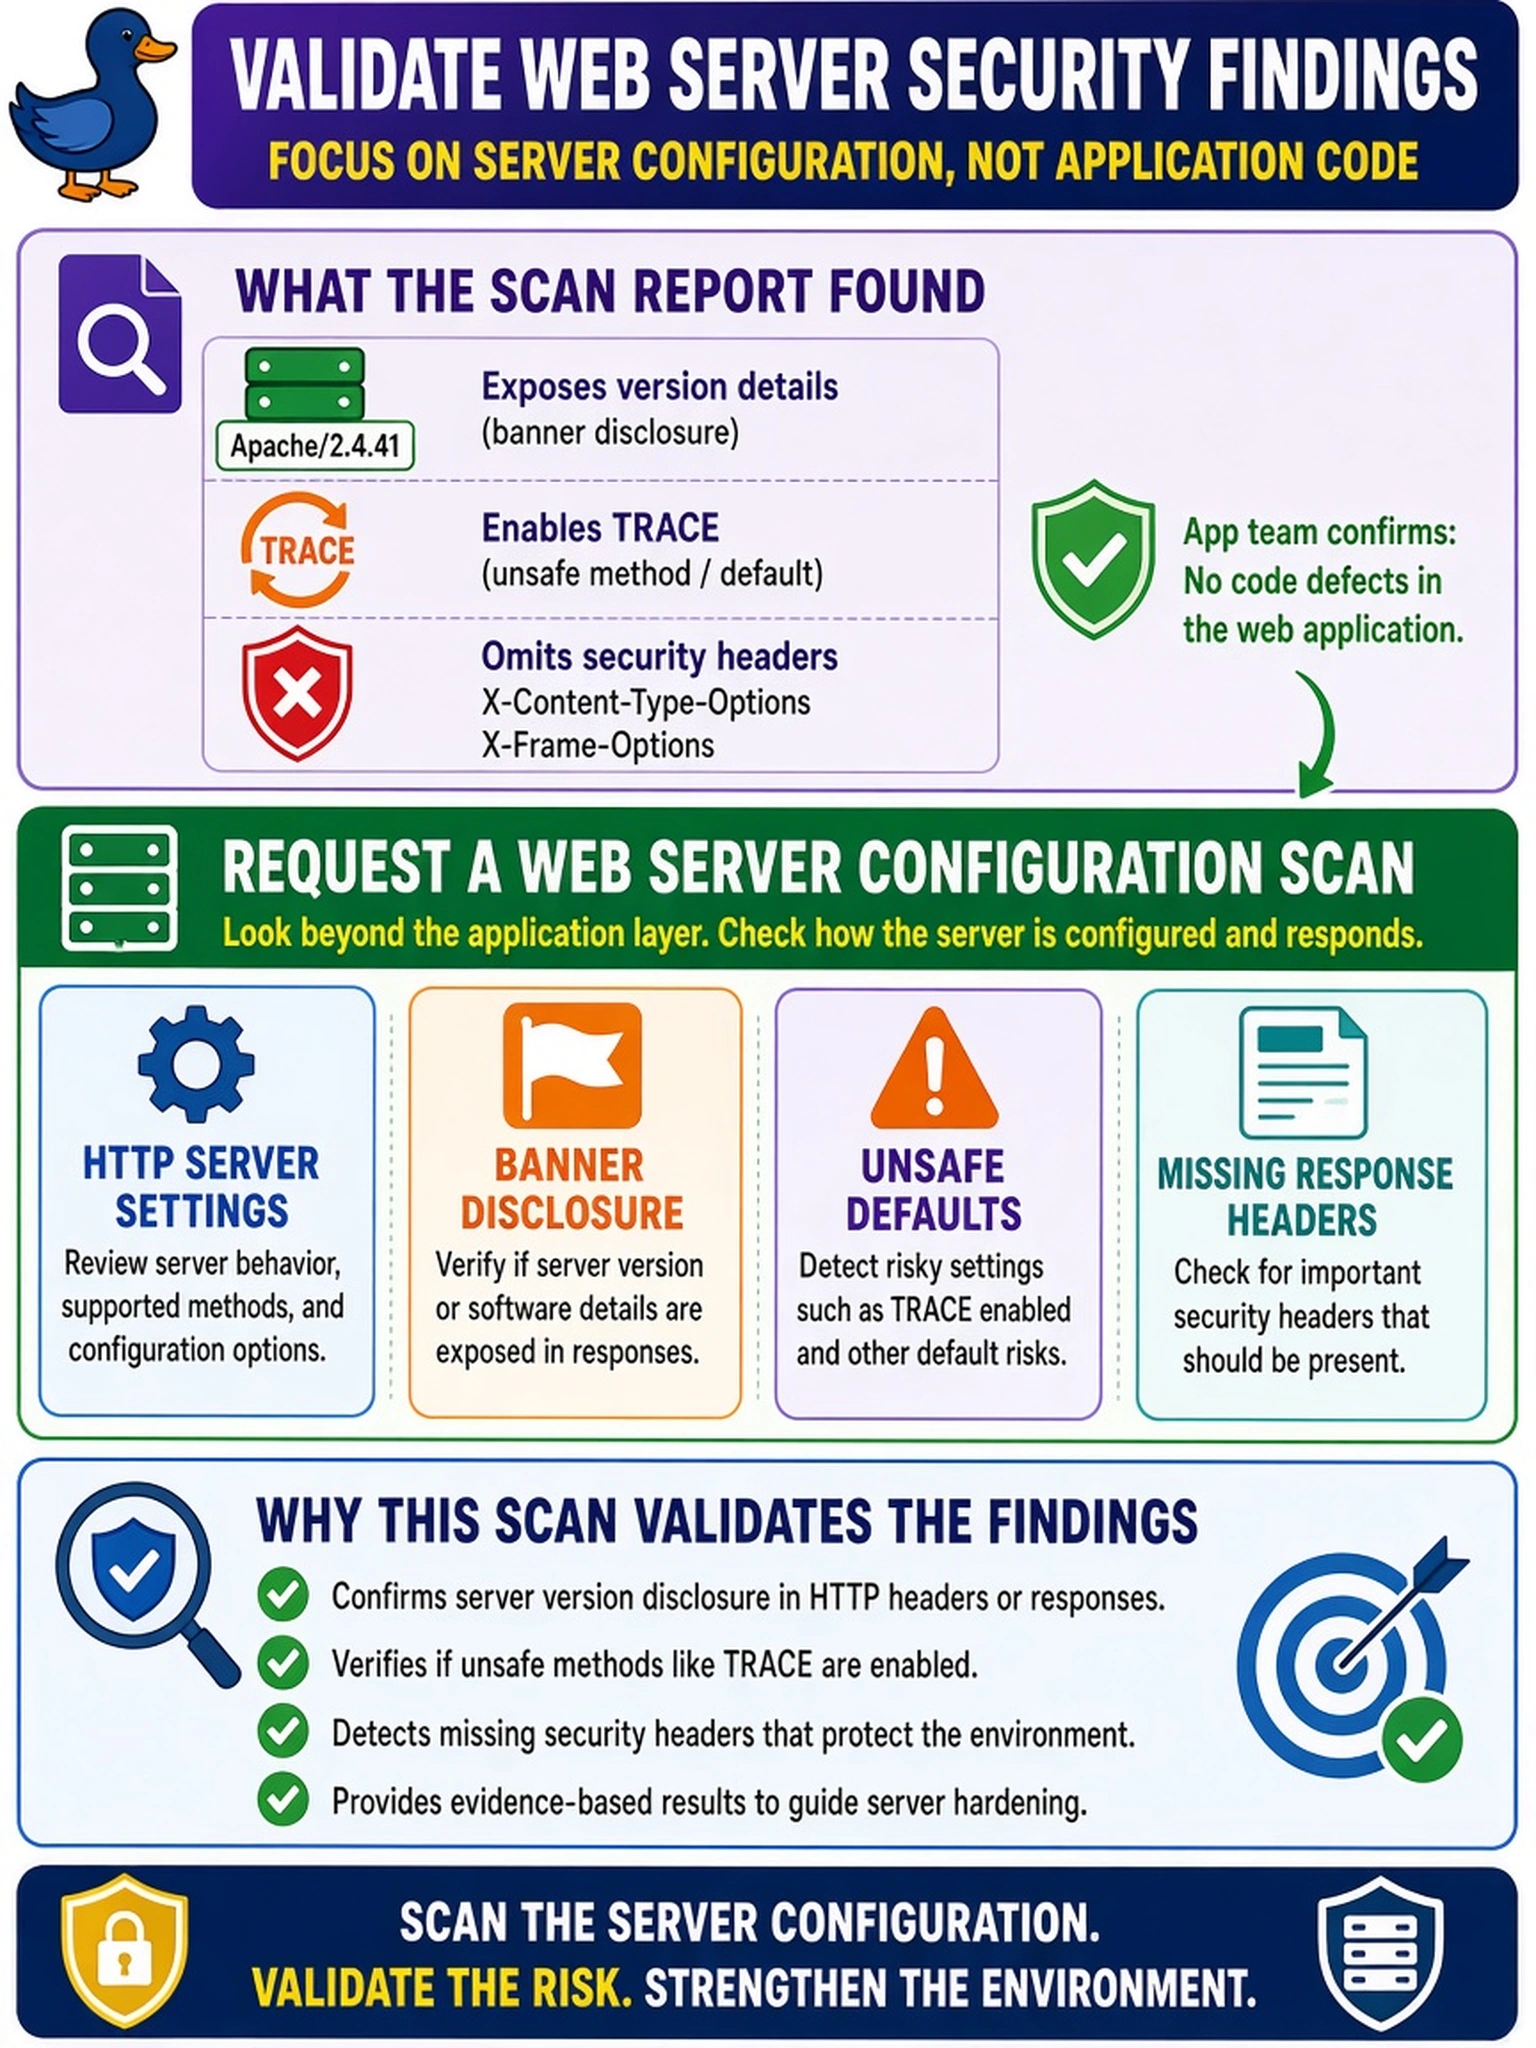
Think of a web server like a storefront window: the signs and locks matter even if the products inside are fine. If the finding is banners, defaults, or headers, you want a web server configuration scan - not an app test. Don't chase code bugs when the server's own settings are the leak.
Full Explanation
Web server configuration scanning examines the settings exposed by the HTTP service itself: software banners, supported methods, default files or directories, TLS choices, and response headers such as X-Content-Type-Options or X-Frame-Options. When the reported issue concerns server settings rather than application logic, the analyst should request a configuration scan because it validates whether the platform is hardened and whether required headers are actually returned. A dynamic application security test is aimed at application behavior, such as input validation, authentication flaws, and injection paths, so it may miss a missing header or enabled TRACE method. An authenticated network vulnerability scan is useful for host inventory, open ports, and missing patches, but it generally does not interpret web server directives or response-header policy. A source code review inspects application source for insecure coding patterns, which is appropriate for code defects but not for web server configuration artifacts or banner disclosure. Exam caveat: choose the scanning method that matches the artifact in the finding - server configuration versus application code versus host patching. Operational check: run the configuration scan against the live web endpoint and compare returned HTTP headers and enabled methods with the approved hardening baseline.