
An EDR alert flags a host beaconing to an external IP every 60 seconds. Full packet capture is disabled due to storage constraints. You need to confirm if this beaconing correlates with other hosts in the subnet and identify the specific destination port without capturing payloads. Which tool provides the necessary visibility?
Select an answer to reveal the explanation.
Short Explanation
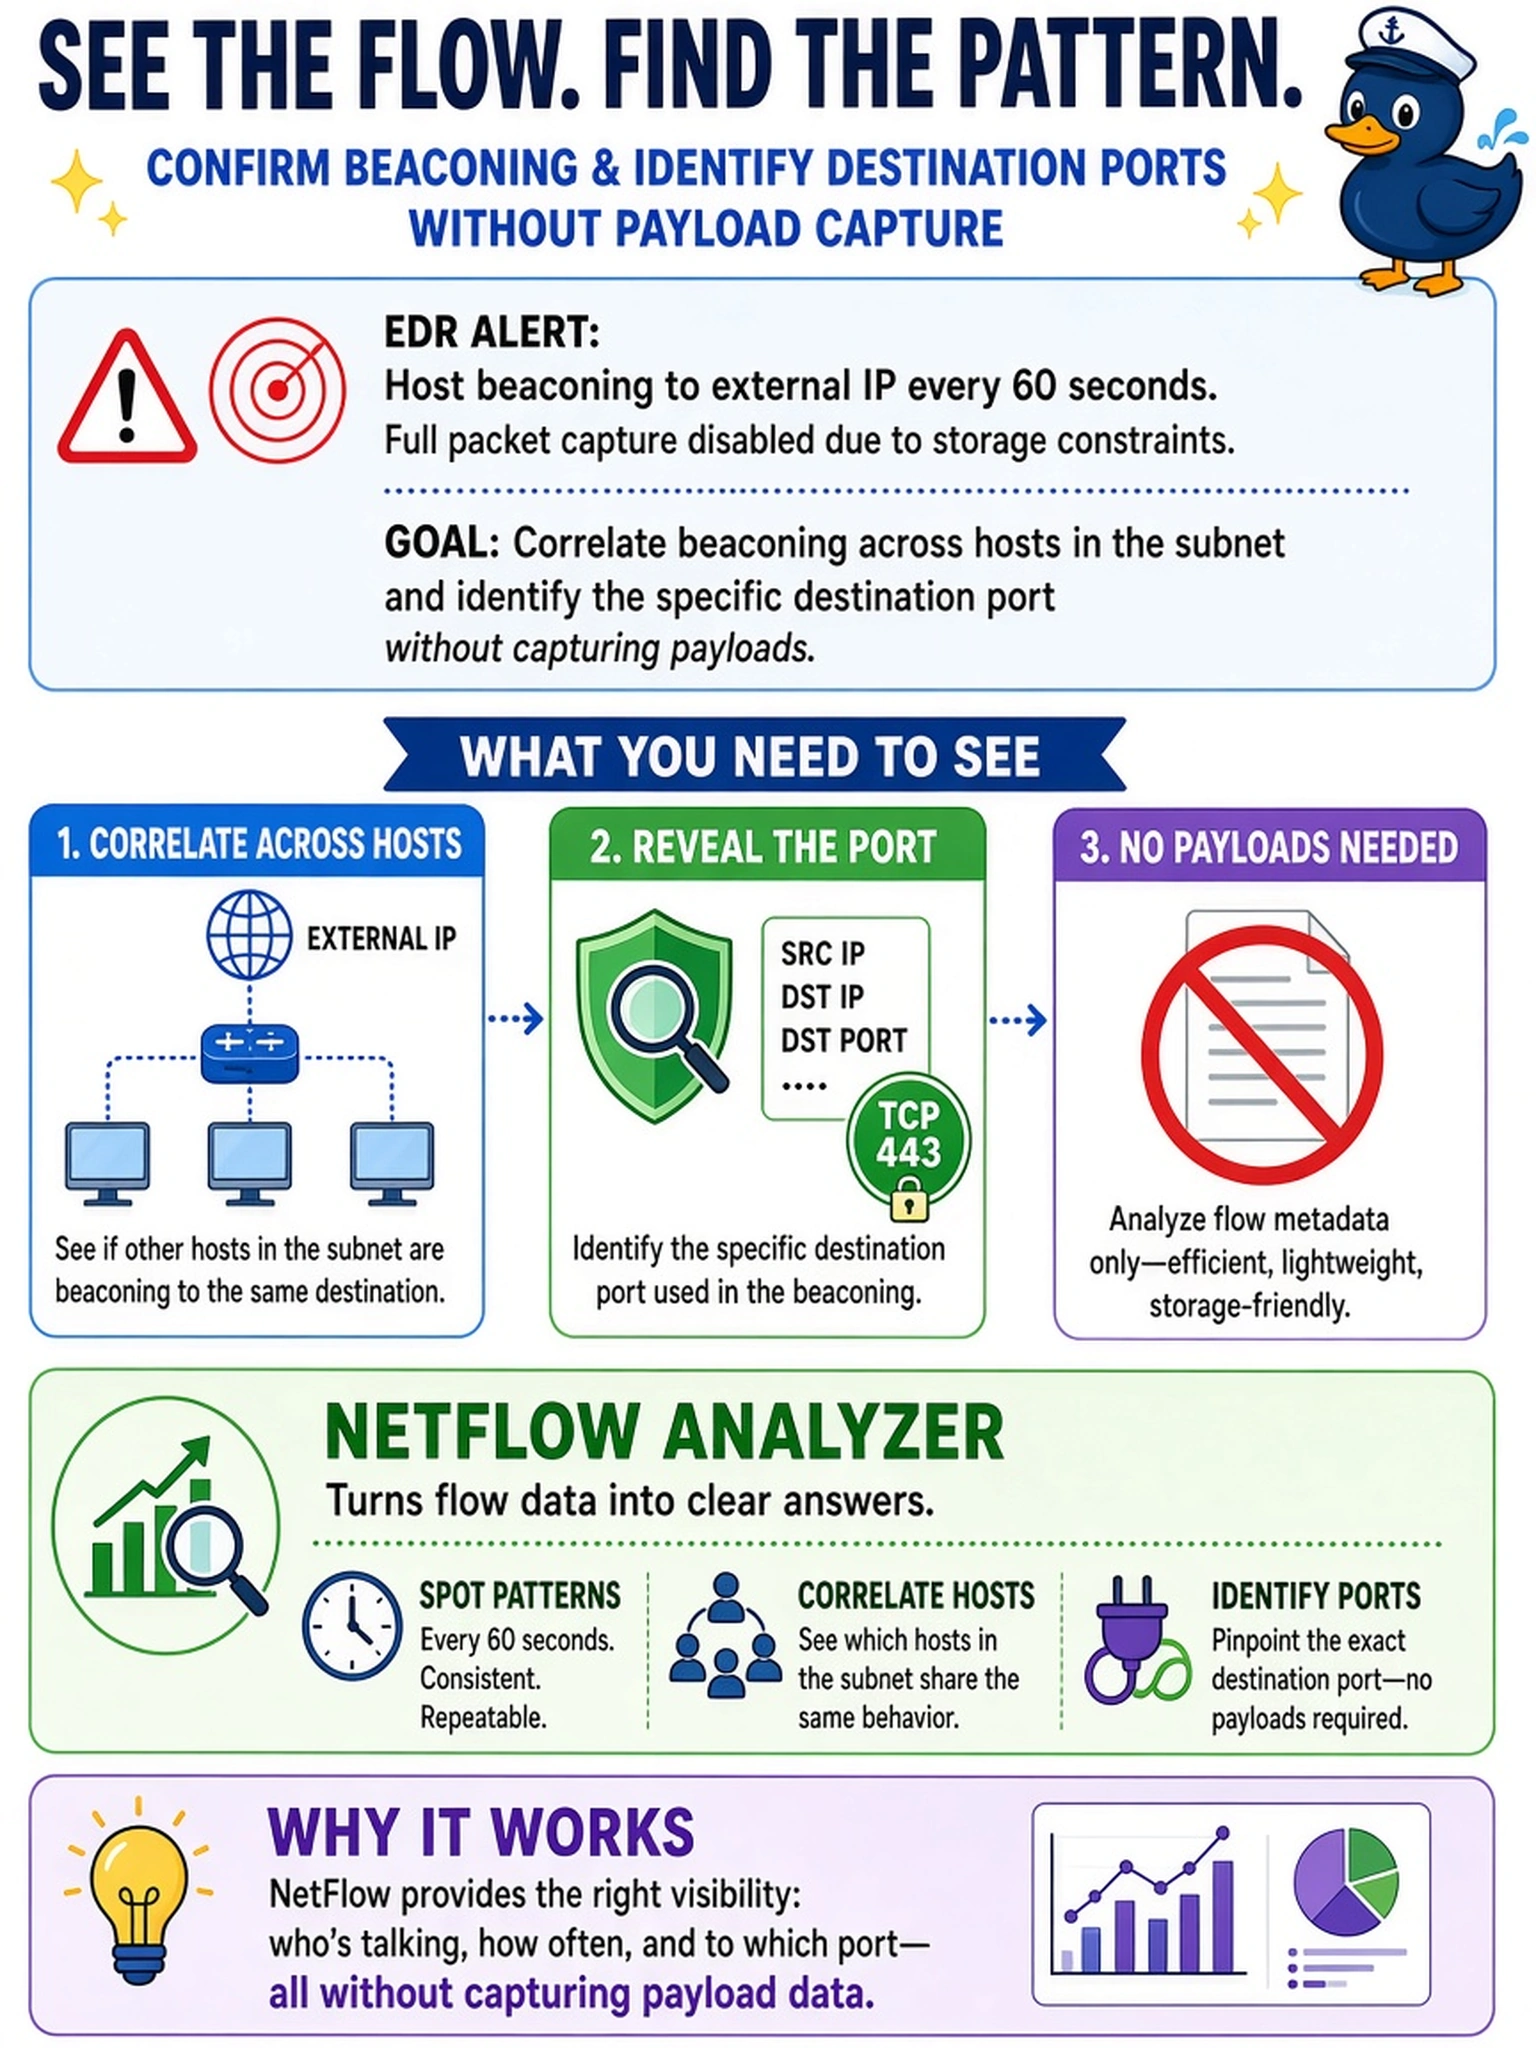
Think of NetFlow as the metadata log for your network traffic: who talked to whom, when, and on what port. Since full packet capture is disabled, you can't use Wireshark, and a vulnerability scanner won't care about beaconing. NetFlow gives you the flow records to see if other hosts are hitting that same IP and port.
Full Explanation
NetFlow is a network protocol that provides statistics about network traffic, including source and destination IP addresses, ports, and timestamps. It is ideal for this scenario because it captures flow metadata without the storage overhead of full packet capture. By analyzing flow records, an analyst can identify periodic connections, unusual destination ports, and lateral movement patterns across multiple hosts. This allows for correlation of the beaconing activity with other subnet hosts, confirming a broader compromise. SIEMs with syslog ingestion typically rely on application or system logs, which may not contain network-level flow details unless specifically configured, and often lack the granular port-level visibility needed for this specific correlation. Wireshark requires full packet capture, which is explicitly disabled in this scenario due to storage constraints, making it impossible to use for this task. Vulnerability scanners are designed to identify known weaknesses in systems, not to analyze real-time network traffic patterns or beaconing behavior. Exam caveat: Do not confuse NetFlow with full packet capture; NetFlow is metadata, while PCAP is the actual data payload. Operational check: Verify that your network devices are exporting flow records to a collector and that the collector is parsing port numbers correctly.