
Utilities NOC builders are air-gapped and cannot reach the public Internet for packages. How should CI obtain approved dependencies?
Select an answer to reveal the explanation.
Short Explanation
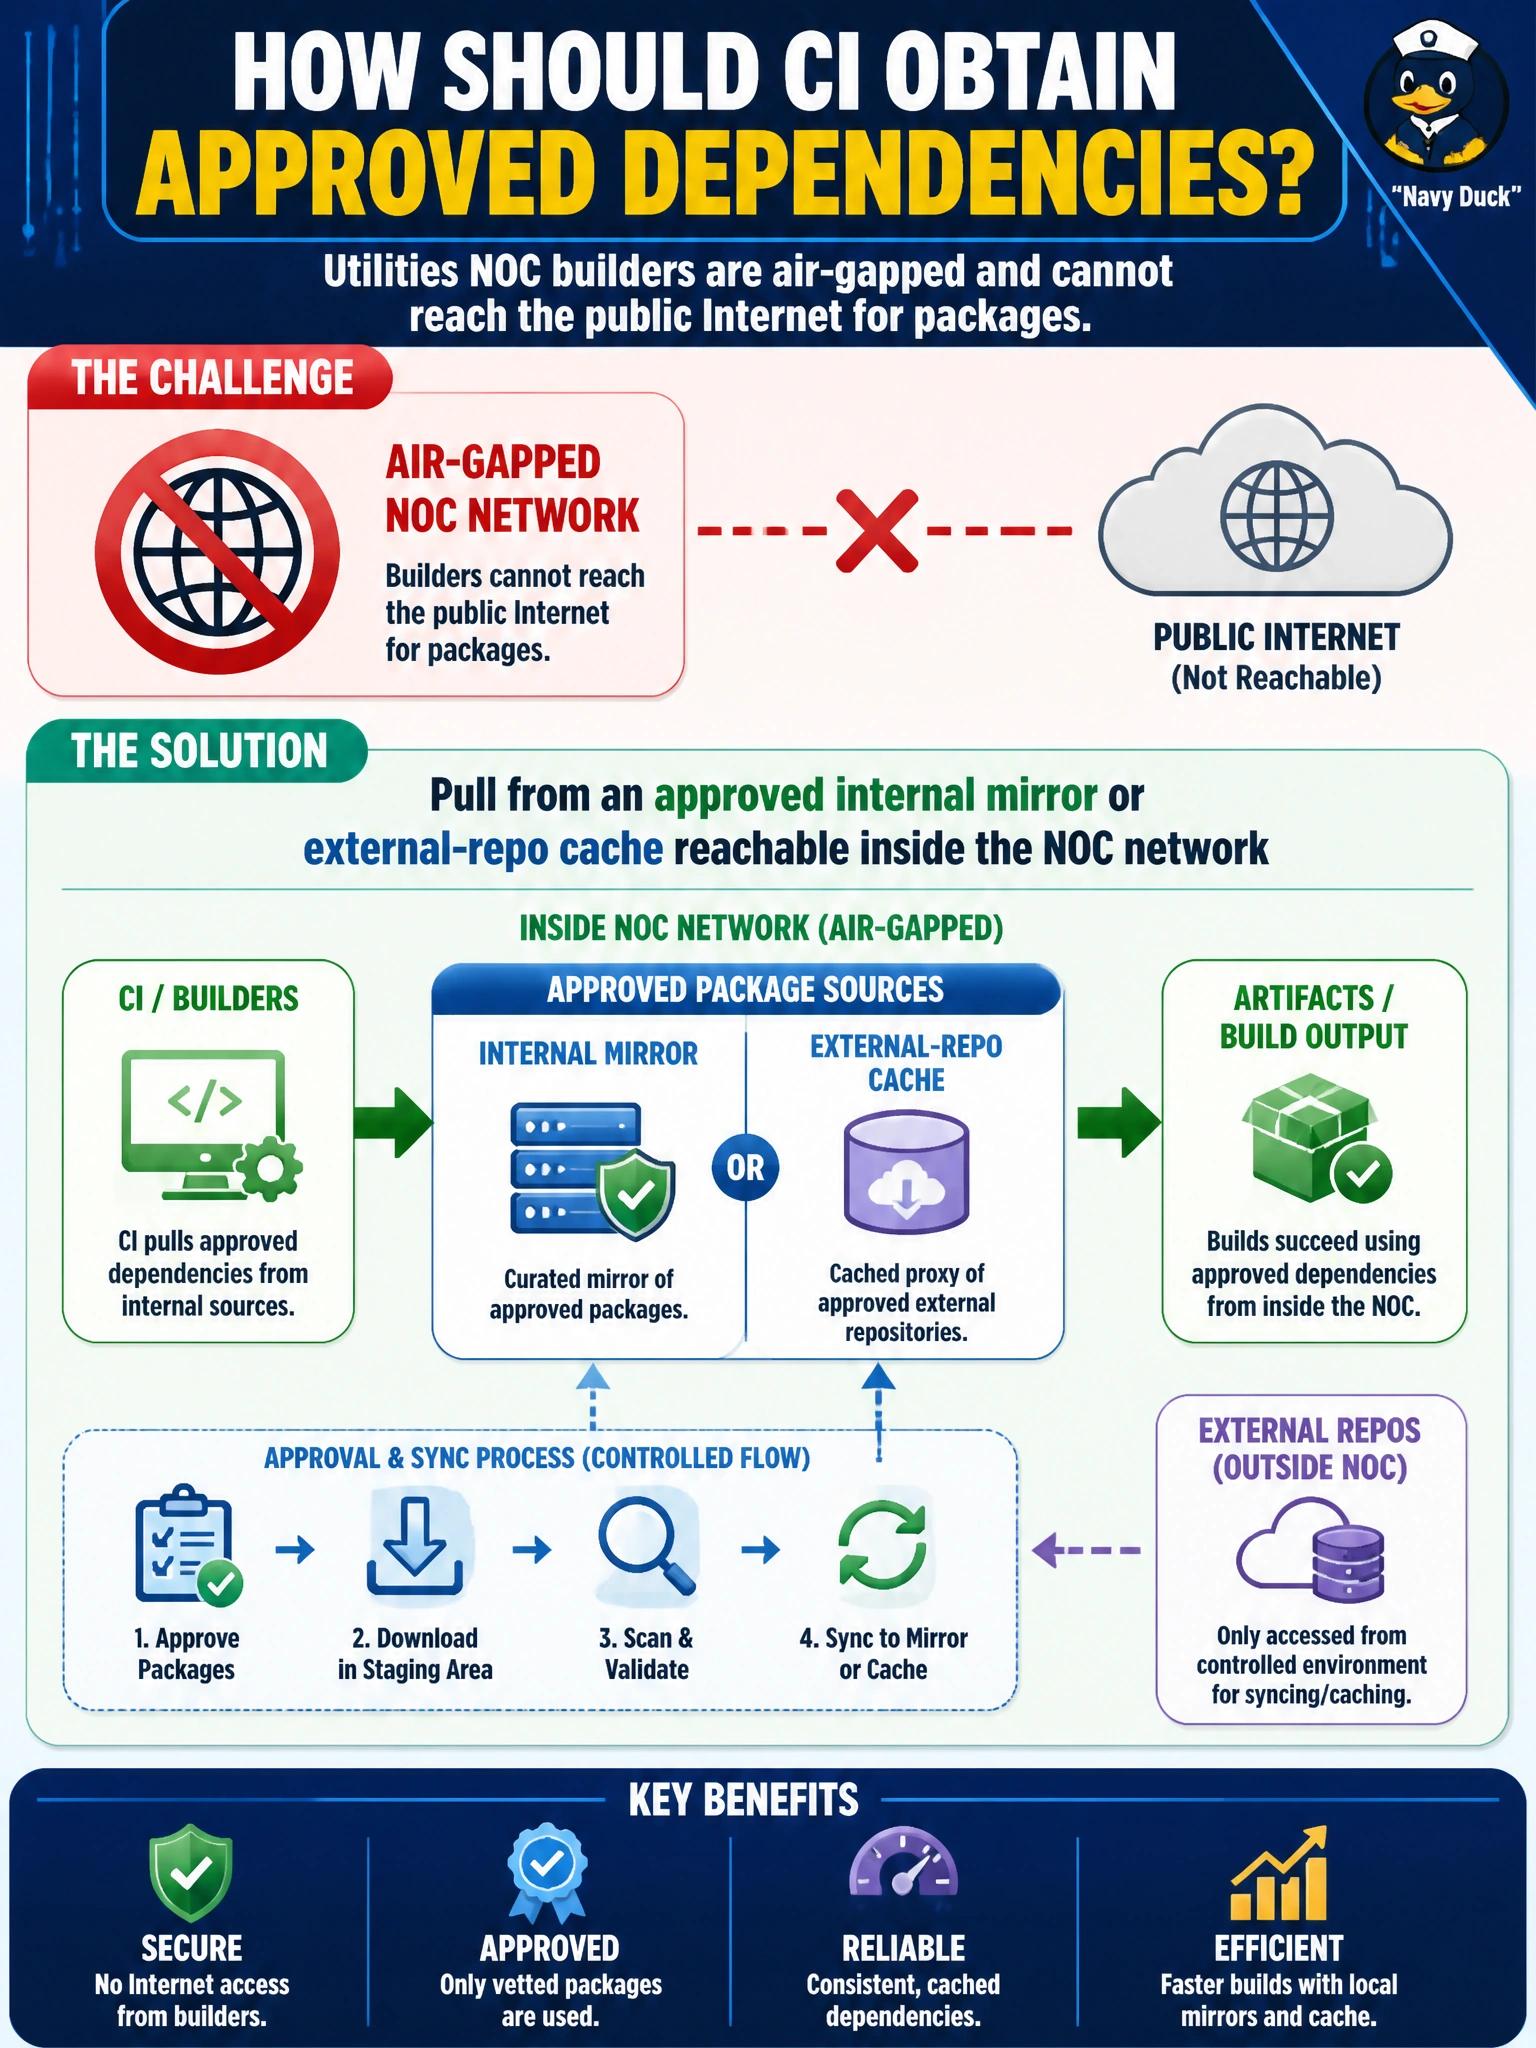
Air-gapped NOC builds need a neighborhood warehouse—the approved internal mirror—not a scavenger hunt of USB sticks. The cache sits inside the fence so builders get known-good packages without punching holes to the open Internet.
Full Explanation
When builders are air-gapped and cannot reach the public Internet, CI obtains approved dependencies from an internal mirror or external-repo cache that is reachable on the NOC network. Utilities NOC pipelines should pull packages only from that controlled source so builds remain reproducible and every artifact has a known provenance path inside the fence. The correct practice works because air-gapped environments still need dependencies; the operational answer is to stage approved packages into a reachable cache, not to punch unrestricted holes from production control networks to the open Internet.
Disabling package installs and copying random binaries from personal USB sticks fails because USB-sourced binaries bypass integrity verification, version pinning, and malware scanning, and they leave no auditable supply chain for regulated utilities tooling. Opening unrestricted outbound Internet from every production SCADA host for convenience fails conceptually: SCADA and NOC production hosts are high-impact assets; broad egress for package convenience violates network segmentation and dramatically expands attack surface. Hard-coding unpaid third-party CDN URLs with no integrity checks into every job fails because those URLs are neither approved mirrors nor integrity-protected—content can change, disappear, or be substituted without the pipeline noticing.
Exam caveat: mirrors must themselves be patched, access-controlled, and periodically reconciled with upstream advisories; a stale internal cache can freeze known-vulnerable packages into "approved" builds. Operational check: from a NOC builder, resolve a dependency only via the approved mirror hostname, confirm checksum or signature verification is enabled, deny direct public registry access in network policy, and document the process for promoting a new package version into the mirror after security review.