
City VPN concentrator certificates will expire during a holiday freeze. What certificate-oriented configuration practice should ops schedule?
Select an answer to reveal the explanation.
Short Explanation
Renew before the parade, not after the floats will not start. Proactive VPN cert renewal is that early maintenance window. Waiting for citizen outages is the expensive alarm clock.
Full Explanation
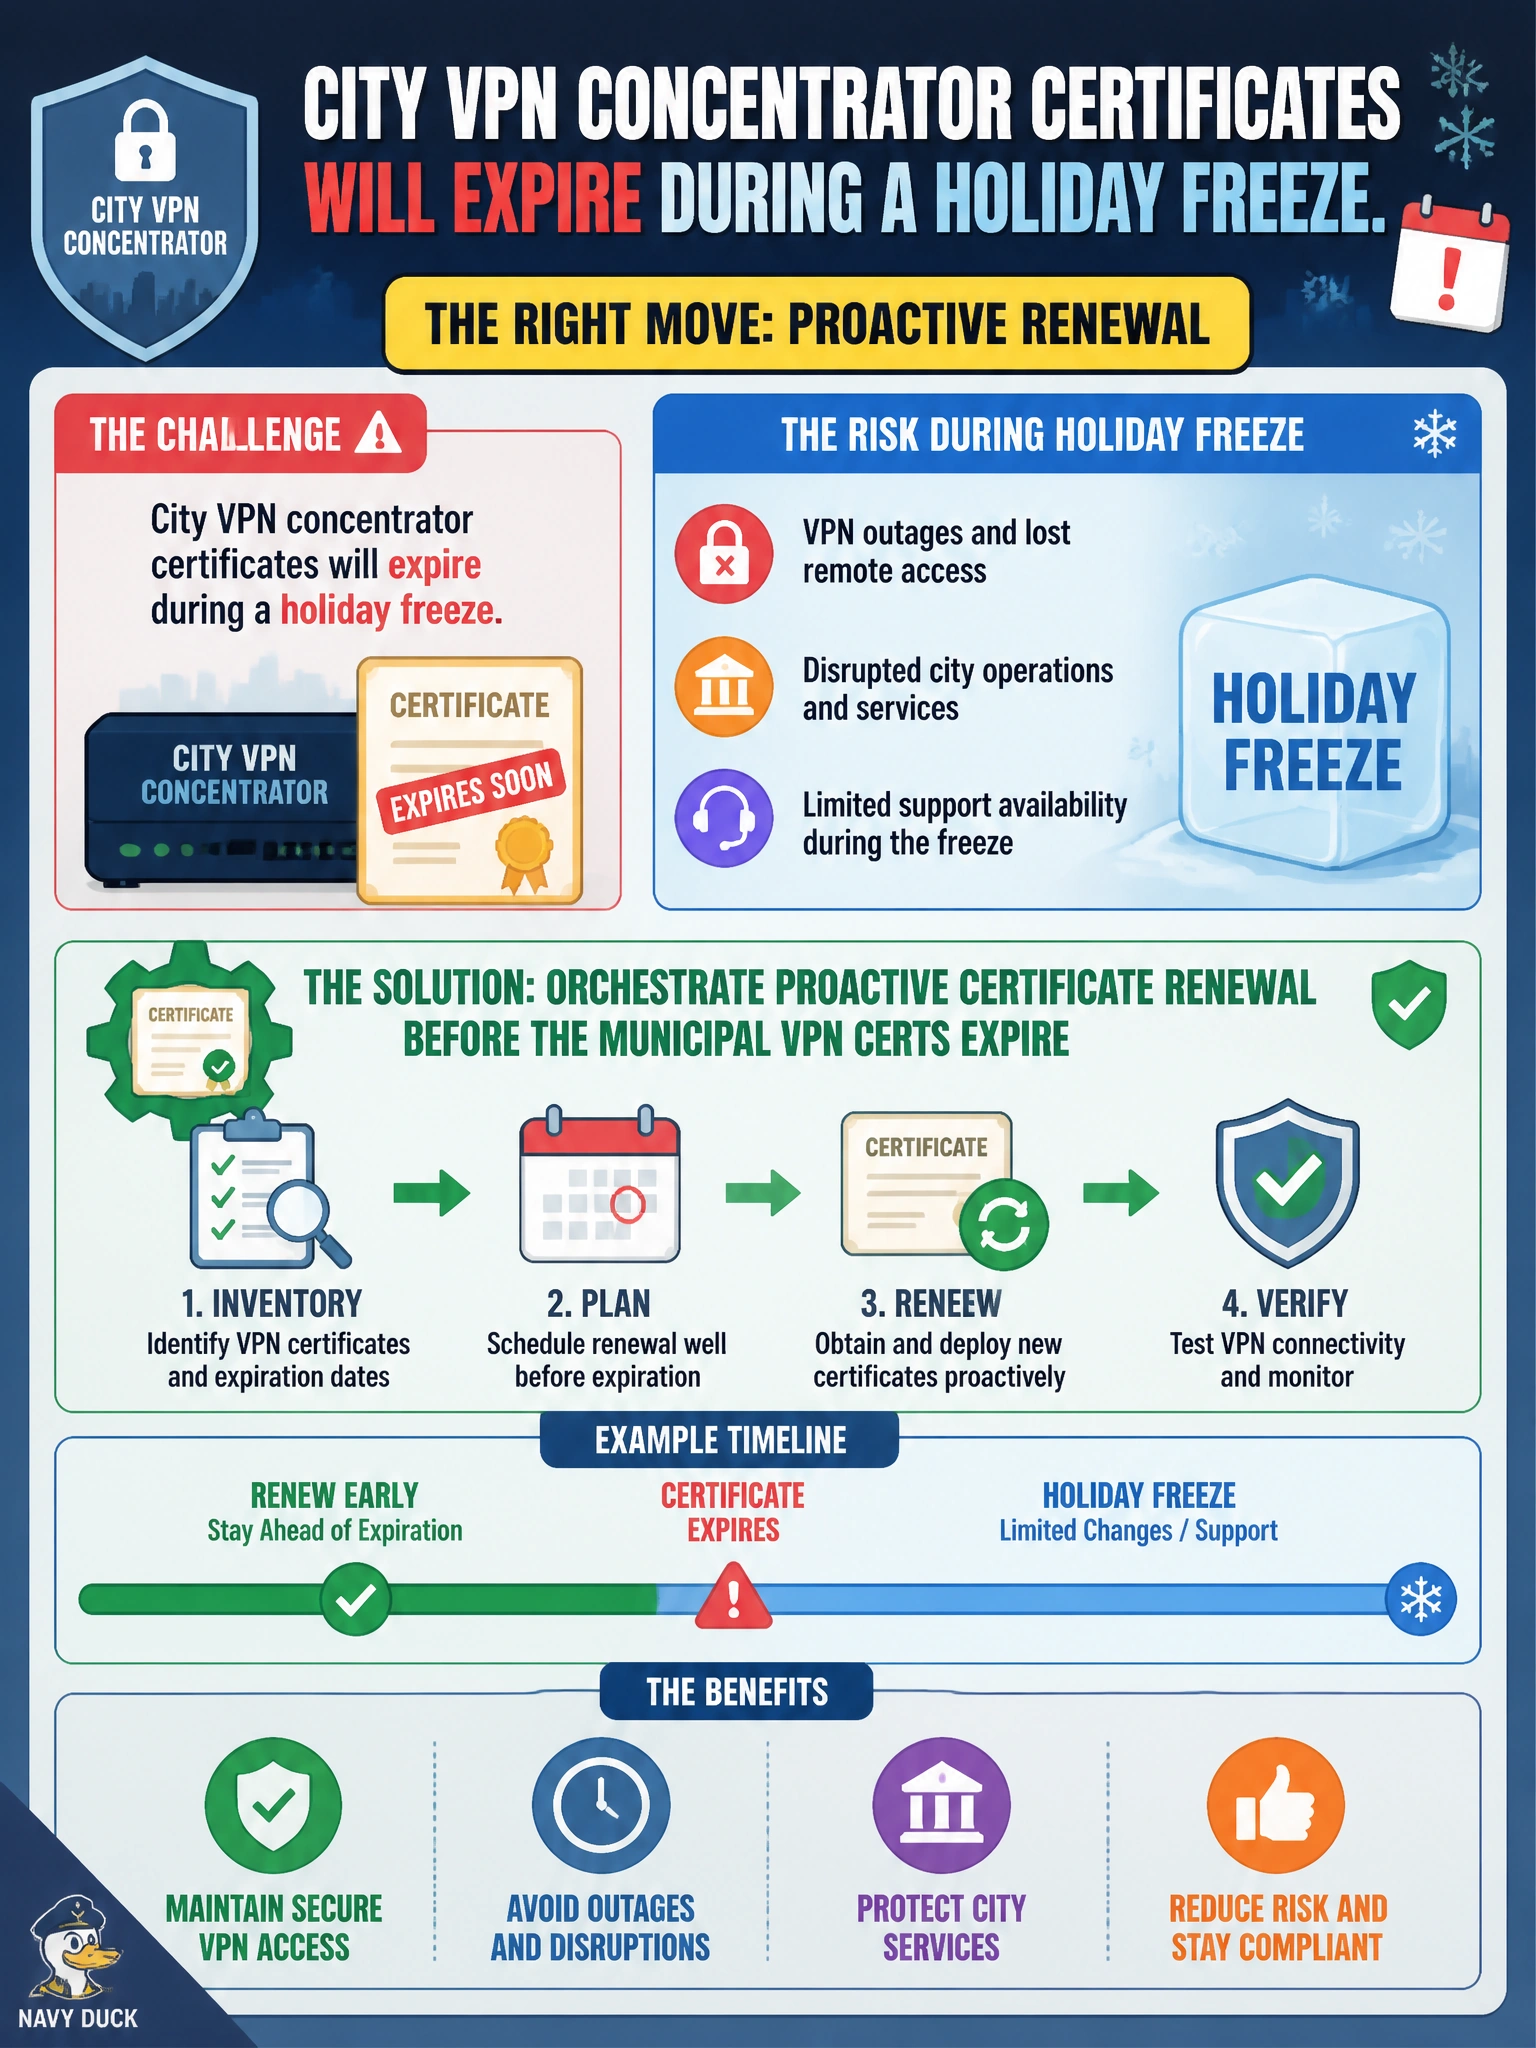
City VPN concentrator certificates that will expire during a holiday freeze require orchestrating proactive certificate renewal before the municipal VPN certs expire. Proactive renewal stages issuance, installs the new cert on concentrators, validates chain and revocation endpoints, and completes cutover while staff are available—avoiding citizen VPN outages when change freezes and on-call coverage are thinnest.
Waiting for citizen VPN failures to detect expiry in production uses outage as monitoring and harms remote workers and telehealth-adjacent municipal access patterns. Disabling VPN authentication so expiry no longer matters removes a security control instead of renewing it. Pasting expired certificates onto a public status page for “transparency” neither restores service nor protects private keys; it only advertises the failure.
Exam caveat: holiday freezes often restrict changes—the operational answer is to renew before the freeze window, with rollback certs retained. Automation should cover intermediate CA and root trust on clients if the issuing chain changes. Monitor NotAfter with alert thresholds measured in weeks, not hours, for public-facing VPN.
Operational check: inventory VPN concentrator NotAfter dates, schedule renewal before the freeze, deploy via the approved config/cert pipeline, run test authentications from clerk and remote-admin profiles, and confirm monitoring no longer warns on imminent expiry.