
Firewalls and servers at a plant should send their log messages to one collector. Which service is that collector?
Select an answer to reveal the explanation.
Short Explanation
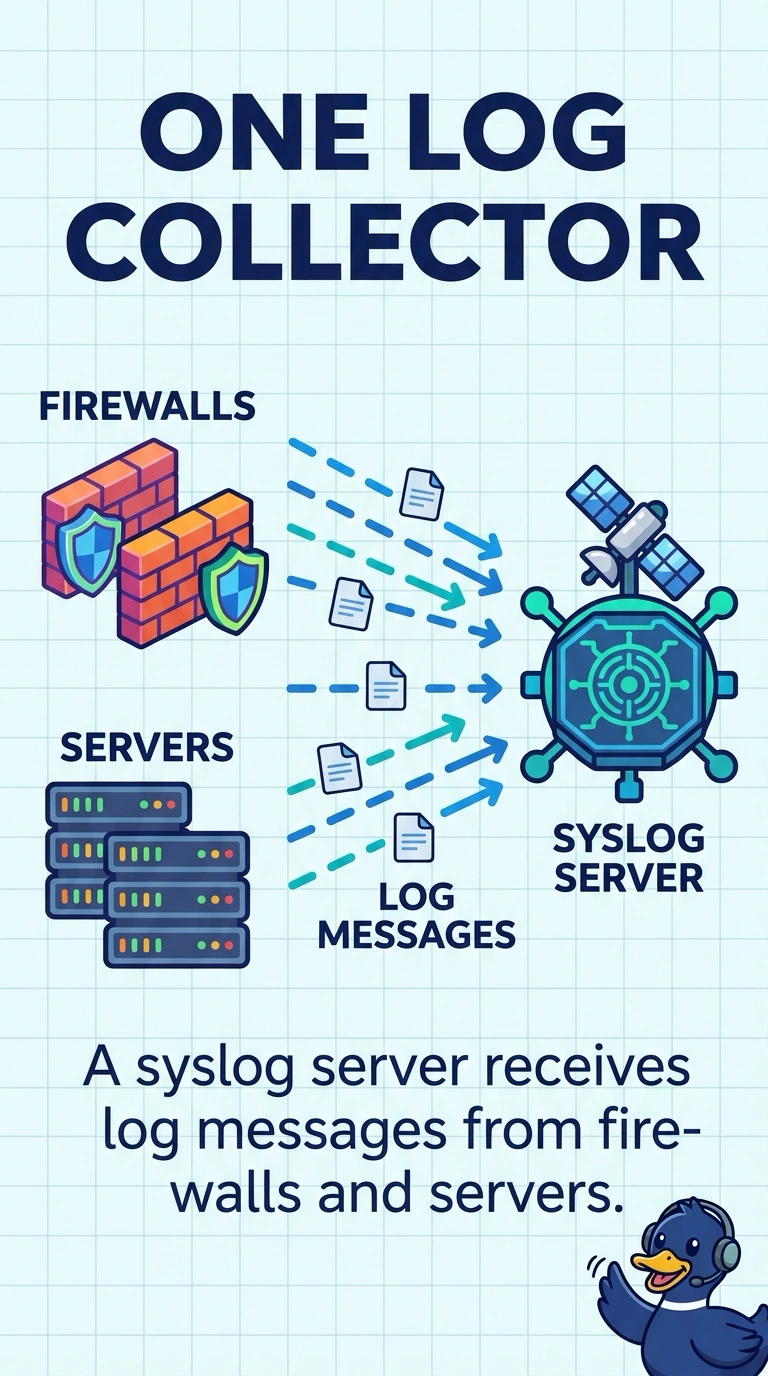
Every device should mail its diary to the same notebook. That notebook is the syslog server you collect on. Mail transfer, time sync, and a spam filter are other services, and they are not the log collector.
Full Explanation
Syslog is the service devices use to send log messages to a central collector. Firewalls and servers sending their logs to one place are using a syslog server. SMTP transfers mail between mail systems. It is not the collector for device logs. NTP synchronizes clocks. Accurate time makes logs easier to read, and the time server does not store the log messages. A spam gateway filters email. Firewalls do not send their security logs there as their collector. Exam caveat: the devices and the collector have to agree on the syslog port and on whether the traffic is protected. Pointing them at the server is not enough if a firewall blocks the path. Operational check: generate a test event on a firewall and confirm that event arrives on the collector. Send a test event from one firewall and find that event on the collector. Confirm the collector and the firewall agree on the path the logs take. Find the test event in the collector before you add the rest of the plant. Set the clocks before you compare events from two devices.