
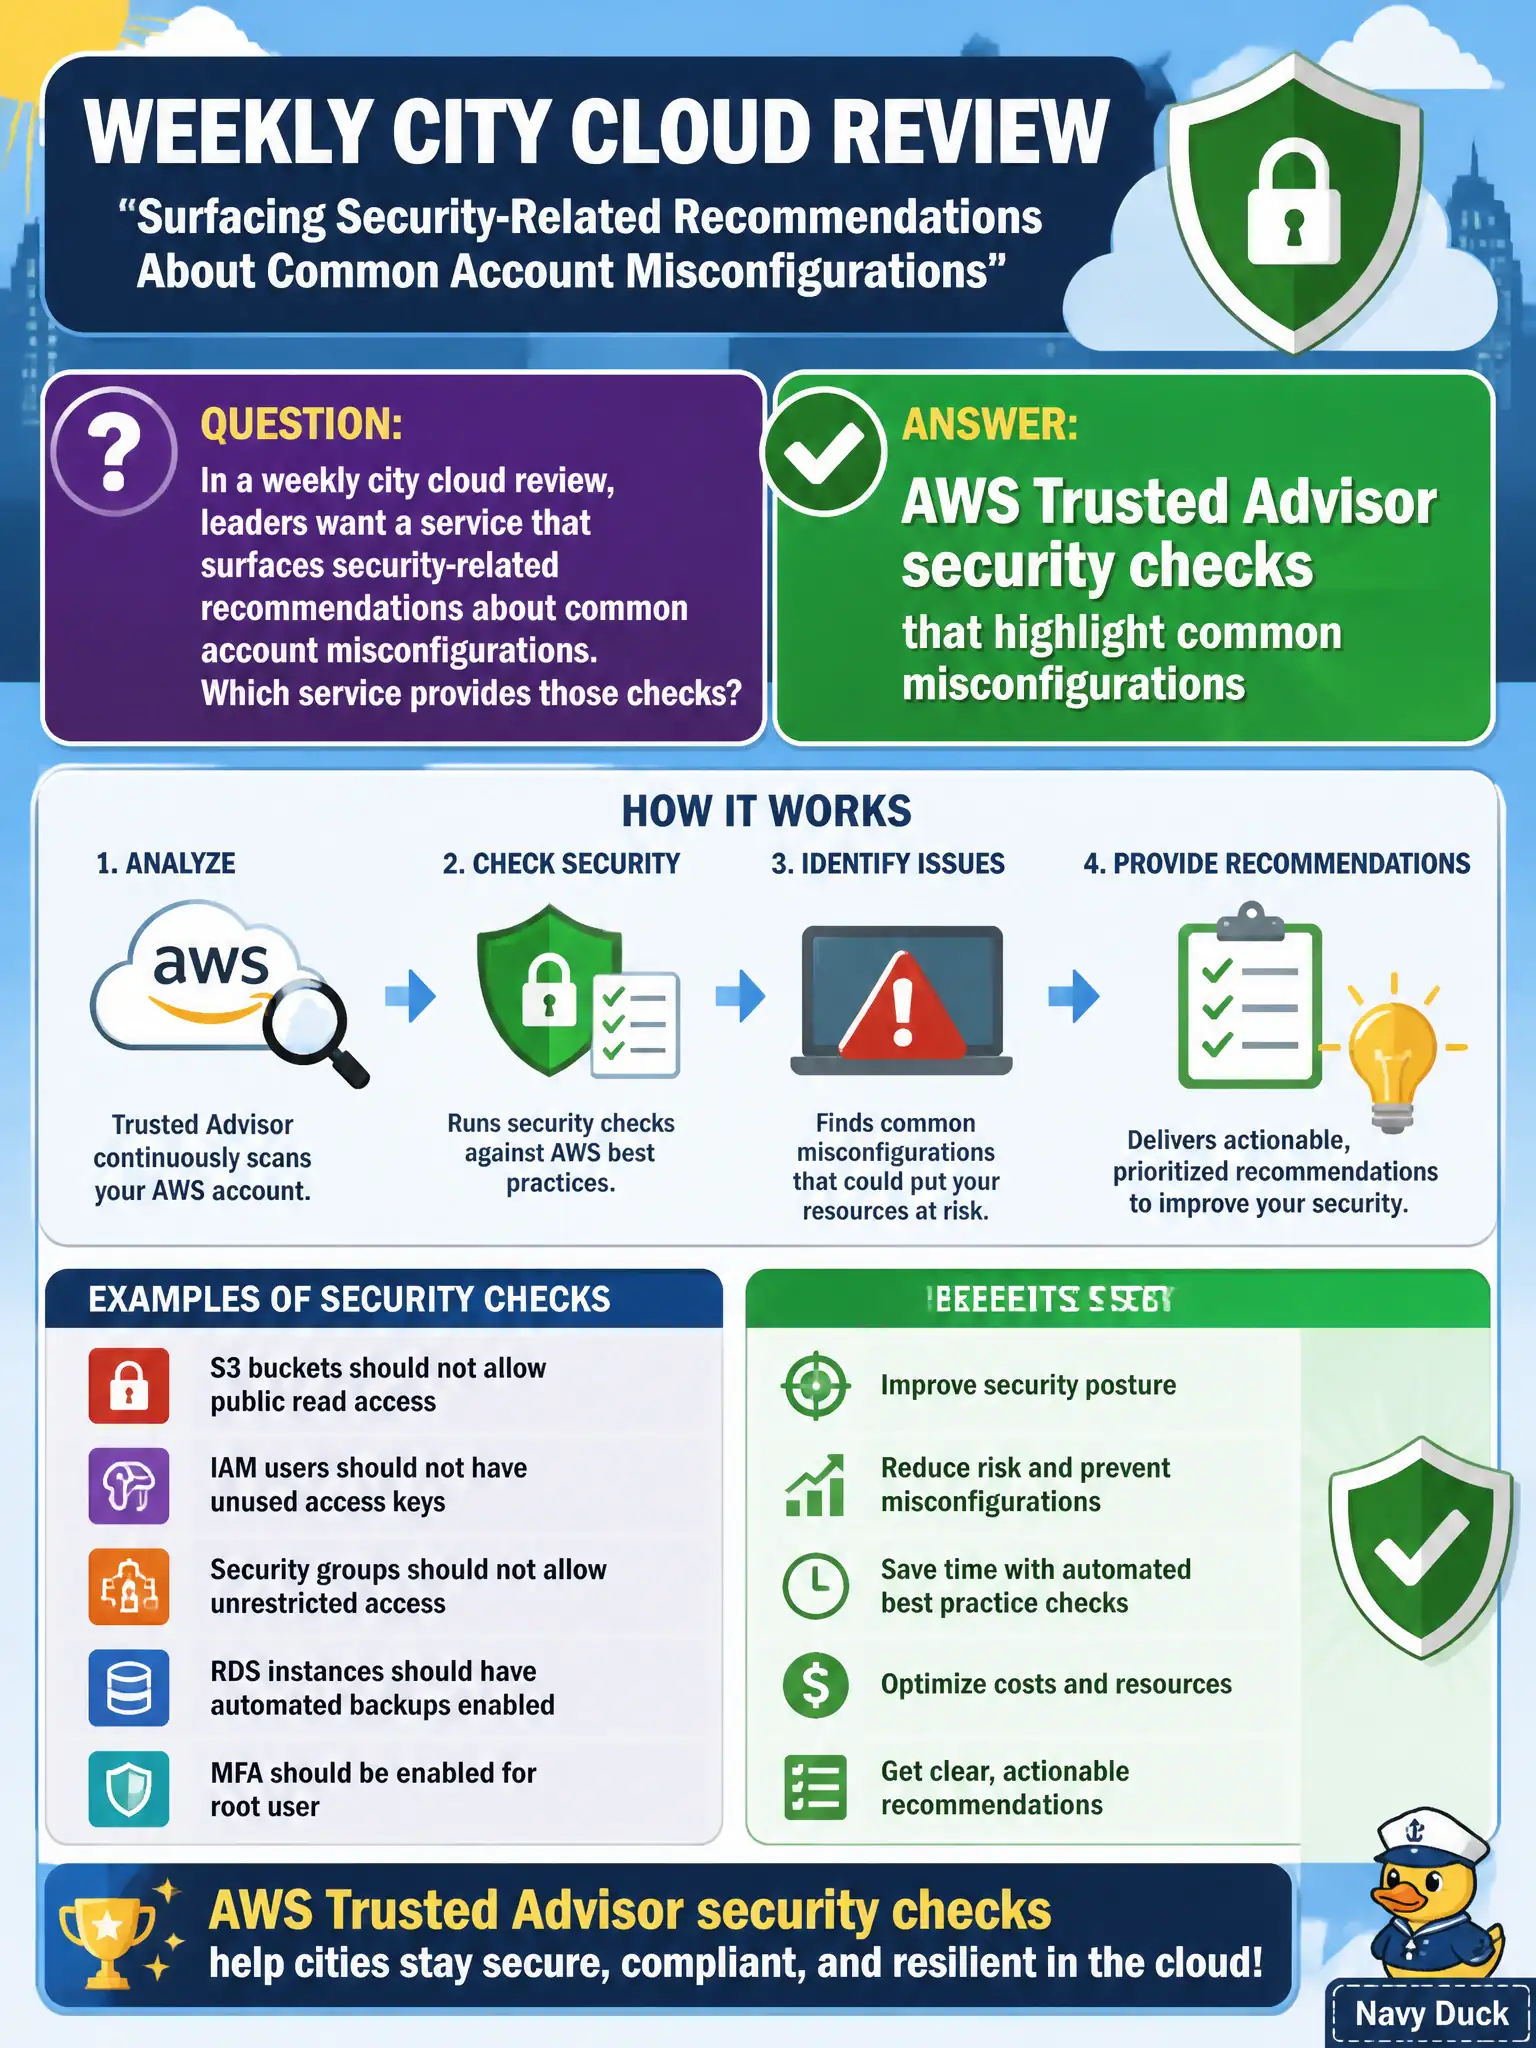
In a weekly city cloud review, leaders want a service that surfaces security-related recommendations about common account misconfigurations. Which service provides those checks?
Select an answer to reveal the explanation.
Short Explanation
Trusted Advisor is the friendly inspection report that points at open buckets, missing MFA on root, and similar oops moments. It is not a database and not a text-to-speech bot.
Full Explanation
In a weekly city cloud review, leaders who want security-related recommendations about common account misconfigurations should use AWS Trusted Advisor security checks. Trusted Advisor evaluates the account against AWS best-practice checks and highlights issues such as overly permissive security groups, lack of MFA on the root user, or other security hygiene findings (check availability depends on Support plan). That recommendation-oriented misconfiguration view is what leadership reviews when asking “what are we doing wrong by default?” rather than “what active threat actor findings do we have right now?”
Amazon Polly synthesizes speech from text; it does not deliver threat-intel briefings as a security posture engine. AWS Snowcone is a small edge compute and data-transfer device; it is not an online account-configuration scanner that only works while offline. Amazon Aurora is a managed relational database engine; it does not replace IAM policy review processes.
Exam caveat: Trusted Advisor = best-practice recommendations and common misconfigurations; GuardDuty = threat detection findings; Config = configuration compliance recording and rules; Security Hub = aggregated security posture. Pick Trusted Advisor when the stem stresses recommendations about misconfigurations.
Operational check: open Trusted Advisor before the weekly review, filter to security checks, assign remediations to account owners, track closure of high-risk items such as open administrative ports on EC2, and note which checks require Business/Enterprise Support so leadership understands coverage limits. Pair the review with GuardDuty finding trends so hygiene and active threats are both visible.