
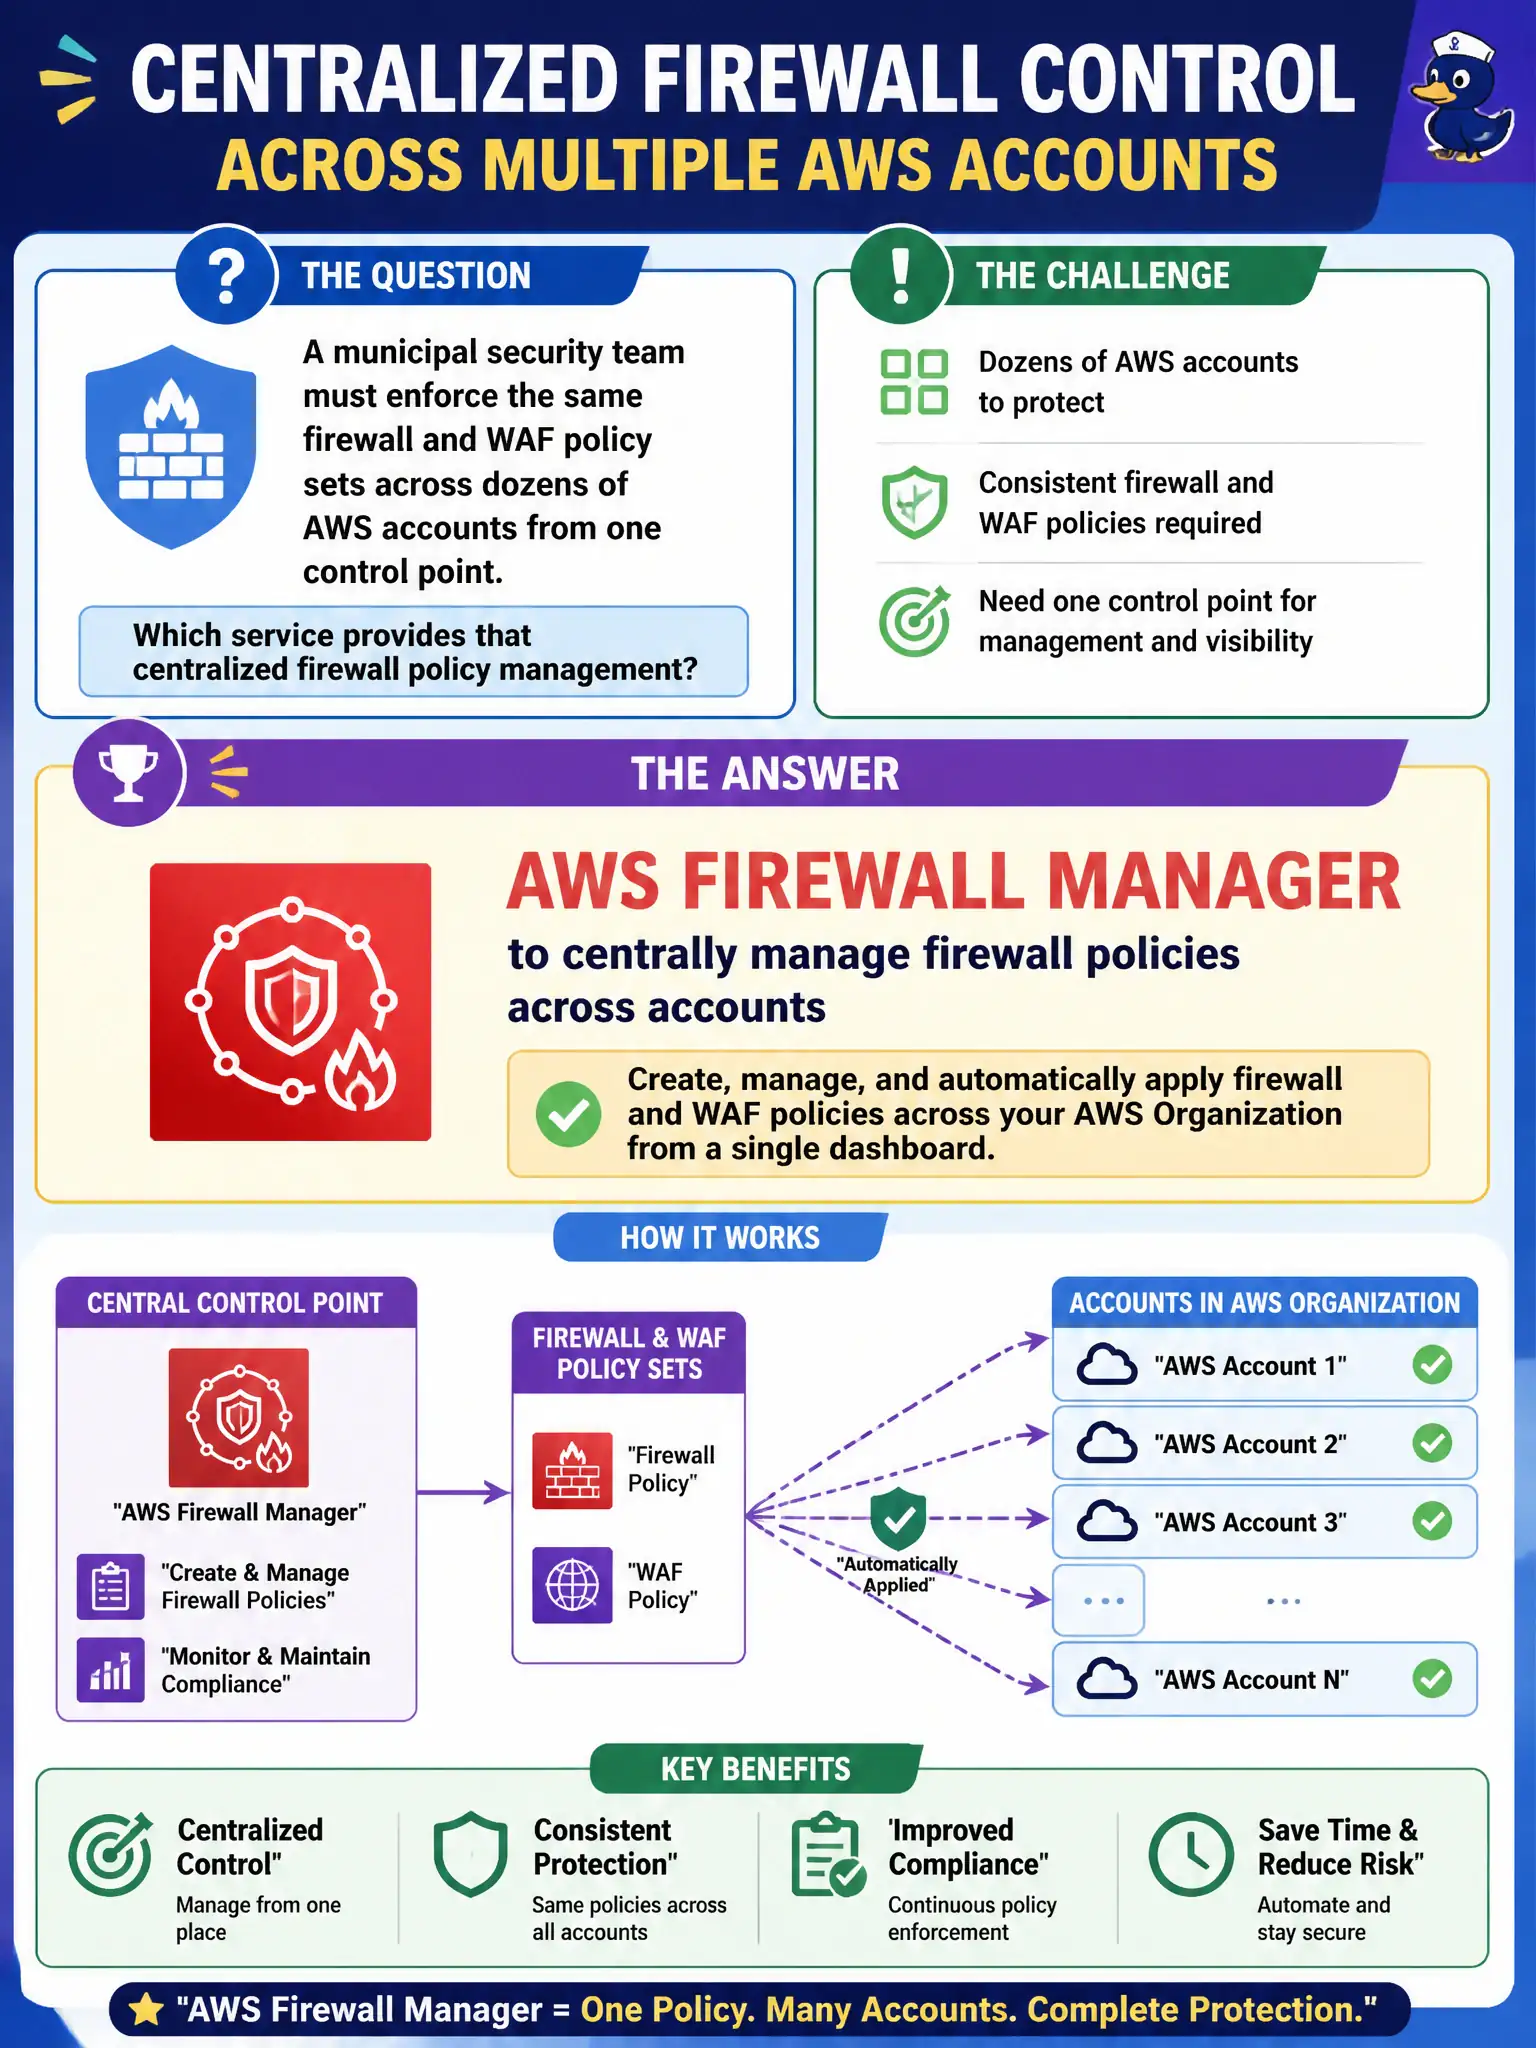
A municipal security team must enforce the same firewall and WAF policy sets across dozens of AWS accounts from one control point. Which service provides that centralized firewall policy management?
Select an answer to reveal the explanation.
Short Explanation
Think of one fire-code office writing the rules once for every city building. Firewall Manager is that central desk for firewall and WAF policies across accounts, instead of hand-editing each account alone.
Full Explanation
When a municipal security team must enforce the same firewall and WAF policy sets across dozens of AWS accounts from one control point, AWS Firewall Manager is the service purpose-built for that centralized policy management. Firewall Manager works with AWS Organizations to define security policies once—covering AWS WAF web ACLs, Shield Advanced protections, security groups, and related firewall constructs—and then applies or audits those policies across member accounts. For a city or county that operates separate accounts per department (public works, parks, permitting, finance), this removes the drift that appears when each team hand-edits rules in isolation.
Amazon Cognito user pools authenticate and authorize application users; they do not deploy VPC route tables or push firewall policies across accounts. Treating Cognito as a network-policy distributor confuses identity for apps with organization-wide network security governance. AWS Snowball is a family of physical data-transfer appliances used to move large datasets into or out of AWS; it does not copy security group rules between Regions as a policy sync mechanism. Amazon Polly converts text to speech. Publishing firewall change tickets as Polly announcements has nothing to do with enforcing WAF or firewall policy sets and is not a control-plane product for security configuration.
Exam caveat: Firewall Manager assumes an Organizations setup and appropriate administrator delegation. At Cloud Practitioner depth, associate Firewall Manager with “central firewall/WAF policy across accounts,” not with day-to-day log analysis (GuardDuty) or configuration inventory alone (Config). It complements those services rather than replacing threat detection or compliance recording.
Operational check: designate a Firewall Manager administrator account, enable the relevant policy types, scope policies to organizational units that hold municipal application accounts, and verify that new accounts inherit the mandated WAF or security-group baseline. Review Firewall Manager compliance findings when a department account drifts from the shared policy, then remediate or tighten scope before the next citizen-facing release.