
A security team wants a third-party firewall or IDS appliance image they can run in AWS. Where can they commonly procure such products?
Select an answer to reveal the explanation.
Short Explanation
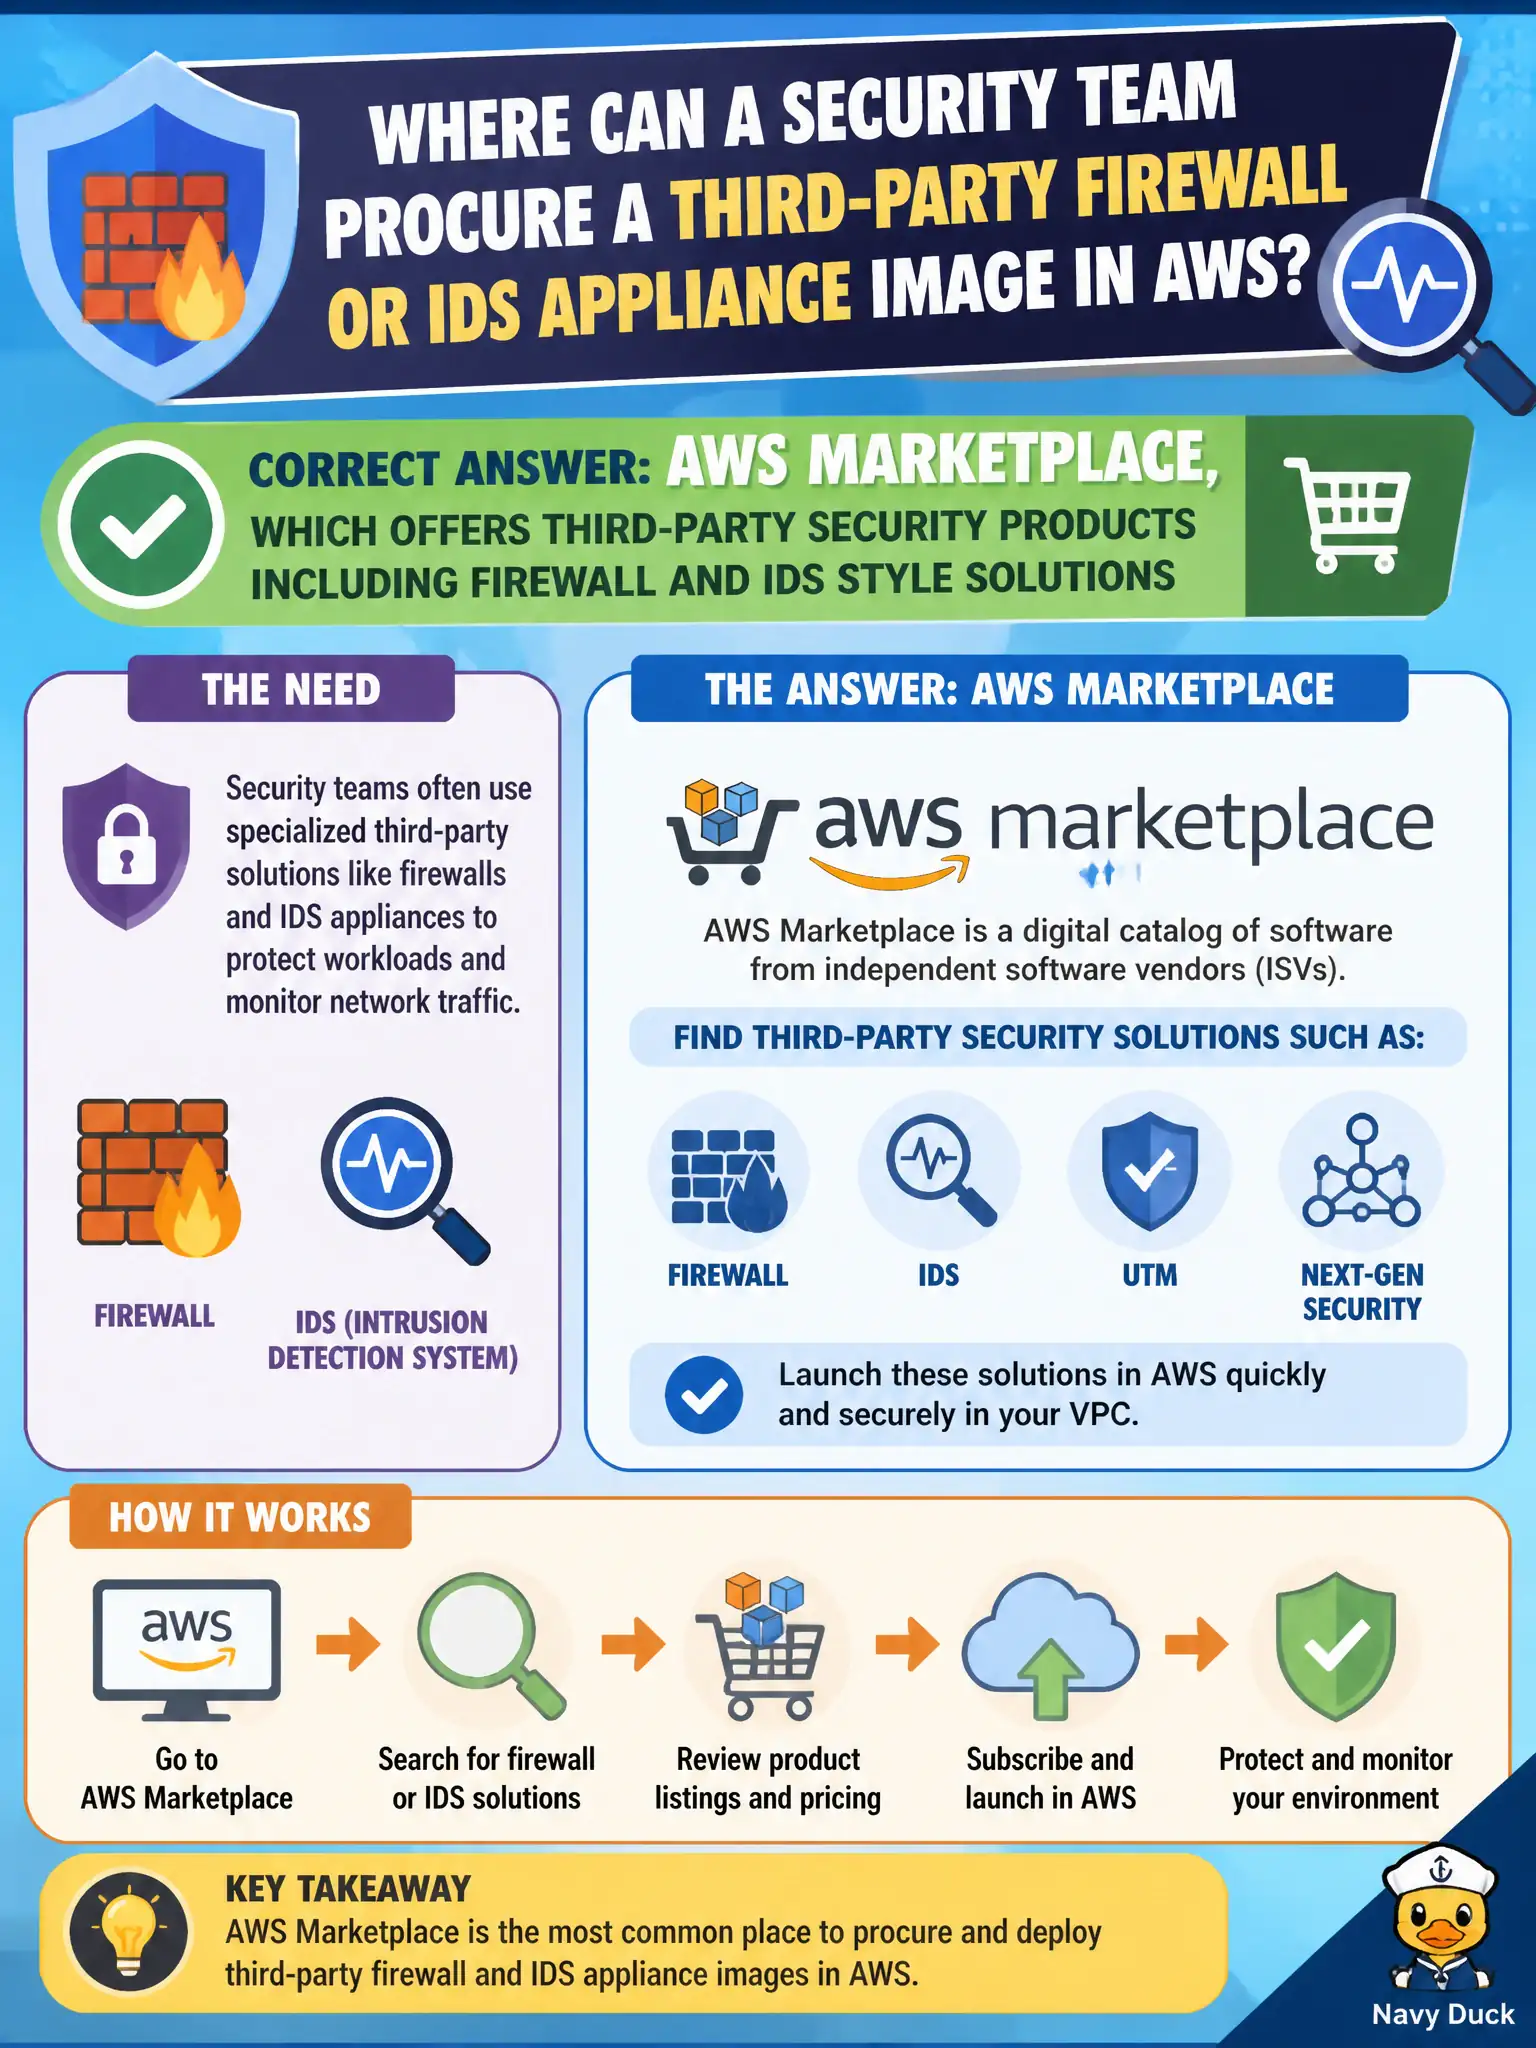
AWS Marketplace is the app store for cloud — including third-party firewalls and IDS tools you can subscribe to and launch. You are not limited to only first-party AWS security services when a partner appliance fits.
Full Explanation
AWS Marketplace commonly offers third-party security products including firewall and IDS style solutions that a security team can subscribe to and launch as appliances in AWS. Marketplace is the app store for cloud partner products when a third-party firewall or IDS image fits better than building from scratch. Amazon SNS topic policies govern pub/sub access; they are not a marketplace for IDS AMIs. Route 53 private hosted zones provide private DNS; they are not where you procure firewall appliances. AWS Artifact business associate agreements are compliance documents, not installable AMIs. Distractors fail by confusing messaging policies, DNS zones, and Artifact paperwork with product procurement. Exam caveat: third-party appliances still fall under shared responsibility for configuration, patching of the guest where applicable, and IAM/network placement. Operational check: evaluate Marketplace firewall/IDS offerings against city standards, launch into appropriate private subnets, restrict management access, integrate logs with CloudWatch or SIEM, and keep licensing and patch cadence under change management. In practice, shortlist Marketplace IDS/firewall AMIs that meet city vendor standards, place management interfaces on private subnets, and fold appliance patching into the same cadence as other EC2 fleets.