
All library helpdesk staff need the same set of IAM permissions. What is the cleanest foundational way to grant that shared policy?
Select an answer to reveal the explanation.
Short Explanation
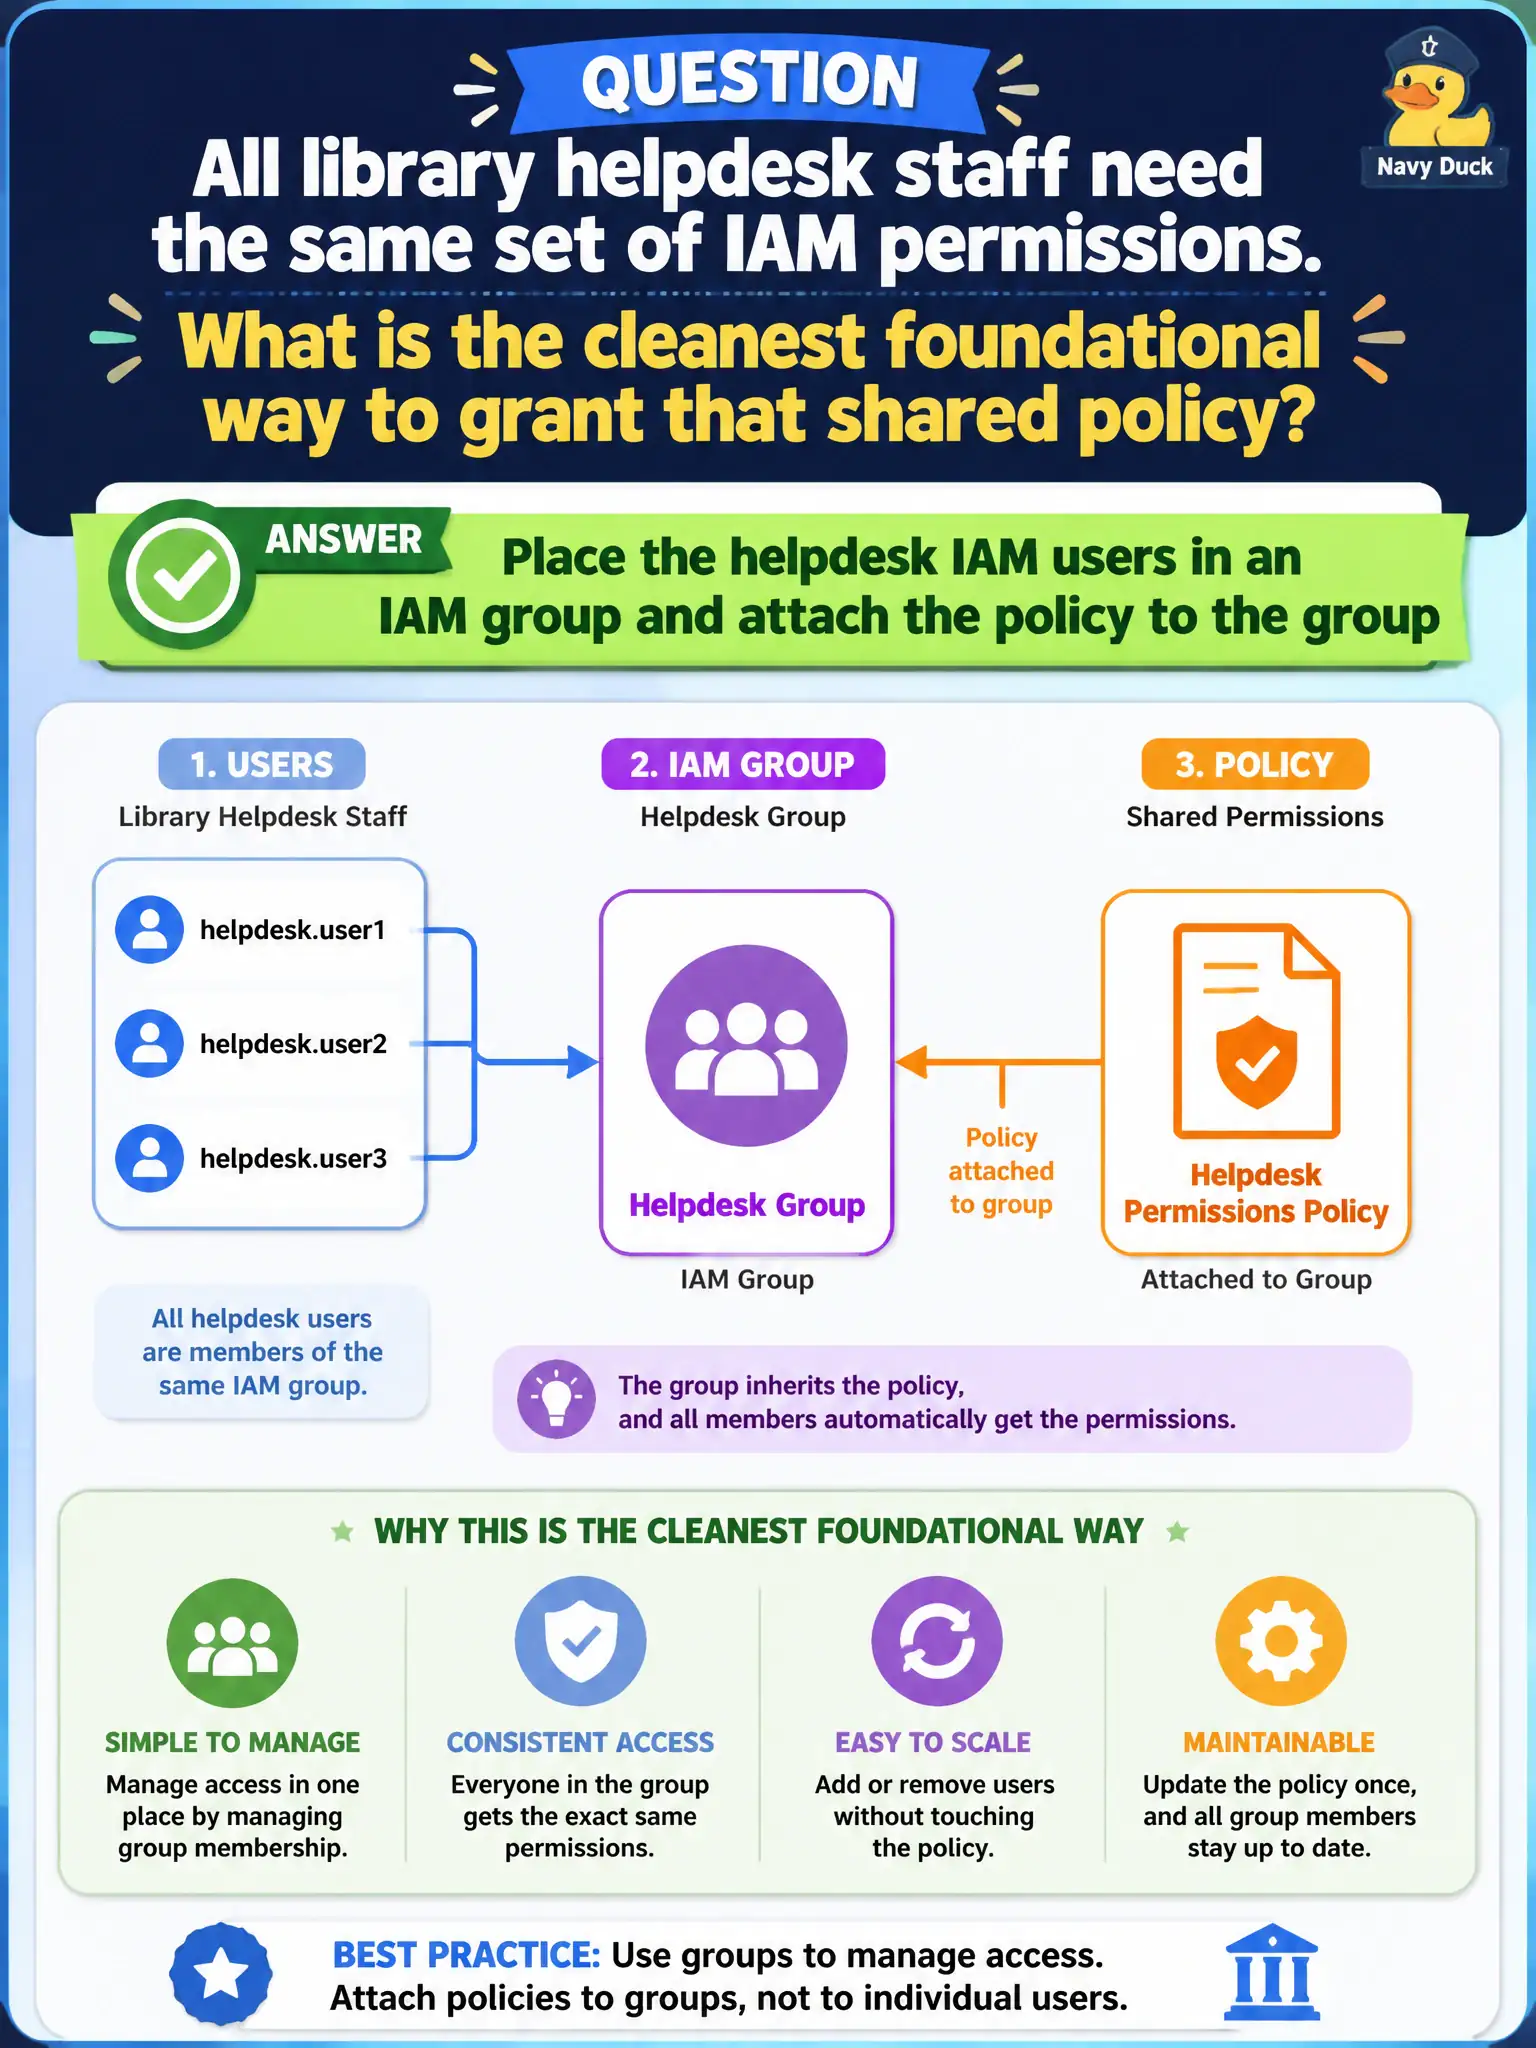
Groups are the team jersey — put every helpdesk user in the same group and attach the policy once. Hire someone new, drop them in the group, and they inherit the same permissions without another copy-paste adventure.
Full Explanation
Place helpdesk IAM users in an IAM group and attach the shared policy to the group — the cleanest foundational way to grant the same permissions to all library helpdesk staff. Groups are the team jersey: hire someone new, drop them in the group, and they inherit permissions without another copy-paste adventure. Creating a unique custom policy copy pasted onto each user by hand only does not scale and drifts. Giving every helpdesk person the account root password is indefensible. Opening all S3 buckets publicly so IAM permissions are unnecessary trades authorization for data exposure. Distractors fail by per-user policy sprawl, by root sharing, or by making data public to avoid IAM work. Exam caveat: prefer groups (or Identity Center permission sets) over repetitive inline user policies for workforce roles. Operational check: create a helpdesk group, attach the least-privilege policy once, move users into the group, remove duplicate inline policies, review membership when staff change desks, and confirm root remains unused for helpdesk tickets. In practice, onboard helpdesk staff by group membership alone, remove per-user policy copies, and audit monthly that nobody in helpdesk holds root or AdministratorAccess.