
Which authentication hardening method should a Cloud Practitioner recommend first when asked how to strengthen IAM user console logins that already use passwords?
Select an answer to reveal the explanation.
Short Explanation
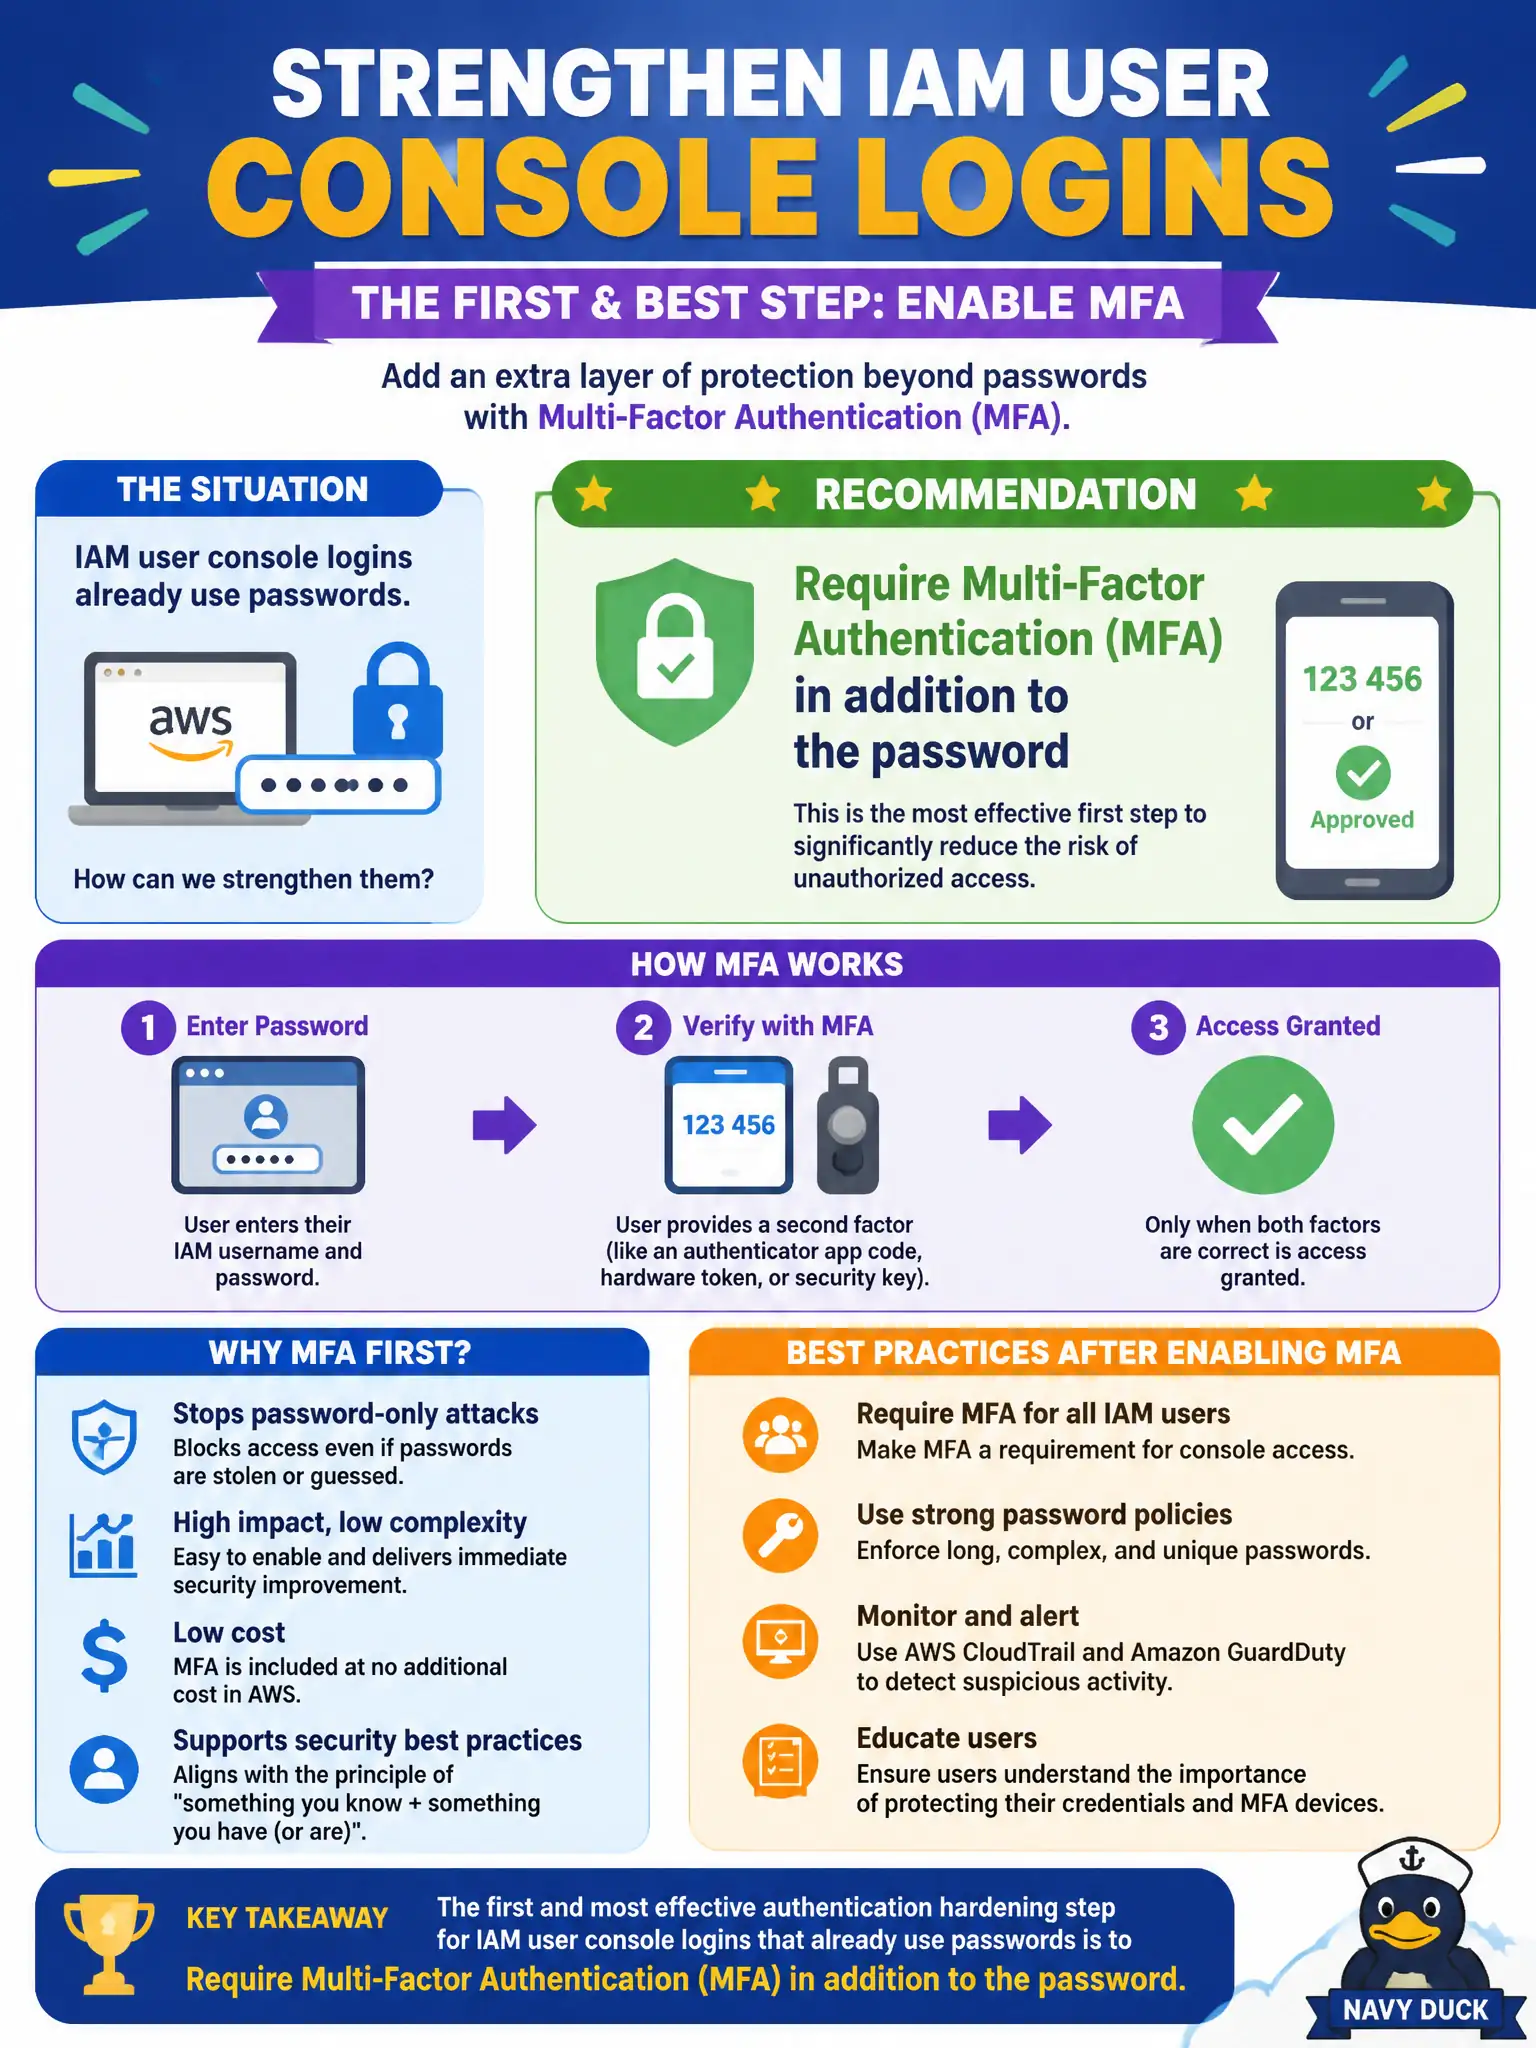
When the question is how to harden a password-based console login, MFA is the classic answer — second factor, much harder to phish. Keep the password, add the authenticator, sleep better.
Full Explanation
Require multi-factor authentication (MFA) in addition to the password when asked how to strengthen IAM user console logins that already use passwords. MFA is the classic Cloud Practitioner answer — second factor, much harder to phish — keep the password, add the authenticator. Removing all passwords and publishing temporary credentials on a wiki is unsafe theater. Replacing console login with anonymous internet access to the account removes authentication entirely. Disabling password policies so users can choose shorter passwords weakens the first factor. Distractors fail by publishing credentials, by going anonymous, or by weakening password rules. Exam caveat: MFA complements password policy; for workforce scale, also consider federation so console access ties to corporate SSO. Operational check: enforce MFA for console users, start with privileged roles, educate staff on authenticator apps or hardware tokens, monitor non-MFA console usage where possible, and never trade MFA away during "busy season" exceptions without time-boxed risk acceptance. In practice, enable MFA enforcement for console users account-wide where feasible, prioritize admins first, and refuse wiki-based credential distribution during hardening projects.