
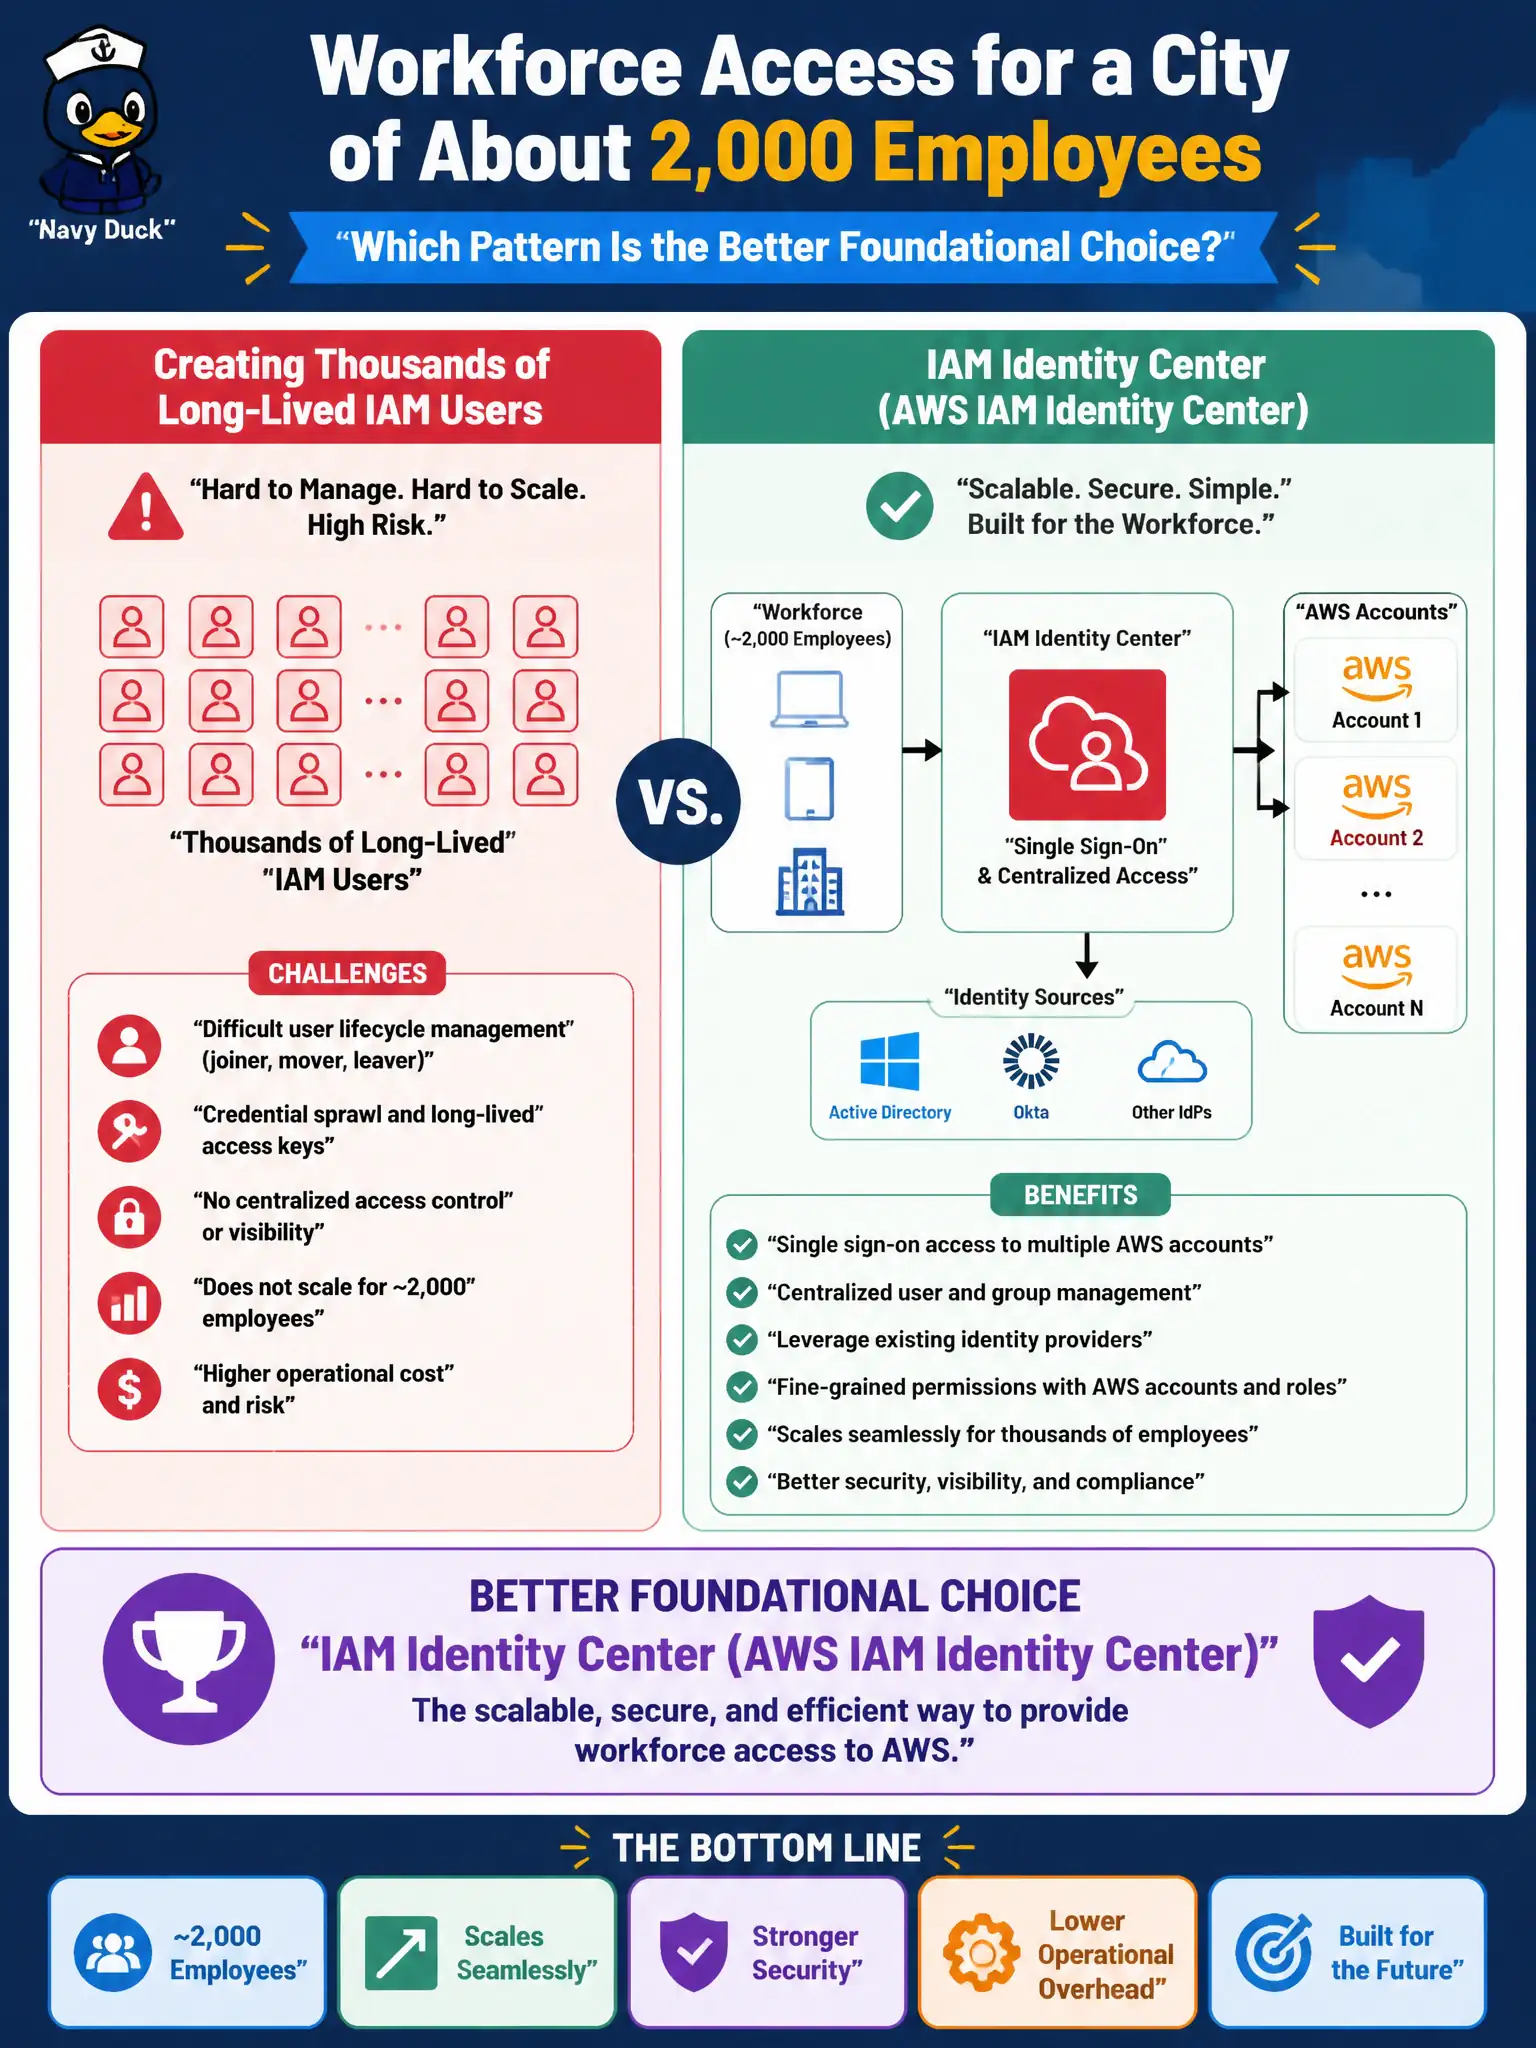
A city of about 2,000 employees needs workforce access to AWS accounts. Which pattern is the better foundational choice compared with creating thousands of long-lived IAM users?
Select an answer to reveal the explanation.
Short Explanation
Minting 2,000 individual IAM users is like cutting 2,000 metal keys and chasing them forever. Identity Center is the modern badge system — workforce SSO into AWS accounts without drowning in long-lived IAM user sprawl.
Full Explanation
For a city of about 2,000 employees, IAM Identity Center for scalable workforce single sign-on style access is the better foundational choice compared with creating thousands of long-lived IAM users. Minting 2,000 individual IAM users is like cutting 2,000 metal keys and chasing them forever; Identity Center is the modern badge system into AWS accounts. One shared IAM user named city-staff with a posted password destroys accountability. Root user sign-in for every employee shift change is unacceptable. Amazon S3 static website hosting is not an identity provider. Distractors fail by sharing credentials, by abusing root, or by confusing static websites with IdP patterns. Exam caveat: Identity Center still needs permission-set design, MFA, and lifecycle integration with HR systems. Operational check: deploy Identity Center, connect the workforce IdP, assign permission sets by department, avoid shared users, migrate leftover IAM users, and audit inactive assignments monthly. In practice, roll Identity Center out before hiring season spikes, avoid any shared city-staff user, and certify that all 2,000 workforce paths use SSO permission sets. Procurement language should forbid shared IAM passwords for workforce access going forward.